
mimosa
 owasp/mimosa
Open-source web application security challenge platform with auto-approved registration, SQL dump generation, and Docker deployment for hands-on…
ctfeducationlabs-practice+3
owasp/mimosaOpen-source web application security challenge platform with auto-approved registration, SQL dump generation, and Docker deployment for hands-on…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
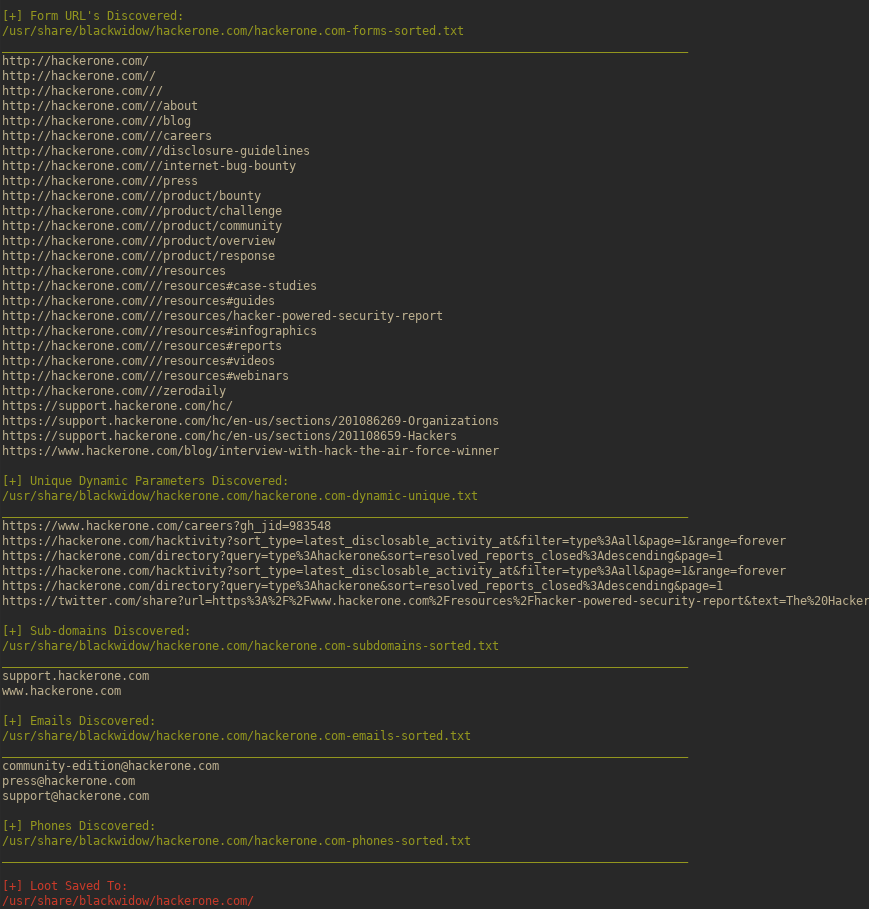 1n3/blackwidow
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
 moeinfatehi/admin-panel_finder
Burp Suite extension that finds exposed admin panels and login pages of web applications and infrastructure. 1,000+ payloads, OWASP WSTG-CONF-05.
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
 purpleteam-labs/purpleteam-app-scanner
Application scanning component of purpleteam
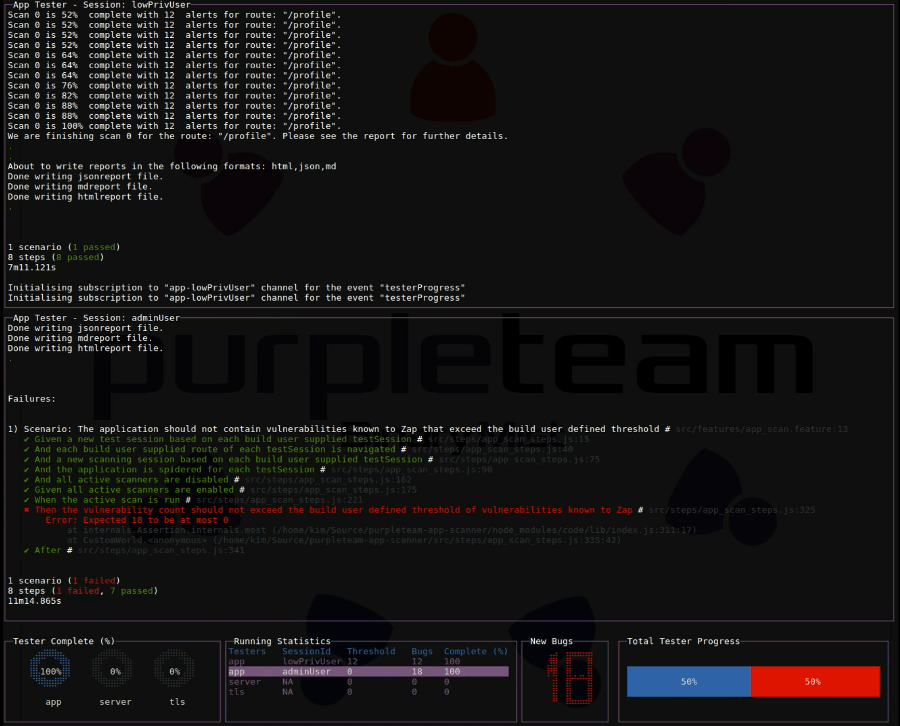 purpleteam-labs/purpleteam
CLI component of purpleteam
 purpleteam-labs/purpleteam-server-scanner
Server scanning component of purpleteam
 infoslack/awesome-web-hacking
Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
 urbanadventurer/whatweb
Next generation web scanner
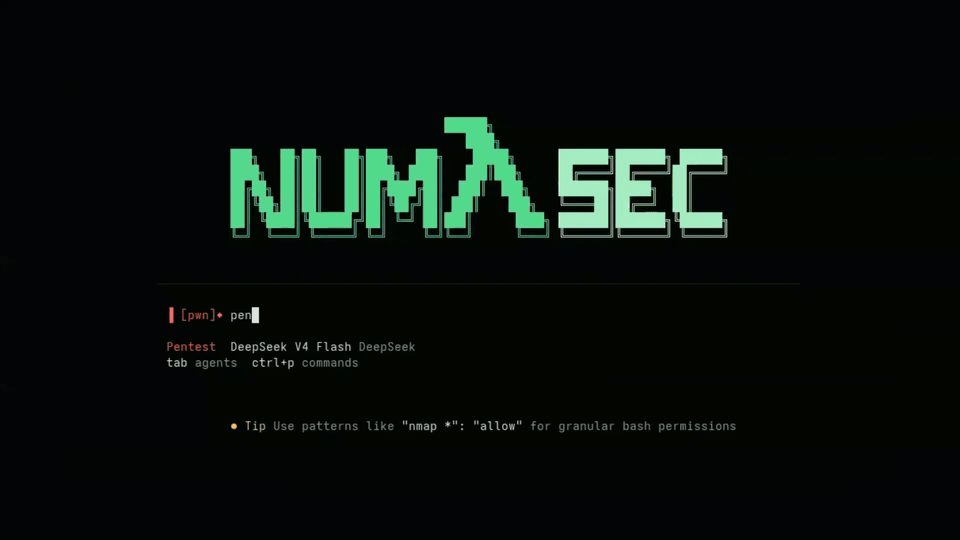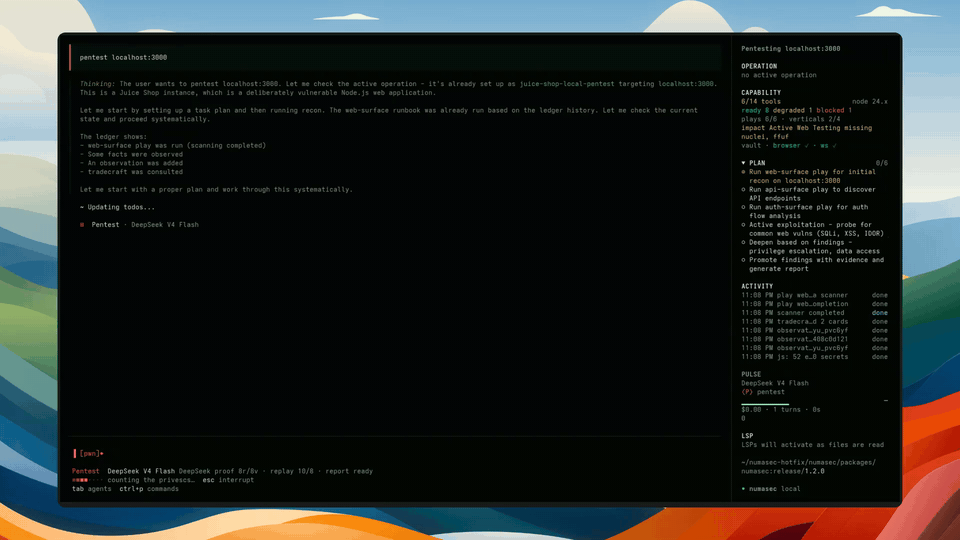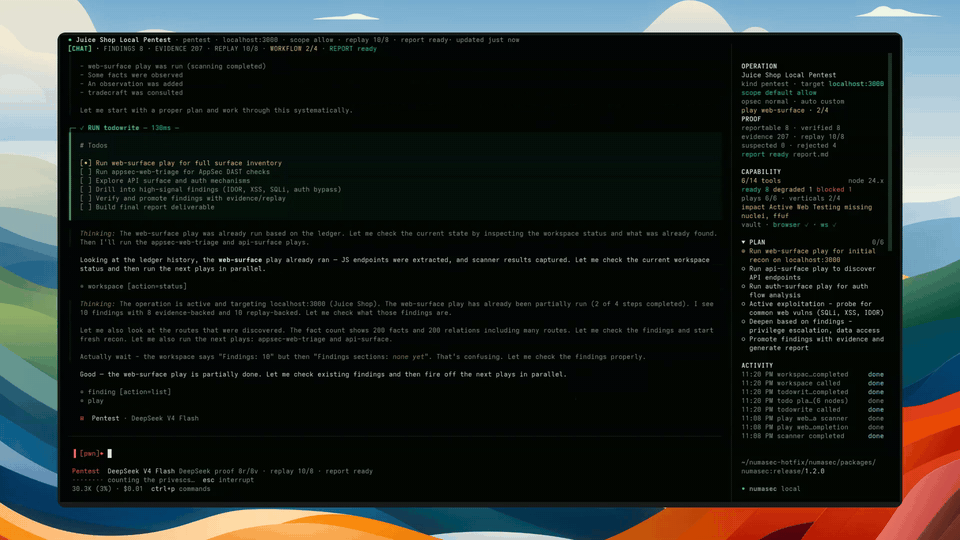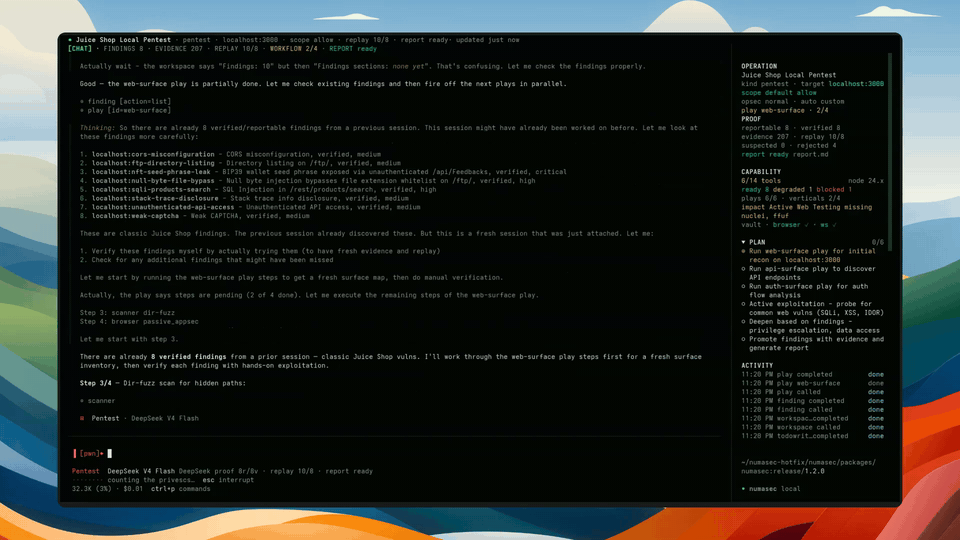 francescostabile/numasec
AI security agent that runs in your terminal, orchestrating local tools, runbooks, and agents for authorized AppSec, pentest, OSINT, and CTF…
 rajanagori/nightingale
Nightingale Docker for Pentesters is a comprehensive Dockerized environment tailored for penetration testing and vulnerability assessment. It comes…
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 dipakpanchal05/cve-2022-23808
Proof-of-concept exploit for CVE-2022-23808, a stored XSS vulnerability in phpMyAdmin 5.1.1 setup script, with payload and reproduction steps for…