
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-37069 — Proof-of-concept for absolute path disclosure in Veno File Manager 4.4.9 via an unauthenticated GET request to a debug script, revealing the server's application directory. | Kitploit
Tools/GitHubGitHub/jfs-jfs/cve-2026-37069
Vulnerability AnalysisInformation GatheringWeb SecurityMisconfiguration
GitHubjfs-jfs/cve-2026-37069

CVE-2026-37069

Proof-of-concept for absolute path disclosure in Veno File Manager 4.4.9 via an unauthenticated GET request to a debug script, revealing the server's application directory.

View Repository
214 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2026-37069

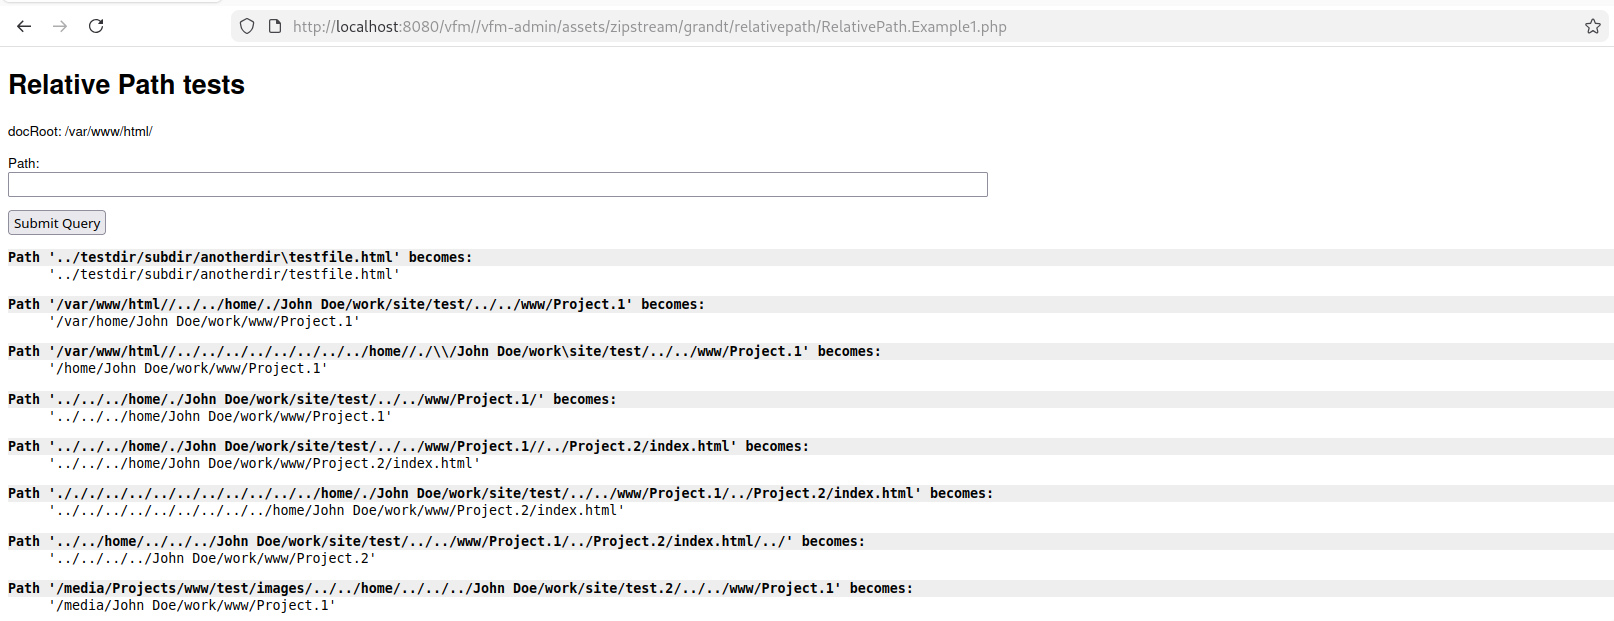
Absolute Path Disclosure in /vfm-admin/assets/zipstream/grandt/relativepath/RelativePath.Example1.php in Veno File Manager Project 4.4.9 allows an unauthenticated attacker to know in which system directory the application code is running by sending a GET request to the endpoint.
root-dir
Download Tool