
CVE-2026-118570
Proof-of-concept and analysis for CVE-2026-118570, a CSRF flaw in Drupal's fasttoggle toggle route, with a browser PoC page, test transcript, and fix…

Proof-of-concept and analysis for CVE-2026-118570, a CSRF flaw in Drupal's fasttoggle toggle route, with a browser PoC page, test transcript, and fix…

Multi-threaded PoC exploiting CVE-2026-119977, a TOCTOU race in WordPress core upgrade staging paths that yields unauthenticated remote code…

Python proof-of-concept for CVE-2026-120491, a stored XSS in Wing FTP Server before 8.2.6 where a crafted nowpath value forges a connection ID…

Shell-based proof-of-concept material for NGINX vulnerabilities CVE-2026-123007 and CVE-2026-123633, covering reproduction and verification of the…

Proof-of-concept and writeup for CVE-2026-125440, an unauthenticated shortcode injection in s2Member PayPal IPN handlers that can escalate to code…

Reflected XSS in Opixido OCMS admin/TUI/index.php (img parameter)

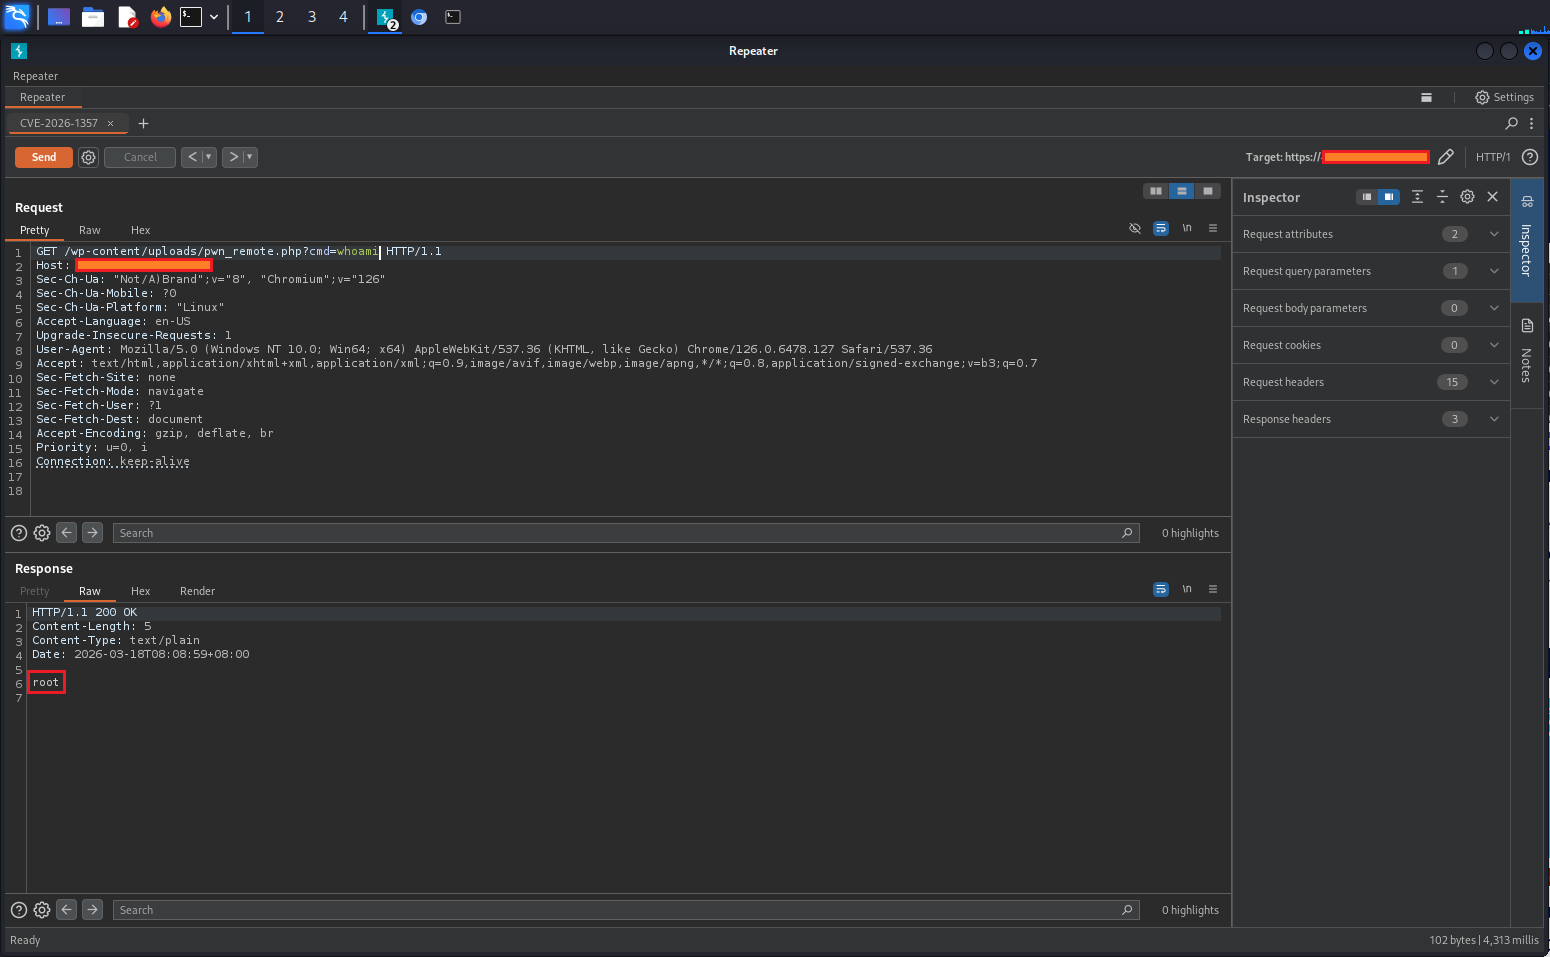
Advisory and technical analysis of CVE-2026-1357, an unauthenticated RCE in the WPvivid Backup & Migration WordPress plugin, covering root cause,…

Bilingual analysis and safe PoC for CVE-2026-124576, a BeikeShop PayPal payment bypass and guest-order IDOR, with source checks, offline logic model,…

Proof-of-concept and analysis for CVE-2026-124040, a CivetWeb HTTP/2 HPACK header-name corruption via use-after-free that bypasses literal-header…

Python PoC for CVE-2026-125283, an nginx alias + try_files integer underflow triggered via map captures, with Docker lab, trigger variants, and…

Printcart <= 2.13.2 Unauthenticated File Upload

Proof-of-concept scripts for CVE-2026-123007, an NGINX HTTP/2 integer underflow, including a minimal trigger and an exploit demonstrating…

Python PoC for CVE-2026-21589, a pre-auth path traversal in Atlassian Data Center products that reads arbitrary files under the web app root via…

Exploit and safe-check toolkit for CVE-2026-21589, an unauthenticated path traversal in Atlassian Data Center: WEB-INF file read, credential…

Advisory write-up for CVE-2026-22557, an unauthenticated path traversal (CWE-22) in Ubiquiti UniFi Network Application, covering affected versions,…

Vulnerability Research, Non-Destructive CVE Verification (CVE-2026-23813 ArubaOS-CX), & Automated Linux/PHP Hardening Suites — by Abishek M A…

Security advisory documenting CVE-2026-31158, an unauthenticated boolean-based SQL injection in a CRM login form's TxtUsername parameter, with…

Proof-of-concept scanner for SSRF and header injection in Angular Universal SSR apps. For authorized security testing only