crawlee
 apify/crawlee
Node.js web scraping and browser automation library for building reliable crawlers with HTTP and headless browser support, proxy rotation, and…
anti-botcrawlerfingerprint-spoofing+6
26.3k
apify/crawleeNode.js web scraping and browser automation library for building reliable crawlers with HTTP and headless browser support, proxy rotation, and…
 elazarl/goproxy
A customizable HTTP/HTTPS proxy library for Go supporting regular forwarding, CONNECT tunneling, MITM TLS interception, and programmatic…

 yukibtc/redknife
A Swiss Army knife for offensive security.
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 dragon-lady/netward-standalone
User-space bot and DDoS deflection for small HTTP services
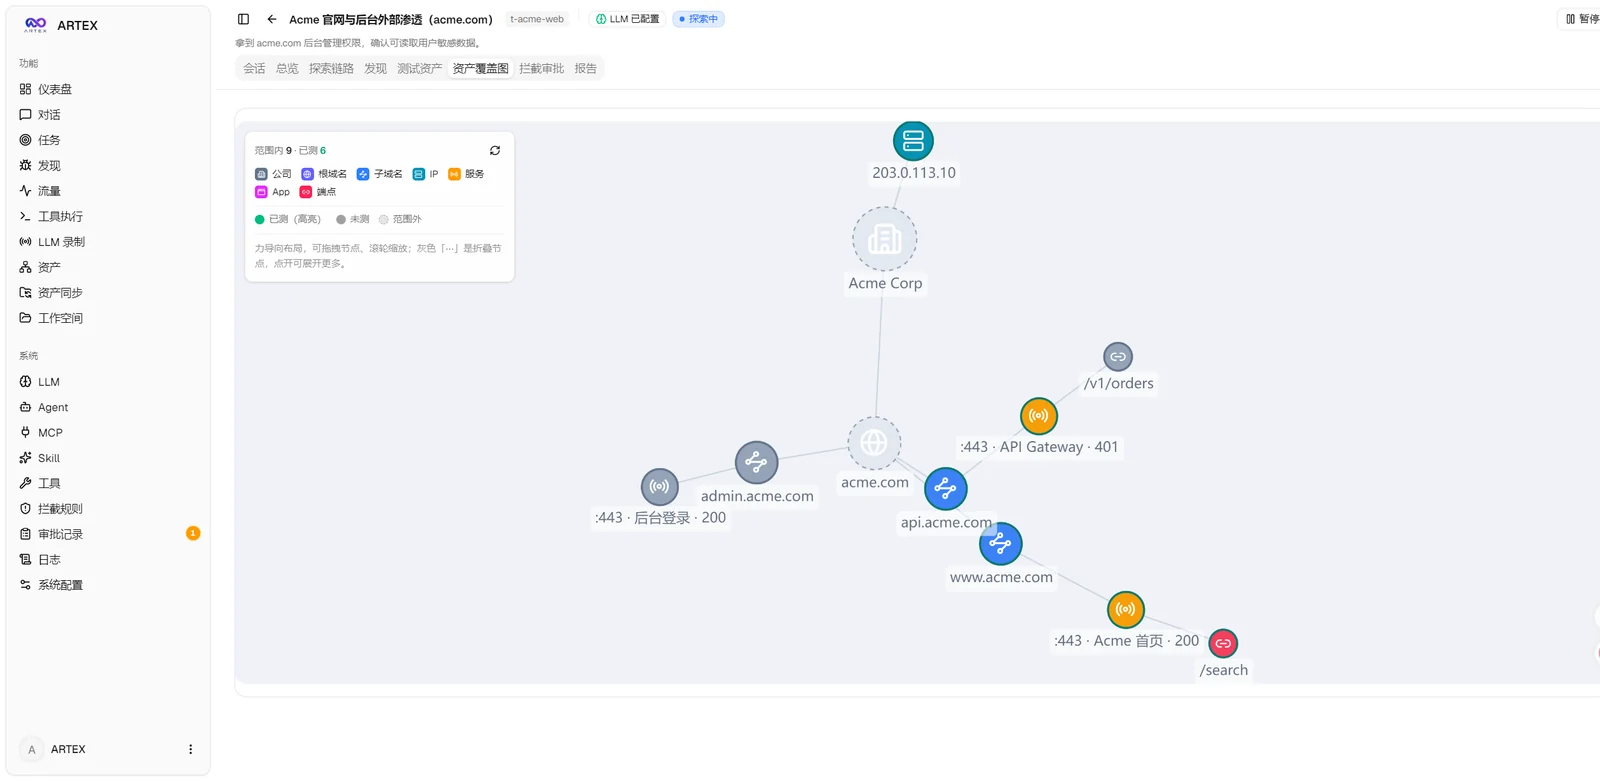 trhhubsd/artex
Multi-agent LLM system for autonomous penetration testing in isolated labs: planner/worker agents share asset and exploration graphs, with MITM…
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 shopify/toxiproxy
:alarm_clock: :fire: A TCP proxy to simulate network and system conditions for chaos and resiliency testing
 splinters-io/blinder
Content-blind reverse proxy for exposure-protected security scanning
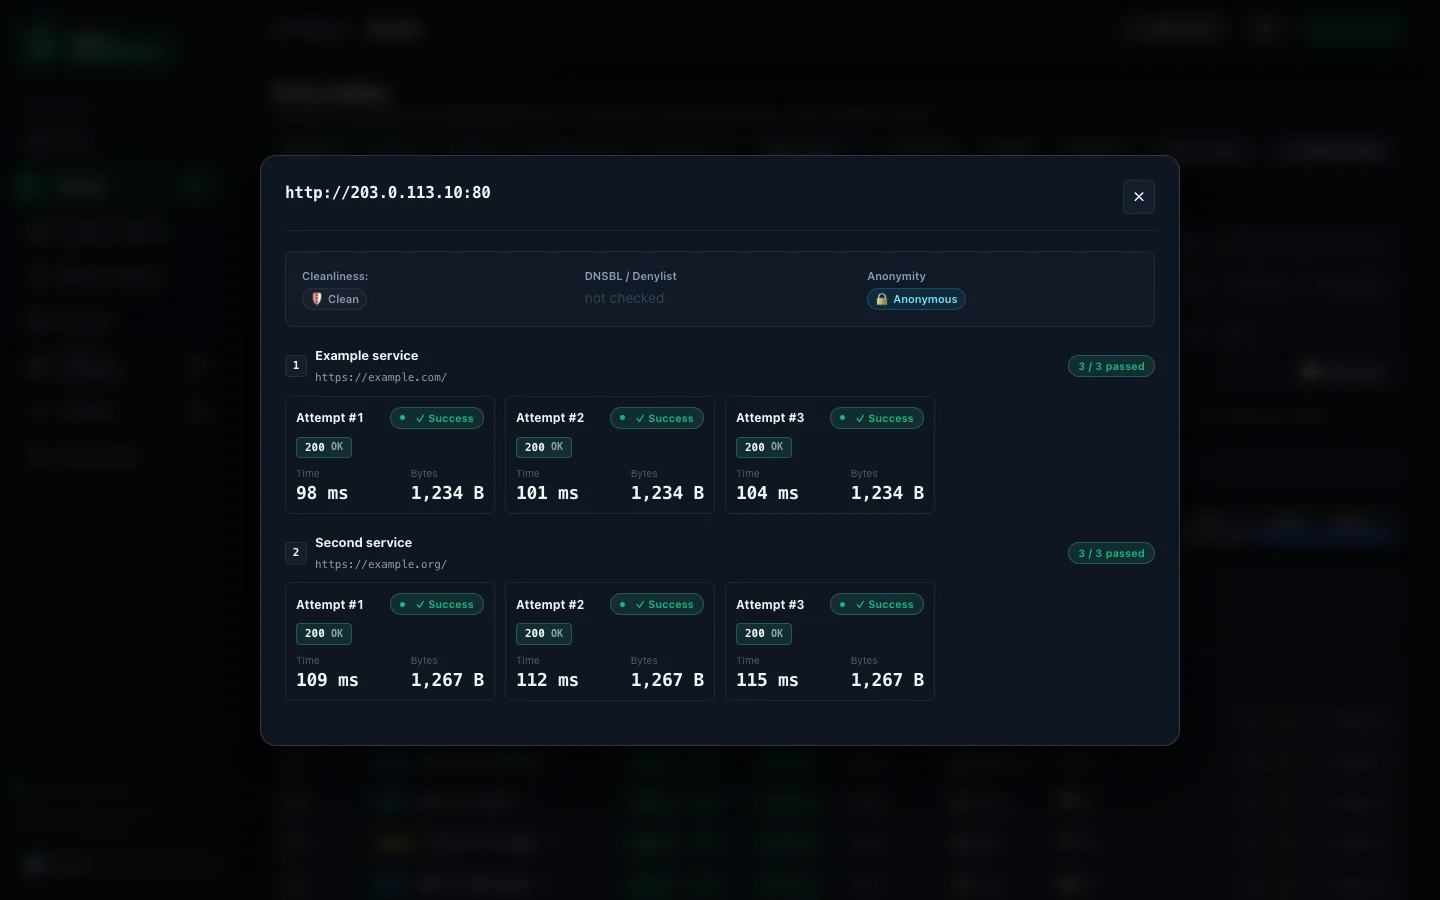 davidvoitenko/proxy-workbench
Collects, checks and ranks public HTTP/SOCKS proxies against your own targets, then serves them via ranked exports, pools, a rotating gateway and a…
 doronz88/harlogger
Simple utility for sniffing decrypted HTTP/HTTPS traffic on a macOS/iOS device (either jailbroken or not)
 confused-binary/waf-fu
Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
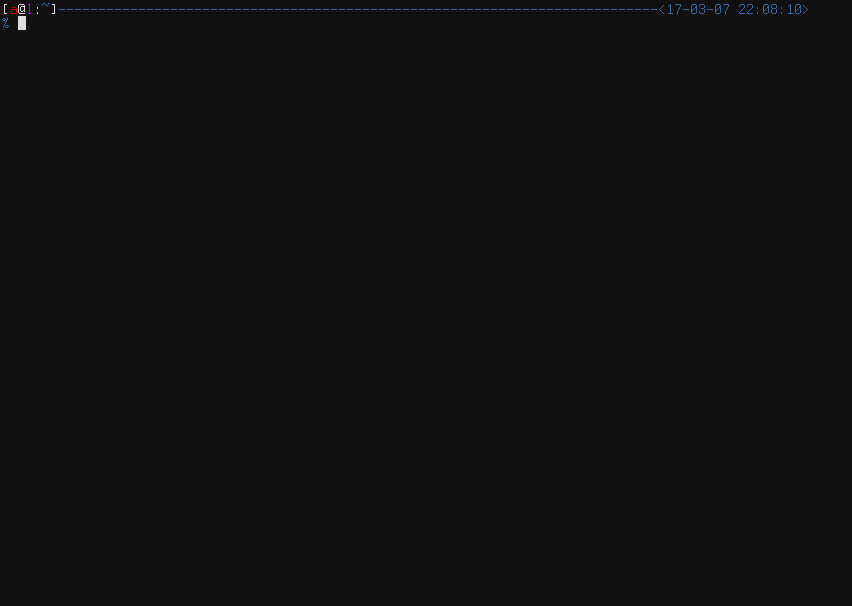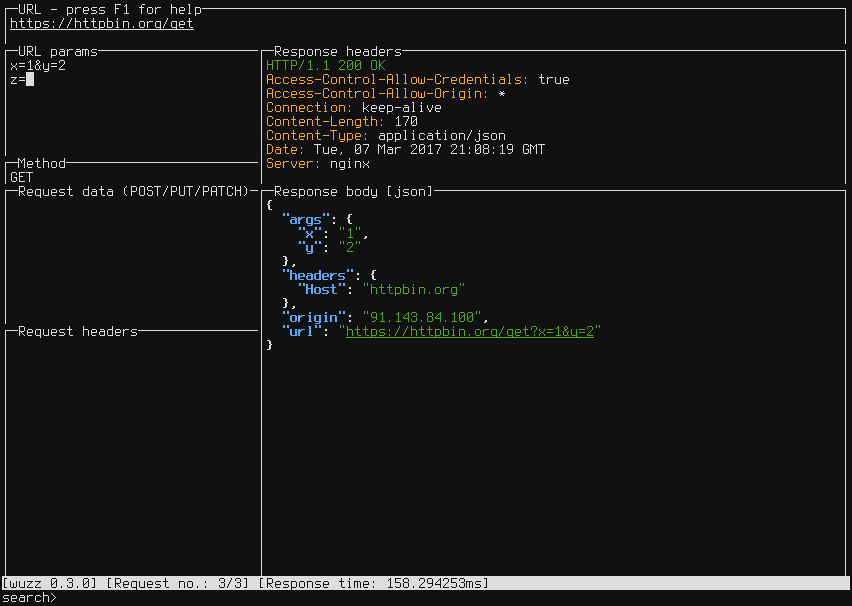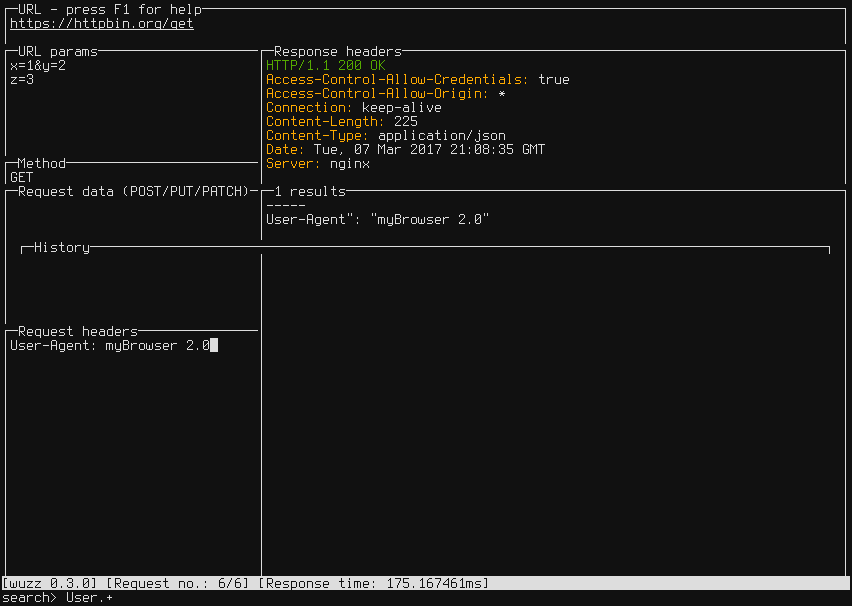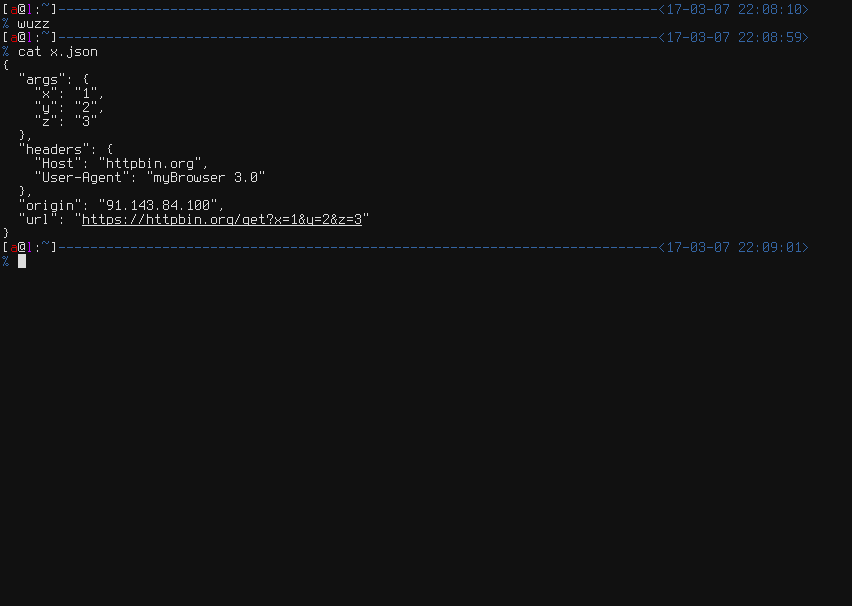 asciimoo/wuzz
Interactive cli tool for HTTP inspection
 ssh-mitm/ssh-mitm
Mirror moved — see GitHub and Codeberg
 pentagridsec/pentagridresponseoverview
Response Overview Extension for BurpSuite - Find exotic responses by grouping response bodies
 imbas007/cve-2025-53770-vulnerable-scanner
Python script to scan SharePoint hosts for CVE-2025-53770 using custom payloads, with optional Burp Suite proxy interception for traffic analysis and…