
CVE-2023-2033
 mistymntncop/cve-2023-2033
JavaScript exploit targeting CVE-2023-2033 for proof-of-concept testing and vulnerability validation in web applications.
exploitationpayload-developmentpenetration-testing+2
64
mistymntncop/cve-2023-2033JavaScript exploit targeting CVE-2023-2033 for proof-of-concept testing and vulnerability validation in web applications.
 ztgrace/mole
Framework for identifying and exploiting out-of-band (OOB) application vulnerabilities with a custom DNS/token server, Burp Suite extension, and…
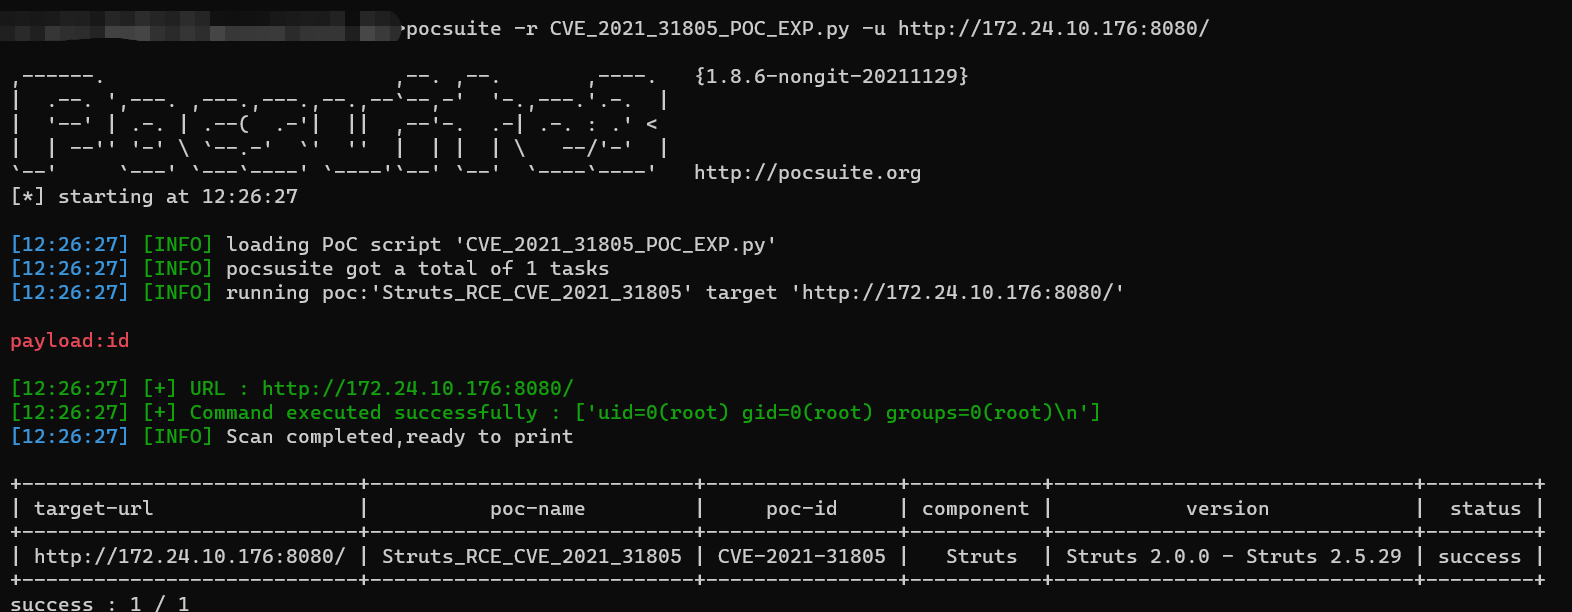 wrin9/cve-2021-31805
Python-based proof-of-concept and exploit for Apache Struts2 RCE (CVE-2021-31805), enabling command execution via OGNL injection. Includes POC and…
 luemmelsec/cve-2023-29357
C# proof-of-concept exploit for CVE-2023-29357 targeting SharePoint, with YARA detection rules and detailed usage instructions for security testing.
 zerodayevil/cve-2026-40369-exploit
Proof-of-concept exploit code targeting CVE-2026-40369, demonstrating the vulnerability for research and authorized security testing.
 holygu/cve-2023-42442
Go-based exploit for JumpServer unauthorized access vulnerability (CVE-2023-42442) with a single-command execution interface for penetration testing.
 rohmatariow/cve-2026-22812-exploit
Exploitation toolkit for CVE-2026-22812 (OpenCode unauthenticated RCE) providing interactive shell, arbitrary command execution, file…
 mcipekci/wp2shell
Pre-auth RCE PoC for WordPress core — chains CVE-2026-63030 (REST /batch/v1 route-confusion desync) with CVE-2026-60137 (author__not_in SQLi) into an…
 ghost-nemesis/cve-2021-20837-poc
Proof-of-concept exploit for CVE-2021-20837, a remote code execution vulnerability in MovableType CMS. Demonstrates exploitation technique for…
 shyam999/athanasius
Framework for penetration testing. The software can identify everything from cross-site scripting to SQL injection. Developers can also use this…
 cve-2019-0708-poc/cve-2019-0708
Exploit tool targeting CVE-2019-0708 in Remote Desktop Services, enabling remote code execution on vulnerable Windows systems for penetration testing…
 manouchehri/cve-2017-1000117
Proof-of-concept exploit for CVE-2017-1000117, a critical remote code execution vulnerability in Git. Includes Go and shell-based PoCs for testing…
 huseyinstif/cve-2024-4577-nuclei-template
Nuclei template for detecting CVE-2024-4577 PHP CGI argument injection vulnerability, enabling automated RCE testing via crafted HTTP requests and…
 cfielding-r7/poc-cve-2023-2868
Ruby-based proof-of-concept exploit for CVE-2023-2868 command injection in Barracuda ESG, delivering a reverse shell for targeted penetration testing.
 ignis-sec/cve-2025-6218
Proof-of-concept exploit for WinRAR path traversal vulnerability (CVE-2025-6218) enabling remote code execution via crafted archive files. Includes…
 adhikara13/cve-2023-24489-sharefile
This project is a Python script that exploits the CVE-2023-24489 vulnerability in ShareFile. It allows remote command execution on the target server.…
 1337g/cve-2018-0101-dos-poc
Proof-of-concept denial-of-service exploit for Cisco ASA WebVPN CVE-2018-0101, demonstrating the vulnerability and enabling security testing on…
 bigherocenter/cve-2024-7029-exploit
Exploit code for CVE-2024-7029, a web application vulnerability, providing proof-of-concept implementation for security testing and research.