

zaproxy
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
android-securityapi-securityapi-security-testing+15
15.6k
zaproxy/zaproxyOpen-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 avoliomattia/nginx-cve-2026-123007-cve-2026-123633
Shell-based proof-of-concept material for NGINX vulnerabilities CVE-2026-123007 and CVE-2026-123633, covering reproduction and verification of the…
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 llcforge/cve-2026-125350
Proof-of-concept trigger and detection notes for CVE-2026-125350, a use-after-free in Chrome's XML parser (CVSS 8.8, Chrome < 157.0.8103.50, CISA…
 sfewer-r7/cve-2026-123007
Proof-of-concept scripts for CVE-2026-123007, an NGINX HTTP/2 integer underflow, including a minimal trigger and an exploit demonstrating…
 al4n4n/cve-2026-125350
Archived pointer repository for CVE-2026-125350, a Chromium libxslt use-after-free; code, packet captures and Suricata/YARA detection rules now live…
 yozturk0/cve-2026-125440
Proof-of-concept and writeup for CVE-2026-125440, an unauthenticated shortcode injection in s2Member PayPal IPN handlers that can escalate to code…
 usama-hanif131/cve-2026-129254
Reflected XSS in Opixido OCMS admin/TUI/index.php (img parameter)
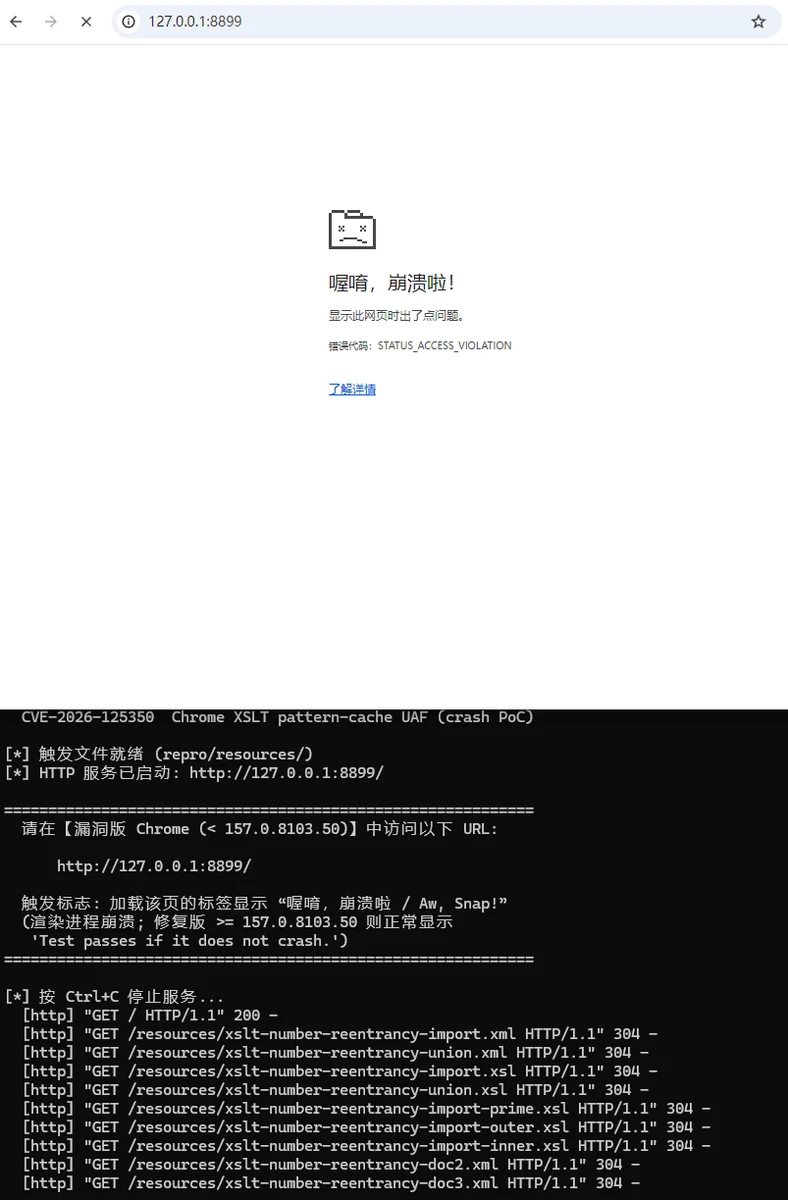 tjt001/cve-2026-125350-poc
Google Chrome XSLT pattern-cache Use-After-Free (CVE-2026-125350) crash PoC — affected < 157.0.8103.50
 zeetee1235/cve-2026-124040
Proof-of-concept and analysis for CVE-2026-124040, a CivetWeb HTTP/2 HPACK header-name corruption via use-after-free that bypasses literal-header…
 rwmicro/cve-2022-23943
Exploit notes and proof-of-concept material for CVE-2022-23943, a mod_sed buffer overflow in Apache HTTP Server 2.4.0-2.4.52, with prerequisites and…
 tc4dy/cve-2026-21589-poc-exploit
Exploit and safe-check toolkit for CVE-2026-21589, an unauthenticated path traversal in Atlassian Data Center: WEB-INF file read, credential…
 aureels/cve-2026-19803
Printcart <= 2.13.2 Unauthenticated File Upload
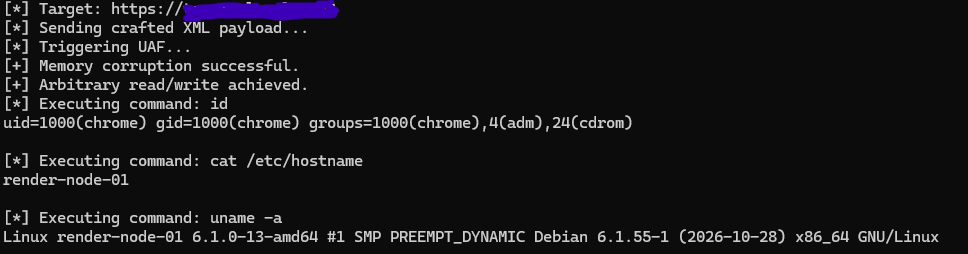 frostmoon39206/cve-2026-125350-poc
Technical analysis and skeleton PoC for CVE-2026-125350 (Chrome XML UAF)
 capivara-research/cve-2026-124576
Bilingual analysis and safe PoC for CVE-2026-124576, a BeikeShop PayPal payment bypass and guest-order IDOR, with source checks, offline logic model,…
 iam-s21-caece/poc-cve-2026-33871
Proof-of-concept Python scripts demonstrating a denial-of-service vulnerability in Keycloak 20.0.3, with configurable targets and iterative attack…
 3jee/cve-2026-120491
Python proof-of-concept for CVE-2026-120491, a stored XSS in Wing FTP Server before 8.2.6 where a crafted nowpath value forges a connection ID…
 worthes/cve-2026-119977-wordpress-upgrade-rce-bypasses-7.1.4
Multi-threaded PoC exploiting CVE-2026-119977, a TOCTOU race in WordPress core upgrade staging paths that yields unauthenticated remote code…