 tjt001/cve-2026-125350-poc
Google Chrome XSLT pattern-cache Use-After-Free (CVE-2026-125350) crash PoC — affected < 157.0.8103.50

| Attribute | Information |
|---|---|
| CVE | CVE-2026-125350 / EUVD-2026-121390 |
| Type | Use After Free (CWE-416) |
| Component | libxslt pattern.c — xsltTestCompMatchDirect |
| Affected versions | Google Chrome < 157.0.8103.50 |
| Fixed version | 157.0.8103.50 |
| Fix CL | 61cab3f7 / M157 cherry-pick 049750111b1e |
| Bug | crbug.com/582442907 |
Before calling xmlXPathEval, libxslt's xsltTestCompMatchDirect reads the node-set pointer from the pattern
match cache slot. When the count predicate of xsl:number references a lazily evaluated
global variable, and that variable's value in turn executes xsl:number, the evaluation process re-enters the same cache slot and
frees/replaces the cached object; after the outer call returns, it frees again using the stale pointer read before evaluation →
double free / use-after-free → renderer process memory corruption.
The fix is only 9 lines: after evaluation completes, re-read the cache slot pointer before freeing.
| Content | Description |
|---|---|
poc.py | Crash PoC: starts a local HTTP service and prints the trigger URL, which the user manually visits in the target browser |
repro/ | Official regression test (included with the fix CL, i.e., the official trigger files): test page + 9 XML/XSLT files |
chrome-vulnerable-157.0.8103.39/ | |
crash-renderer-157.0.8103.39.dmp |
# Zero dependencies, pure Python standard library
python poc.py                # start service (default port 8899) and print trigger URL
python poc.py --port 9999    # custom port
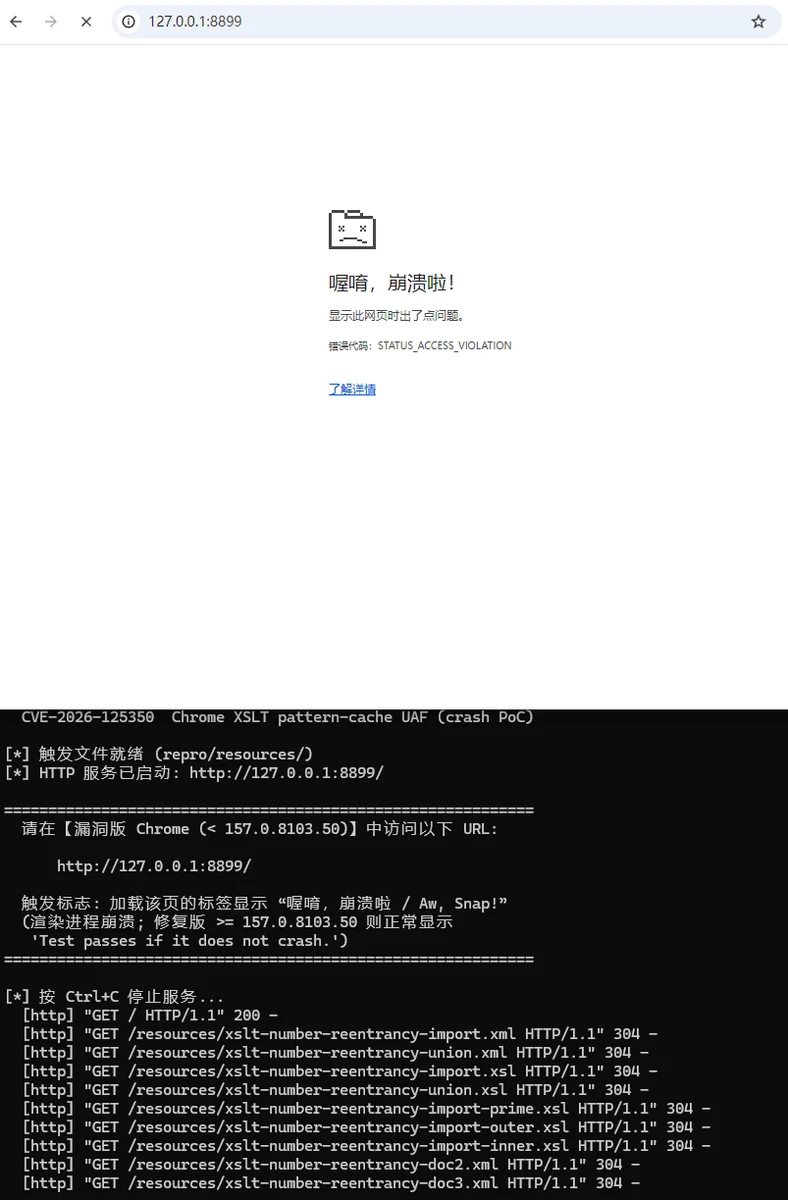
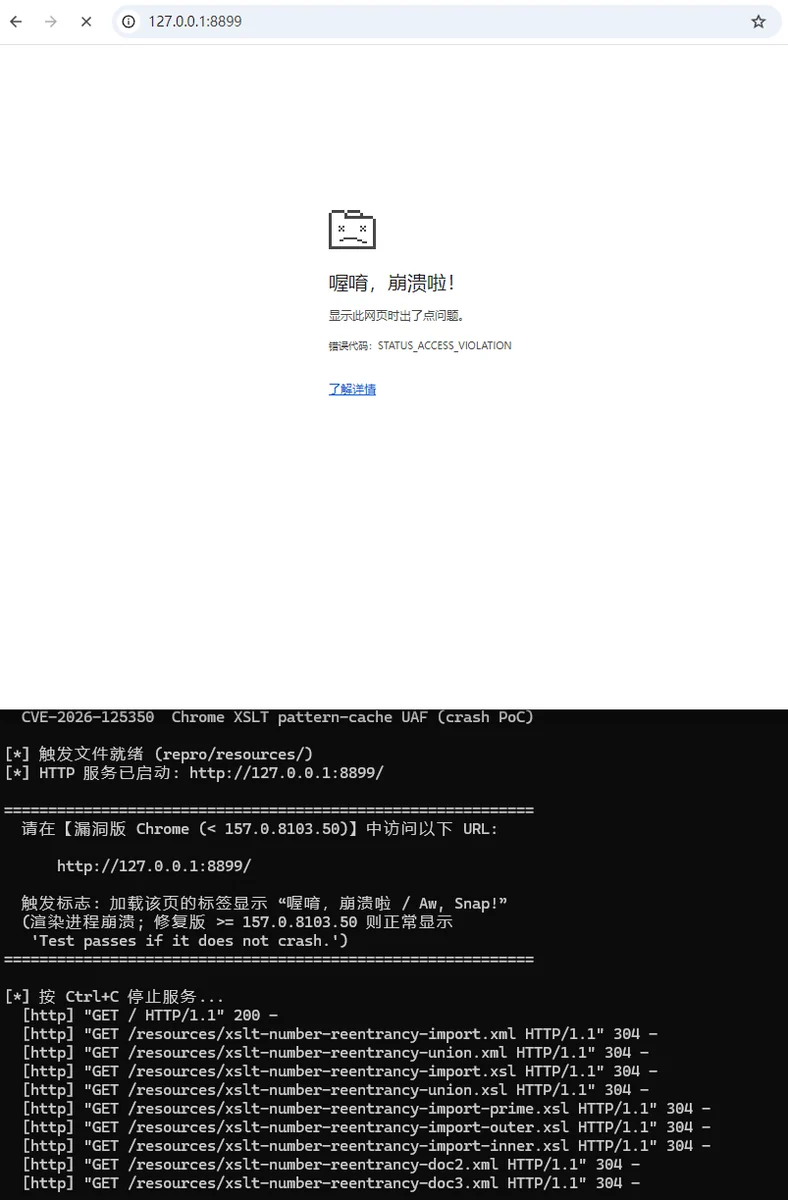
Flow: start a local HTTP service → print the trigger URL http://127.0.0.1:8899/ →
the user manually visits it in the target browser (vulnerable Chrome version).
document() requires HTTP delivery;
opening directly via file:// does not work)Ctrl+C stop, it counts the number of times the trigger XML was delivered in this sessionDetermination:
| Symptom | Conclusion |
|---|---|
| Tab shows "Aw, Snap!" | Renderer process crash → Affected (< 157.0.8103.50) |
| Normally displays "Test passes if it does not crash." | Fixed (≥ 157.0.8103.50) |
| Version | Result |
|---|---|
| 157.0.8103.39 (vulnerable version, manually visit trigger URL) | Tab crashes, renderer process Crashpad dump generated (stably reproduced multiple times) |
| 157.0.8103.51 (fixed version) | No crash, normally displays test passed |
For authorized security research and educational purposes only.






