

cve-2026-41940-PoC
 yasouxken/cve-2026-41940-poc
Python PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
authenticationcommand-and-controlexploitation+7
yasouxken/cve-2026-41940-pocPython PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
 ledksv/monitorsfour
HackTheBox MonitorsFour walkthrough covering credential leak, CVE-2025-24367 Cacti RCE, and CVE-2025-9074 Docker Desktop API container escape to root.
 ledksv/wingdata
HackTheBox Wingdata walkthrough covering WingFTP CVE-2025-47812 command injection for initial access and tar path traversal sudo privilege escalation…
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 r3fr4kt/devvortex
HackTheBox Devvortex walkthrough covering subdomain fuzzing, Joomla API enumeration, template-based web shell, bcrypt hash cracking, and Apport-CLI…
 hunt-benito/the-callback-that-outlived-the-page-cve-2026-78997-uc-browser-android-universal-xss
PoC for CVE-2026-78997, a Universal XSS in UC Browser for Android. Includes a crafted URL builder, a callback-dispatch oracle, and Frida hooks to…
 hainhc/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…
 0xgh057r3c0n/cve-2026-41940
cPanel & WHM - Authentication Bypass via Session-File CRLF Injection
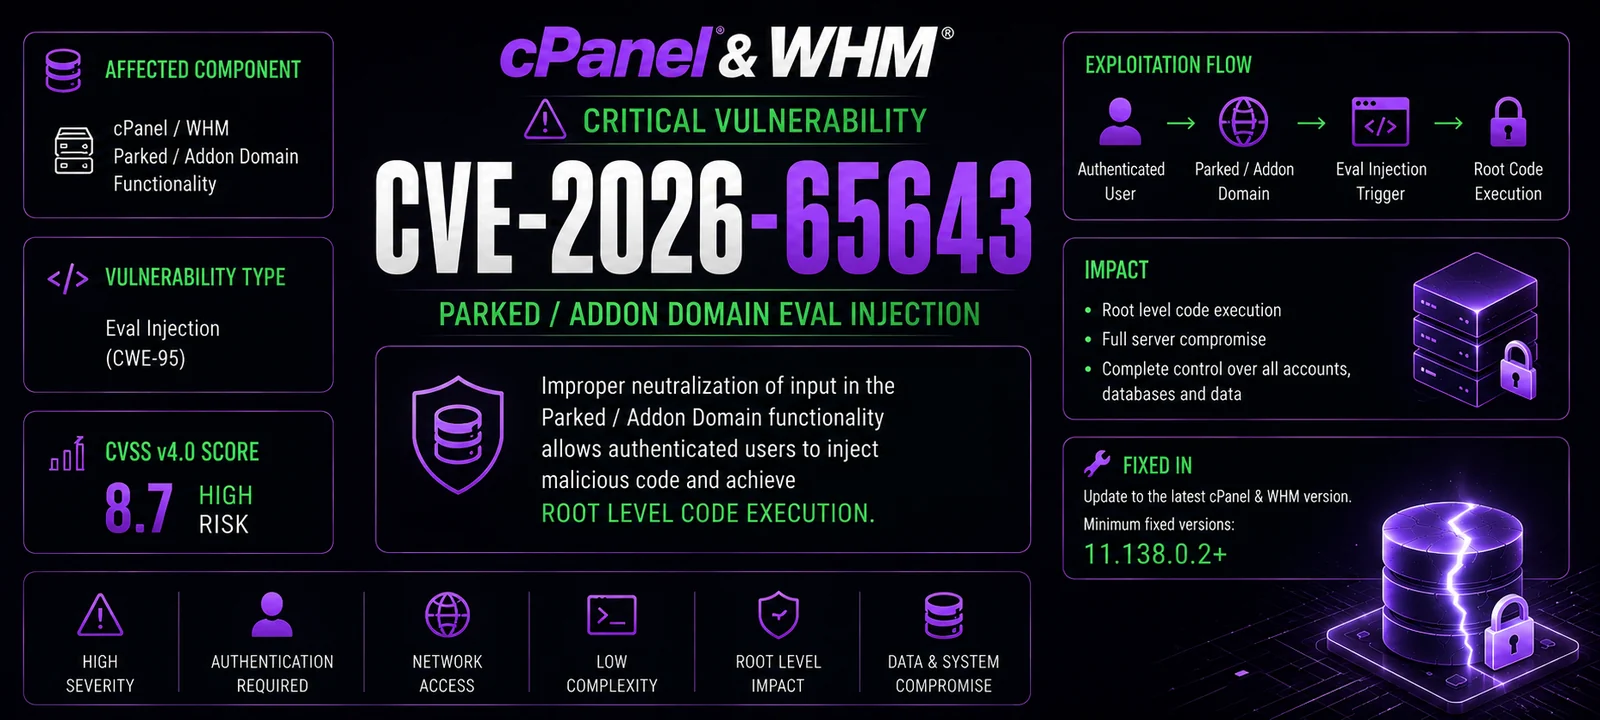 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
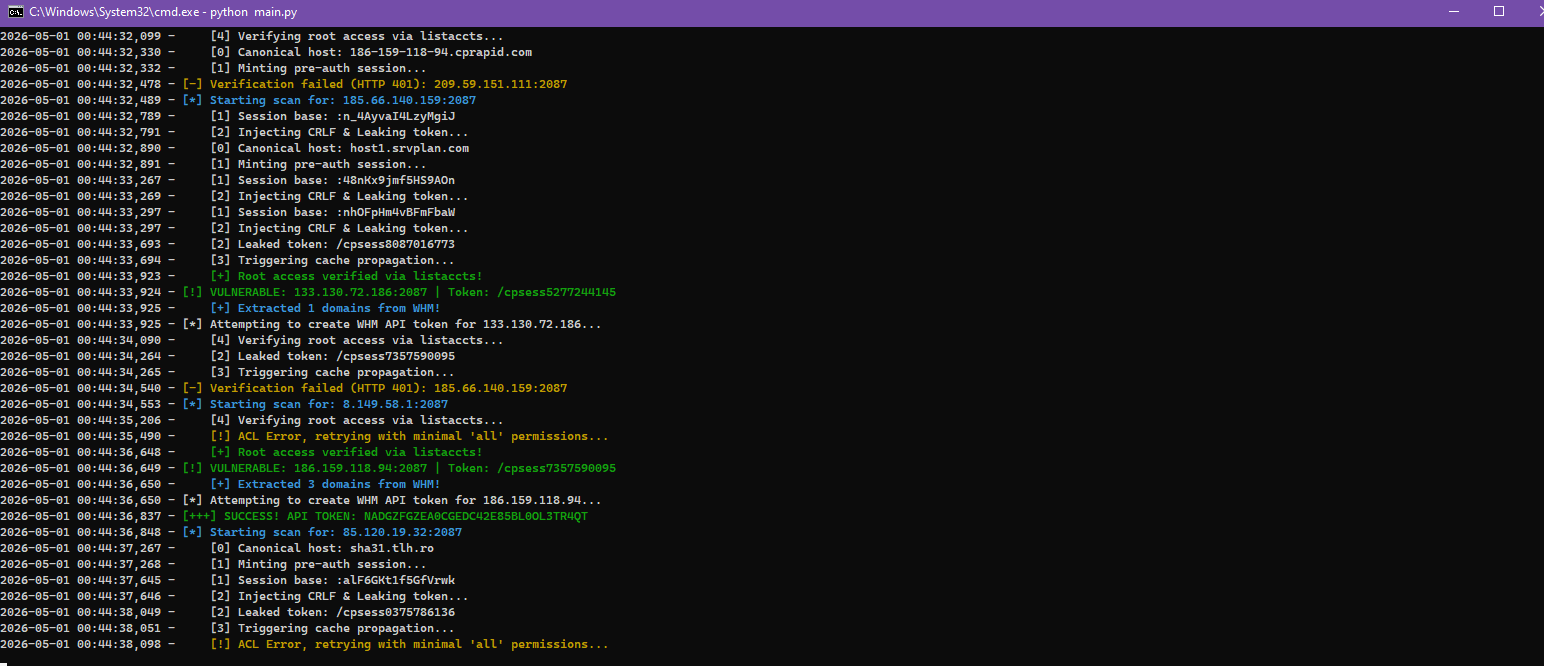 merdw/cpanel-cve-2026-41940-scanner
Advanced cPanel & WHM Security Scanner for CVE-2026-41940. with mass Shodan discovery
 nu113d/cve-2024-12856
An exploit for Four-Faith routers to get a reverse shell
 fcjaviergarcia/cve-2026-23744-poc
Proof of Concept (PoC) exploit for CVE-2026-23744, a vulnerability affecting MCPJam Inspector that allows remote command execution (RCE) through…
 dzmind2312/mass-cve-2026-23550-exploit
Multi-threaded Python scanner for CVE-2026-23550, detecting unauthenticated admin takeover in WordPress Modular DS plugin with full wp-admin…
 cypher-21/cve-2026-23520
Proof-of-concept exploit for CVE-2026-23520, a command injection vulnerability in Arcane's updater service, enabling remote code execution via…
 morphykutay/cve-2025-4123-exploit
Proof-of-concept tool that sends a crafted payload to a target and detects open redirect vulnerabilities by inspecting 301/302 responses and Location…
 selecthch/cve-2026-41551
Proof-of-concept exploit for CVE-2026-41551, a path traversal vulnerability in Siemens ROS# file_server, demonstrating remote file read via crafted…
 filipegaudard/cve-2026-33149-poc
Proof-of-concept exploit for CVE-2026-33149, a Host header injection in Tandoor Recipes that enables invite link poisoning and cache poisoning.…
 adityabhatt3010/cve-2026-27579-cors-misconfiguration-leading-to-authenticated-data-exposure
CVE-2026-27579 - CORS Misconfiguration – Arbitrary Origin with Credentials → Authenticated Cross-Origin Account Data Exposure