
 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning, plus a non-intrusive verifier for detection and auditing.



** ETHICAL USE ONLY – AUTHORIZED SECURITY TESTING**
This repository provides tools for authorized security professionals, blue teams, and penetration testers only.
Unauthorized access to computer systems is illegal under CFAA (US), Computer Misuse Act (UK), TCK 243/244 (Turkey), and similar laws worldwide.
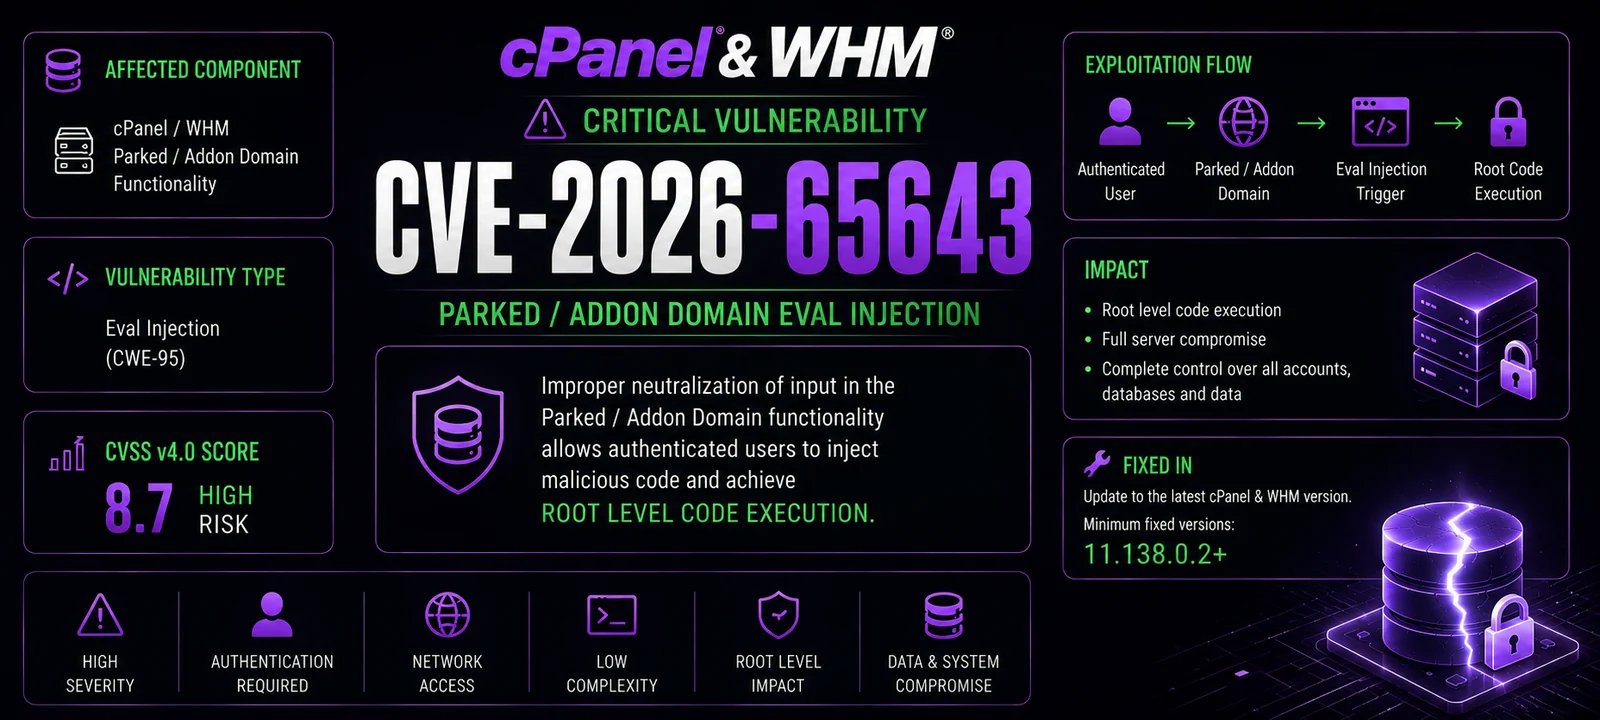
CVE‑2026‑65643 is a critical command injection vulnerability in cPanel & WHM versions 11.x that allows an authenticated cPanel user to execute arbitrary system commands with root privileges via the domain parking functionality.
`).| Tool | Purpose | Intended User |
|---|---|---|
exploit.py | Full weaponized toolkit with reverse shell, webshell, persistence, file read/write, root password change, mass scanning, Tor support, and OPSEC features. | Red teams / authorized pentesters |
verifier.py | Non‑intrusive vulnerability checker that detects cPanel version, validates injection, and assesses risk without executing any malicious payload. Generates detailed reports. | Blue teams / security auditors |
| Feature | exploit.py | verifier.py |
|---|---|---|
| Vulnerability detection | [+] | [+] |
| Version detection (4 endpoints) | [+] | [+] |
| Command injection | [+] | [-] |
| Reverse shell | [+] | [-] |
| WebShell upload | [+] | [-] |
| Persistence (cPanel user creation) | [+] | [-] |
| Root password change | [+] | [-] |
| File read/write | [+] | [-] |
| 4 injection methods (JSON/Form/CGI/API2) | [+] | [+] |
| Tor support (anonymity) | [+] | [-] |
| User‑Agent rotation (OPSEC) | [+] | [-] |
| Jitter (OPSEC) | [+] | [-] |
| Mass scanning (multi‑thread) | [+] | [-] |
| Interactive shell | [+] | [-] |
| Non‑intrusive (safe) mode | [-] | [+] |
| Timeline logging | [+] | [+] |
| HTML report | [+] | [-] |
| JSON report | [+] | [+] |
| Log cleanup (anti‑forensic) | [+] | [+] |
| Proxy support | [+] | [+] |
| Custom User‑Agent | [+] | [+] |
| SSL verification control | [+] | [+] |
| Scenario | Recommended Tool |
|---|---|
| Blue Team – verifying if your cPanel installation is vulnerable | verifier.py |
| Security Audit – non‑intrusive vulnerability assessment | verifier.py |
| Red Team – authorized penetration testing with full exploitation | exploit.py |
| Bug Bounty – responsible disclosure testing | verifier.py |
| Mass Scanning – checking multiple targets for vulnerability | exploit.py (detection only) |
| Incident Response – checking if systems are compromised | verifier.py |
git clone https://github.com/tc4dy/CVE-2026-65643-PoC-Toolkit
cd CVE-2026-65643-PoC-Toolkit
pip install -r requirements.txt
requests
urllib3
exploit.py Parameters| Parameter | Description |
|---|---|
-t, --target | Target cPanel URL (e.g. https://cpanel.example.com:2083) |
-l, --target-file | File containing list of targets (one per line) for mass scanning |
-u, --username | cPanel username |
-P, --password | cPanel password |
-p, --port | Override cPanel port (default from URL or 2083) |
--threads | Number of threads for multi‑target (default: 10) |
-o, --output | Save JSON report to file |
--html-report | Save HTML report to file |
-v, --verbose | Verbose output |
--proxy | HTTP/HTTPS proxy (e.g. http://127.0.0.1:8080) |
--tor | Route through Tor (localhost:9050) |
-ua, --user-agent | Custom User‑Agent |
--no-keep-alive | Do not keep session alive |
--delay | Delay between requests (default: 2.0s) |
--jitter | Random jitter (0‑1 sec) between requests (default: 0.5) |
--max-retries | Max retries (default: 5) |
--ssl-verify | Verify SSL certificates |
--timeout | Request timeout (default: 15s) |
--cmd | Execute a single command on the target |
--reverse-shell | Reverse shell IP:PORT |
--passwd | Change root password |
--adduser | Create cPanel user (USER DOMAIN PASSWORD) |
--read | Read a file |
--write | Write a file (specify path) |
--write-content | Content to write |
--cleanup | Clean logs and history after exploitation |
-i, --interactive | Interactive shell after exploitation |
--domain-suffix | Suffix for parked domain (default: exploit.local) |
verifier.py Parameters| Parameter | Description |
|---|---|
-t, --target | Target cPanel URL (e.g. https://cpanel.example.com:2083) |
-u, --username | cPanel username |
-P, --password | cPanel password |
-o, --output | Save JSON report to file |
-v, --verbose | Verbose output |
--proxy | HTTP/HTTPS proxy (e.g. http://127.0.0.1:8080) |
--tor | Route through Tor (localhost:9050) |
--ssl-verify | Verify SSL certificates |
--timeout | Request timeout (default: 15s) |
--cleanup | Clean logs after test |

