
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Pingpon-Exploit — Exploit for Mass Remote Code Execution on GPON home routers (CVE-2018-10562) obtained from Shodan. | Kitploit
Tools/GitHubGitHub/649/pingpon-exploit
OSINT (Open Source Intelligence)ReconnaissanceVulnerability AnalysisExploitationWeb Application ExploitationRemote Access Tool
GitHub649/pingpon-exploit

Pingpon-Exploit

Exploit for Mass Remote Code Execution on GPON home routers (CVE-2018-10562) obtained from Shodan.

View Repository
241198 years agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

PINGPON EXPLOIT

  • Author: @037

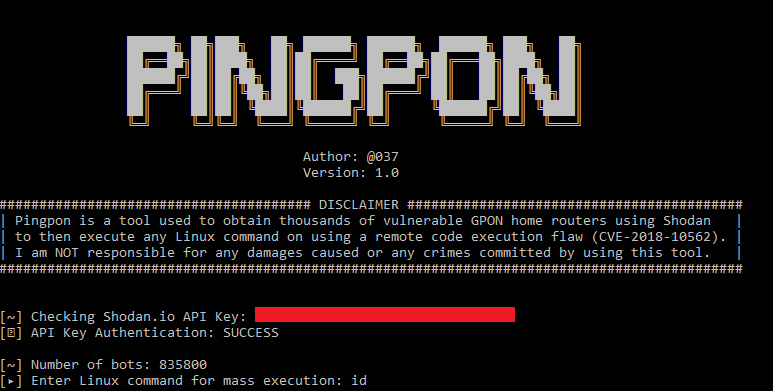
Pingpon is a tool used to obtain thousands of vulnerable GPON home routers using Shodan.io to then execute any Linux command on using a remote code execution flaw (CVE-2018-10562).

DISCLAIMER

I am NOT responsible for any damages caused or any crimes committed by using this tool.

Original Script: github.com/f3d0x0/GPON

Prerequisites

You're required to install Python 3.x

apt-get install python3

You also require to have the Shodan and Request modules installed

pip install shodan
pip install requests

Using Shodan API

This tool requires you to own an upgraded Shodan API

You may obtain one for free in Shodan if you sign up using a .edu email
alt text alt text

Download Tool