Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
XXStrike β€” XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications. | Kitploit
Tools/GitHubGitHub/anonmoty/xxstrike
Vulnerability ScannersWeb Vulnerability ScannersDynamic Code Analysis (DAST)Web Application ExploitationWAF BypassWeb SecurityFuzzingPenetration Testing
GitHubanonmoty/xxstrike

XXStrike

XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.

511002 months agoNot yet reviewed
View Repository
Share

XXStrike

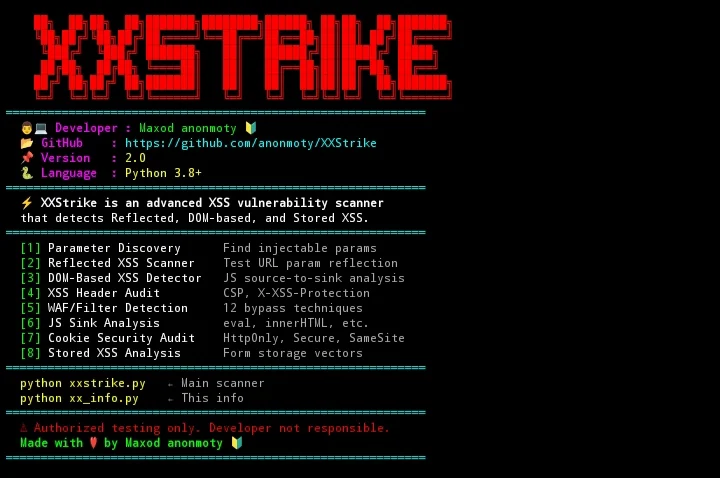
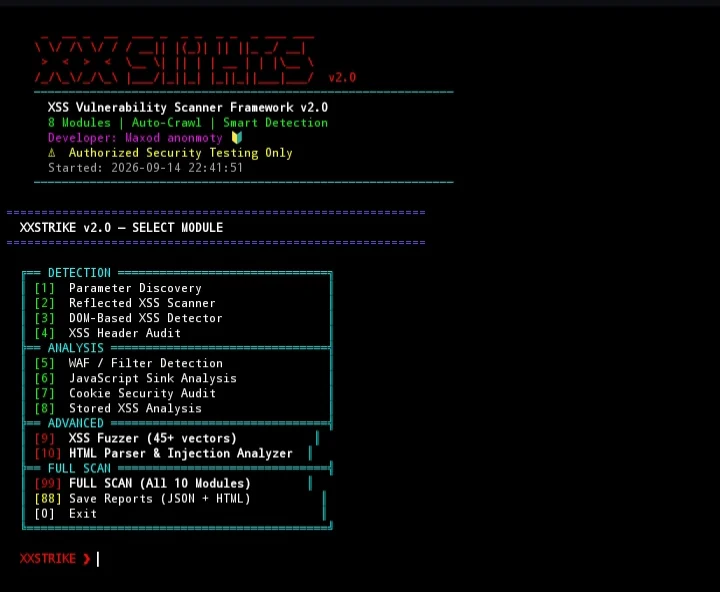
Image Image Image

cat << 'READMEEOF' > README.md
⚑ XXStrike v2.0

Next-Generation XSS (Cross-Site Scripting) Scanner & Fuzzing Suite

Developed by: Maxod anonmoty πŸ”°
Official Repository: https://github.com/anonmoty/XXStrike

Overview β€’ Key Features β€’ Modules β€’ Installation β€’ Usage β€’ Comparison β€’ Disclaimer


πŸ“Œ Overview

XXStrike is an advanced, multi-threaded Cross-Site Scripting (XSS) detection and vulnerability assessment framework engineered for penetration testers, bug bounty hunters, application security engineers, and DevSecOps professionals.

Designed as a modern, lightweight, and high-speed alternative to legacy XSS scanners, XXStrike combines intelligent parameter discovery, DOM source-to-sink tracking, context-aware payload fuzzing, and WAF/filter bypass heuristics into a single cohesive terminal interface.

Optimized natively for both Android (Termux) and standard Linux distributions.


πŸš€ Key Features

  • ⚑ Multi-Engine Detection: Identifies Reflected, DOM-based, and Potential Stored XSS vectors in single runs.
  • 🎯 Context-Aware Fuzzer: 45+ specialized payloads categorized into HTML body, attributes, scripts, comments, and event handlers.
  • πŸ›‘οΈ WAF & Filter Bypass Engine: Heuristic checks for 14+ firewalls (Cloudflare, AWS WAF, ModSecurity, Imperva, Sucuri).
  • πŸ”¬ Intelligent HTML & JS Parser: Deep syntax analysis for DOM sinks (innerHTML, document.write, eval(), postMessage).
  • πŸ”’ Security Headers & Cookie Audit: Evaluates CSP, X-XSS-Protection, HSTS, SameSite, HttpOnly, and Secure flags with letter grades (A+ to F).
  • πŸ“Š Automated Reporting: Generates clean, production-ready reports in HTML and JSON formats.
  • πŸ“± Termux Native: Zero external compilation required, 100% pure Python with minimal footprint.

🧩 Modules Breakdown (10 Powerful Modules)

#Module NameMethod & Capabilities
01Parameter DiscoveryUncovers query parameters, hidden form fields, and reflected arguments.
02Reflected XSS ScannerContextual injection verification with boundary-breaking tests.
03DOM-Based XSS DetectorJavaScript source-to-sink flow tracing and dangerous pattern extraction.
04XSS Header AuditEvaluates Content-Security-Policy (CSP), X-XSS-Protection, and X-Content-Type-Options.
05WAF / Filter DetectionTests 12 bypass transformations (Unicode, Hex, Double-encoding, mixed cases).
06JavaScript Sink AnalysisScans external scripts and inline blocks for insecure APIs.
07Cookie Security AuditChecks session token flags (HttpOnly, Secure, SameSite) for XSS-assisted exfiltration.
08Stored XSS Vector AnalyzerDetects persistent storage entry points (forms, textareas, comment fields).
09Advanced XSS Fuzzer45+ categorized vectors testing encoding, protocol handlers (javascript:, data:), and nested tags.
10HTML & Injection Point AnalyzerParses meta tags, sandboxed iframes, event attributes, and sanitizers (DOMPurify, Bleach).

πŸ“Š Comparison: XXStrike vs Legacy Tools

CapabilityLegacy XSStrikeGeneric Scanners⚑ XXStrike v2.0
Termux / Mobile Linux Support⚠️ Unstable❌ Noβœ… Native (100% Optimized)
Integrated DOM Sink TrackerPartial❌ Noβœ… Full Source-to-Sink
Cookie Flag & CSP Security Scoring❌ NoPartialβœ… Comprehensive (A+ to F)
Interactive CLI + Full Auto Scan❌ CLI Only❌ CLI Onlyβœ… Dual (Menu + Batch 99)
HTML / JSON Auto-Reporter❌ NoPartialβœ… Built-in Exporter
Active DevelopmentStaleVariesβœ… Active (2025 Release)

πŸ’» Installation

πŸ“± Android (Termux)

# Update repository lists
pkg update && pkg upgrade -y

# Install dependencies
pkg install python git -y

# Clone repository
git clone https://github.com/anonmoty/XXStrike.git

# Navigate to project directory
cd XXStrike

# Install required Python packages
pip install -r requirements.txt

# Launch XXStrike
python XSStrike.py

Download Tool

Most Popular

View all β†’

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurityβ€”where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools β†’