

Oihk-pentesting
 broskigx/oihk-pentesting
Autonomous multi-agent AI penetration-testing engine: a governed tool sandbox, an immutable evidence-and-validation gate, and a reproducible…
ai-securityeducationexploit-frameworks+7
4
broskigx/oihk-pentestingAutonomous multi-agent AI penetration-testing engine: a governed tool sandbox, an immutable evidence-and-validation gate, and a reproducible…
 simplifaisoul/osiris
Open Source Global Intelligence Platform - Real-Time OSINT Dashboard - A Palantir Alternative - …
 gillarchnganasan2735/cve-2026-41089-netlogon-rce-poc
Automate Netlogon CVE-2026-41089 validation and defensive testing through integrated AI security workflows, enabling rapid risk assessment and…
 yasouxken/cve-2026-41940-poc
Python PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
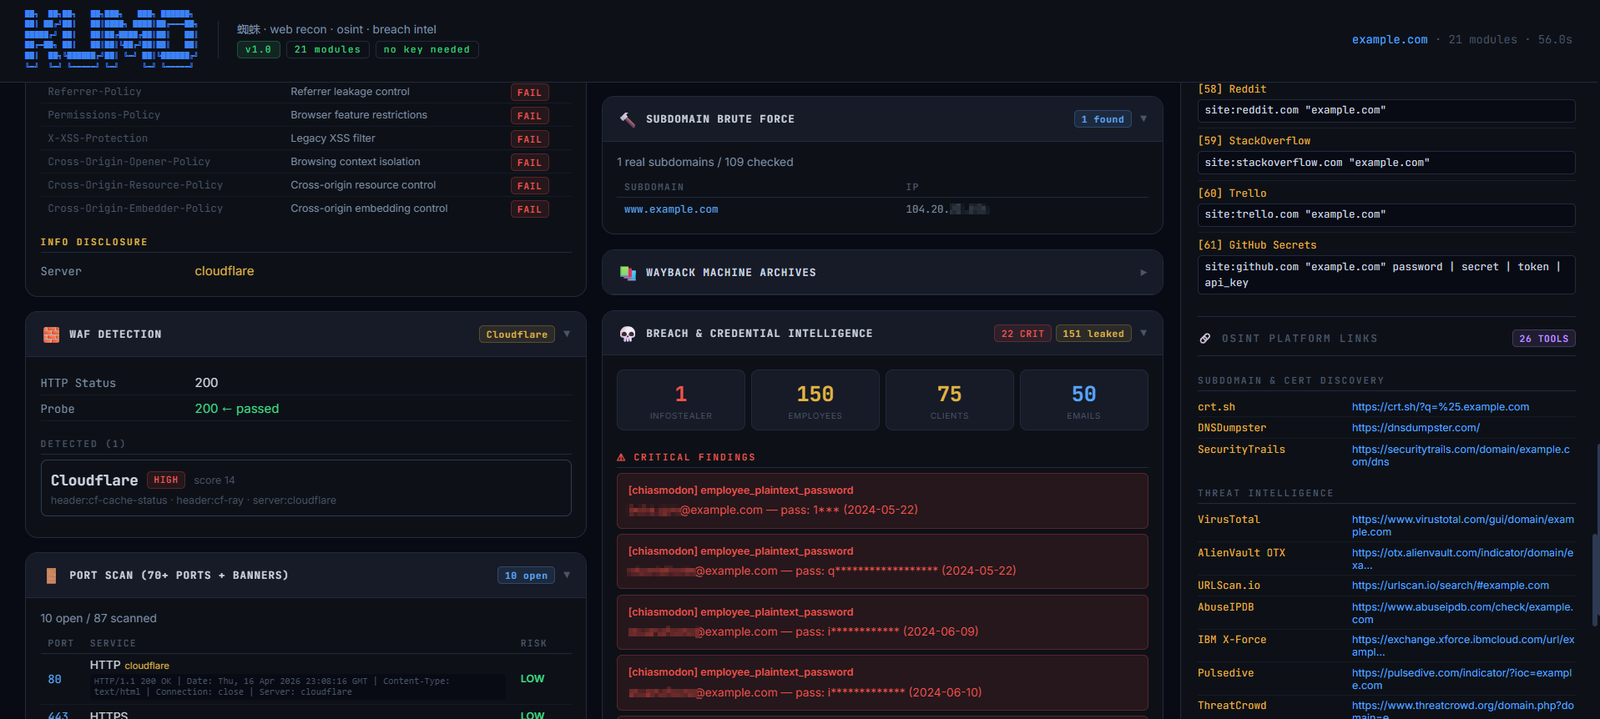 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
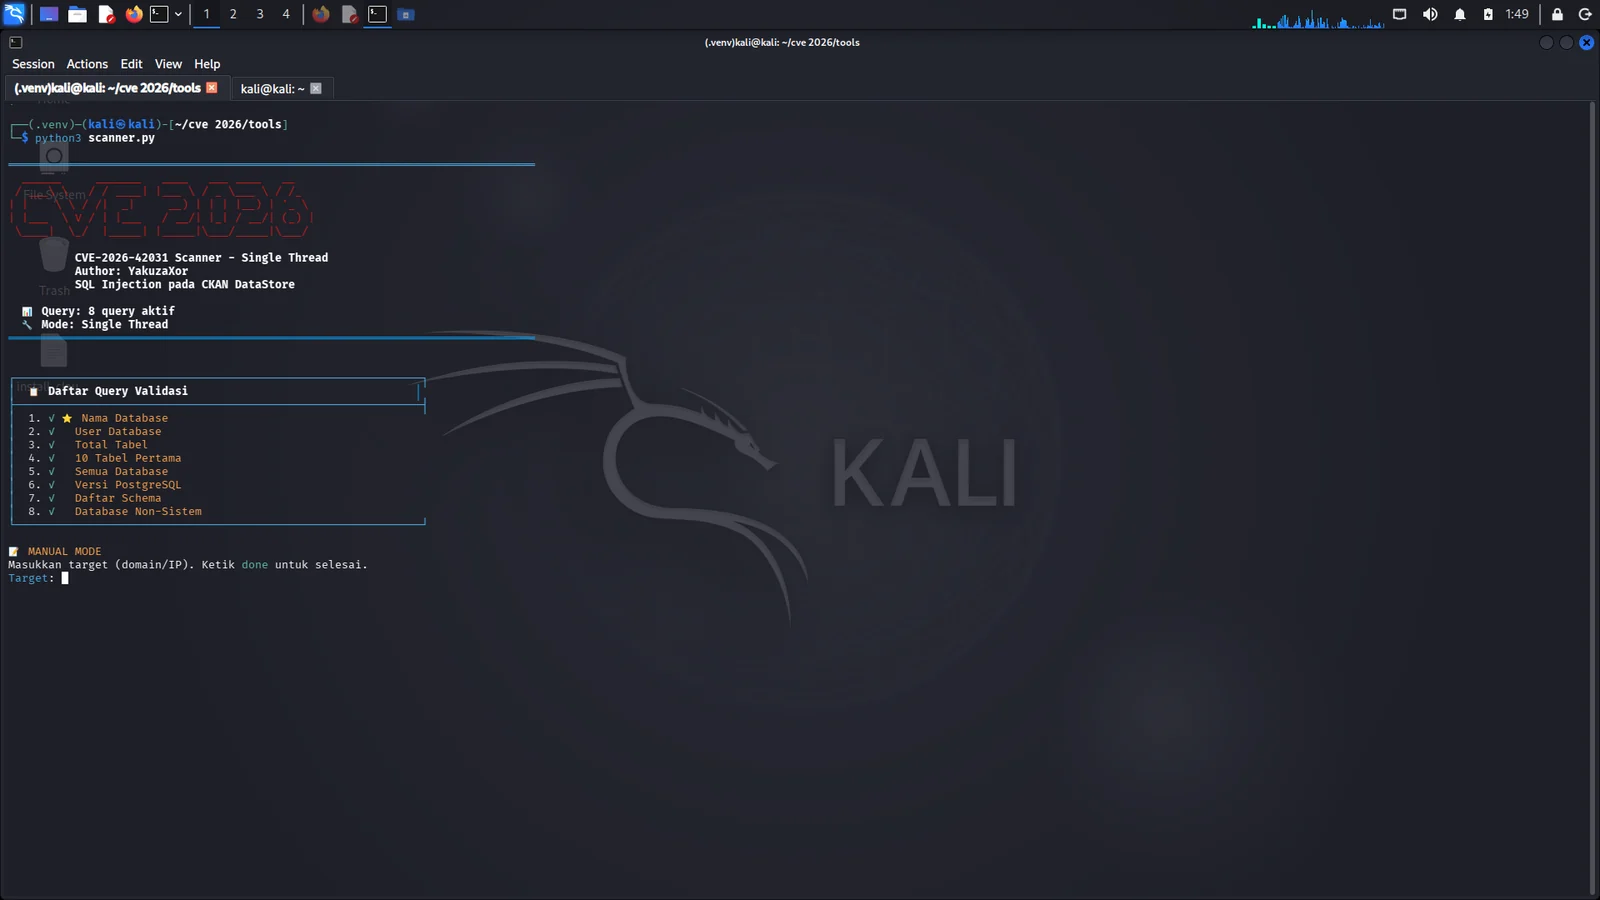 ddrvahandzo90-hue/cve-2026-42031-sql-injection-scanner
Automated SQL injection scanner for CKAN DataStore, detecting and validating CVE-2026-42031 with multi-target scanning, data dumping, and report…
 0xgh057r3c0n/cve-2026-41940
cPanel & WHM - Authentication Bypass via Session-File CRLF Injection
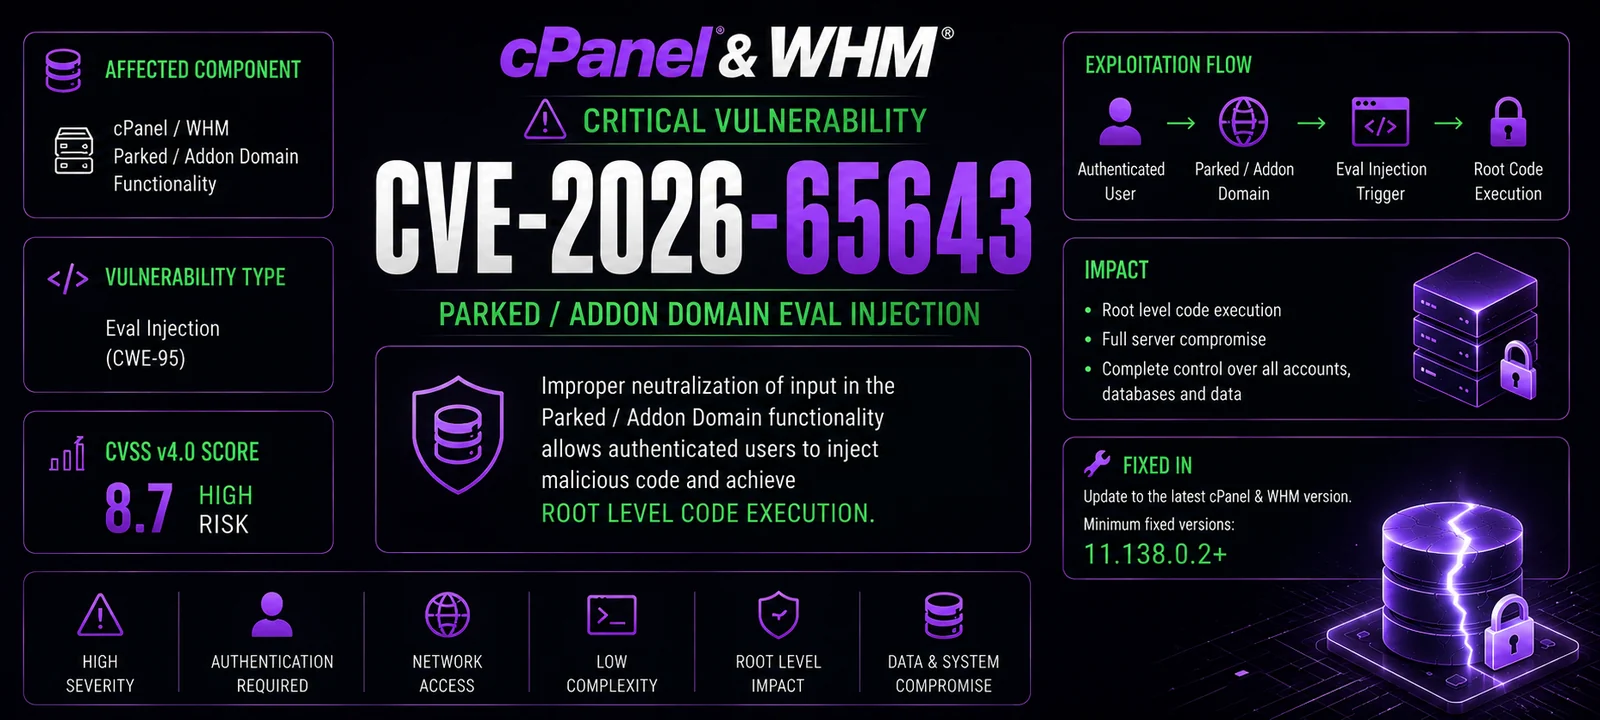 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
 virologi-info/mssharepoint-scanner
A scanner for CVE-2026-55040 and CVE-2026-63520, designed to determine whether the server is affected by these two CVEs.
 qassam-315/cve-2026-23918-elite-auditor
Elite reconnaissance script for auditing Apache's HTTP/2 stack against memory corruption (CVE-2026-23918). Features ALPN protocol forcing and…
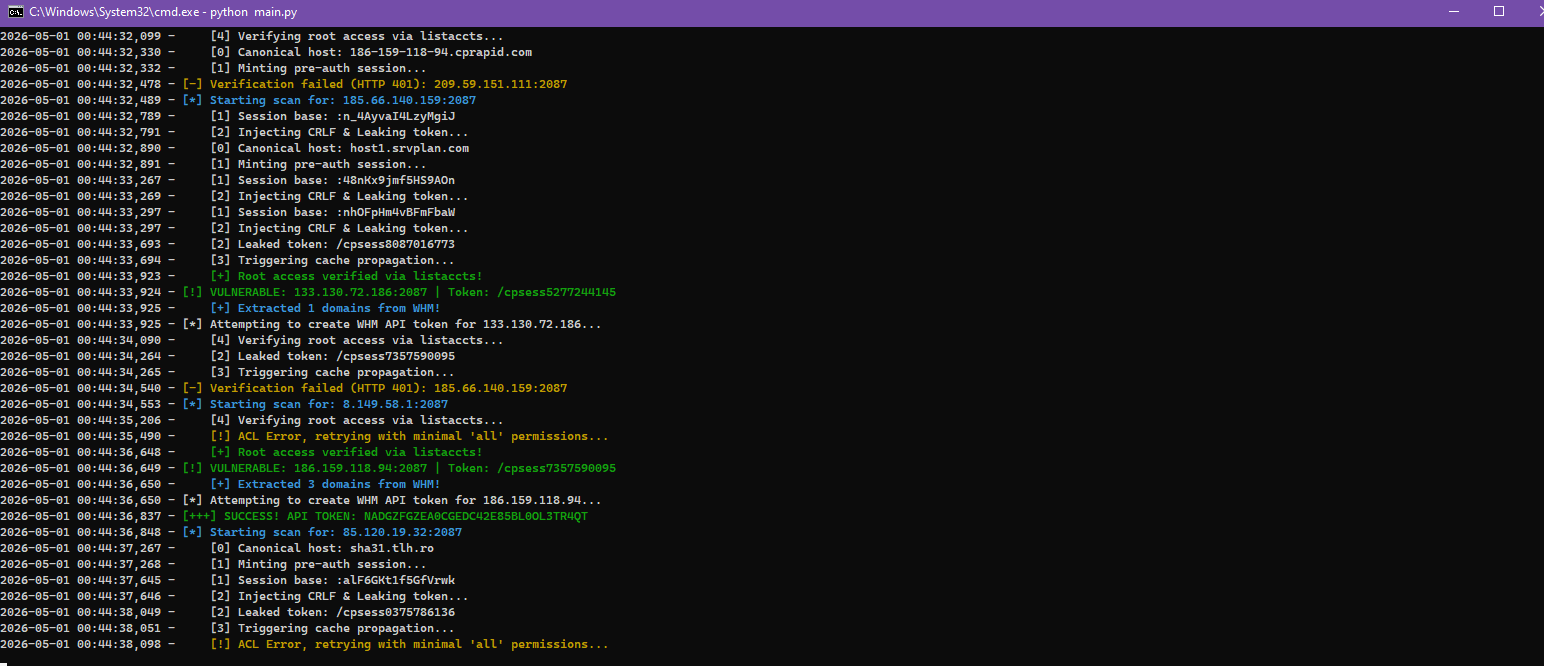 merdw/cpanel-cve-2026-41940-scanner
Advanced cPanel & WHM Security Scanner for CVE-2026-41940. with mass Shodan discovery
 mr-vill4in/log4j-fuzzer
Automated scanner for CVE-2021-44228 (Log4Shell) that tests single or multiple web targets for the vulnerability using remote callback servers.
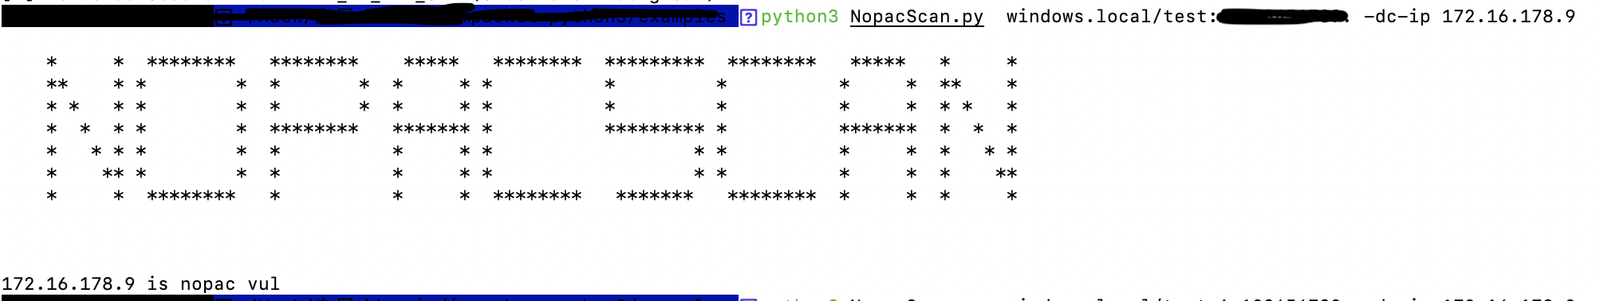 knightswd/nopacscan
Scans Active Directory domain controllers for CVE-2021-42287 and CVE-2021-42278 by querying DNS for all DCs and analyzing PAC structures for the 0x10…
 dzmind2312/mass-cve-2026-23550-exploit
Multi-threaded Python scanner for CVE-2026-23550, detecting unauthenticated admin takeover in WordPress Modular DS plugin with full wp-admin…
 danaug23/detect_cve-2026-25177
Production-safe scanner that detects CVE-2026-25177 (AD SPN Unicode Collision) exploitation on Active Directory Domain Controllers. Read-only.
 arnaudluti/ps-cve-2021-44228
Static detection of vulnerable log4j librairies on Windows servers, members of an AD domain.
 yassdev221608/cve-2024-6387_poc
Scans and exploits CVE-2024-6387 (regreSSHion) in OpenSSH servers. Features multi-threaded scanning, banner retrieval, grace time detection, and…