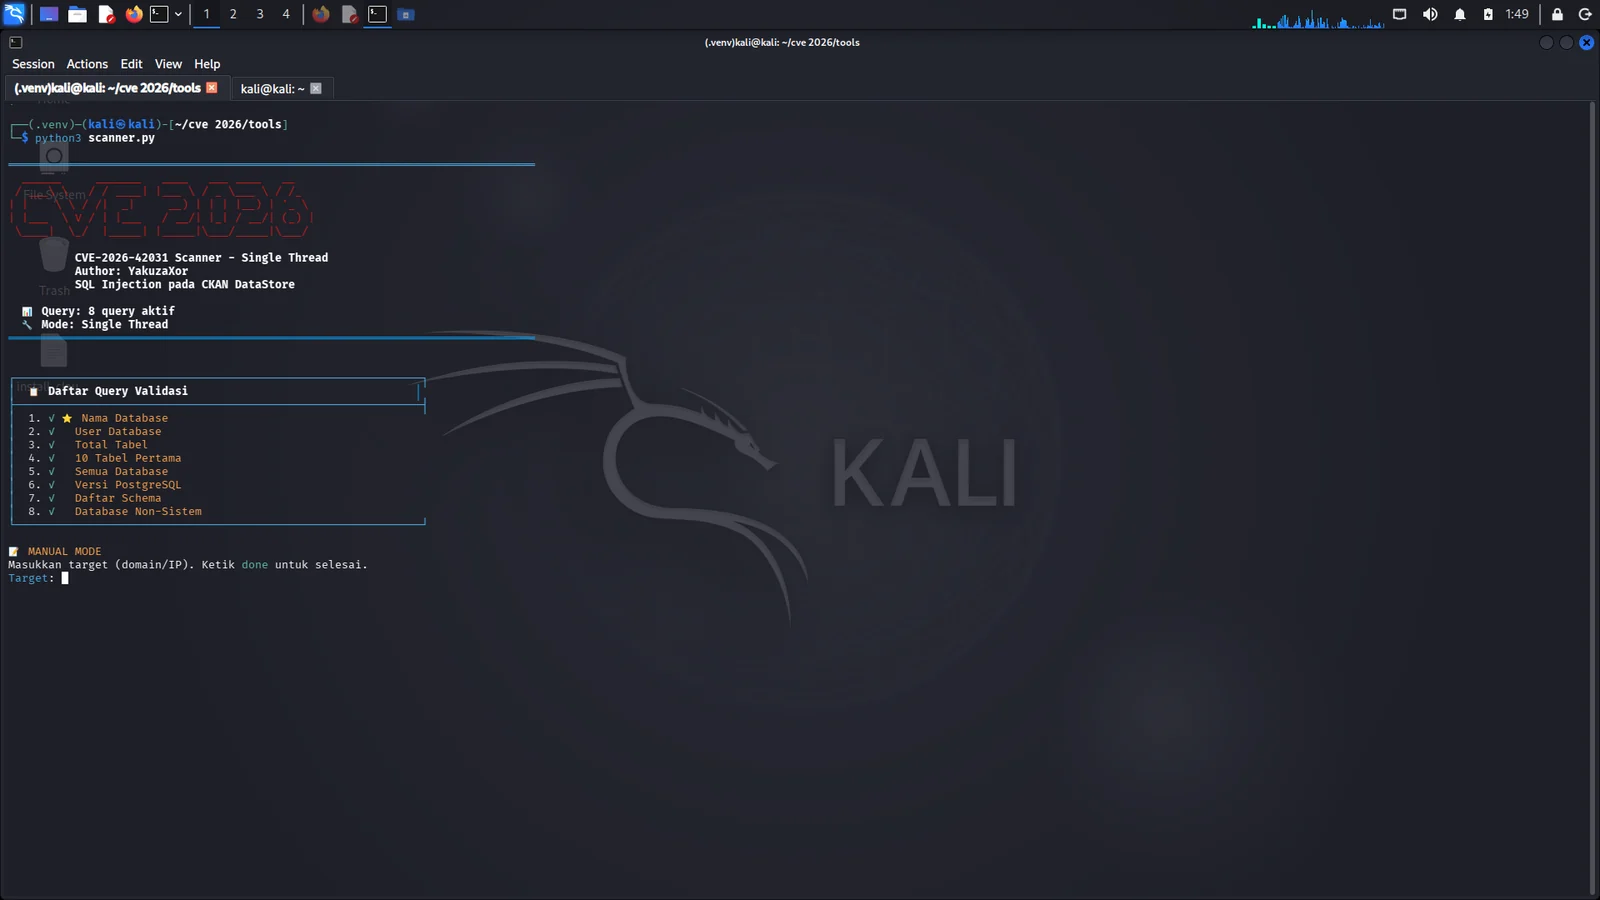
 ddrvahandzo90-hue/cve-2026-42031-sql-injection-scanner
Automated SQL injection scanner for CKAN DataStore, detecting and validating CVE-2026-42031 with multi-target scanning, data dumping, and report generation.

SQL Injection Scanner for CKAN DataStore
This tool is used to detect and validate the CVE-2026-42031 vulnerability (SQL Injection) on the CKAN DataStore platform.
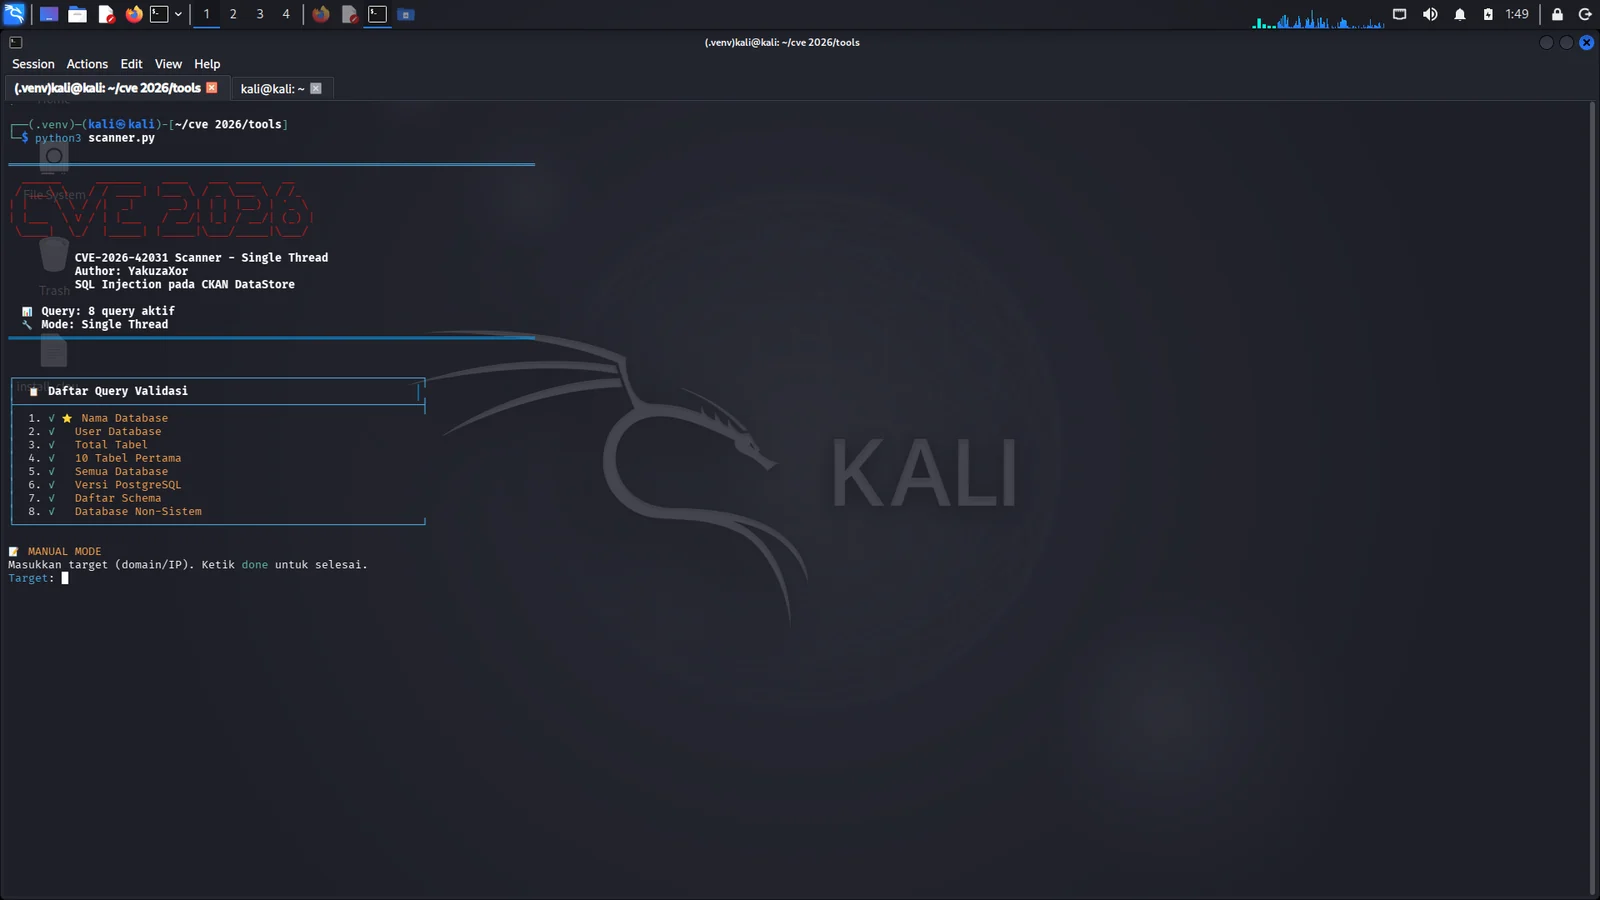
pip install -r requirements.txt

# Auto Mode (baca targets.txt)
python3 scanner.py

# Manual Mode (enter targets one by one)
python3 scanner.py

⚠️ Disclaimer

This tool is for educational purposes and legitimate security testing only. Use it only on systems for which you have written permission. The author is not responsible for any misuse.

📝 License

MIT License By YakuzoHaxor






