

zaproxy
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
android-securityapi-securityapi-security-testing+15
15.6k
zaproxy/zaproxyOpen-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
 checkmk1/checkmk_php2shell
Checkmk extension with an agent plug-in that inventories PHP binaries and Apache mod_php on Linux hosts and reports PHP2Shell…
 intuitem/ciso-assistant-community
GRC platform for risk management, compliance, and audit with 200+ frameworks, automatic control mapping, vulnerability management, and incident…
 avoliomattia/nginx-cve-2026-123007-cve-2026-123633
Shell-based proof-of-concept material for NGINX vulnerabilities CVE-2026-123007 and CVE-2026-123633, covering reproduction and verification of the…
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 llcforge/cve-2026-125350
Proof-of-concept trigger and detection notes for CVE-2026-125350, a use-after-free in Chrome's XML parser (CVSS 8.8, Chrome < 157.0.8103.50, CISA…
 llcforge/cve-2026-121810
Docker-based proof-of-concept for CVE-2026-121810, an nginx HTTP/3 (QUIC) use-after-free triggered by worker_connections exhaustion, with a Python…
 llcforge/cve-2026-125283
Python PoC for CVE-2026-125283, an nginx alias + try_files integer underflow triggered via map captures, with Docker lab, trigger variants, and…
 sfewer-r7/cve-2026-123007
Proof-of-concept scripts for CVE-2026-123007, an NGINX HTTP/2 integer underflow, including a minimal trigger and an exploit demonstrating…
 greenbone/openvas-scanner
This repository contains the scanner component for Greenbone Community Edition.
 future-architect/vuls
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
 patrowl/patrowlhears
PatrowlHears - Vulnerability Intelligence Center / Exploits
 al4n4n/cve-2026-125350
Archived pointer repository for CVE-2026-125350, a Chromium libxslt use-after-free; code, packet captures and Suricata/YARA detection rules now live…
 yozturk0/cve-2026-125440
Proof-of-concept and writeup for CVE-2026-125440, an unauthenticated shortcode injection in s2Member PayPal IPN handlers that can escalate to code…
 usama-hanif131/cve-2026-129254
Reflected XSS in Opixido OCMS admin/TUI/index.php (img parameter)
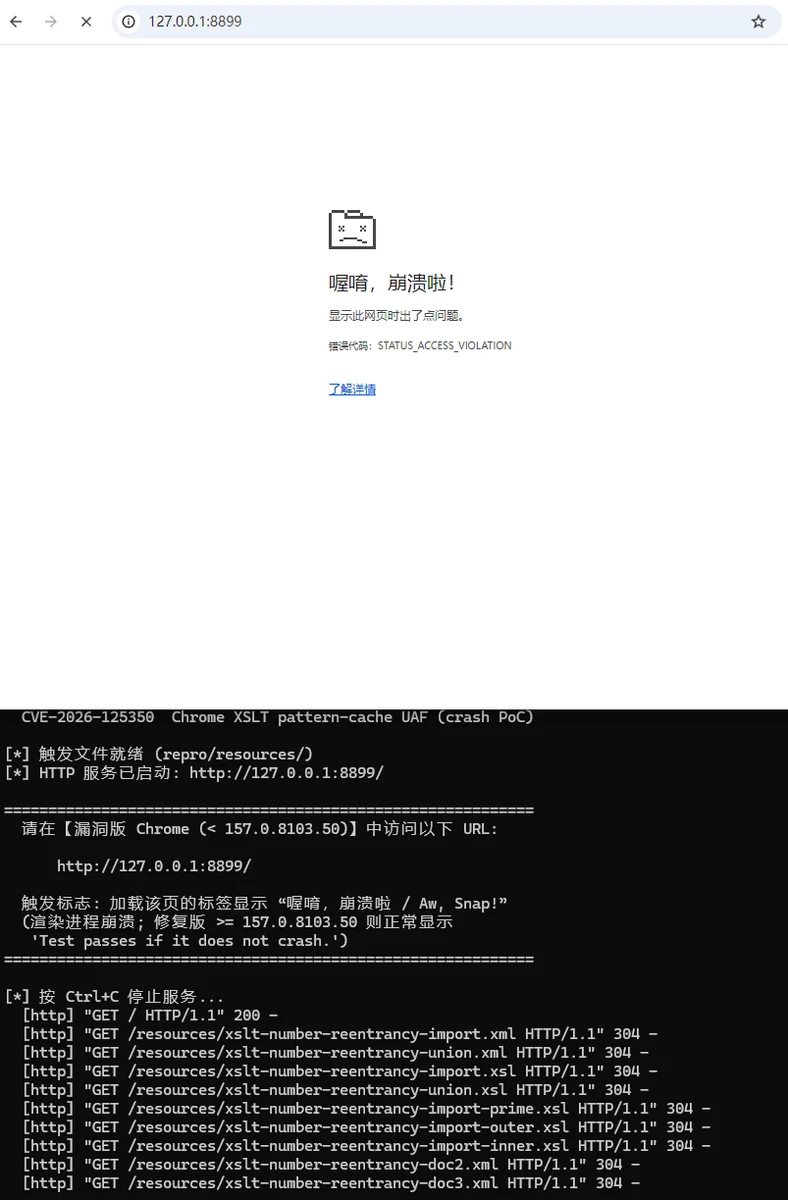 tjt001/cve-2026-125350-poc
Google Chrome XSLT pattern-cache Use-After-Free (CVE-2026-125350) crash PoC — affected < 157.0.8103.50