

capa
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ai-assisted-reversingbinary-analysiscode-analysis+10
6.1k
mandiant/capaRule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 jev-sec/jev-ids
Blazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
 thelightscope/thelightscope
TheLightScope
 corelight/ecs-logstash-mappings
Mapping Corelight or Zeek data to Elastic Common Schema logs
 corelight/ecs-mapping
Mapping Corelight or Zeek data to Elastic Common Schema fields
 neo23x0/process-watcher
A process monitoring tool that tries to detect exploitation
 wagga40/zircolite
A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs
 capesandbox/capesolo
Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
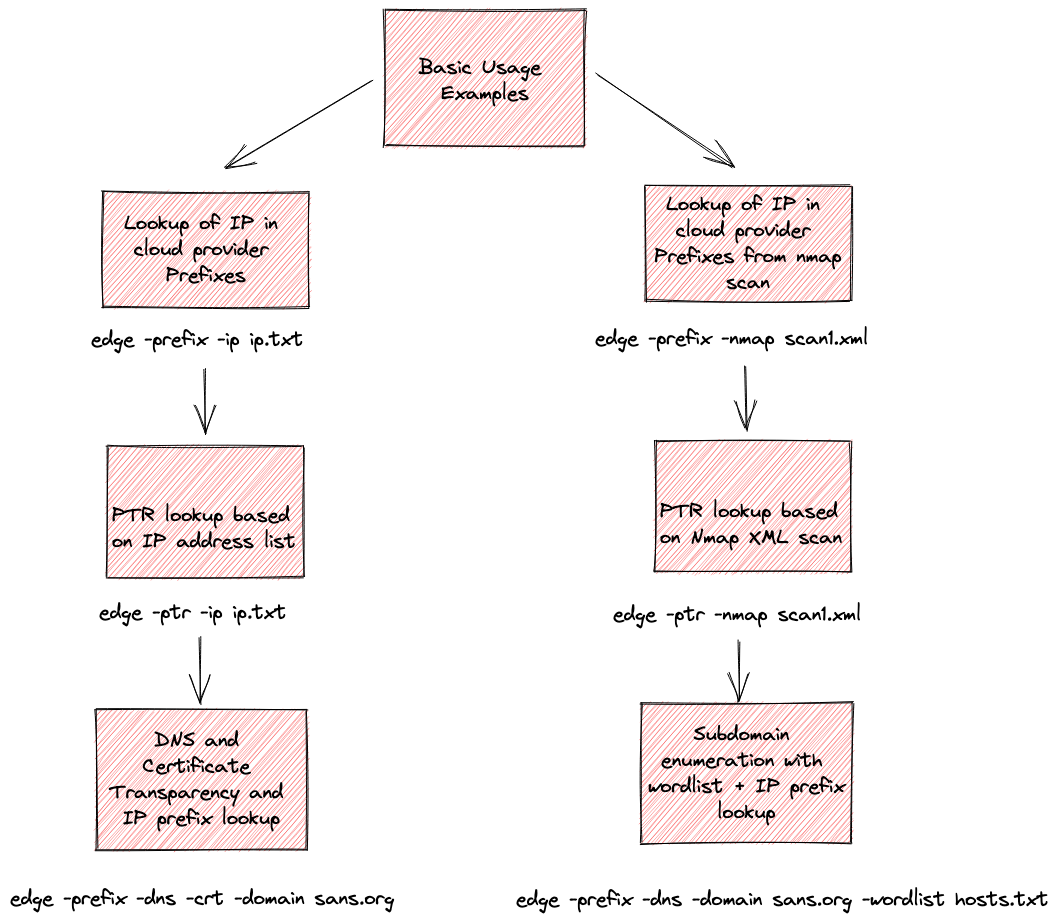 iknowjason/edge
Whois for the Cloud: Recon tool for cloud provider attribution. Supports AWS, Azure, Google, Cloudflare, and Digital Ocean.
 nullarray/intrec-pack
Intelligence and Reconnaissance Package/Bundle installer.
 initconf/cve-2017-5638_struts
Bro/Zeek script for detecting Apache Struts CVE-2017-5638 reconnaissance, compromise, and malware download tracking with automated IP extraction.