gitlab-cve-2026-85706-ioc

CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…

CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…

YARA signature and IOC database for my scanners and tools

Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…

Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.

Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.

Trust & Safety tools for working together to fight digital harms.

IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.

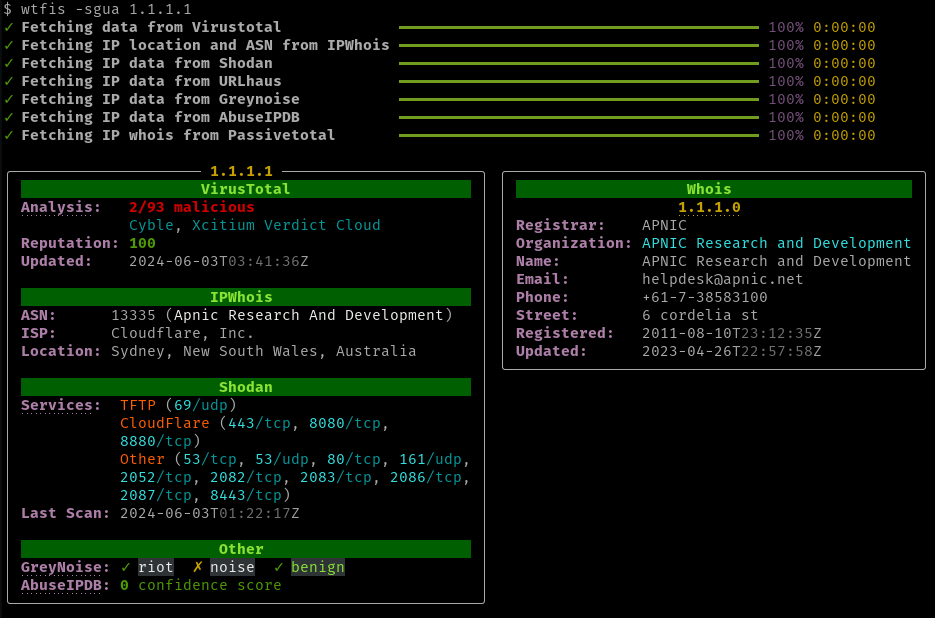
Automated security intelligence collector that queries public feeds and APIs for threat data on IPs, domains, URLs, hashes, and SSL fingerprints,…

Passive hostname, domain and IP lookup tool for non-robots

Curated Intelligence is working with analysts from around the world to provide useful information to organisations in Ukraine looking for additional…

STIX 2.1 collections of the MITRE ATT&CK knowledge base, providing adversary tactics and techniques for enterprise, mobile, and ICS threat…

Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…

A query aggregator for OSINT based threat hunting

Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…

Web interface for Suricata ruleset management, threat hunting, and rule tuning with multi-source feed aggregation, transformation, and activity…

Searches For Threat Hunting and Security Analytics