

cplt
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
ai-securitycommand-and-controlconfiguration-auditing+7
140
navikt/cpltSandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
 hashgraph-online/hol-guard
Open-source antivirus and firewall for AI agents: block risky tools, secret access, prompt injection, malicious packages, MCP servers, plugins, and…
 anthropics/oss-scanner
Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 nvidia/skillspector
Security scanner for AI agent skills. Detect vulnerabilities, malicious patterns, security risks, prompt injection, data exfiltration, and…
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
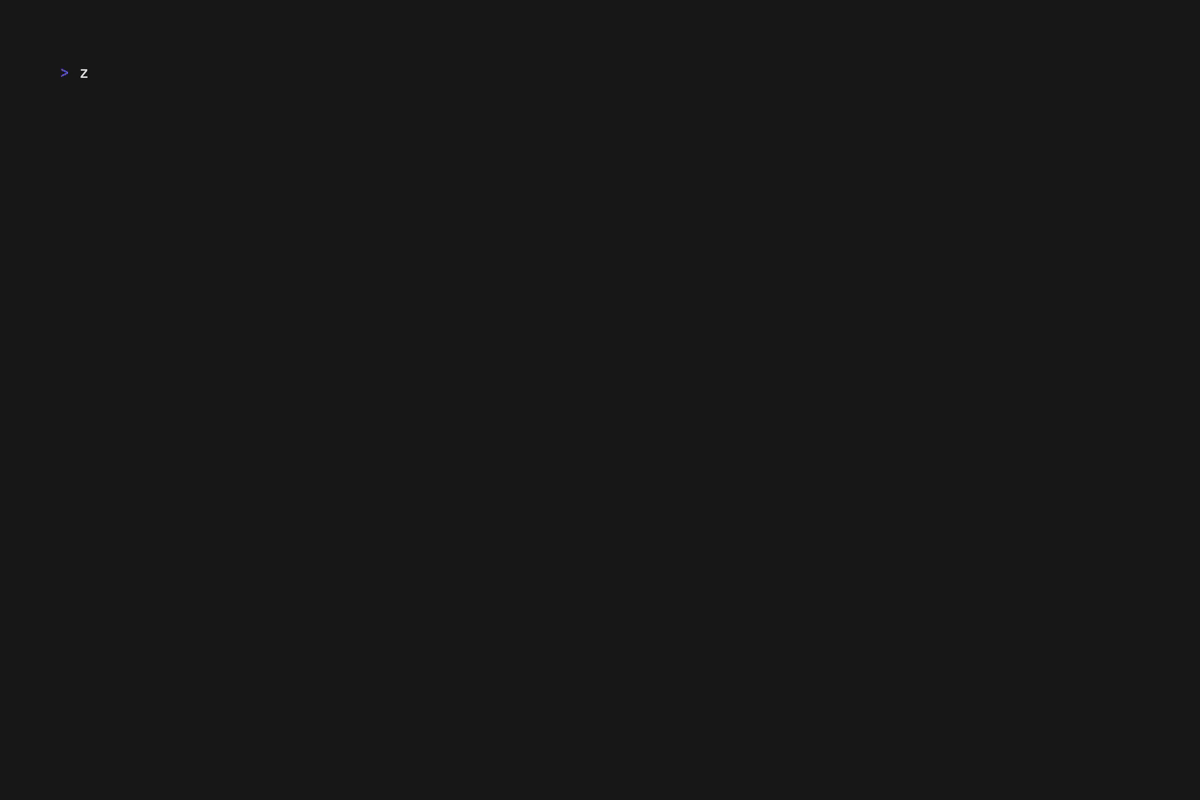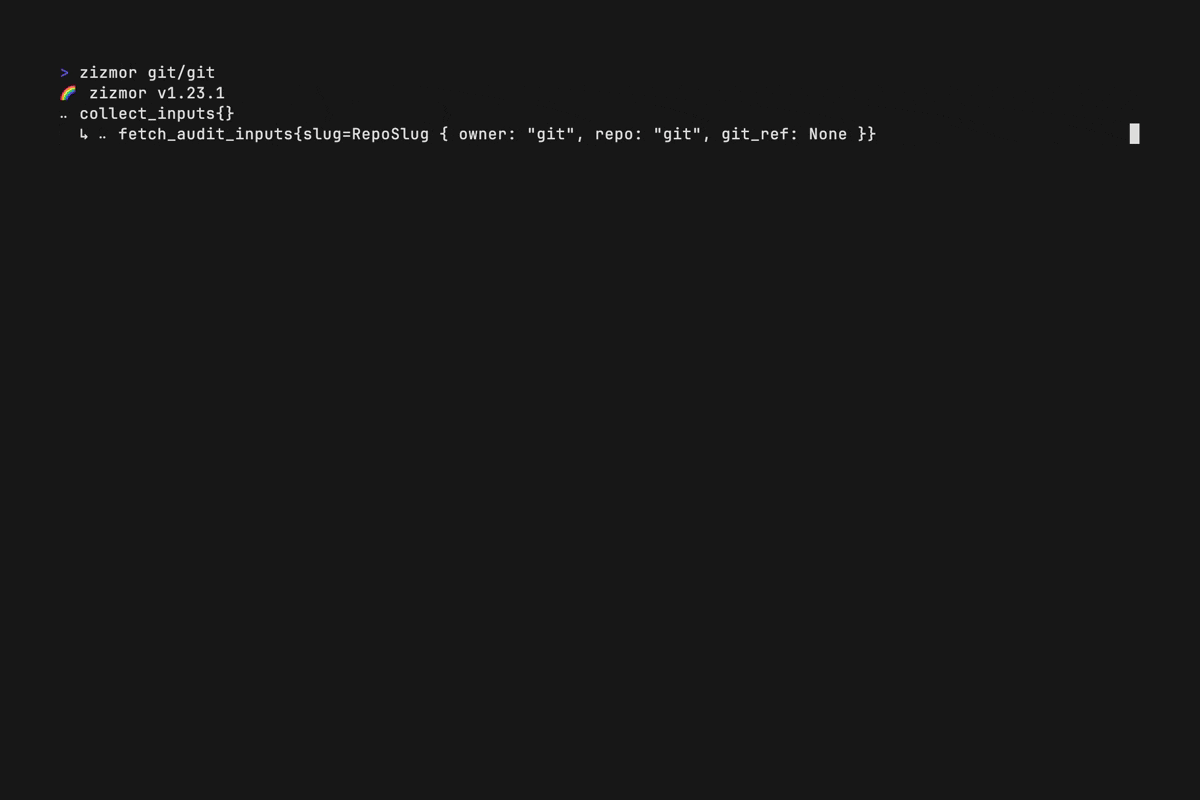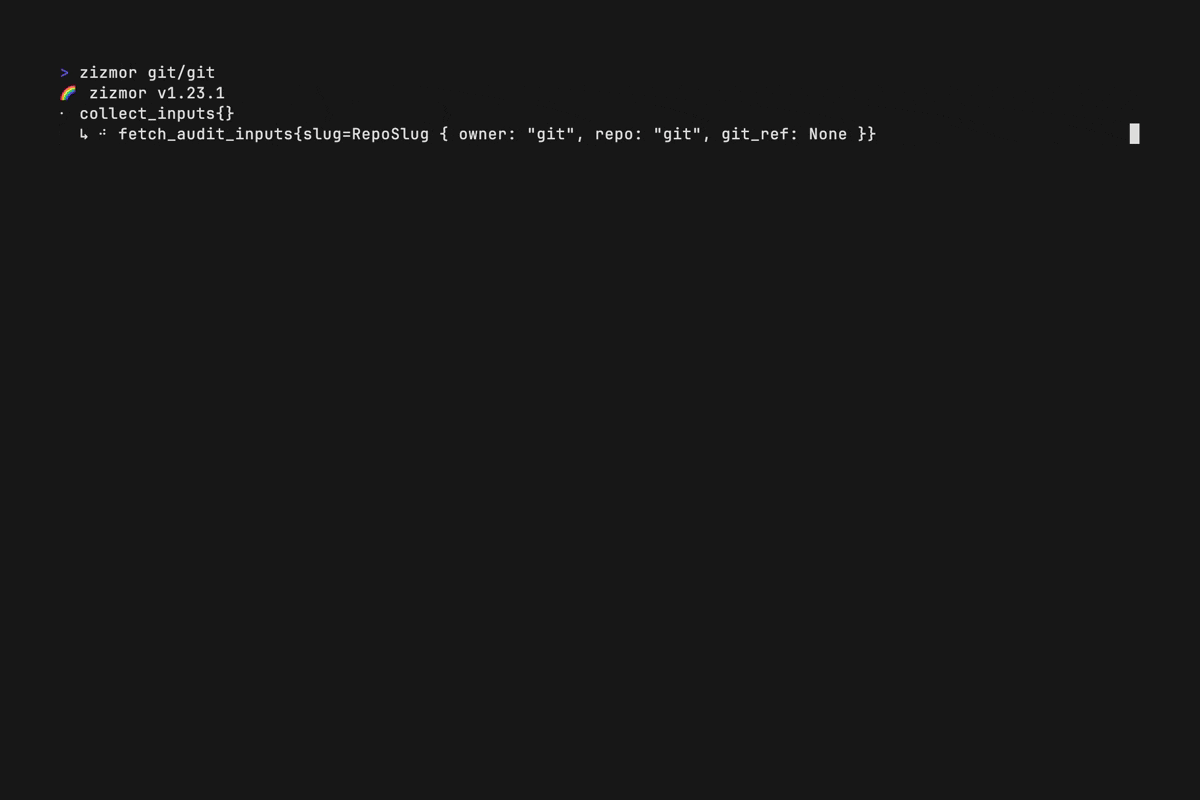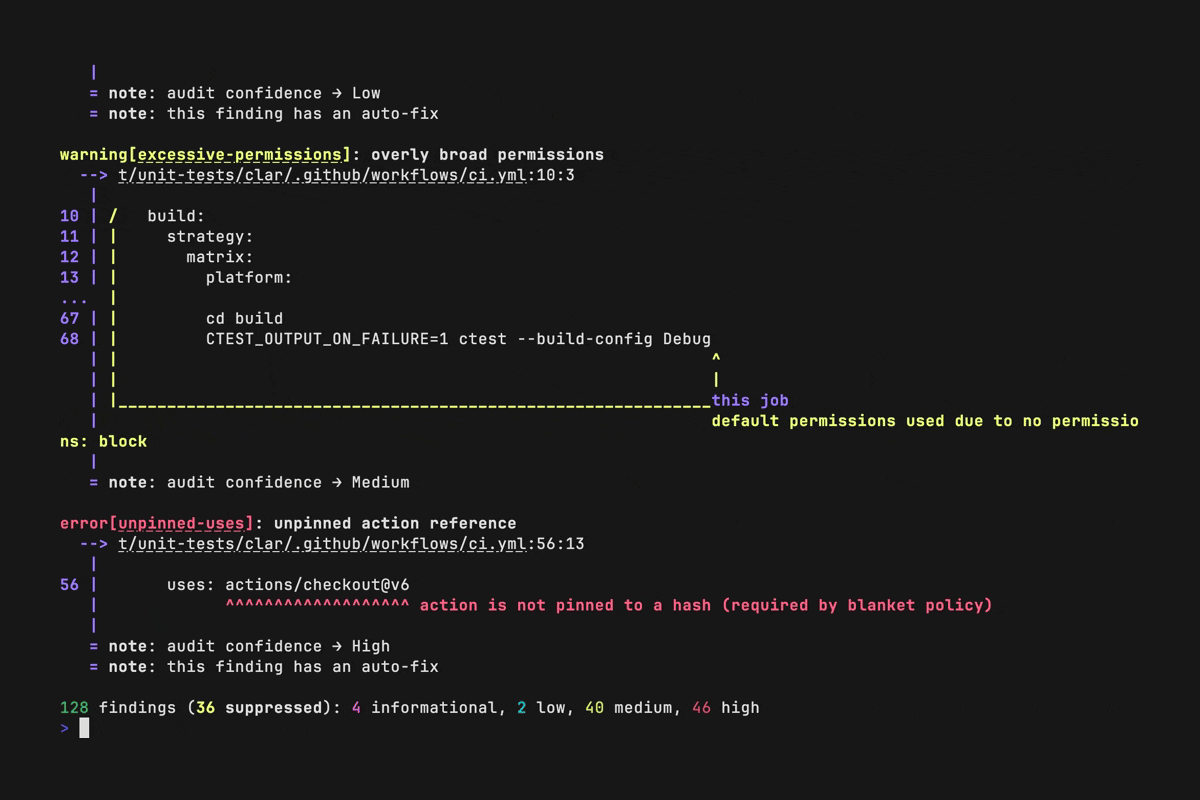 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
 8b-is/smart-tree
Smart Tree: not just a tree, a philosophy. A context-aware, AI-crafted replacement for 20+ tools with MEM8 quantum compression, semantic search,…
 node9-ai/node9-proxy
Access control for AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run,…
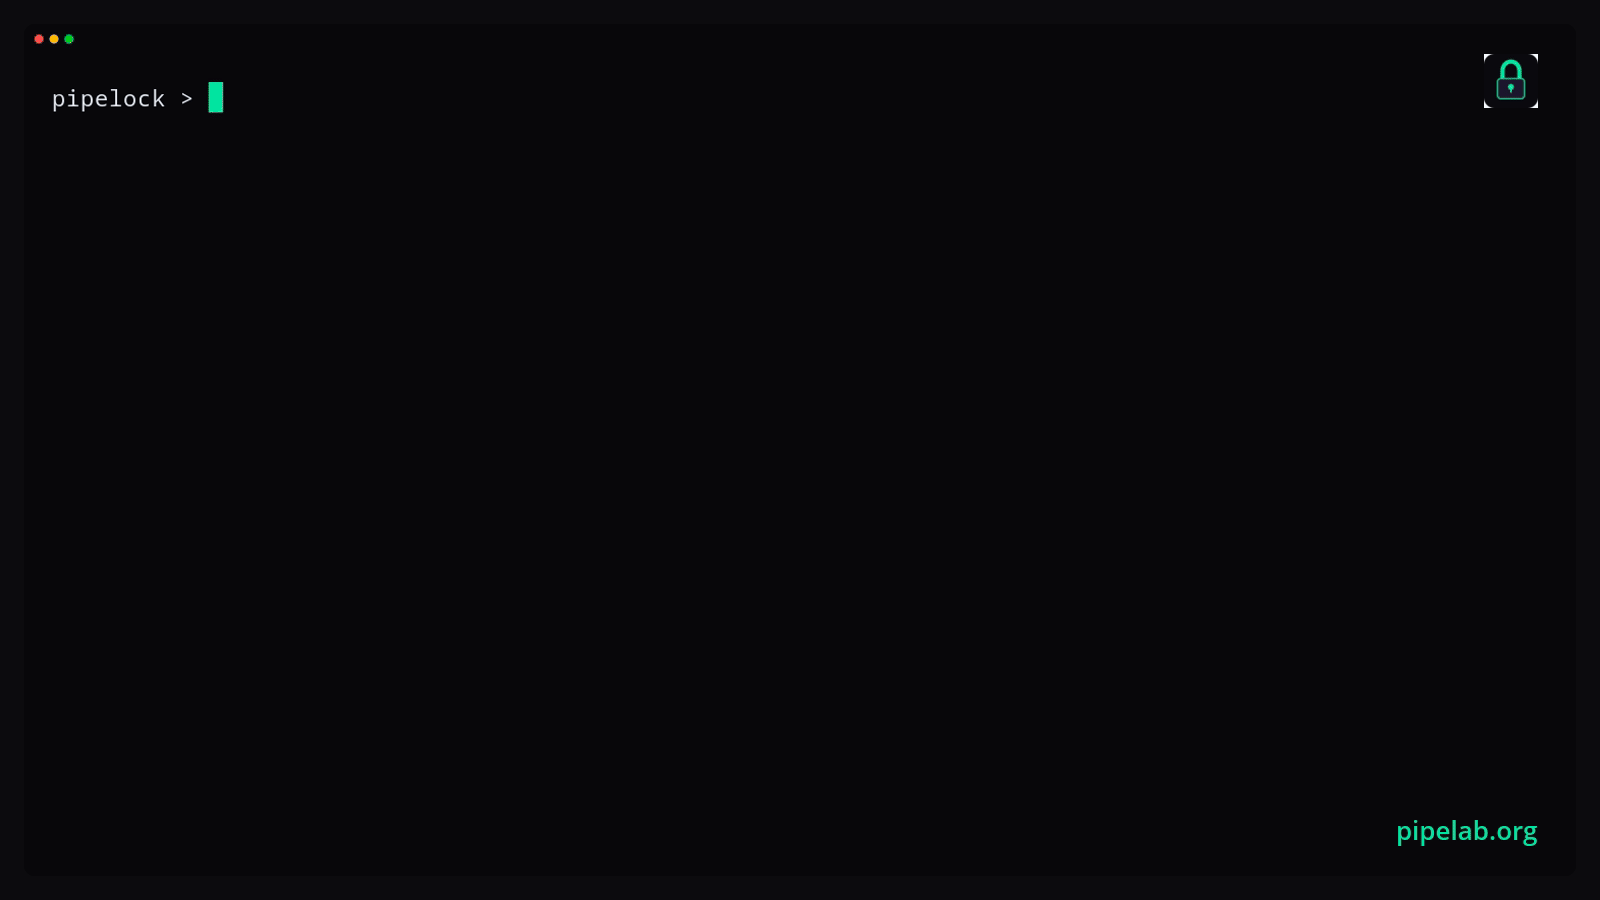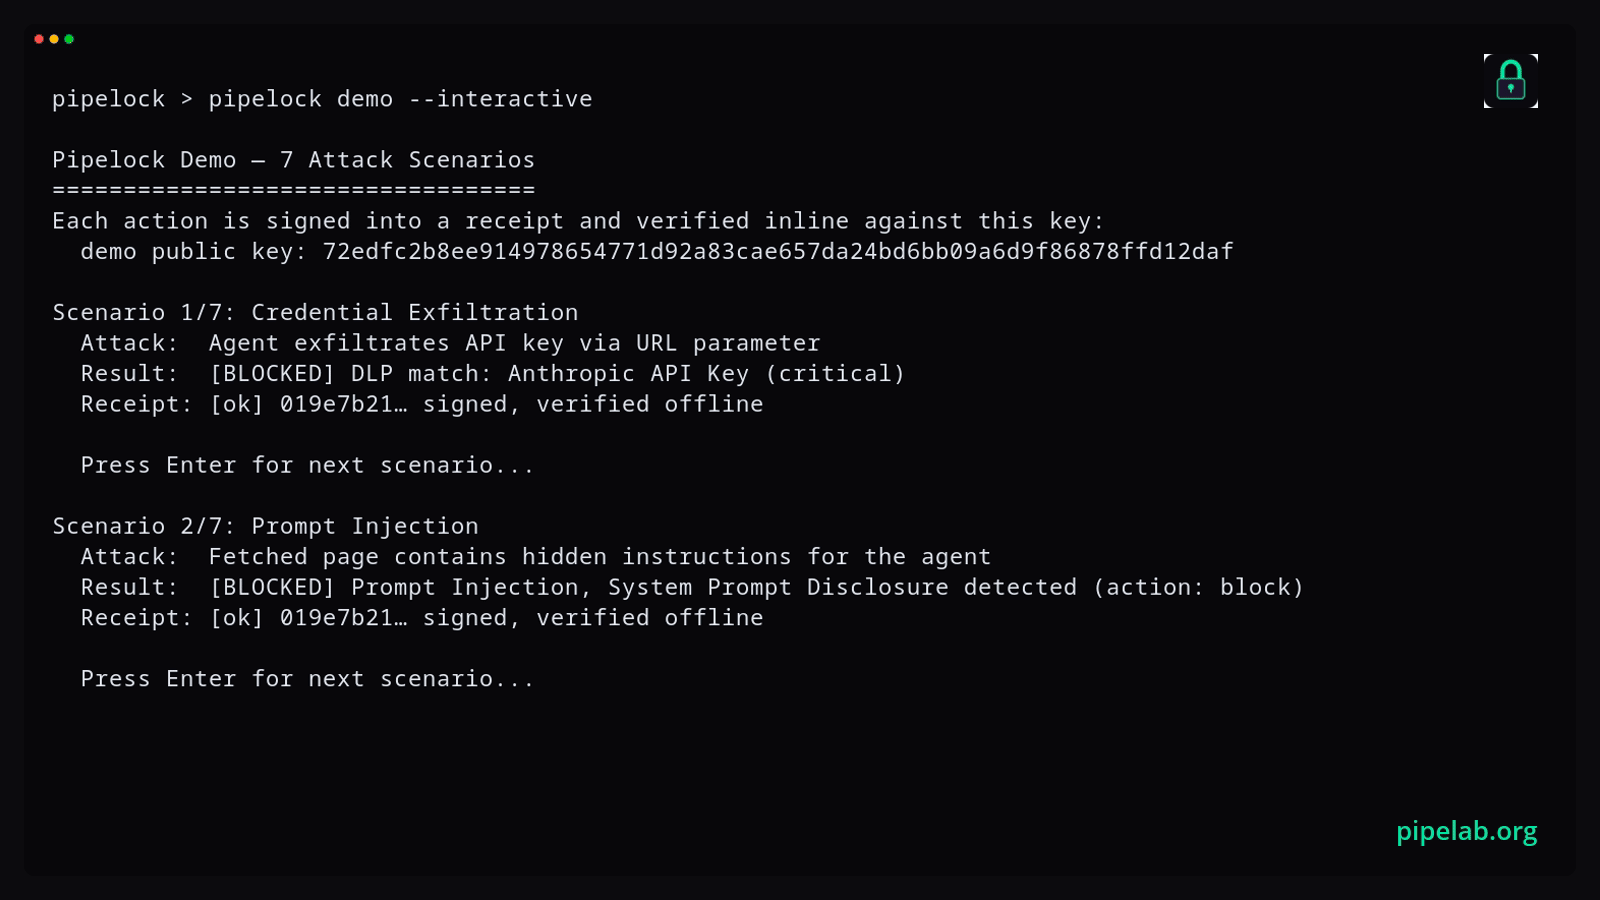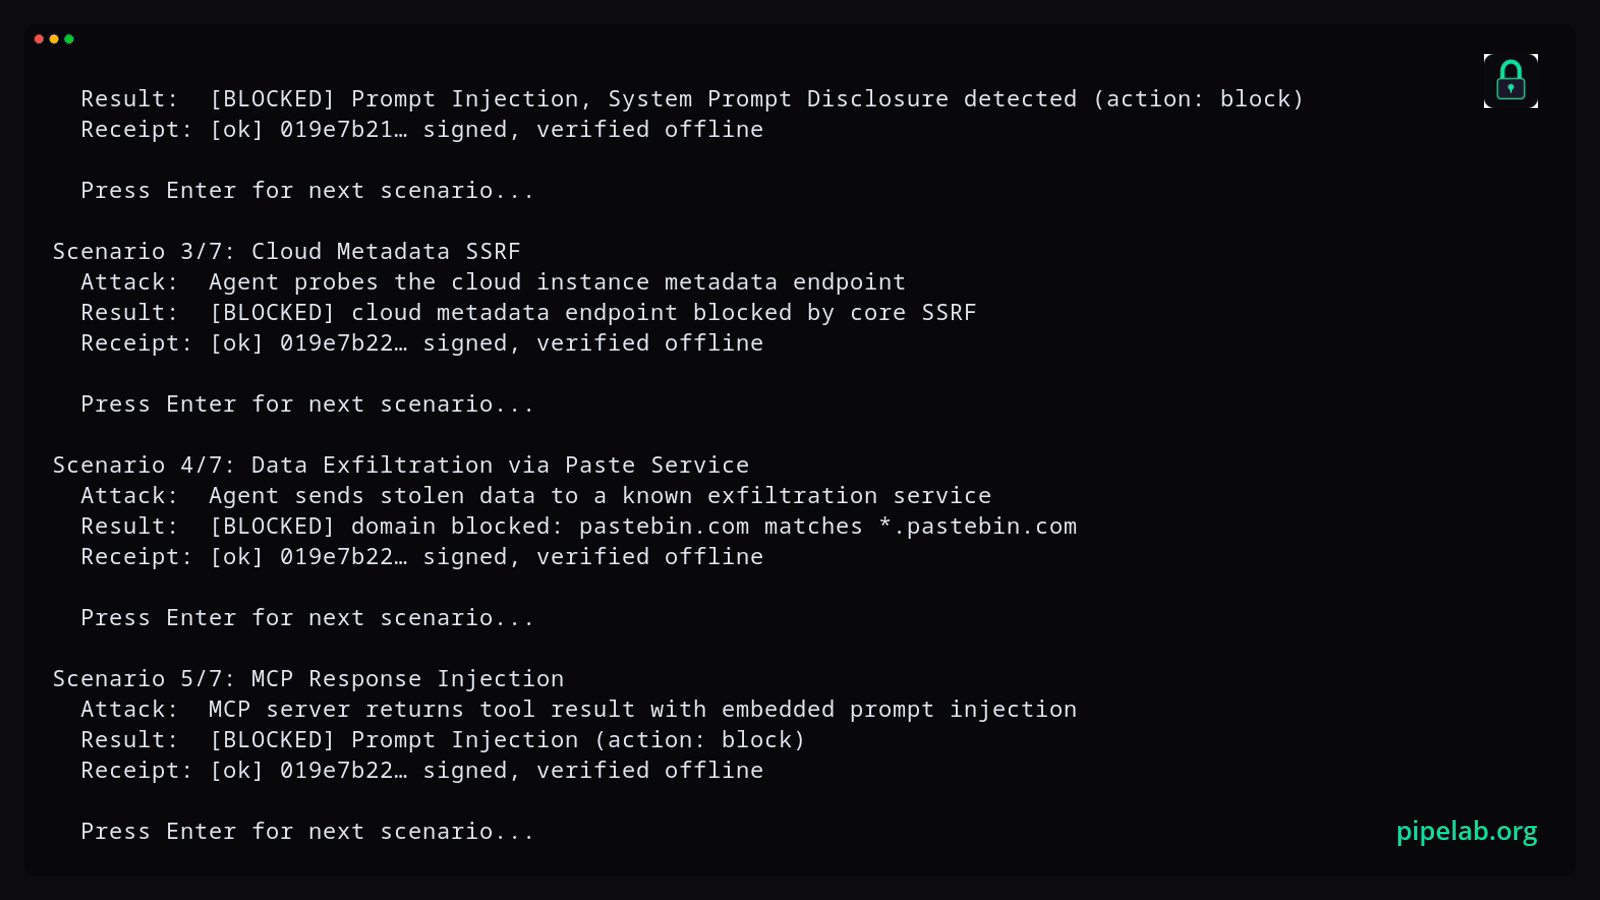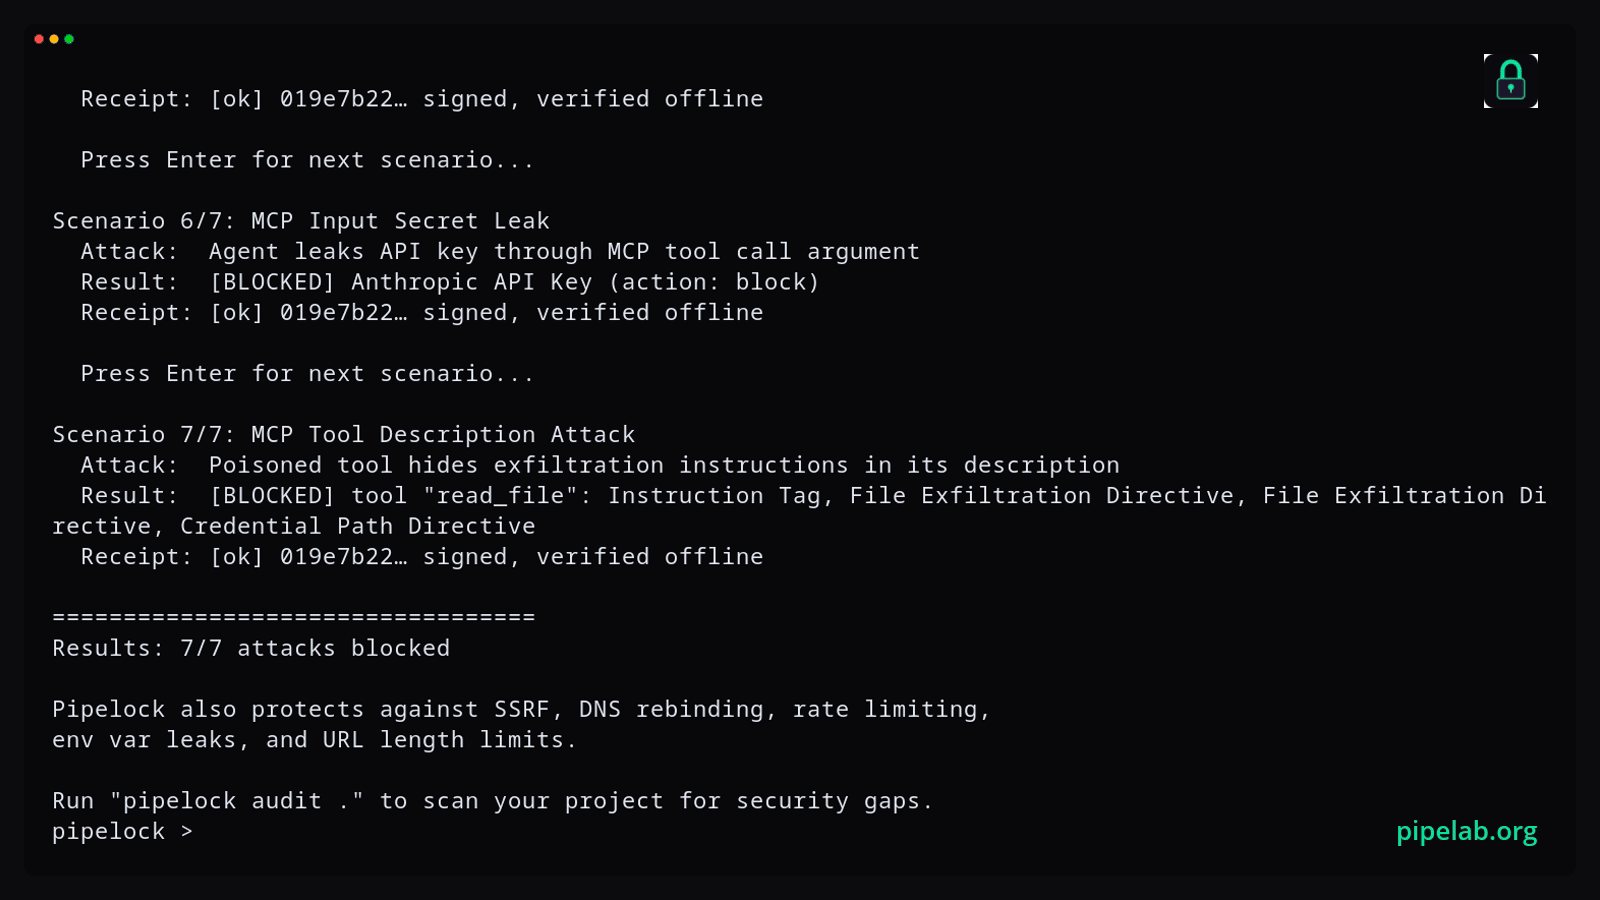 luckypipewrench/pipelock
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 studiomeyer-io/mcp-stdio-shellguard
Defense-in-depth bundle for MCP stdio servers: drop-in guardExec/guardSpawn wrappers, AST audit CLI, reference MCP server. Closes the Ox-Security…
 mindersec/minder
Software Supply Chain Security Platform
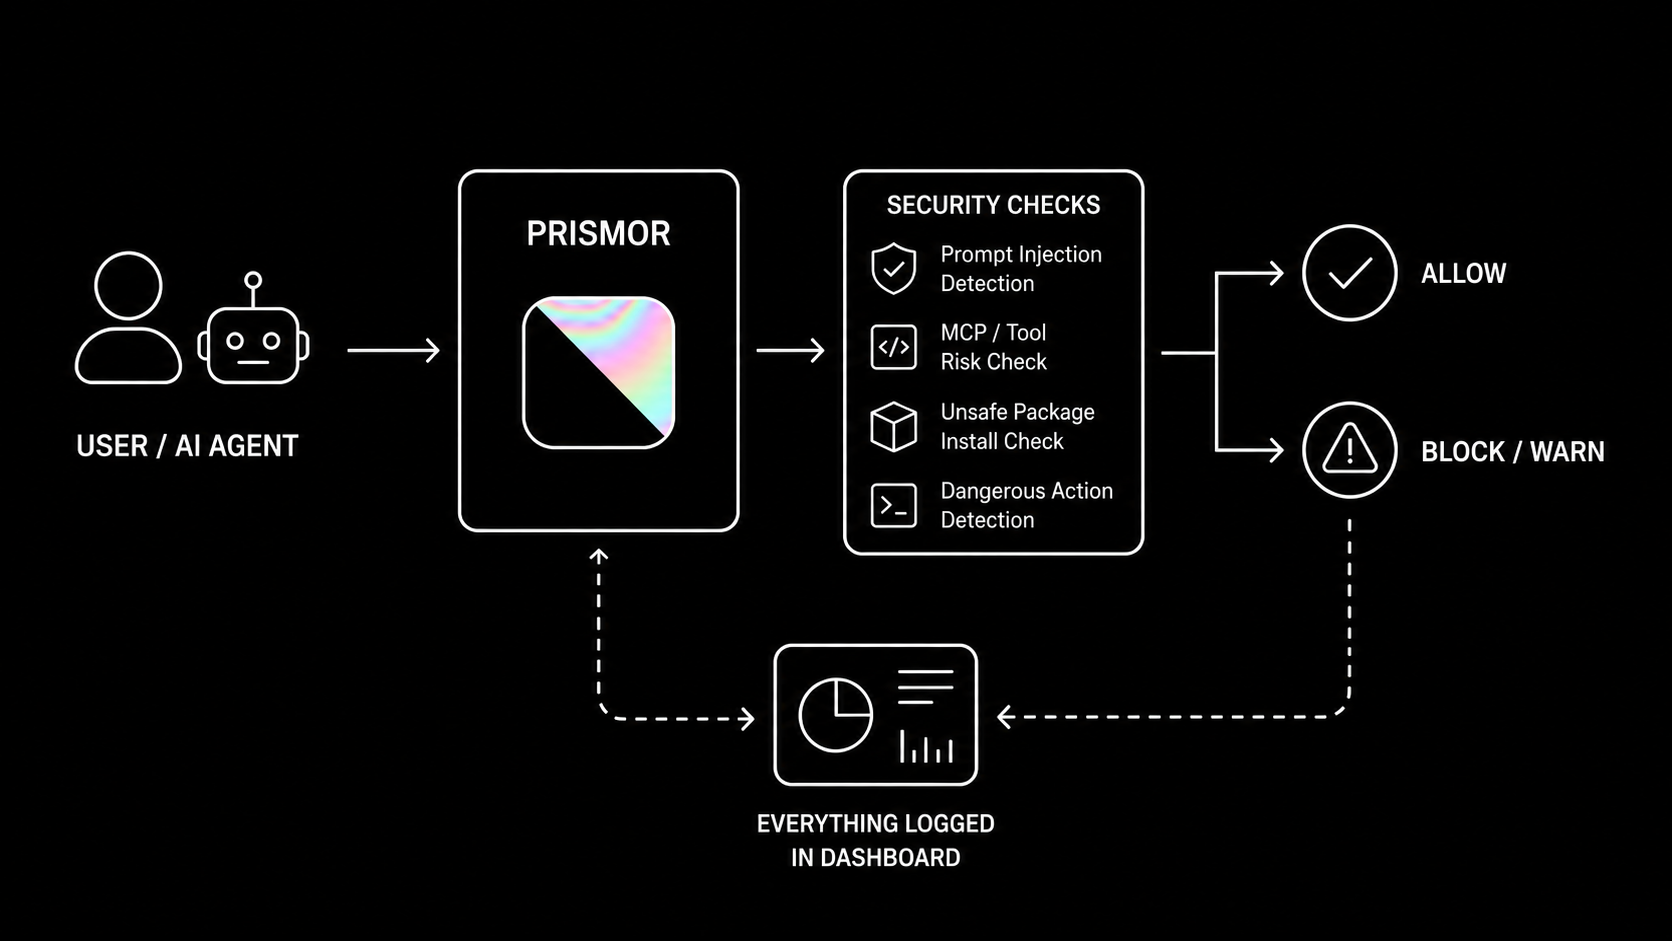 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
 aikidosec/safe-chain
Protect against malicious code installed via npm, yarn, pnpm, npx, pnpx, pip, uv and poetry with Aikido Safe Chain. Free to use, no tokens required.
 fazmin/cve-intel
Local security intelligence for CVE triage - 40 data sources and 41 tools, risk scores and an MCP server for AI agents, all in native Rust. Private…
 ag3ntsc4rn/autorun-audit
Find code that runs without you asking: repo files that execute on folder open (VS Code tasks, agent hooks, MCP, devcontainers) and Python…