

cve-2021-33879
 mmiszczyk/cve-2021-33879
GameLoop update MITM
exploitationmalware-analysispenetration-testing+3
mmiszczyk/cve-2021-33879GameLoop update MITM
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 viralmaniar/vulnvault
Developer-focused knowledge base of application security vulnerabilities with insecure vs secure code examples, prevention guidance, and OWASP/CWE…
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 ossf/allstar
GitHub App to set and enforce security policies
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
 koadt/oss-oopssec-store
Security training for the apps you actually ship. Open your browser and start hacking.
 ossf/criticality_score
Computes a criticality score for open source projects from repository, contributor, and dependency metrics to prioritize security improvements.
 ohaswin/pyscan
python dependency vulnerability scanner, written in Rust.
 bkhablenko/cve-2017-8046
Demonstrates exploitation of CVE-2017-8046 in a Spring Boot application, including a SpEL injection payload and dependency-check verification for…
 ossf/scorecard
OpenSSF Scorecard - Security health metrics for Open Source
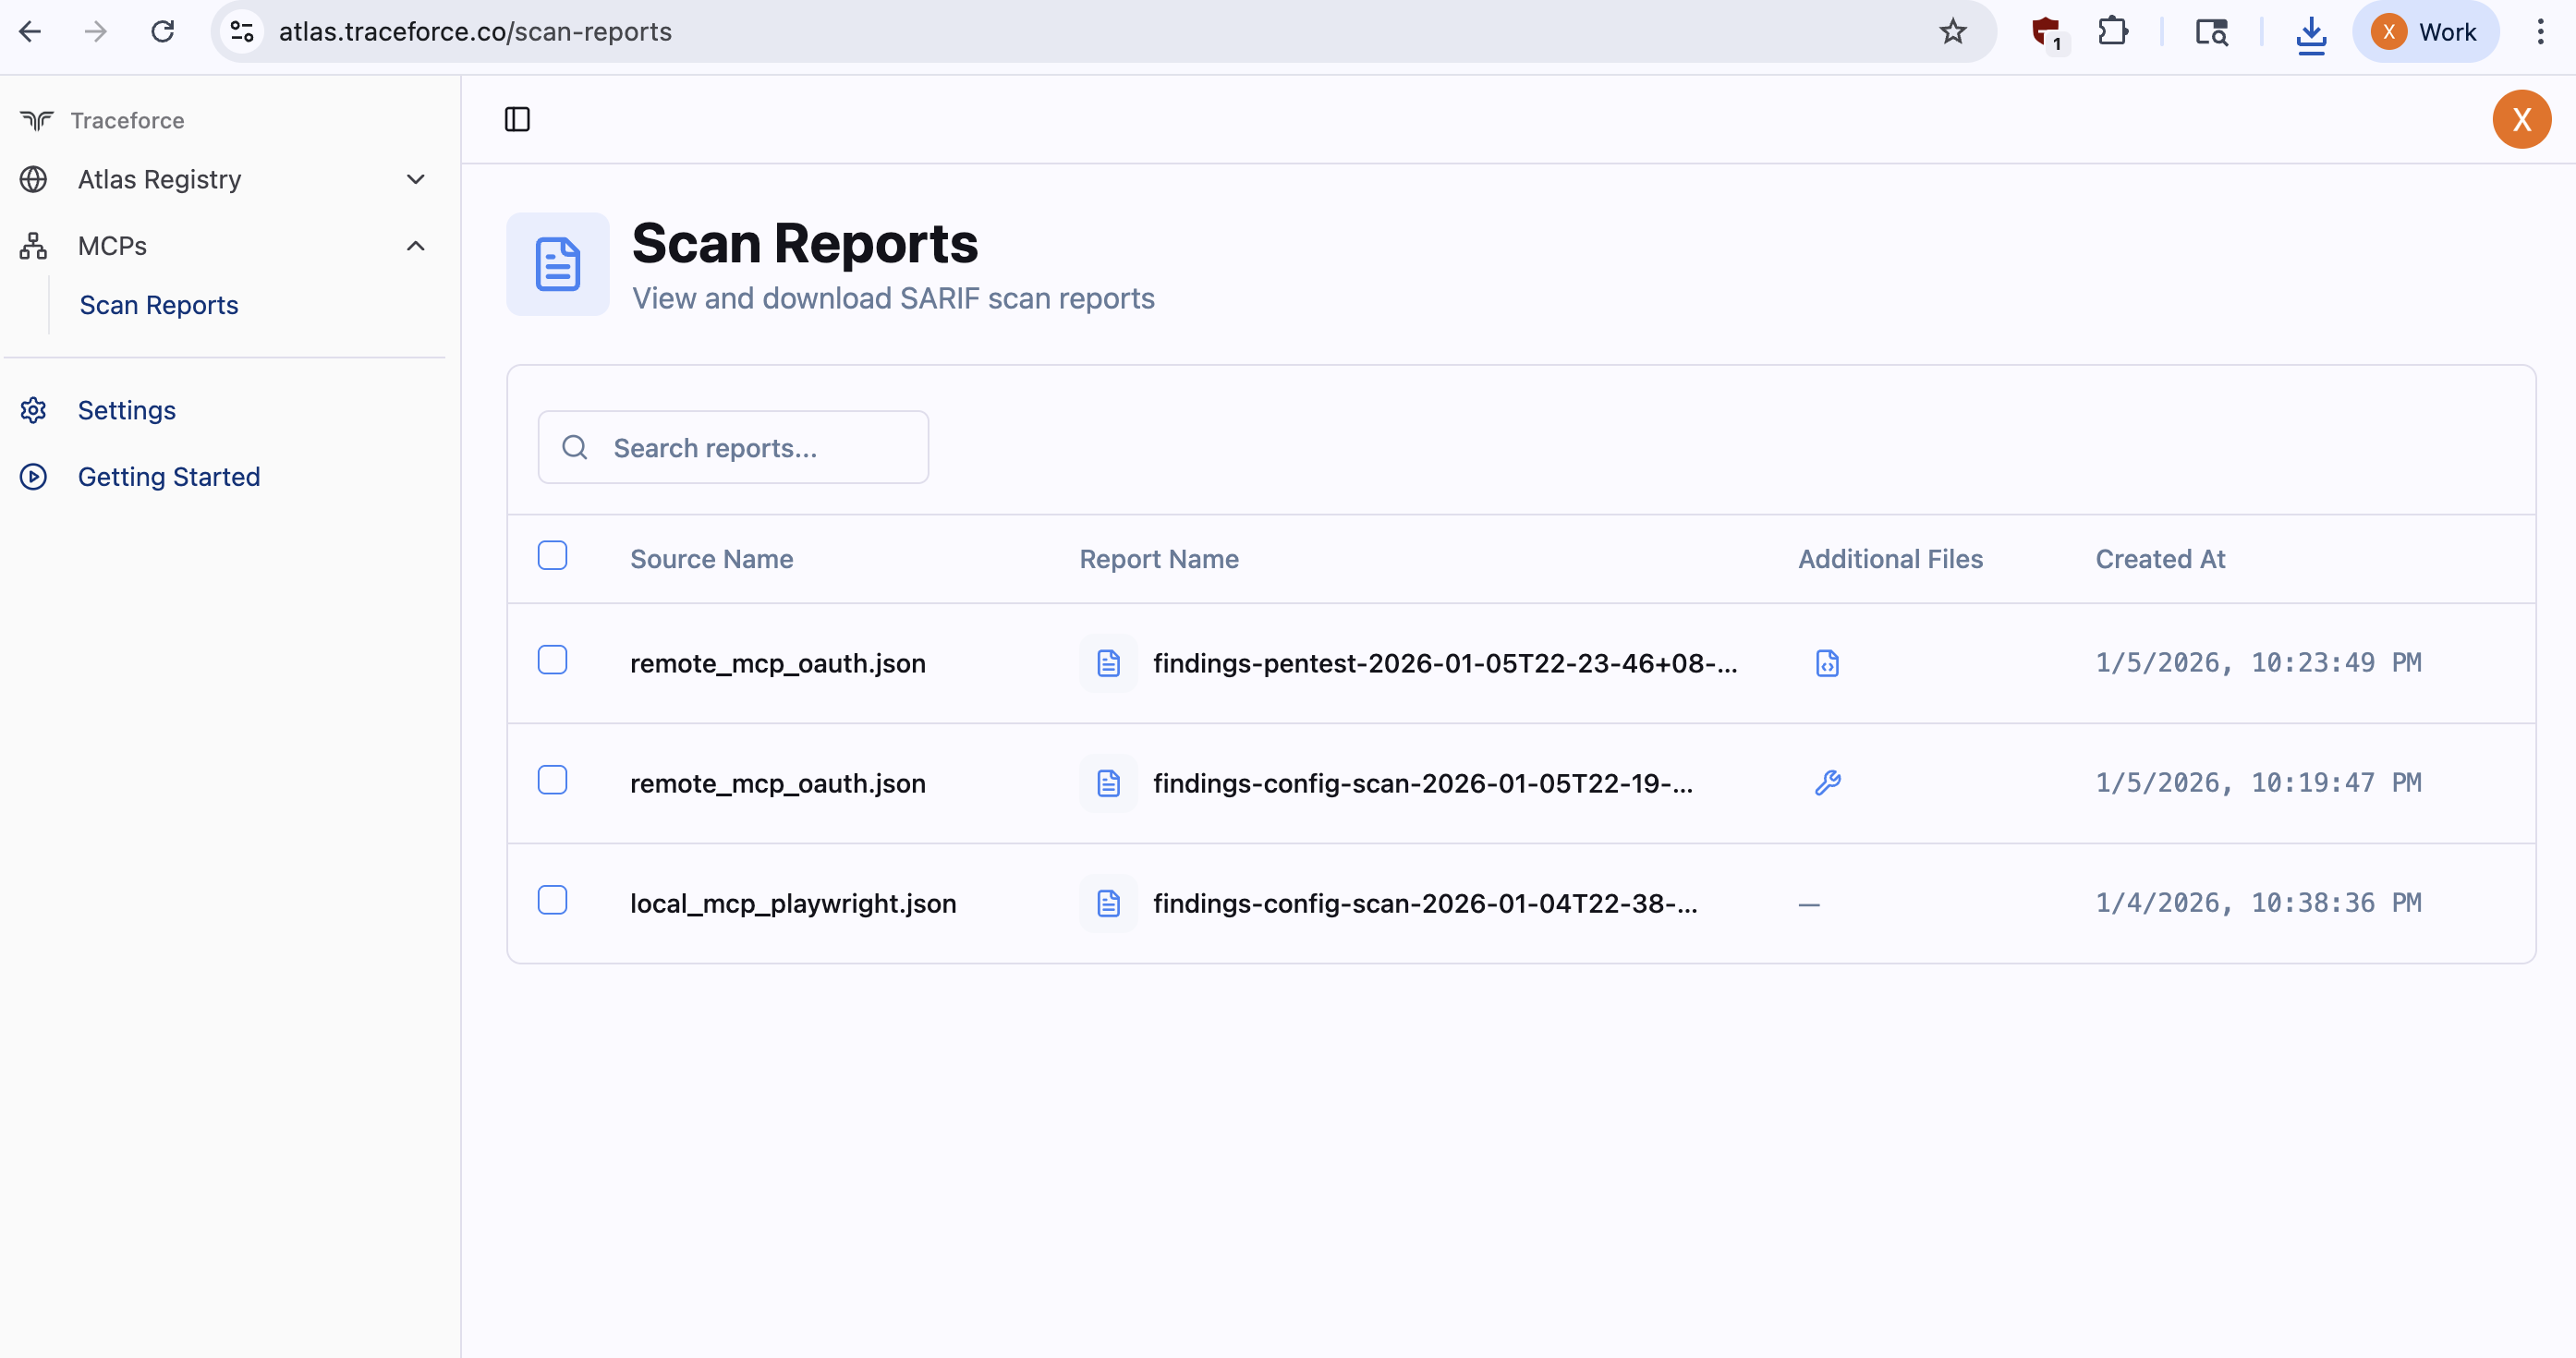 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 devang-solanki/cve-2018-6574
Exploit for remote command execution in Golang go get command.
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 appsecco/vulnerable-mcp-servers-lab
A collection of servers which are deliberately vulnerable to learn Pentesting MCP Servers.
 jackadamson/cve-2021-26700
Proof-of-concept for CVE-2021-26700: remote code execution in the VSCode npm-script extension via malicious workspace settings.json, with detailed…
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
 mbadanoiu/mvn_pwn
Malicious Maven pom.xml that uses "groovy-maven-plugin" to get RCE