

osv-scanner
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
code-analysiscontainer-securitydevsecops+4
11.3k20h 17m ago
google/osv-scannerVulnerability scanner written in Go which uses the data provided by https://osv.dev
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
 nvidia/skillspector
Security scanner for AI agent skills. Detect vulnerabilities, malicious patterns, security risks, prompt injection, data exfiltration, and…
 anchore/grype
A vulnerability scanner for container images and filesystems
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
 sheeki03/tirith
Terminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
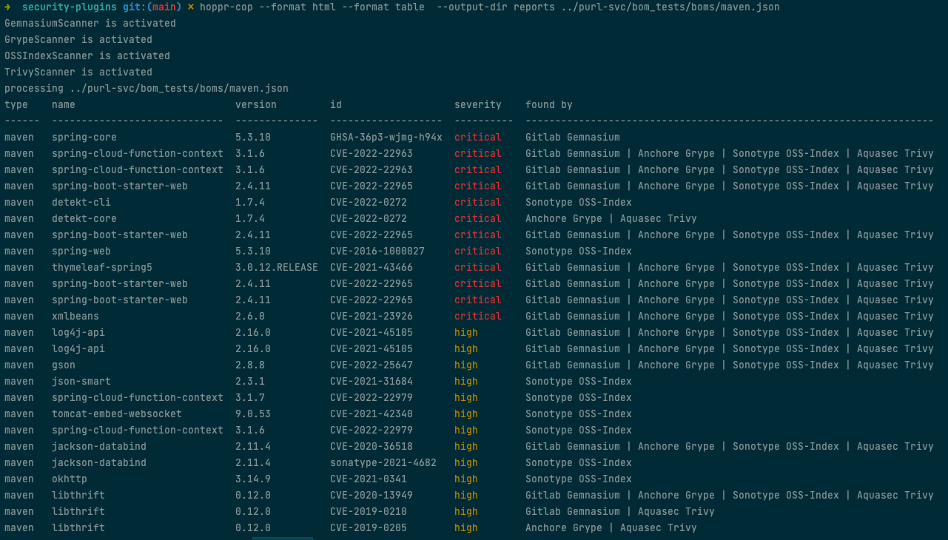
 hoppr/hoppr-cop
Aggregates vulnerability data from multiple databases into CycloneDX SBOMs, generating deduplicated VEX, HTML, and GitLab-compatible reports for…
 mmiszczyk/cve-2021-33879
GameLoop update MITM
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 dependencytrack/dependency-track
Intelligent Component Analysis platform that leverages SBOMs to identify and reduce software supply chain risk through continuous vulnerability…
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
 vulncheck-oss/cli
VulnCheck's official command line tool