Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
hoppr-cop — Aggregates vulnerability data from multiple databases into CycloneDX SBOMs, generating deduplicated VEX, HTML, and GitLab-compatible reports for continuous supply-chain security monitoring. | Kitploit
Tools/GitLabGitLab/hoppr/hoppr-cop
Vulnerability ScannersVulnerability AnalysisDevSecOpsSupply Chain Security
GitLabhoppr/hoppr-cop

hoppr-cop

Aggregates vulnerability data from multiple databases into CycloneDX SBOMs, generating deduplicated VEX, HTML, and GitLab-compatible reports for continuous supply-chain security monitoring.

View Repository
871881 month agoNot yet reviewed
Share

Hoppr-Cop

For Policing Your SBOM Vulnerabilities

Hoppr Cop is a cli and python library that generates high quality vulnerability information from a cyclone-dx Software Bill of Materials (SBOM) by aggregating data from multiple vulnerability databases. This project is offered as part of the hoppr ecosystem, however it is fully functional as a standalone cli or python library.

For more information please see the project documentation

Requirements

  • Hoppr Cop supports CycloneDX spec versions 1.3, 1.4, and 1.5
  • Scanning tools (required if desired)
    • grype -- version `0.73.0`` or later
    • trivy -- version `0.46.0`` or later

Project Status

Initial Release

Features

  • Integrates data from four leading opensource vulnerability databases
    • gemnasium community
    • grype
    • trivy
    • oss-index
  • Combines information from these sources in a way that reduces duplicates and ensures complete information for each vulnerability.
  • Generates reports in multiple formats
    • cyclone-dx vex either embedded in the existing bom or as a standalone file.
    • html - detailed vulnerability information that can be viewed in disconnected networks.
    • Gitlab Dependency Scanning, which enables Vulnerability Reports, Dependency List, and Security Dashboard

Why

SBOMs provide an ideal way to inventory all the dependencies in a project. A project's vulnerabilities should be monitored on a regular basis. hoppr-cop provides an easy mechanism to keep your vulnerability information up to date without regenerating an SBOM. The vex and html reports provide an ideal way to communicate vulnerability status to users, even in disconnected networks.

Why Use Multiple Scanners

  • Provides broad coverage of the upstream vulnerability data sources. You can see the full details of the data-sources here. Gitlab and Sonotype provide their own vulnerability reporting that you won't get elsewhere.
  • Provides much better coverage of a variety of package manager types. Each bom scanner has package managers that it excels at scanning, and some that it does a poor job of. Additionally, each product supports a different set of package ecosystems.
  • Seeing that multiple datasources agree on a finding, improves confidence that the finding is not a false positive.
  • Combining information from multiple sources leads to more complete and accurate information for each vulnerability identified, leading to quicker resolutions.

Demo
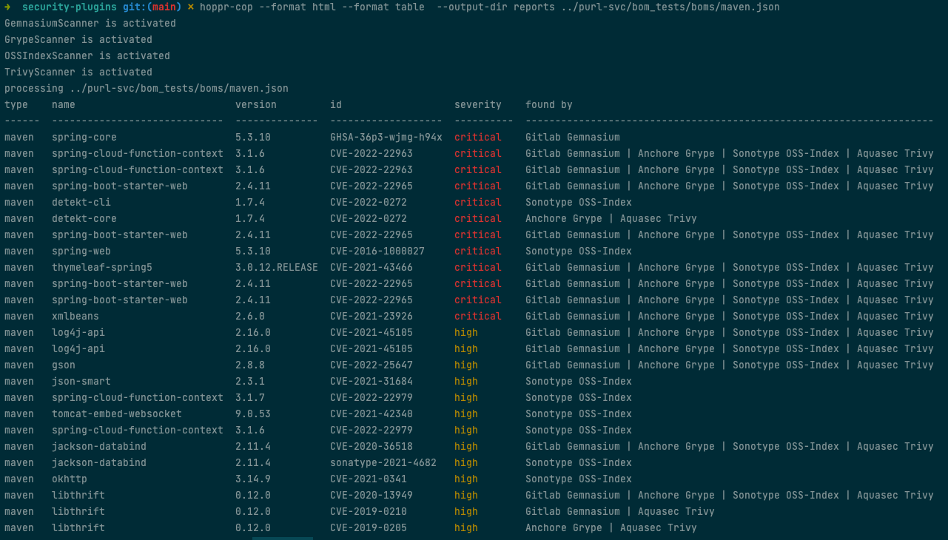
HopprCop usage example

Documentation

For more information please see the project documentation

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    491
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    462
  • 3

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    345
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    340
  • 5

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    306
  • 6

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    292

Explore all tools

Browse our collection of tools

View all tools →








