
ReconHound
 s_r_e_e_r_a_j/reconhound
ReconHound is a Python-based web reconnaissance tool designed for penetration testers, bug bounty hunters, and ethical hackers. It supports directory…
fuzzinginformation-gatheringpenetration-testing+3
1
s_r_e_e_r_a_j/reconhoundReconHound is a Python-based web reconnaissance tool designed for penetration testers, bug bounty hunters, and ethical hackers. It supports directory…

 offxec/pavelow
PAVELOW Exploit Toolbox is a BASH script that corresponds with your KALI distro to better help your vulnerability hunting and exploiting proccess…
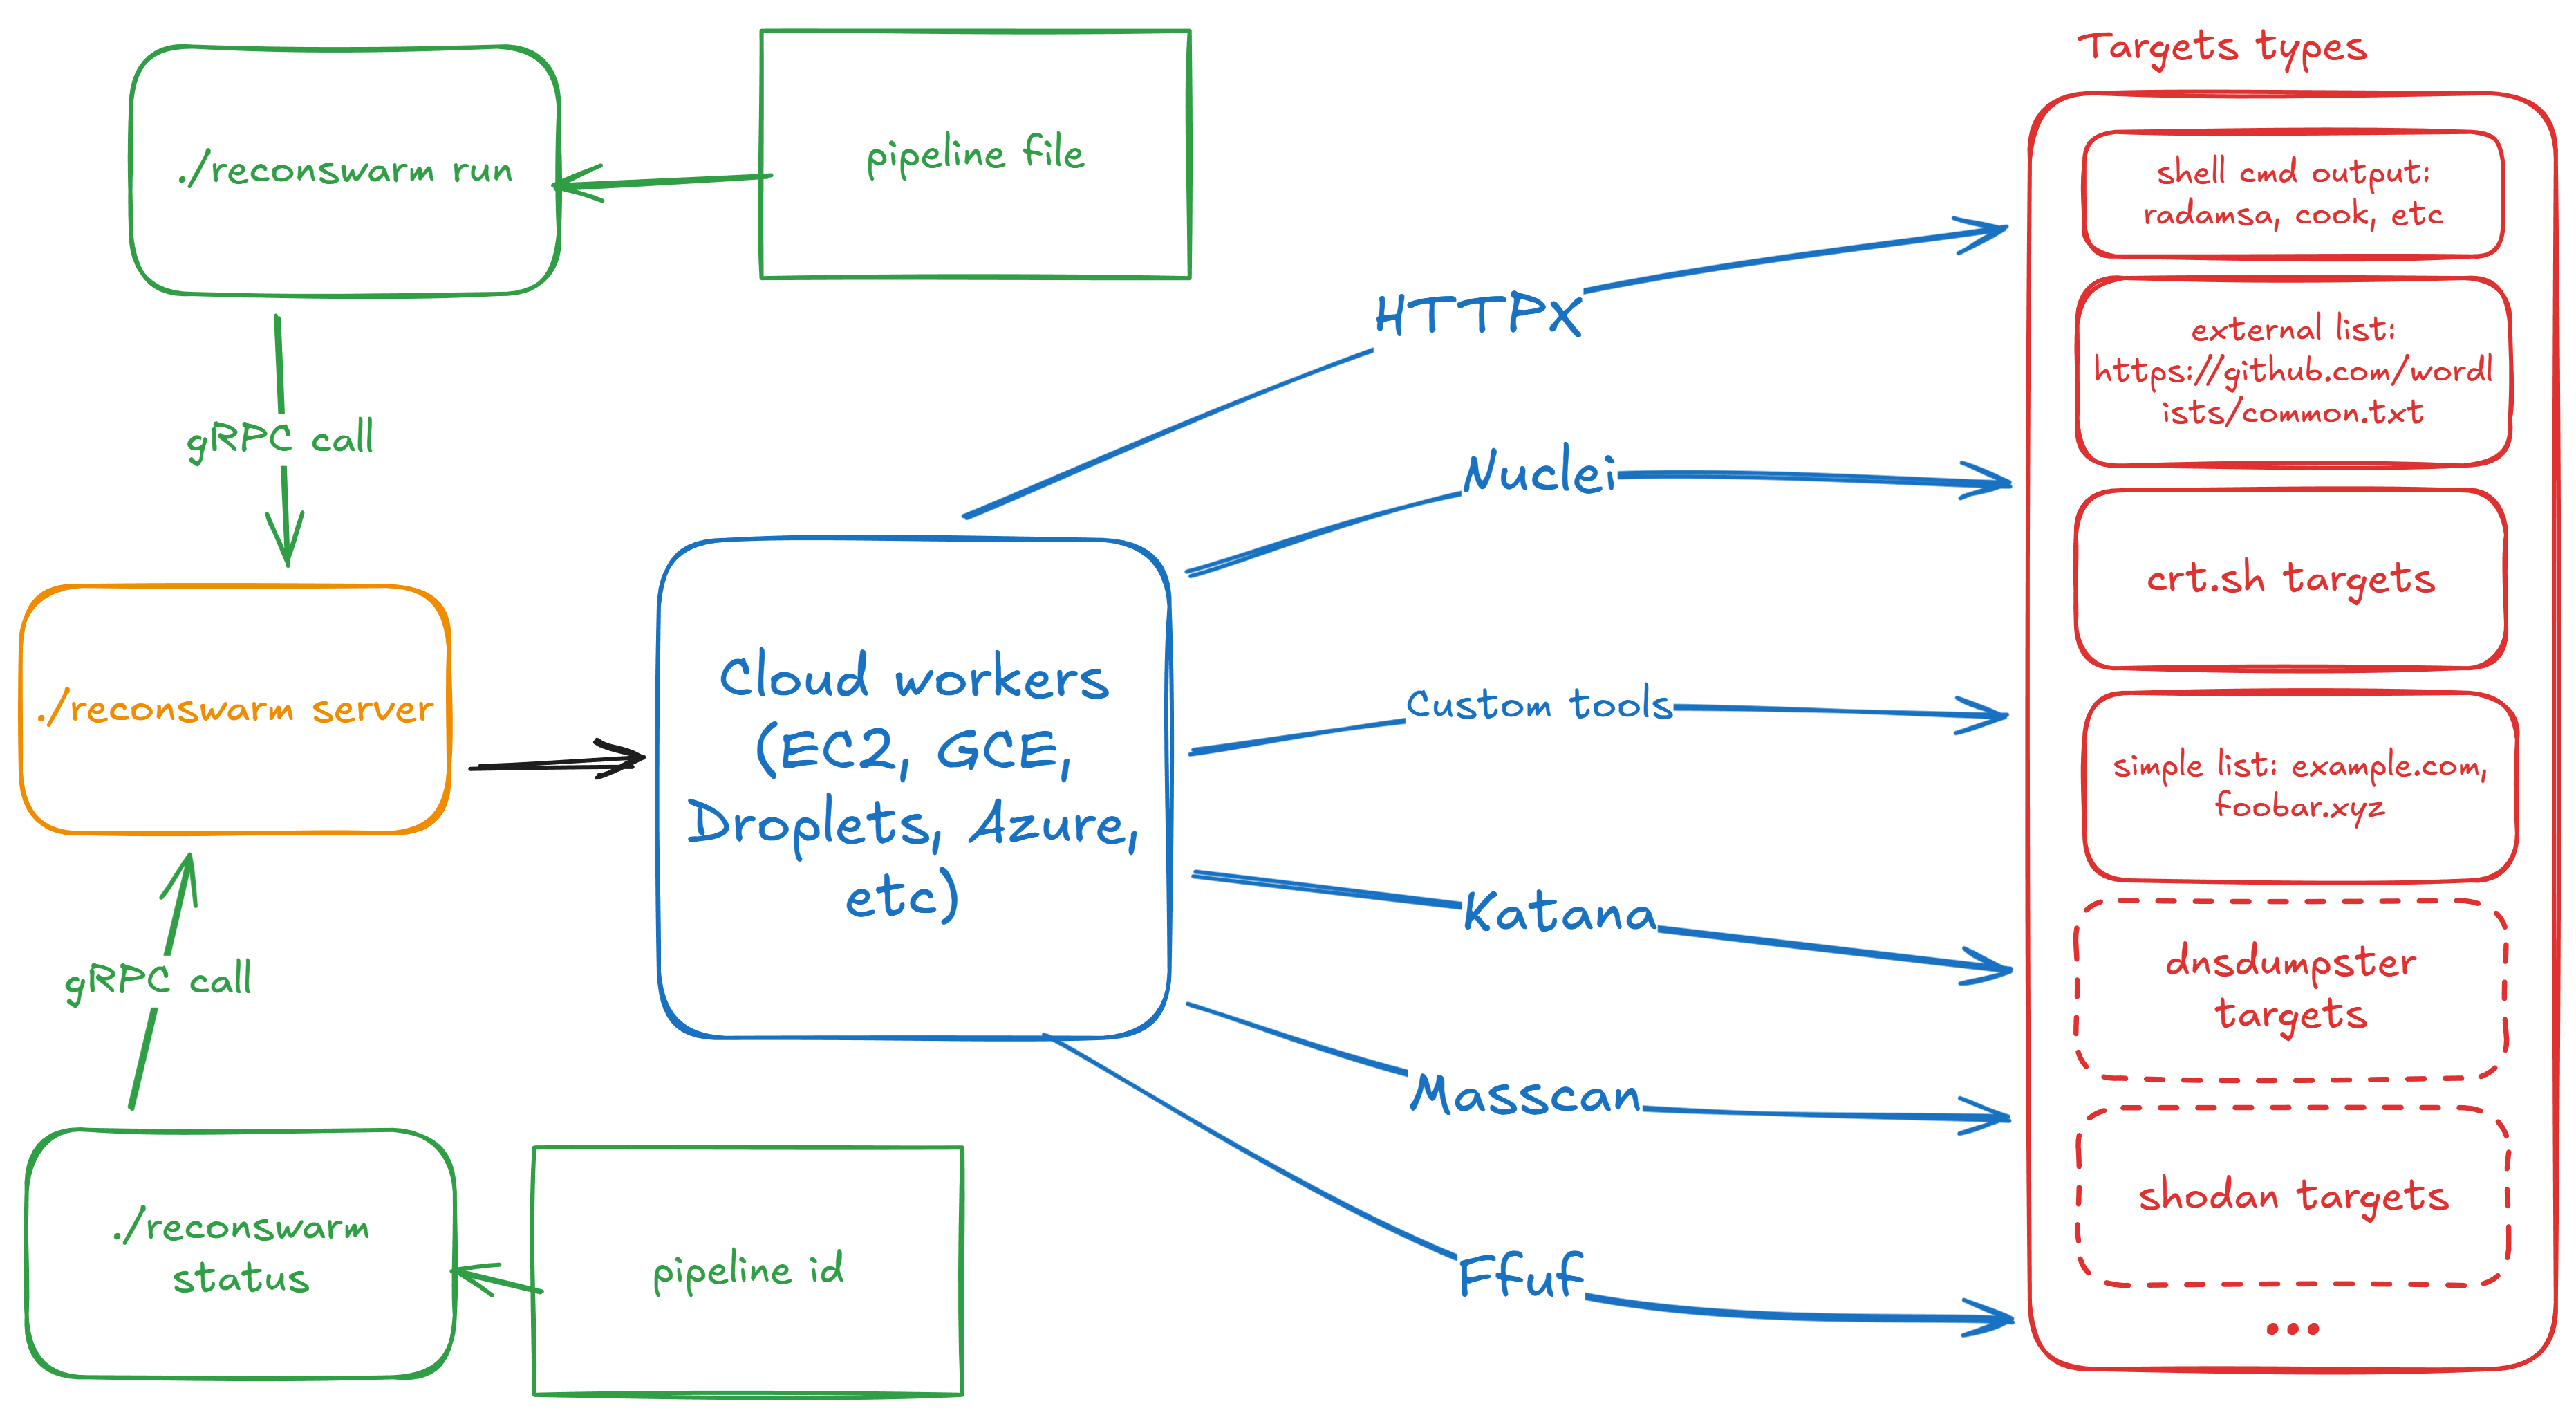 renatus-cartesius/reconswarm
Extend your recon with cloud power
 haccer/subjack
Concurrent DNS takeover scanner detecting CNAME, NS, AXFR, SPF, MX, SRV, and stale A record vulnerabilities across cloud providers, with multi-level…
 anshumanbh/tko-subs
A tool that can help detect and takeover subdomains with dead DNS records
 ice3man543/subover
A Powerful Subdomain Takeover Tool
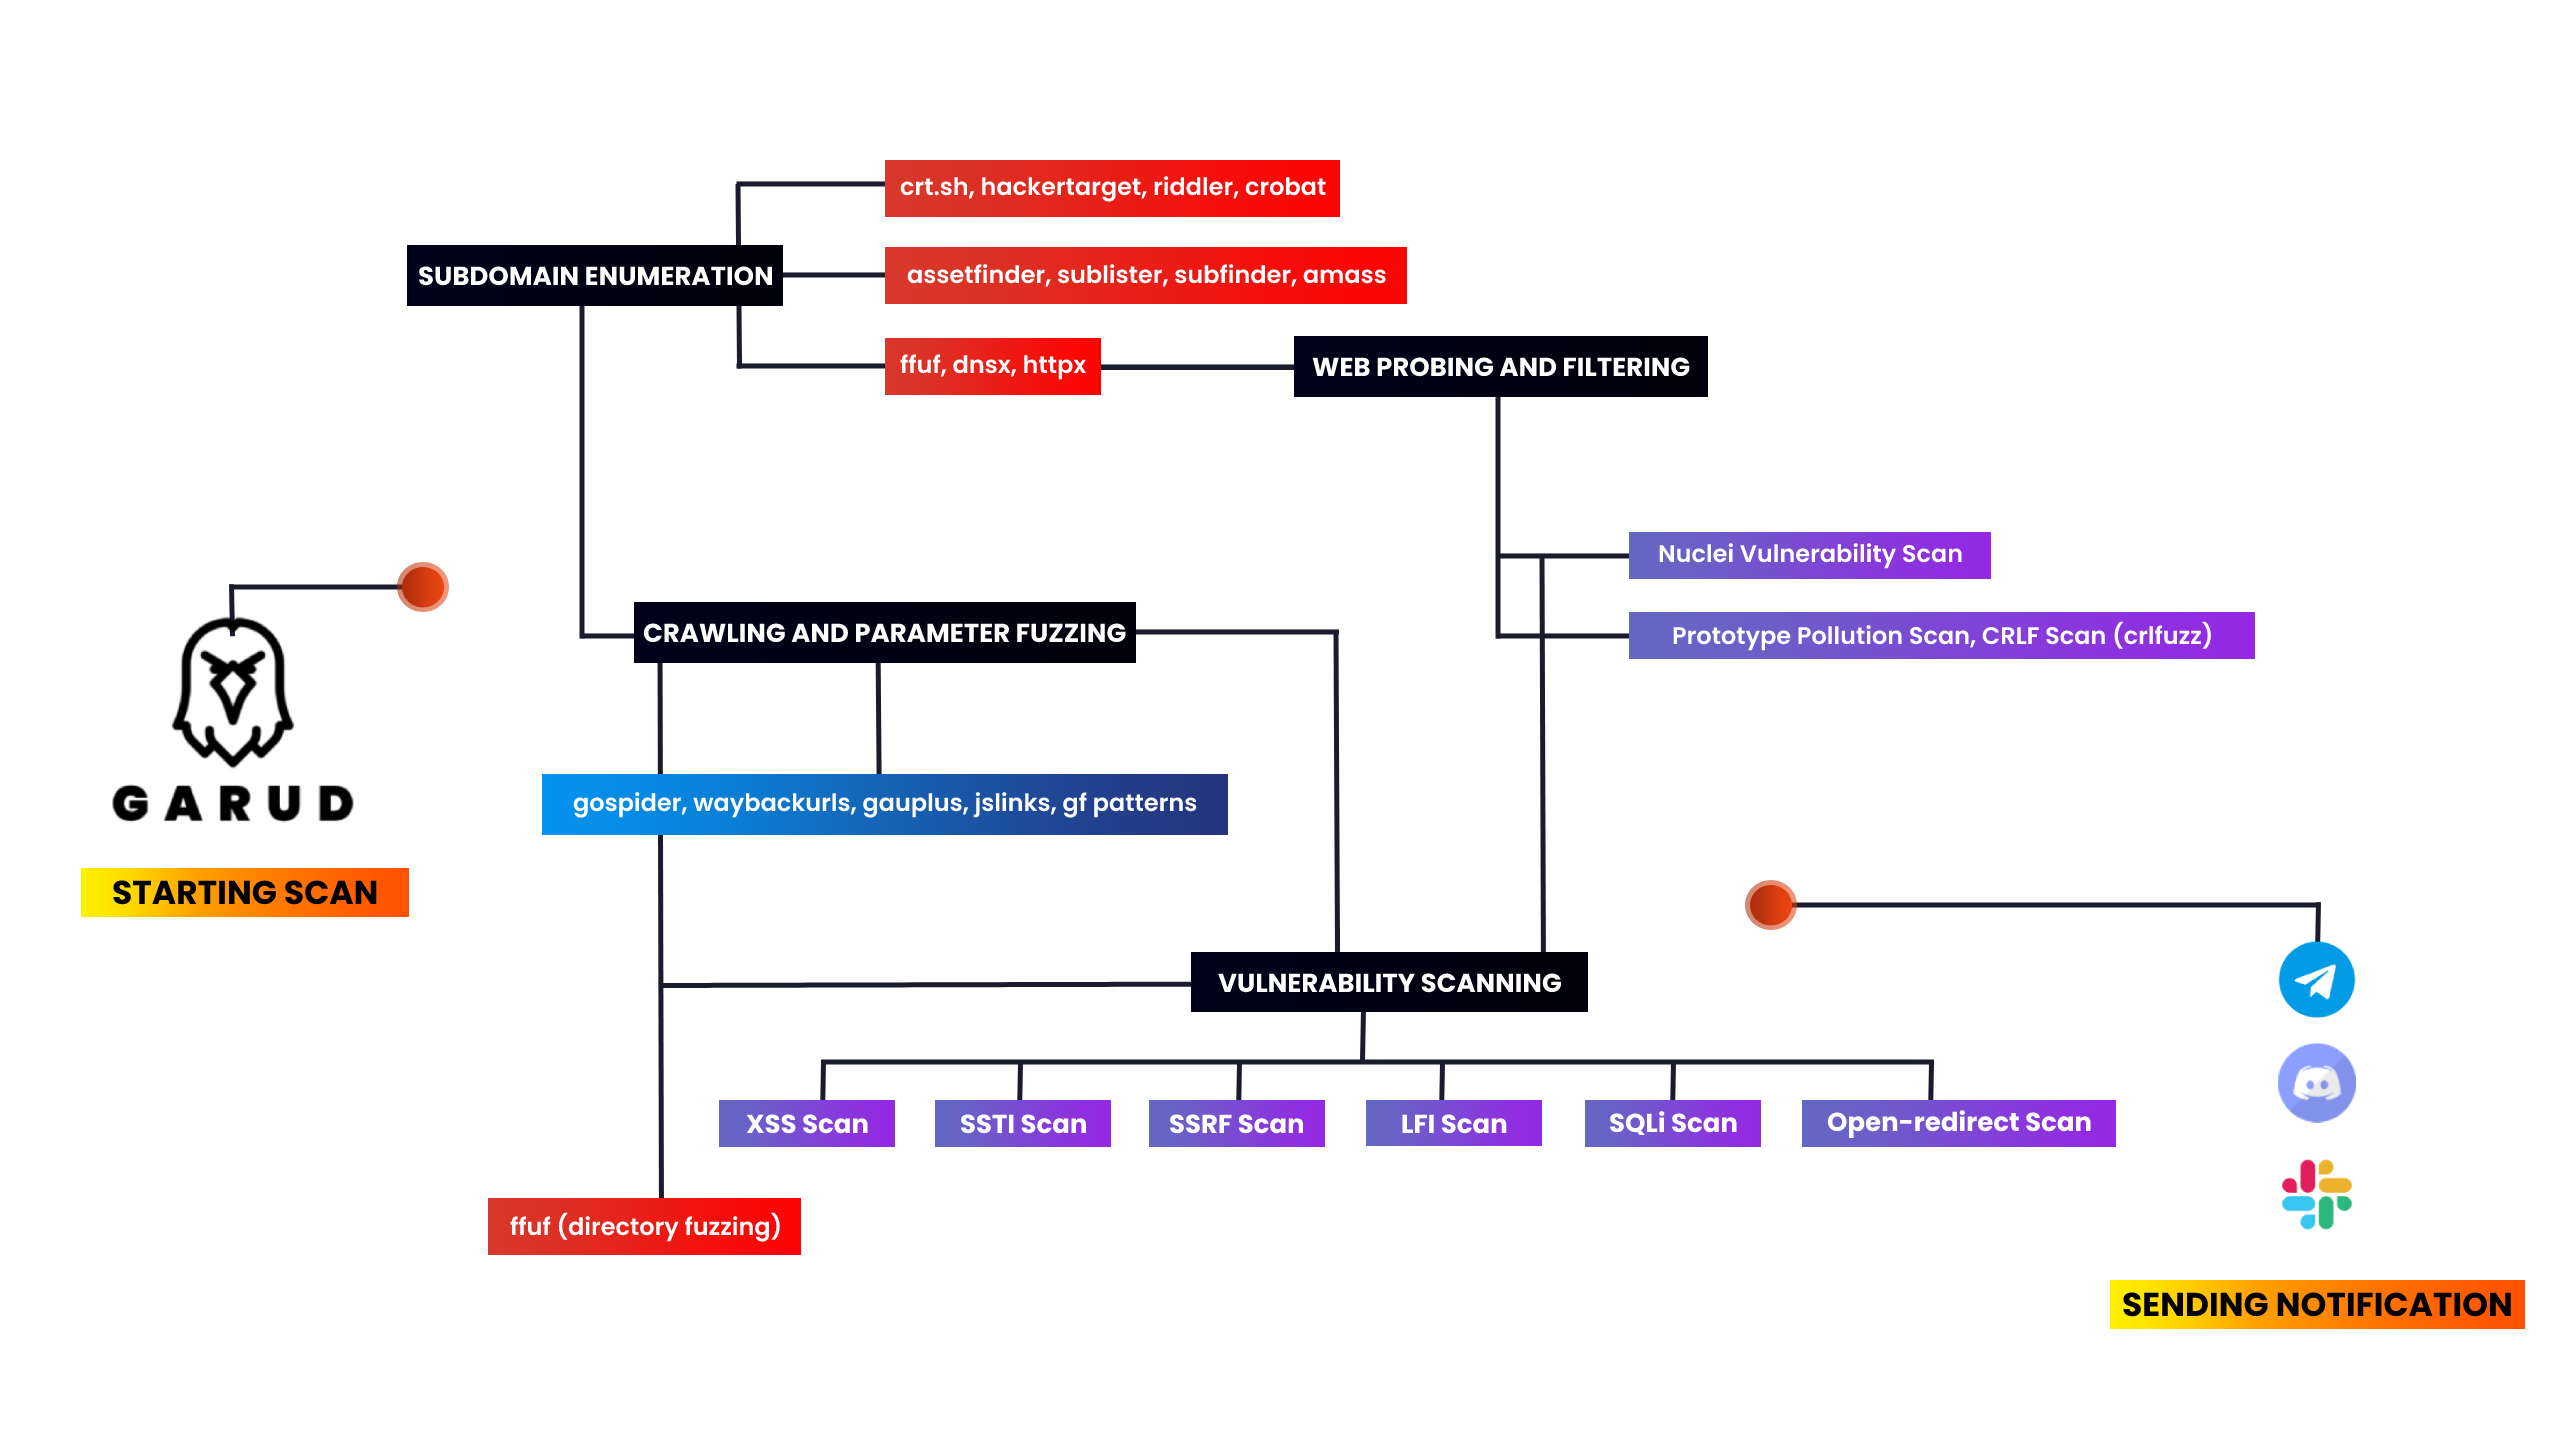 r0x4r/garud
An automation tool that scans sub-domains, sub-domain takeover, then filters out XSS, SSTI, SSRF, and more injection point parameters and scans for…
 umutcamliyurt/subhunter
Fast subdomain takeover scanner that checks DNS CNAME records against known fingerprints to detect vulnerable subdomains. Built in Go with…
 thecyberneh/scriptkiddi3
Automated reconnaissance and vulnerability detection tool that enumerates subdomains, collects URLs, and runs Nuclei scans to identify…
 toritoio/torito-r2s
Torito React2Shell Scanner & Exploit Tool (CVE-2025-55182 / 66478)
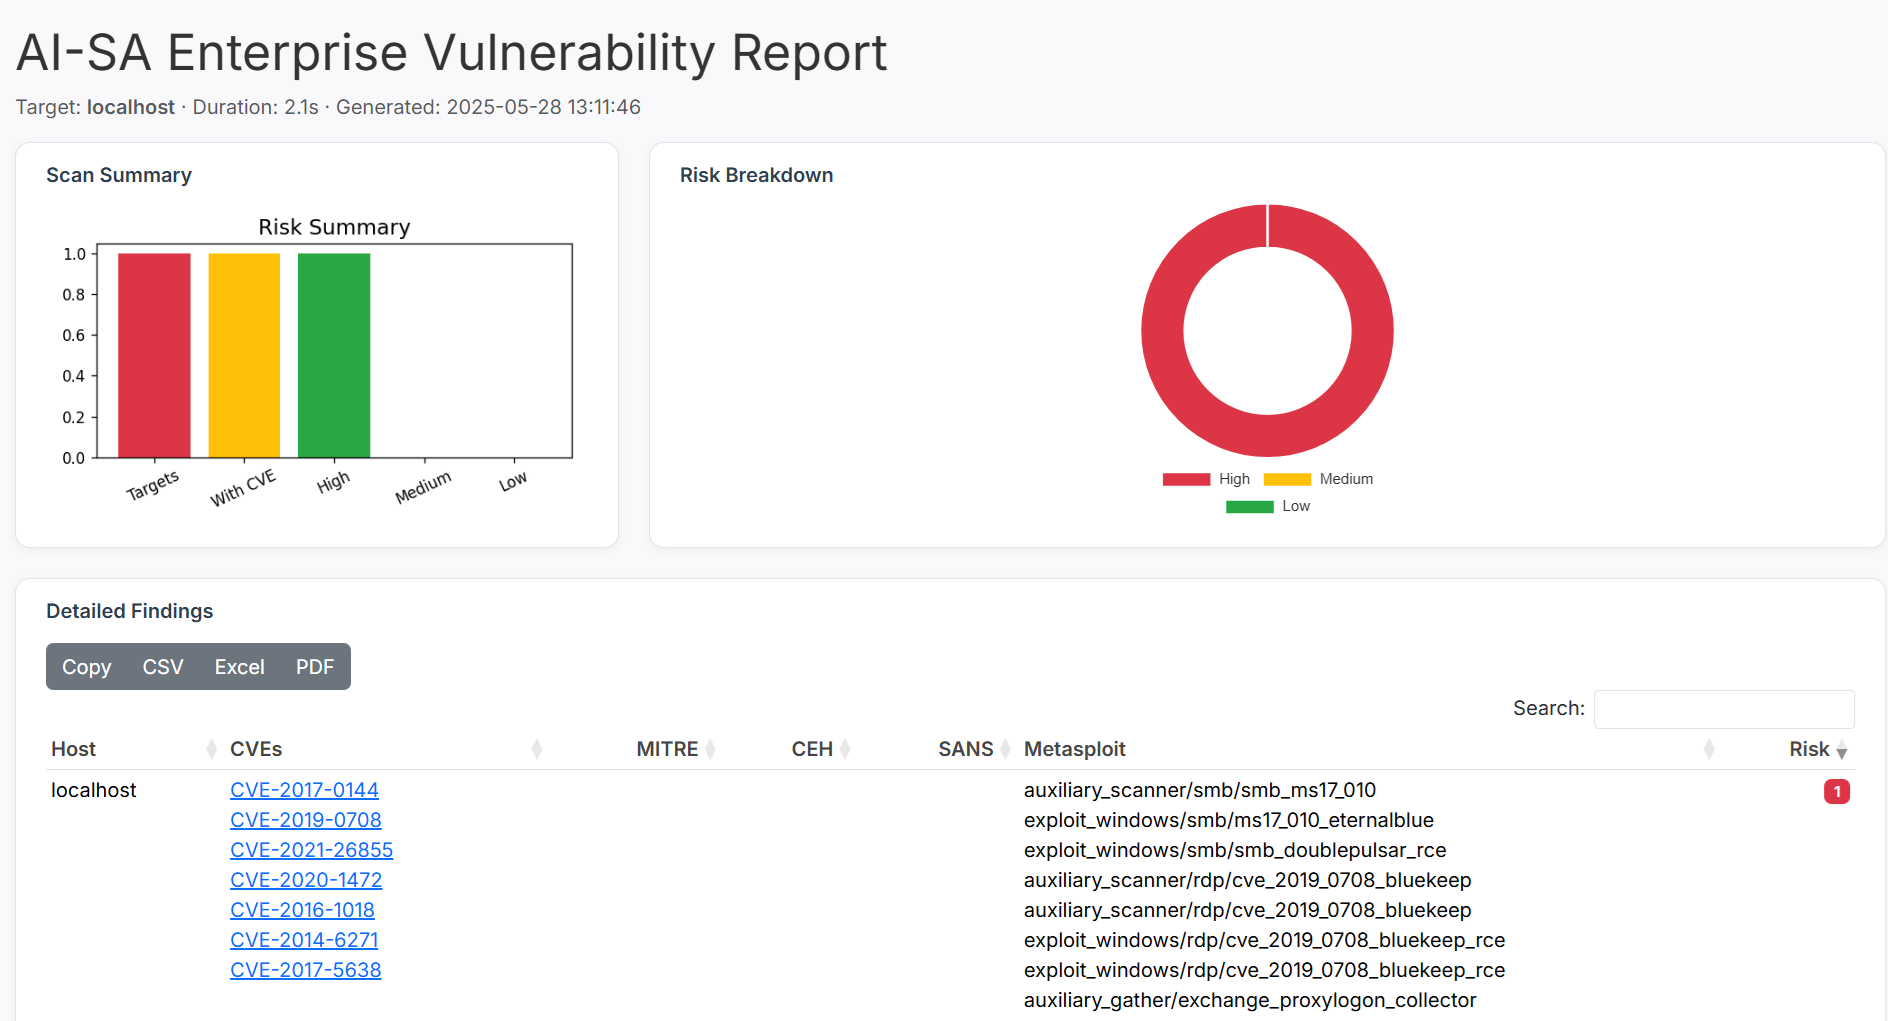 gmh5225/aisa-scanner
AISA-Scanner is an AI-powered autonomous vulnerability scanner that maps CVEs to metasploit exploits, MITRE, CEH, and SANS, delivering intelligent,…
 rapticore/ore_react2shell_scanner
CVE-2025-55182 (React2Shell) Scanner
 termireum/react2shell
React2Shell is a high-performance vulnerability scanner written in Go, specifically designed to detect Server-Side Remote Code Execution (RCE)…
 r3curs1v3-pr0xy/sub404
A python tool to check subdomain takeover vulnerability
 1n3/sn1per
Automated penetration testing & attack surface management platform. Recon, scan, exploit, report — 600+ exploits, 90+ integrations, 10K+ detections.
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 uphiago/recon-skills
Field-validated offensive security skill pack with 169 techniques for reconnaissance and penetration testing. Covers CORS, SSRF, subdomain takeover,…