
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
SubOver — A Powerful Subdomain Takeover Tool | Kitploit
Tools/GitHubGitHub/ice3man543/subover
Vulnerability AnalysisWeb SecurityPenetration TestingSubdomain Enumeration
GitHubice3man543/subover

SubOver

A Powerful Subdomain Takeover Tool

View Repository
967197748 years agoReviewed by Kitploit
Share

SubOver

Note - This project is discontinued. No more updates will be provided! Sorry!

But something more awesome will come soon!

Subover is a Hostile Subdomain Takeover tool originally written in python but rewritten from scratch in Golang. Since it's redesign, it has been aimed with speed and efficiency in mind. Till date, SubOver detects 30+ services which is much more than any other tool out there. The tool uses Golang concurrency and hence is very fast. It can easily detect and report potential subdomain takeovers that exist. The list of potentially hijackable services is very comprehensive and it is what makes this tool so powerful.

Installing

You need to have Golang installed on your machine. There are no additional requirements for this tool.

go get github.com/Ice3man543/SubOver

NOTE - Do not change the location of providers.json file. Or the tool will not work.

Usage

./SubOver -l subdomains.txt

  • -l List of Subdomains
  • -a Check all hosts regardless of CNAME (Time Consuming and prone to fp's)
  • -t Number of concurrent threads. (Default 10)
  • -v Show verbose output (Default False)
  • -https Force HTTPS Connection (Default HTTP)
  • -timeout Set custom timeout (Default 10)
  • -h Show help message

Currently Checked Services

Github, Heroku, Unbounce, Tumblr, Shopify, Instapage, Desk, Tictail, Campaignmonitor, Cargocollective, Statuspage, Amazonaws, Cloudfront, Bitbucket, Smartling, Acquia, Fastly, Pantheon, Zendesk, Uservoice, Ghost, Freshdesk, Pingdom, Tilda, Wordpress, Teamwork, Helpjuice, Helpscout, Cargo, Feedpress, Surge, Surveygizmo, Mashery, Intercom, Webflow, Kajabi, Thinkific, Tave, Wishpond, Aftership, Aha, Brightcove, Bigcartel, Activecompaign, Compaignmonitor, Acquia, Proposify, Simplebooklet, Getresponse, Vend, Jetbrains, Azure

Count : 51
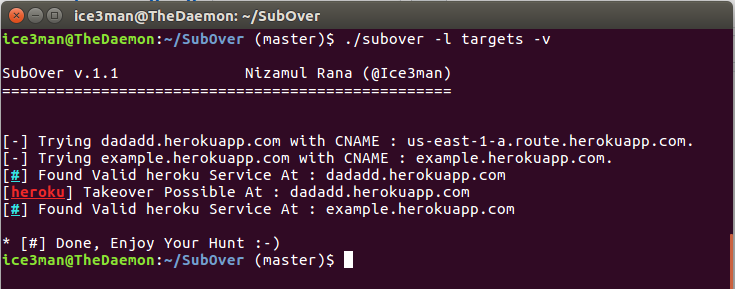
Screenshot

tool_in_action

FAQ

Q: What should my wordlist look like?

A: Your wordlist should include a list of subdomains you're checking and should look something like:

backend.example.com
something.someone.com
apo-setup.fxc.something.com

Your tool sucks!

Yes, you're probably correct. Feel free to:

  • Not use it.
  • Show me how to do it better.

TODO

  • Add more services :-)
  • Improve the tool (There are many things that can be done :-) )

Development

Want to contribute? Great!

You can add more services or recommend any changes to the existing ones. Any kind of help is appreciated.

Or buy me a coffee \o/

Buy me a coffee ko-fi

License

BSD 2-Clause "Simplified" License

Contact

Meet me on Twitter: Twitter

Changelog

[1.2] 2018-05-19

  • Refactored whole code making it cleaner
  • Added better error handling and more verbose stuff
  • Implemented checking all domains
  • Fixed other stuff, etc...

[1.1.1] - 2018-03-20

  • Providers corrected using EdOverflow's Awesome List
  • Added Information regarding various takeovers to the tool

[1.1.0] - 2018-03-16

  • Rewritten from scratch in Golang
  • This time it's damn fast because of Go Concurrency.
  • The console output looks better :-)

[1.0.0] - 2018-02-04

  • Initial Release with 35 Services written in Python.
  • Pretty Slow :-)

Credits

  • subjack : Hostile Subdomain Takeover Tool Written In GO
  • Subdomain Takeover Scanner by 0x94
  • Anshumanbh : tko-subs
  • EdOverflow : can-i-take-over-xyz
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    772
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    505
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    251

Explore all tools

Browse our collection of tools

View all tools →







