 r0x4r/garud
An automation tool that scans sub-domains, sub-domain takeover, then filters out XSS, SSTI, SSRF, and more injection point parameters and scans for some low hanging vulnerabilities automatically.



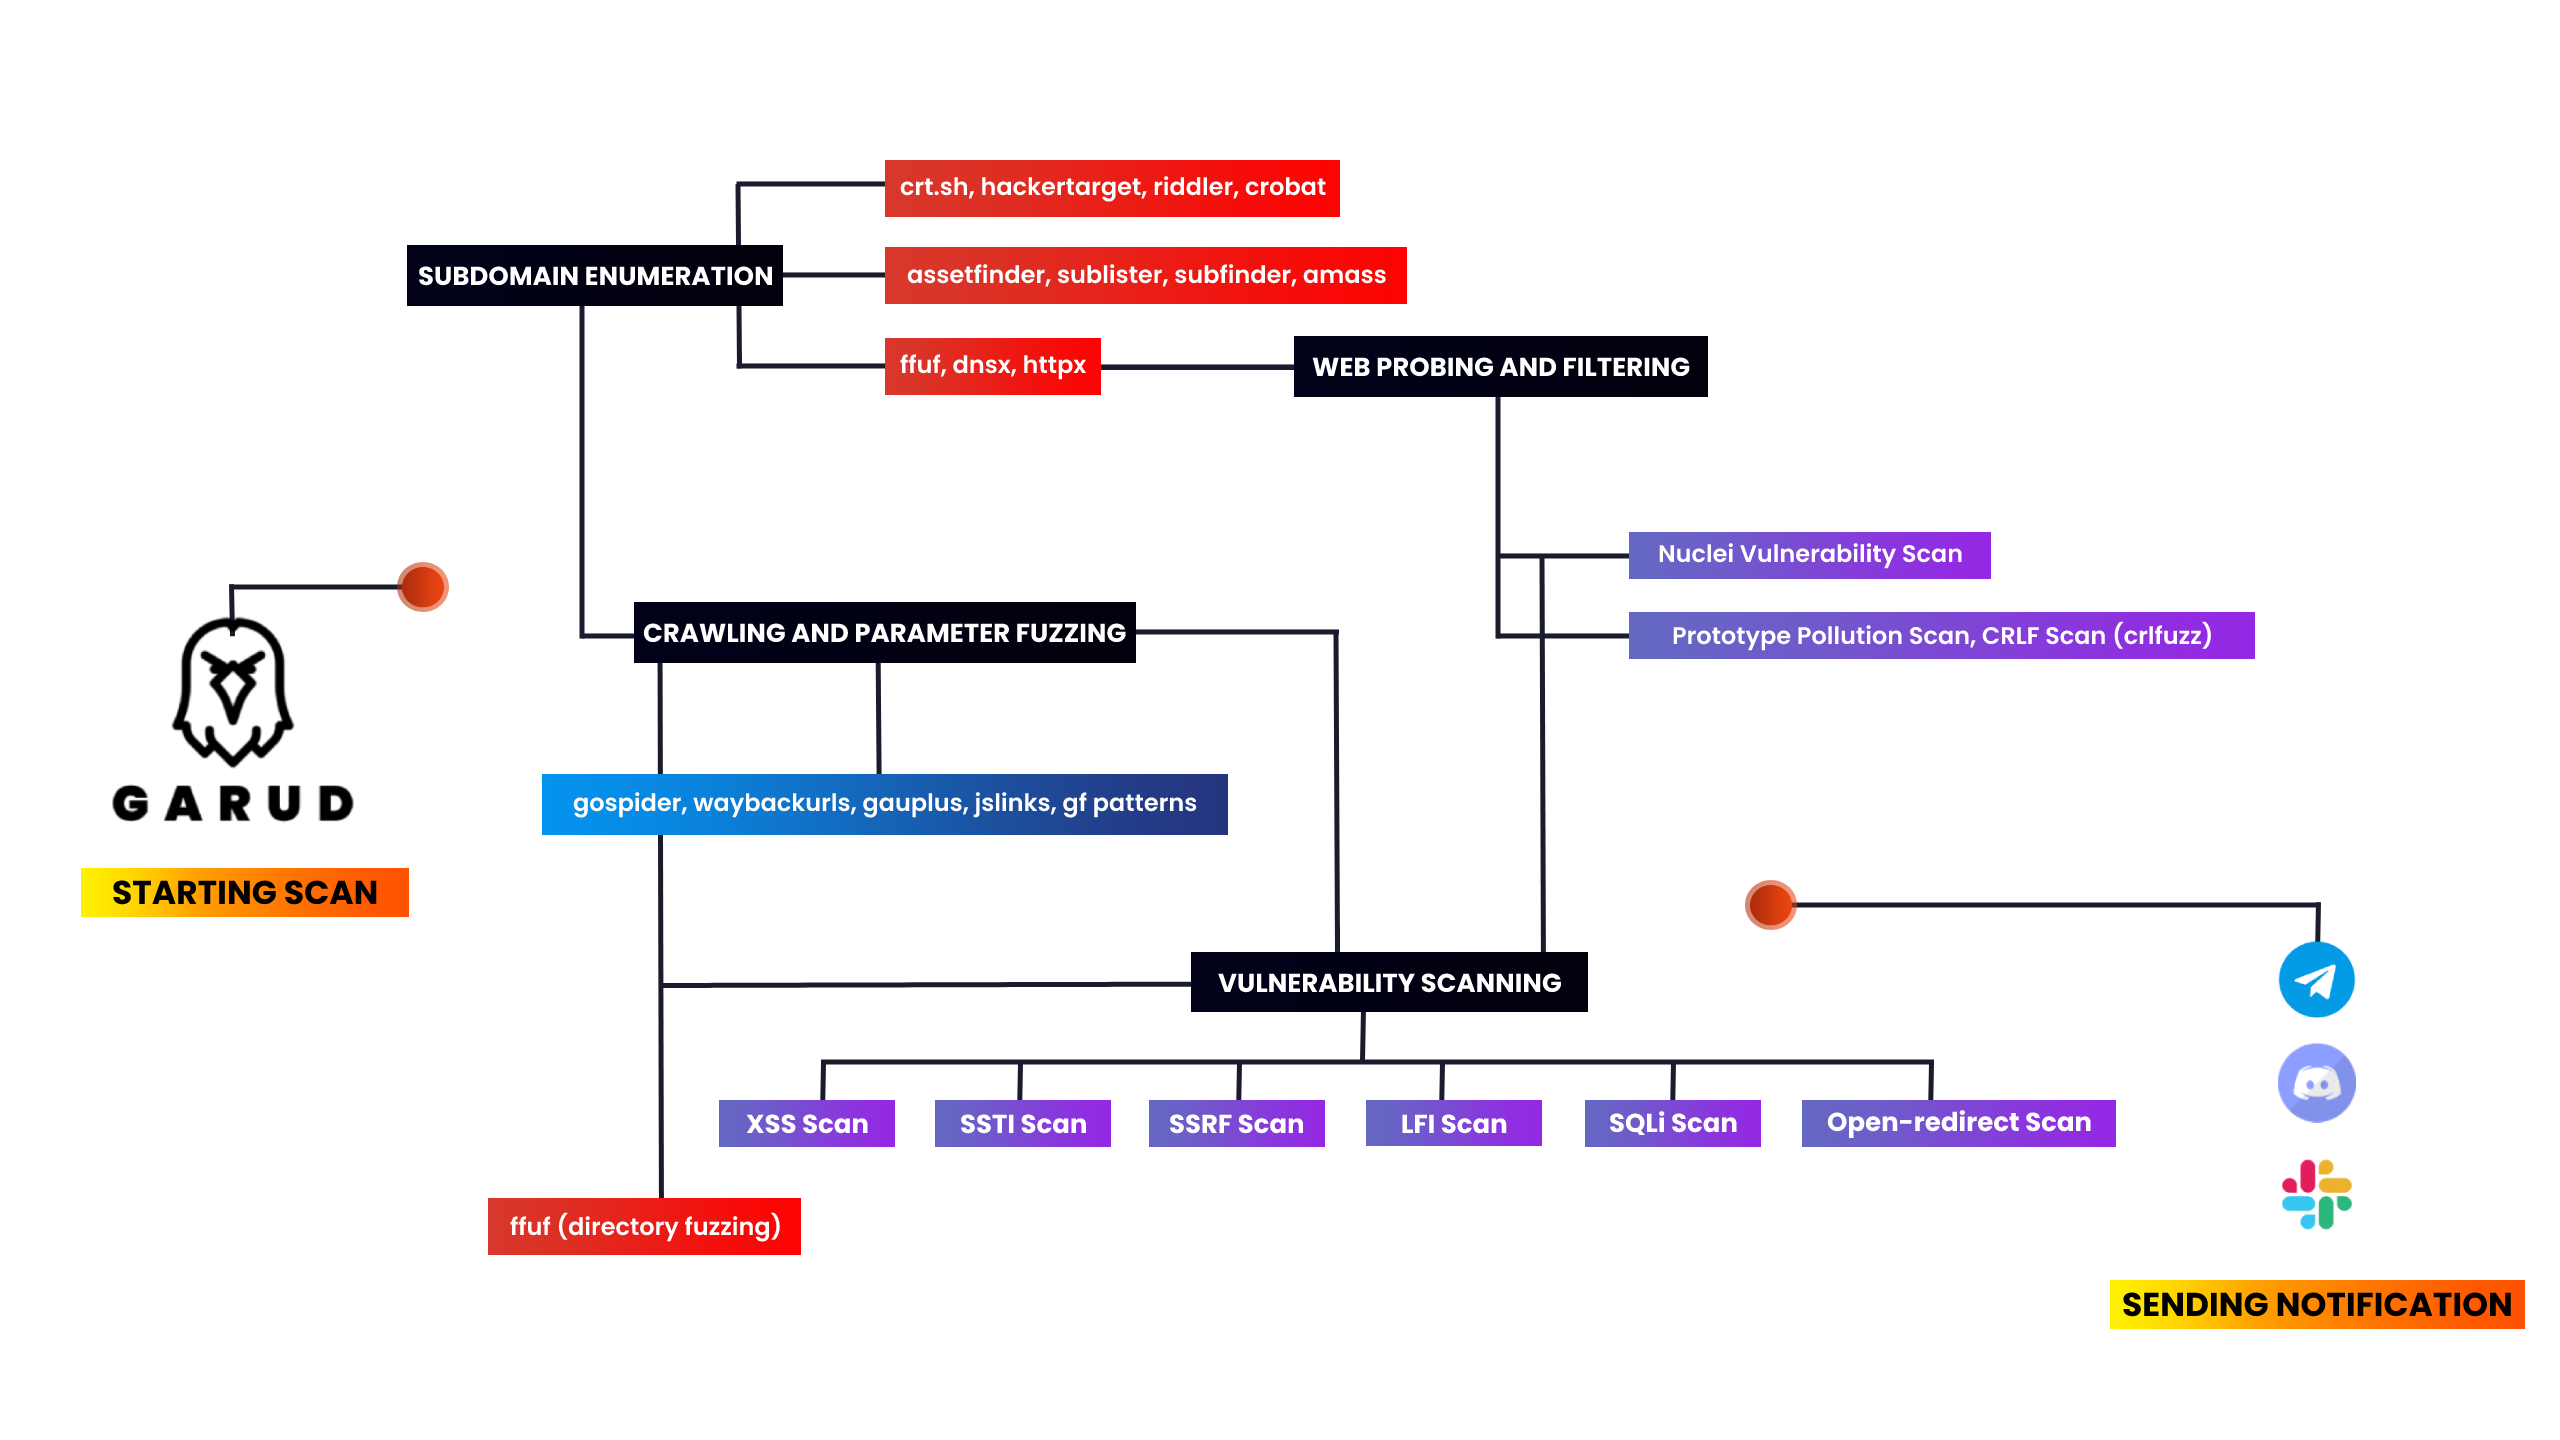
I made this tool to automate my recon and save my time. It really give me headache always type such command and then wait to complete one command and I type other command. So I collected some of the tools which is widely used in the bugbounty field. In this script I used Assetfinder, subfinder, amass, httpx, sublister, gauplus and gf patterns and then it uses dirsearch, dalfox, nuclei and kxss to find some low-hanging fruits.
The script first enumerates all the subdomains of the give target domain using assetfinder, sublister, subfinder and amass then filters all live domains from the whole subdomain list then it extarct titles of the subdomains using httpx then it scans for subdomain takeover using nuclei. Then it uses gauplus to extract paramters of the given subdomains then it use gf patterns to filters xss, ssti, ssrf, sqli params from that given subdomains and then it scans for low hanging fruits as well. Then it'll save all the output in a text file like target-xss.txt. Then it will send the notifications about the scan using notify.
What's new in v4.0: fixed some previous issues and filter out time waste vulns(you need to find them manually) and added dorking.
Requirements: Go Language and Python 3.
System requirements: Recommended to run on vps with 1VCPU and 2GB RAM.
Tools used - You must need to install these tools to use this script
subfinder •
sublist3r •
gf patterns •
dnsx •
assetfinder •
httpx •
kxss •
nuclei •
dalfox •
anew •
notify •
aquatone •
amass •
gau •
crlfuzz •
uro •
ffuf •
naabu •
crobat •
gobuster •
gospider •
waybackurls
#Make sure you're root before installing the tool

garud:~ sudo su
garud:~ apt install git
garud:~ git clone https://github.com/R0X4R/Garud.git && cd Garud/ && chmod +x garud install.sh && mv garud /usr/bin/ && ./install.sh
Note: If you encounter any-issue while running
install.shfile orgarudrunsed -i -e 's/\r$//' install.sh
                █▀▀▀ █▀▀█ █▀▀█ █░░█ █▀▀▄
                █░▀█ █▄▄█ █▄▄▀ █░░█ █░░█
                ▀▀▀▀ ▀░░▀ ▀░▀▀ ░▀▀▀ ▀▀▀░

[GARUD] == A RECONNAISSANCE SUITE FOR BUG BOUNTY (@R0X4R)

Example Usage:
garud [-d target.tld] [-x exclude domains] [--json] [-s]

Flags:
   -d, --domain                 string     Add your target                         -d target.tld
   -x, --exclude                string     Exclude out of scope domains            -x /home/dommains.list

Optional Flags:
   -s, --silent                            Hide output in the terminal             Default: False
   -j, --json                              Store output in a single json file      Default: False
   -v, --version                           Print current version of Garud
Fix errors while using or installing Garud
garud:~ chmod +x install.sh && ./install.sh
Error: ./install.sh : /bin/bash^M : bad interpretor: No such file or directory

# fix
garud:~ sed -i -e 's/\r$//' install.sh
You can also copy the error and search on google this will make your debugging skills better ;)
Example Usage
# garud -d hackerone.com
Exclude out of scope domains
# echo test.hackerone.com > ossdomain.txt
# garud -d hackerone.com -x ~/ossdomain.txt
With all flags
# garud -d hackerone.com -j -s -x /home/oss.txt
Hide output in the terminal
# garud -d hackerone.com -s
Store output in a single json file
# garud -d hackerone.com -s -j
# cd hackerone
# cat output.json | jq
{
  "nuclei_critical": [],
  "vuln_crlf": [],
  "dalfox": [
    "[POC][V][GET][inATTR-double(3)-URL] http://subdomain.target.tld/hpp?pp=FUZZ%22onpointerout%3Dconfirm.call%28null%2C1%29+class%3Ddalfox+",
    ----------------------snip----------------------
    "subdomains": [
      "sub.target.tld",
      "tub.target.tld",
      "subdomain.target.tld"
  ],
  "vuln_xss": [
    "[POTENTIAL XSS] - http://subdomain.target.tld/hpp/?pp=%22%3E%2F%3E%3Csvg%2Fonload%3Dconfirm%28document.domain%29%3E ",
    "[POTENTIAL XSS] - http://subdomain.target.tld:80/hpp/?pp=%22%3E%2F%3E%3Csvg%2Fonload%3Dconfirm%28document.domain%29%3E ",
    "[POTENTIAL XSS] - http://subdomain.target.tld:80/hpp/index.php?pp=%22%3E%2F%3E%3Csvg%2Fonload%3Dconfirm%28document.domain%29%3E "
  ]
}
Docker
Contributed by @frost19k
This image needs to be built with Buildkit
garud:~ git clone https://github.com/R0X4R/Garud.git
garud:~ cd Garud
garud:~ docker buildx build -t garud -f Dockerfile .
