
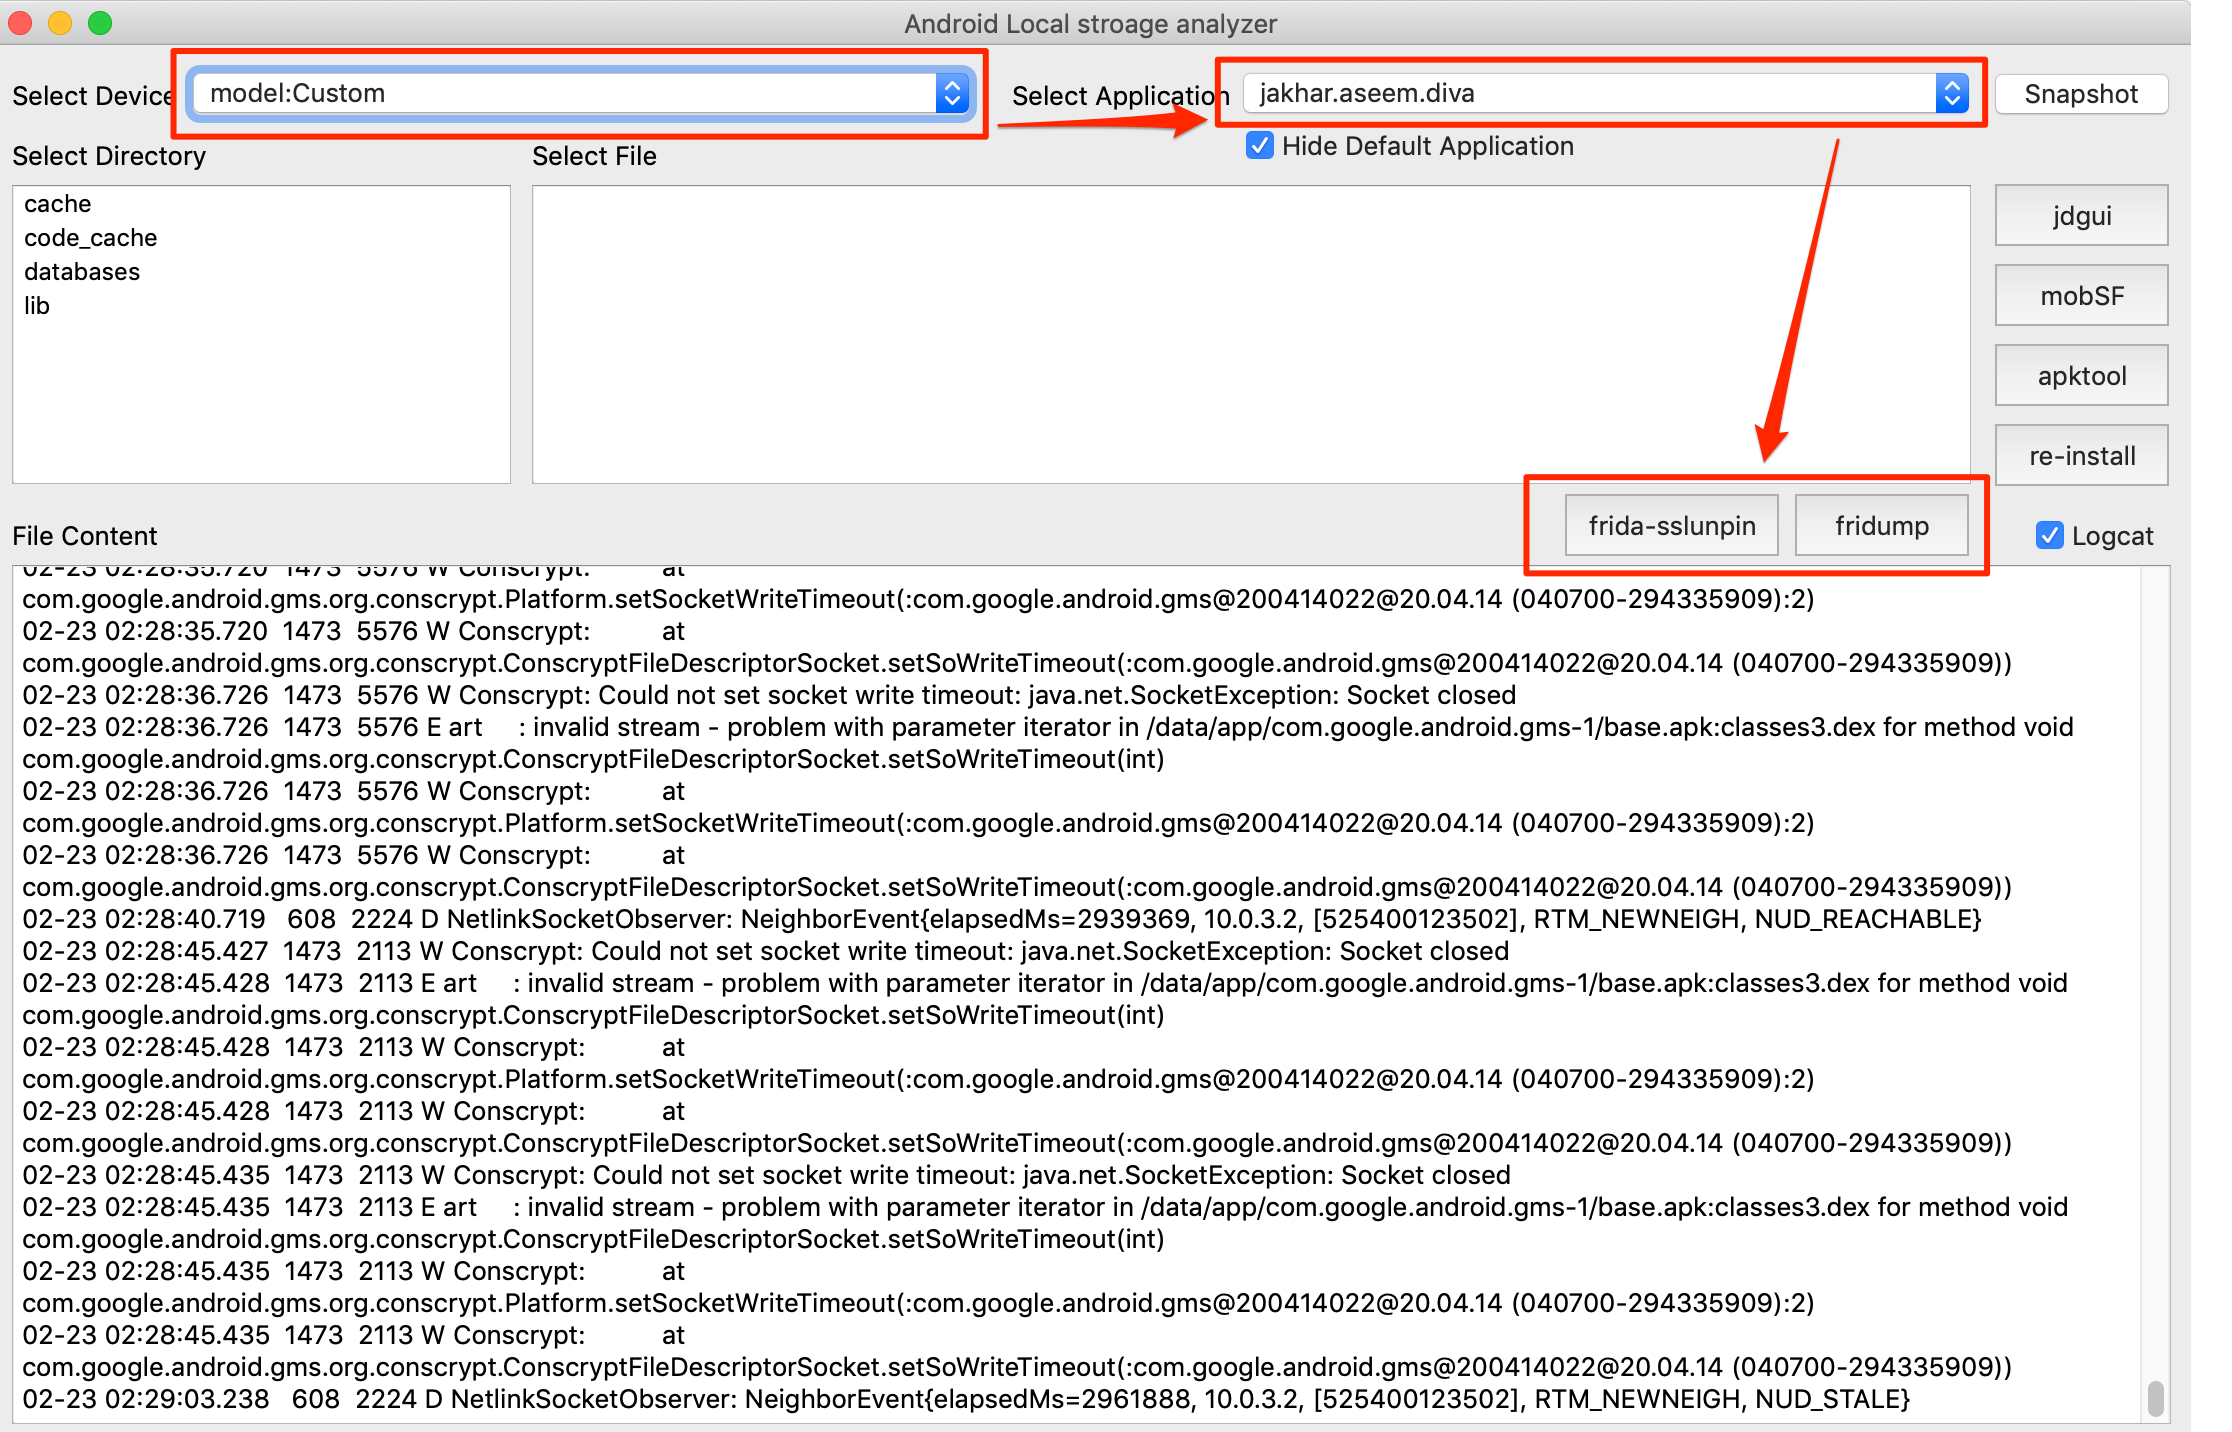
android_application_analyzer
 notsosecure/android_application_analyzer
The tool is used to analyze the content of the android application in local storage.
android-securitydynamic-analysis-sandboxingmobile-app-pentesting+2
175
notsosecure/android_application_analyzerThe tool is used to analyze the content of the android application in local storage.
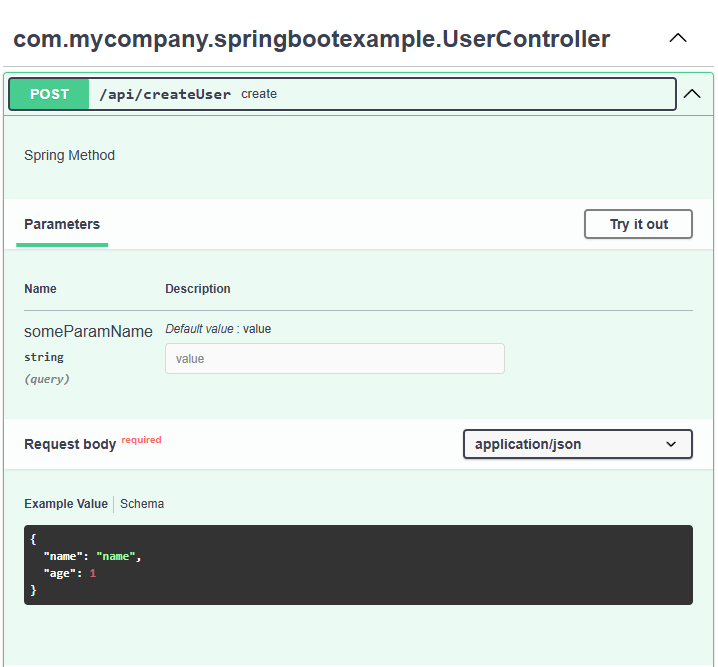 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
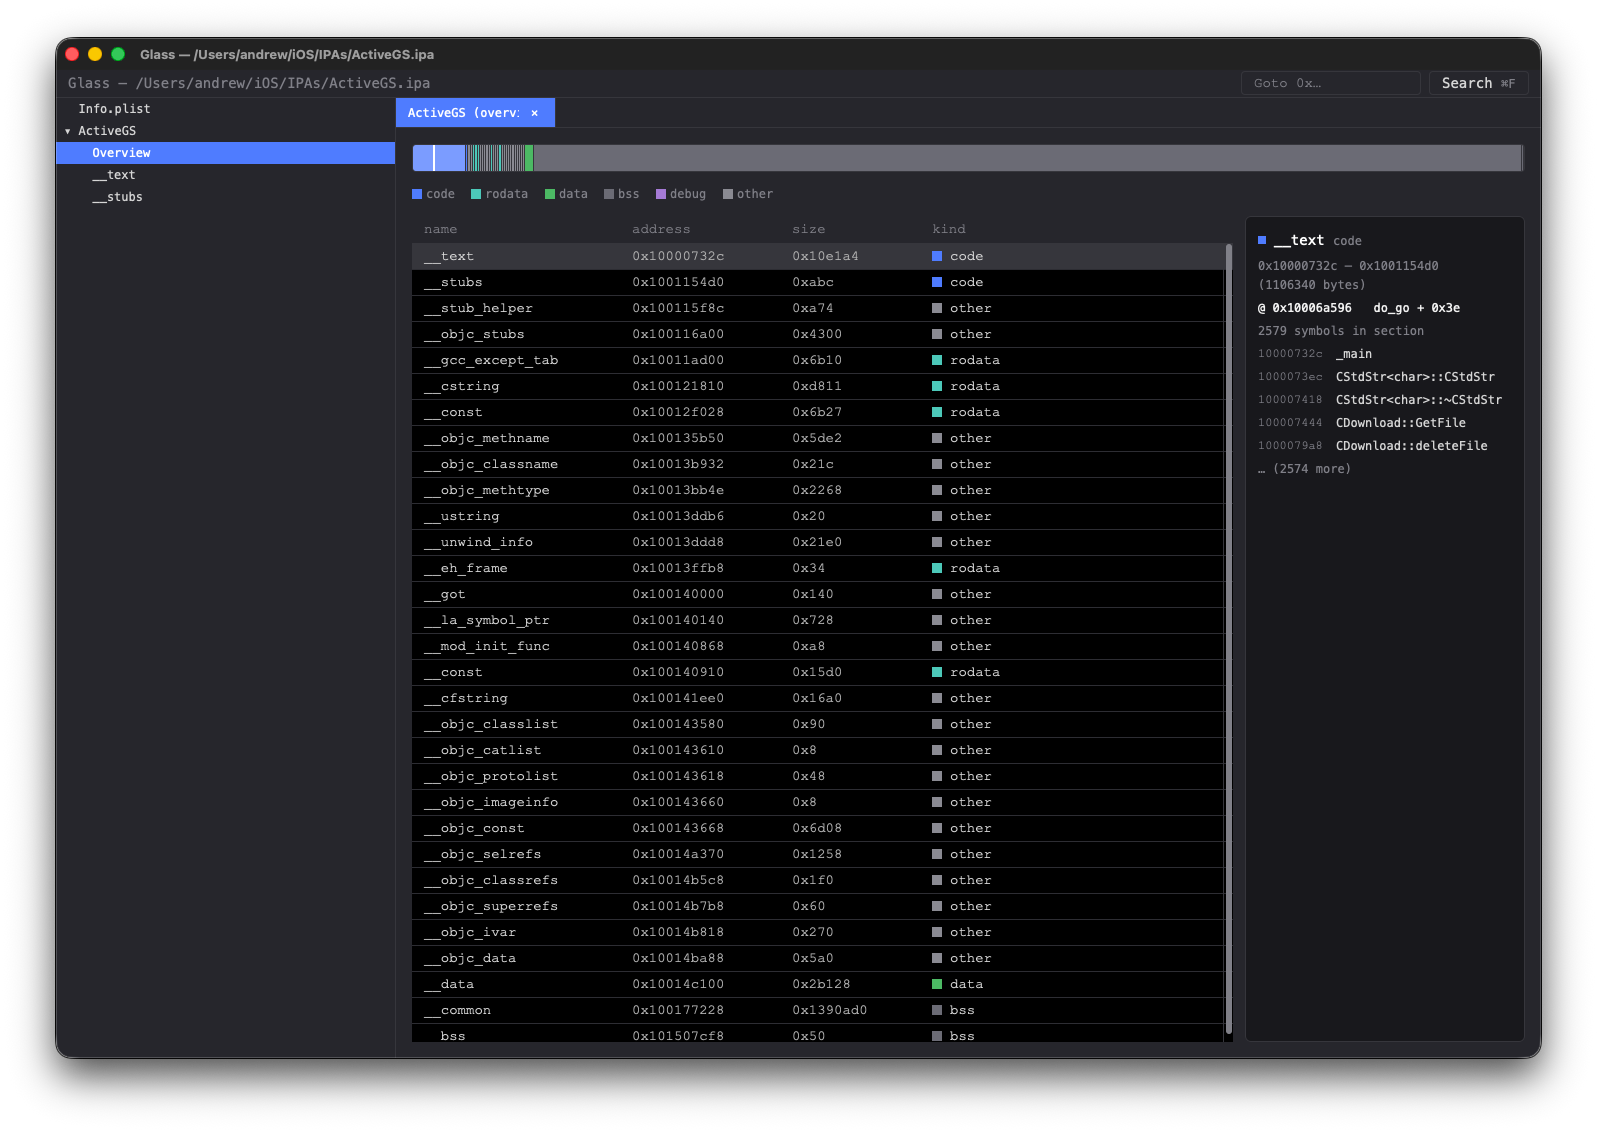 azw413/glass
Glass - a fast and free IDA Pro alternative
 dkhuuthe/madlira
Malware detection using learning and information retrieval for Android
 0xdsm/apepe
Extracts app settings, permissions, deeplinks, and SSL pinning bypass suggestions from Android APK files via static analysis of AndroidManifest.xml,…
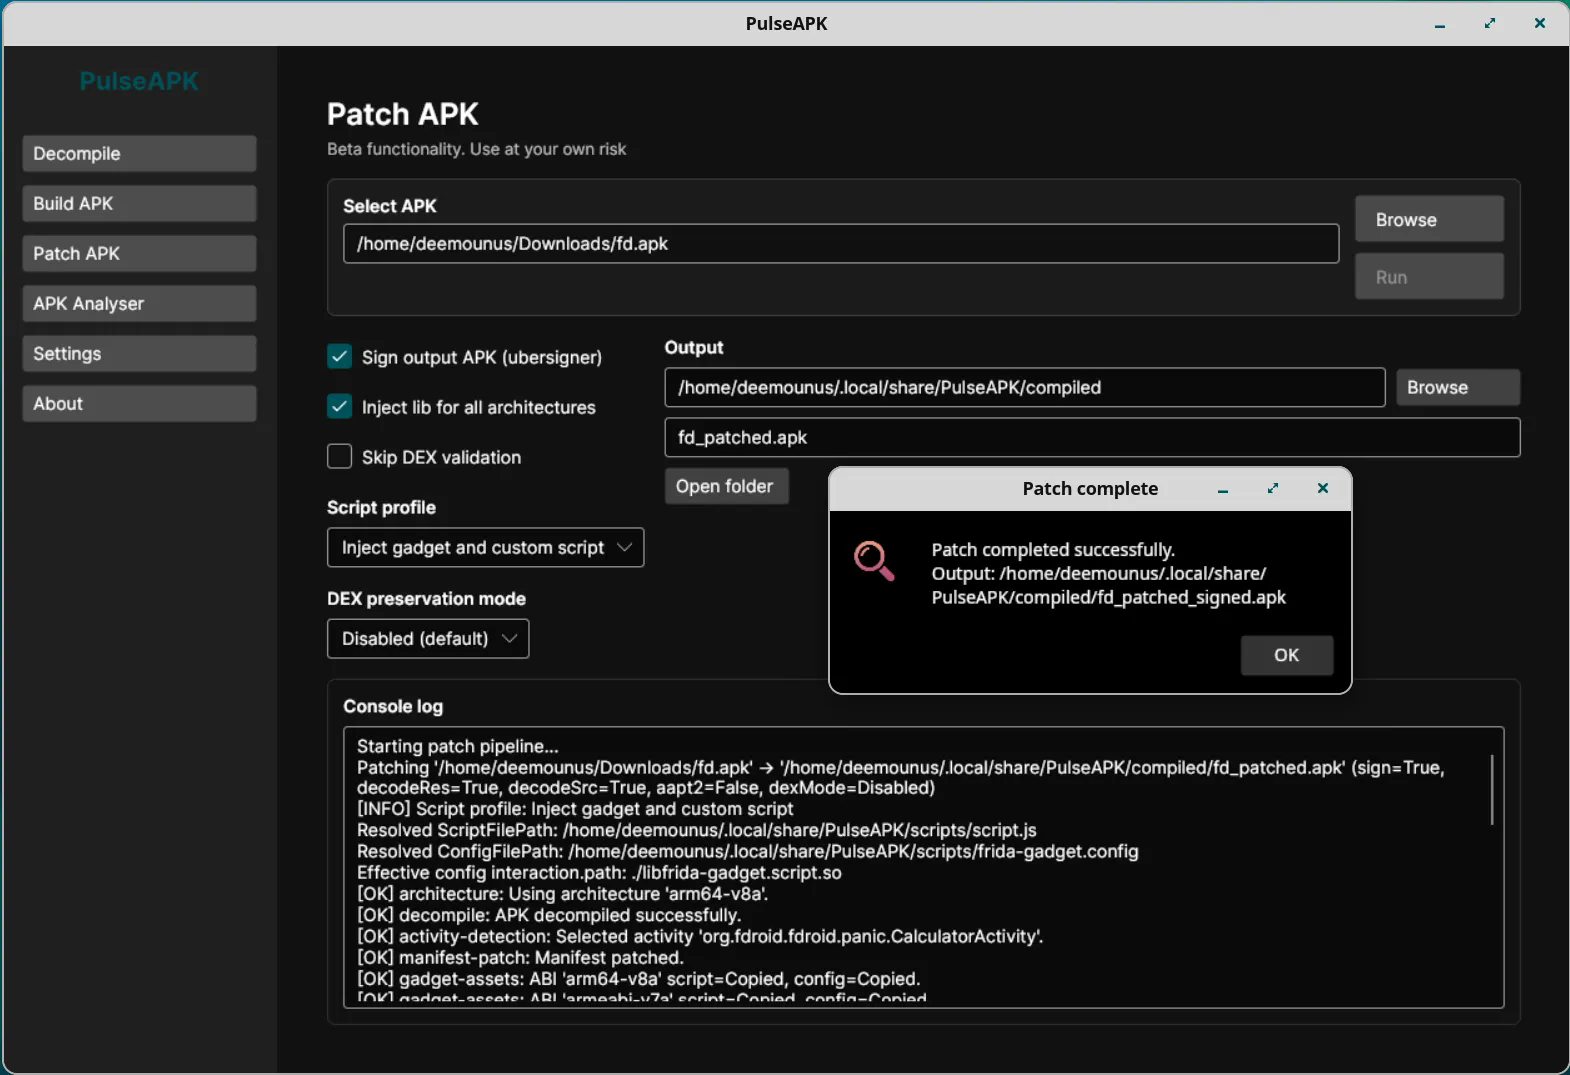 deemoun/pulseapk-core
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building
 alterakey/trueseeing
Non-decompiling iOS/Android app vulnerability scanner (DC25 demo lab, CB17)
 maldroid/maldrolyzer
Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
 user1342/droiddetective
A machine learning malware analysis framework for Android apps.
 kishorbal/deep-c
Android deeplink misconfiguration detector and exploitation tool
 stefan2200/aparoid
Static and dynamic Android application security analysis
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 ultrasina/androidreverse
Android reverse engineering entirely on-device. Radare2 binary analysis, 8 Java decompilers, Flutter & Unity il2cpp support.
 nightwatchcybersecurity/truegaze
Static analysis tool for Android/iOS apps focusing on security issues outside the source code
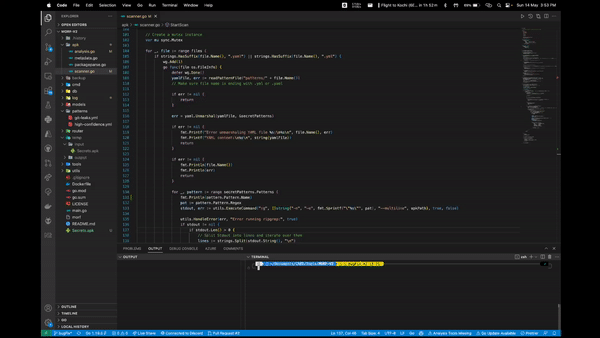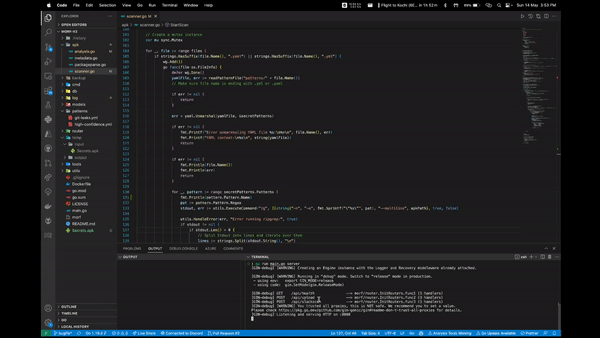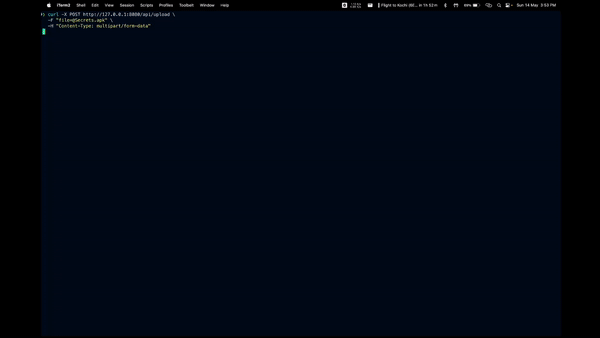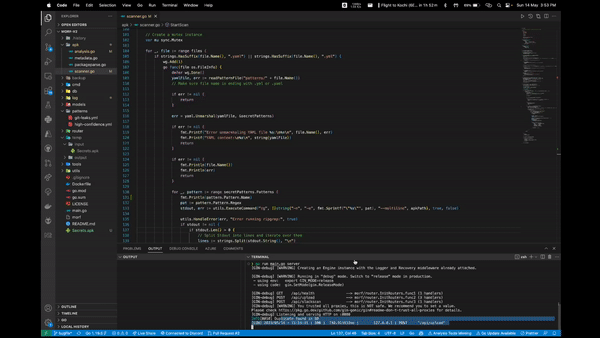 amrudesh1/morf
Mobile Reconnaissance Framework is a powerful, lightweight and platform-independent offensive mobile security tool designed to help hackers and…
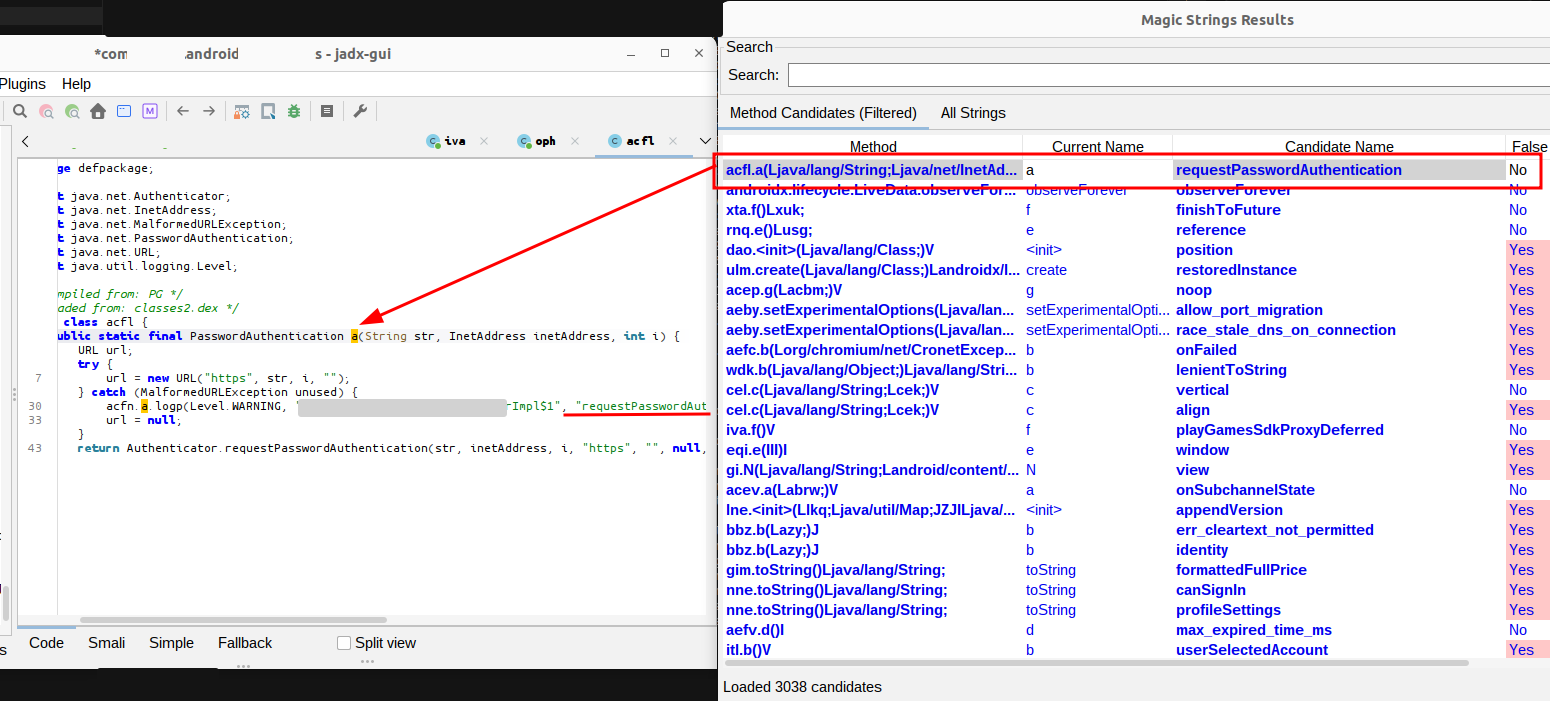 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
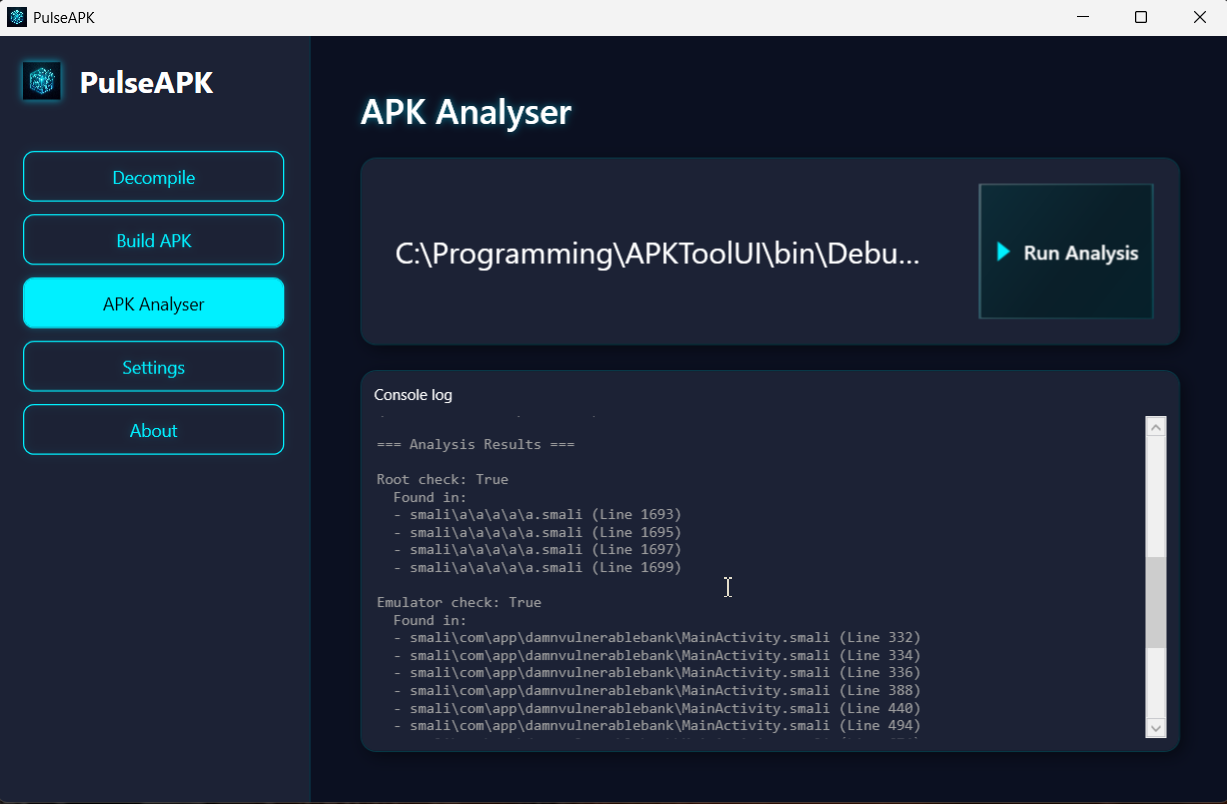 deemoun/pulseapk
PulseAPK is a WPF frontend for apktool and uber-signer with drag-and-drop support, live decompilation output, smali analysis, and integrated APK…
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…