
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
deep-C β€” Android deeplink misconfiguration detector and exploitation tool | Kitploit
Tools/GitHubGitHub/kishorbal/deep-c
Android SecurityStatic AnalysisDynamic Analysis (Sandboxing)Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingMobile SecurityRed TeamingAI Security
9111408 months agoReviewed by Kitploit
Share
GitHubkishorbal/deep-c

deep-C

Android deeplink misconfiguration detector and exploitation tool

View Repository

Deep-C

Deep-C is an Android Deep Link Exploitation Framework that automatically decompiles APKs, identifies exposed and insecure deep link entry points, validates exploitability using static analysis and optional AI verification, and generates executable adb Proof-of-Concepts (PoCs).

Deep-C is designed for mobile application penetration testing, red team assessments, and Android security research, with a strong focus on real-world exploitability rather than noisy findings.

WebdeepC -(Web version)
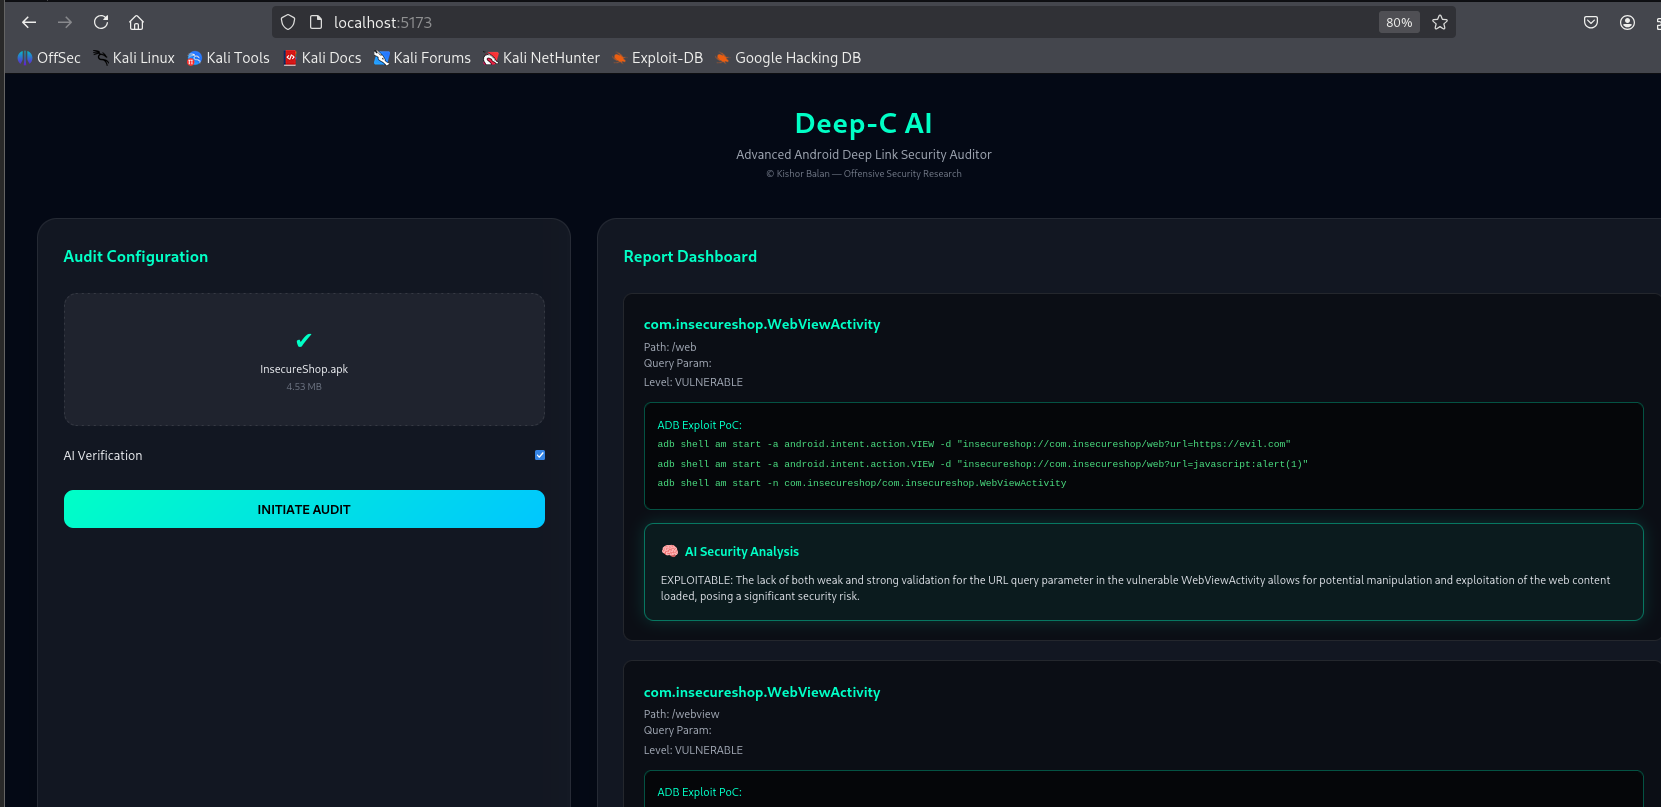
image

CLI image


✨ Features

πŸ“¦ APK Analysis

  • Automatic APK decompilation using apktool
  • Bytecode processing using dex2jar
  • Java source recovery using jadx

πŸ” Deep Link Discovery

  • Custom scheme deep links
  • App links (http / https)
  • Exported and browsable activities
  • Intent filter analysis (VIEW + BROWSABLE)

πŸšͺ Exported Component Detection

  • Exported activity identification
  • Deep link entry-point enumeration
  • Custom scheme reachability analysis

🌐 WebView Abuse Identification

  • Detection of attacker-controlled data reaching WebView.loadUrl
  • Identification of unsafe URL handling
  • Java & Kotlin (jadx-decompiled) code support

⚠️ Insecure Deep Link Pattern Detection

  • Missing or improper host validation
  • Weak validation logic (endsWith, contains, regex)
  • Unsafe custom scheme handling
  • Sensitive paths:
    • login
    • reset
    • wallet
    • payment
    • admin / privileged flows

🎯 Attack Mapping

  • Intent hijacking
  • Open redirects
  • Authentication bypass via deep links
  • WebView URL injection
  • Arbitrary URL loading

πŸ€– AI-Assisted Vulnerability Verification (Optional)

  • Optional ChatGPT-based AI review (--ai-review)
  • AI acts as a second-pass security reviewer
  • Confirms exploitability based on:
    • Decompiled source code
    • Intent data flow
    • Validation logic
  • Reduces false positives
  • AI never invents findings β€” it only validates existing ones
  • AI verdict is merged safely with static confidence

AI integration is opt-in and disabled by default.


πŸ§ͺ Proof-of-Concept (PoC) Generation

  • Scheme-aware PoC generation
  • Custom scheme handling
  • Multiple payload variants:
    • external URLs
    • javascript: payloads
  • Executable adb commands
  • Optional auto-execution of PoCs

πŸ“€ Output & Reporting

  • Clear, human-readable console output
  • Structured JSON result file
  • Includes:
    • Static confidence
    • AI confidence (if enabled)
    • Final merged confidence
    • Reasoning
    • Generated PoCs

How Deep-C Works

πŸ”„ High-Level Workflow

APK
 ↓
Decompile APK (apktool)
 ↓
Extract Manifest & Bytecode
 ↓
Identify Exported Deep Link Entry Points
 ↓
Decompile Source (dex2jar + jadx)
 ↓
Validate Exploitability (code / heuristics)
 ↓
(Optional) AI Verification (--ai-review)
 ↓
Generate adb PoCs
 ↓
Console Output + JSON Report

πŸ”§ Requirements

Make sure the following tools are installed and available in your PATH:

Python 3.8+ apktool adb (Android Platform Tools) d2j-dex2jar openai

Verify Installation apktool --version adb version python3 --version

For AI Based analysis (openAI)

Export your openAI API key to the enviornment variables

export OPENAI_API_KEY="Your_openai_API_key"

Usage

πŸ” Analyze APK (No Exploitation) python deepc.py -a target.apk

πŸ’₯ Analyze + Execute PoCs via adb python deepc.py -a target.apk --exec

⚠️ Ensure a device/emulator is connected via adb before using --exec.

Download Tool

Most Popular

View all β†’

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    524
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    478
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    357
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    317
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    305
  • 6

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    275

Explore all tools

Browse our collection of tools

View all tools β†’






