
craft-anything
 storytold/craft-anything
Pure-Rust reverse-engineering engine with 314 CLI/MCP inspection tools (disassembly, decompilation, strings, call graphs) that studies any app, site…
ai-assisted-reversingai-securitybinary-analysis+9
4.6k
storytold/craft-anythingPure-Rust reverse-engineering engine with 314 CLI/MCP inspection tools (disassembly, decompilation, strings, call graphs) that studies any app, site…
 ricardoquesada/regenerator2000
An interactive disassembler for the CPU 6502, focused on Commodore 8-bit computers. Features a TUI with modern features like x-ref, undo/redo, flow…
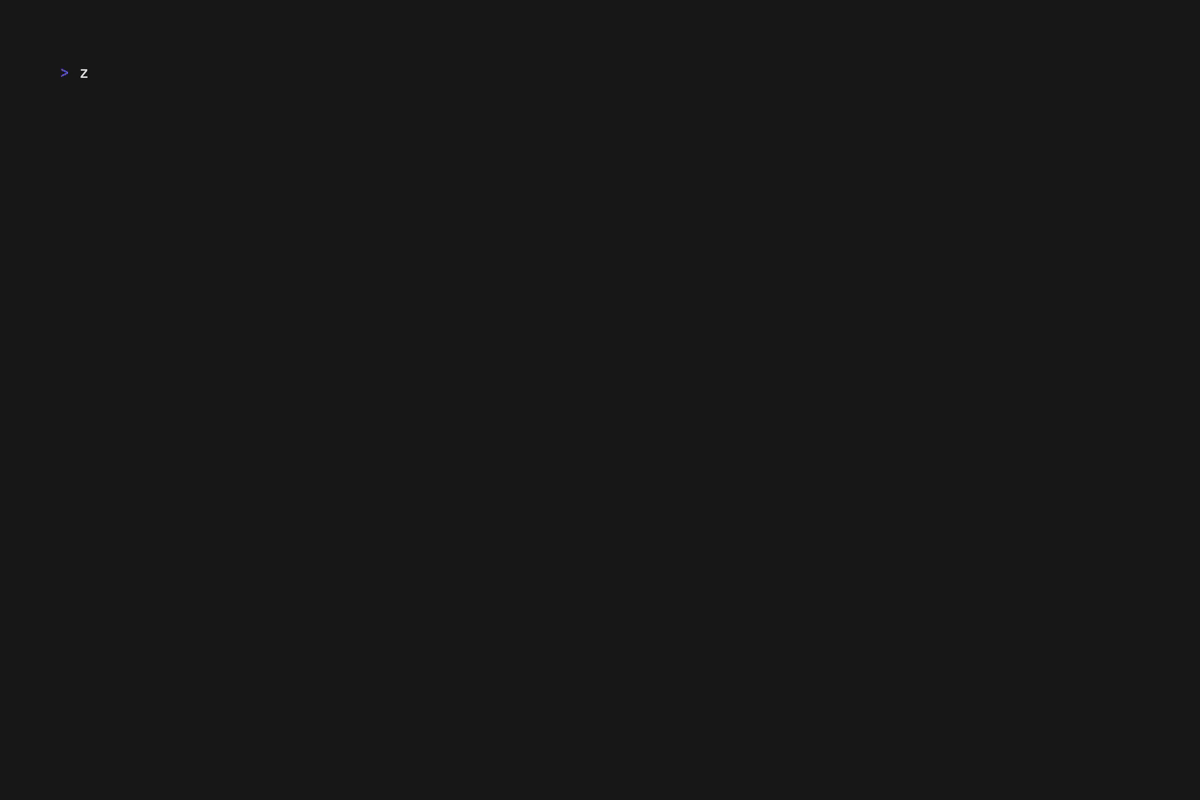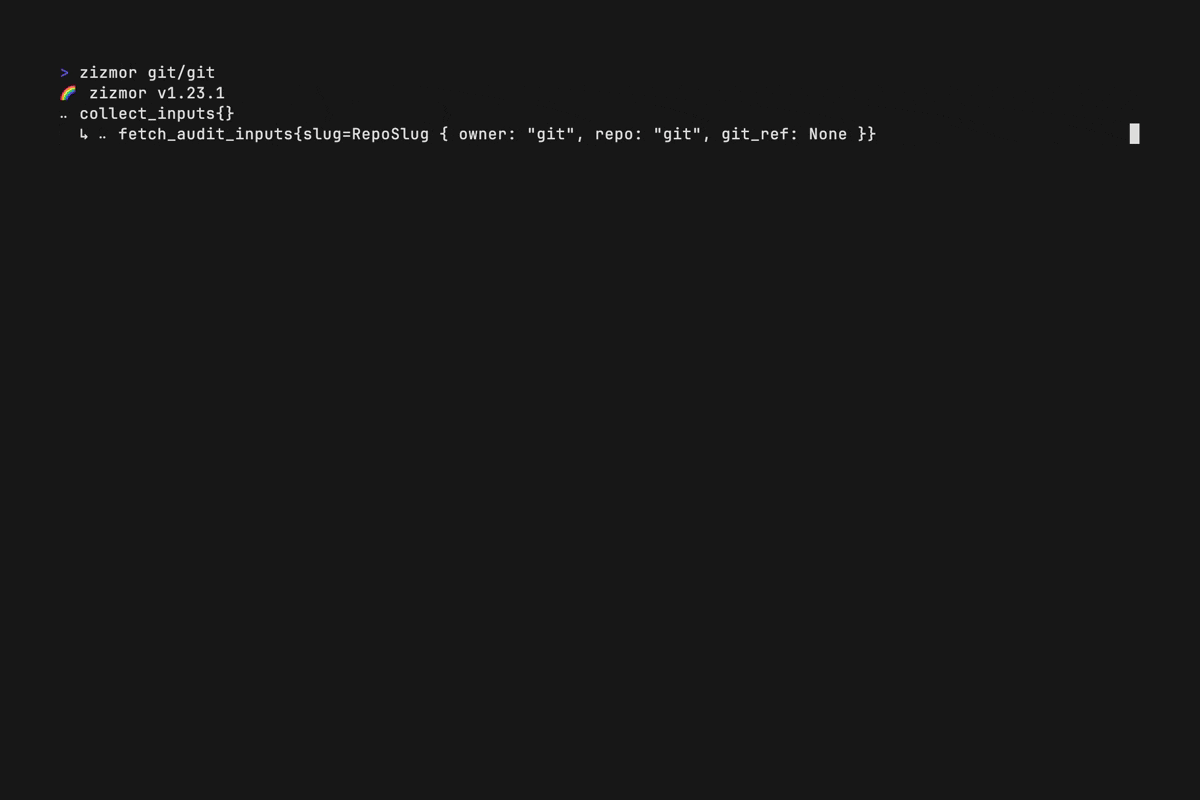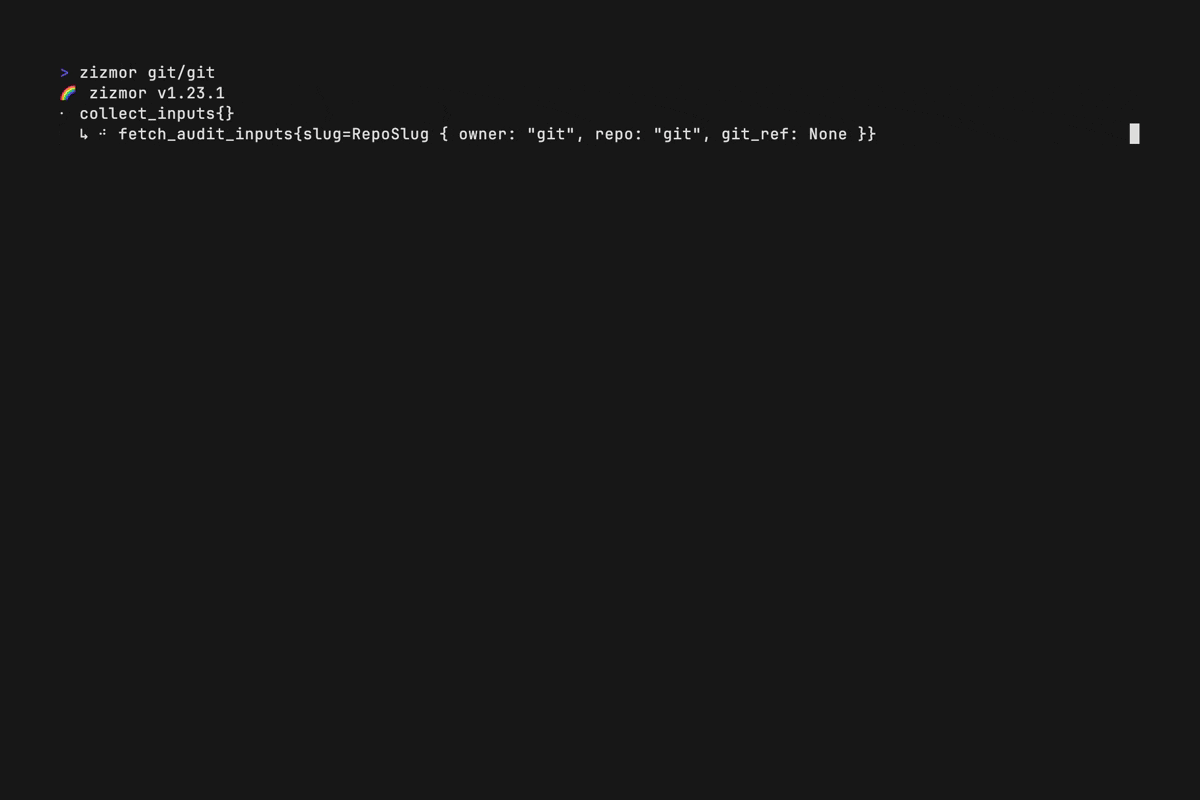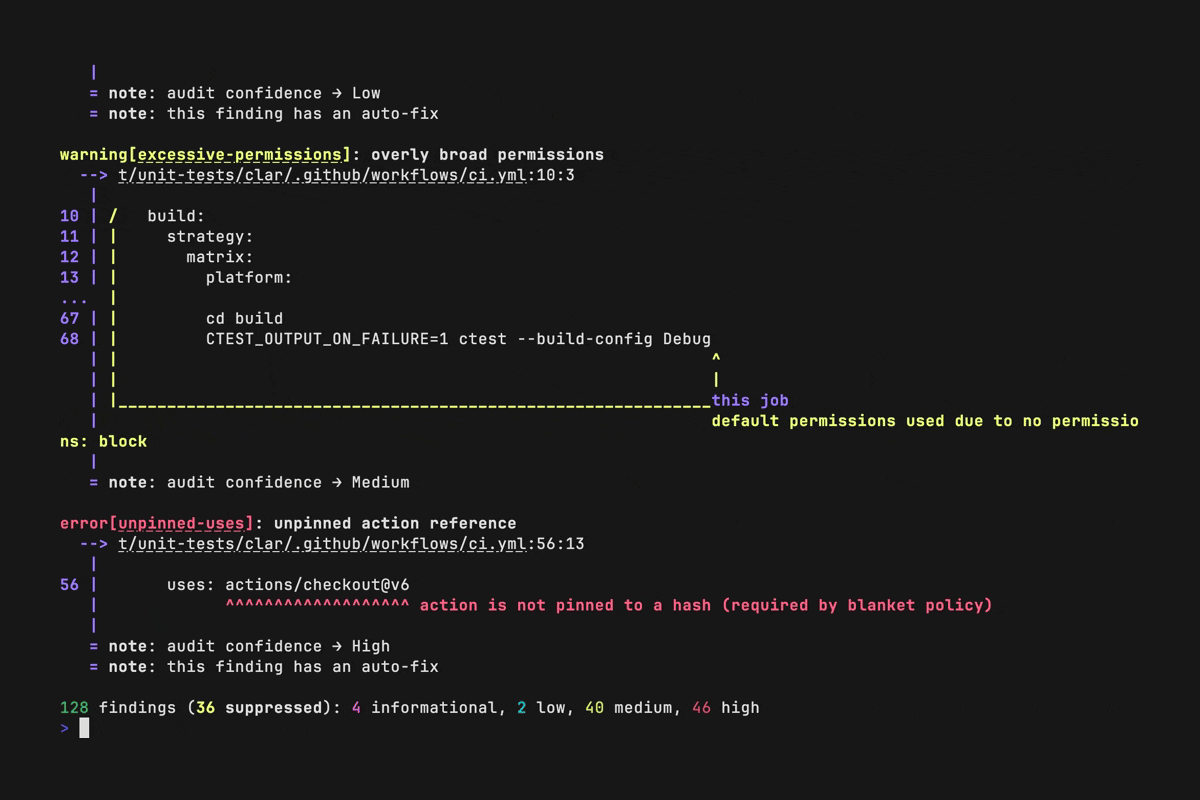 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
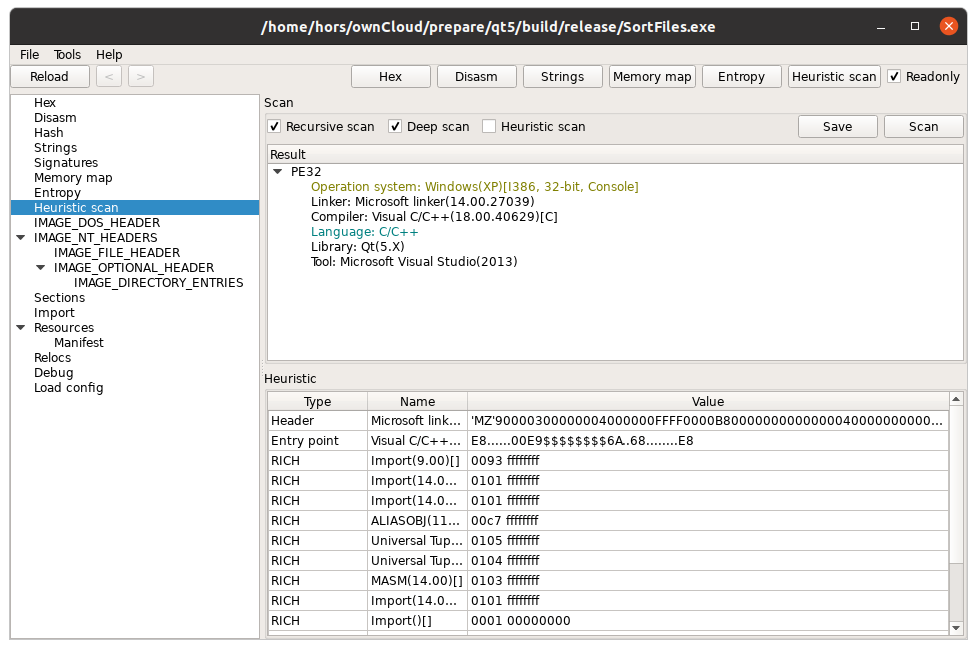 horsicq/xpeviewer
PE file viewer/editor for Windows, Linux and MacOS.
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 loadingalias/rscrypto
Rust cryptography w/ zero required deps: hashes, checksums, MACs, KDFs, password hashing, AEADs, signatures, RSA, key exchange, ML-KEM, and ML-DSA.…
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
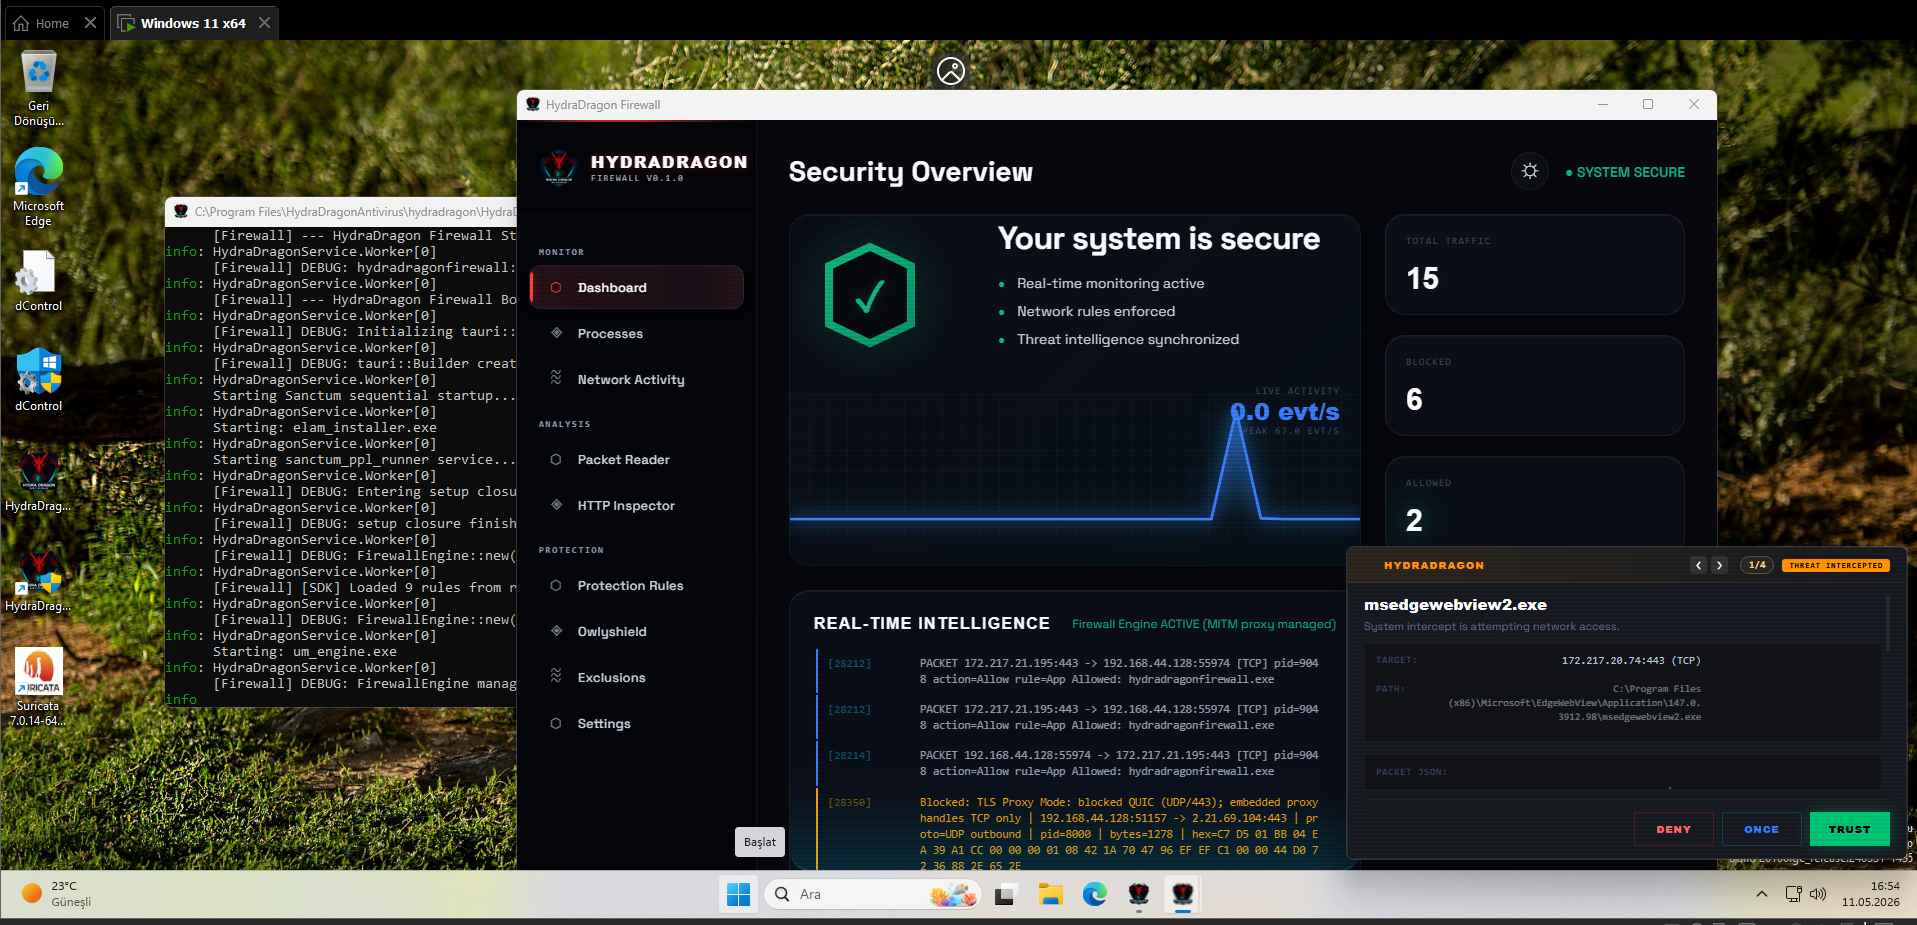 hydradragonantivirus/hydradragonantivirus
Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 trailofbits/skills
Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows

 hashgraph-online/hol-guard
Open-source antivirus and firewall for AI agents: block risky tools, secret access, prompt injection, malicious packages, MCP servers, plugins, and…
 morluto/rea
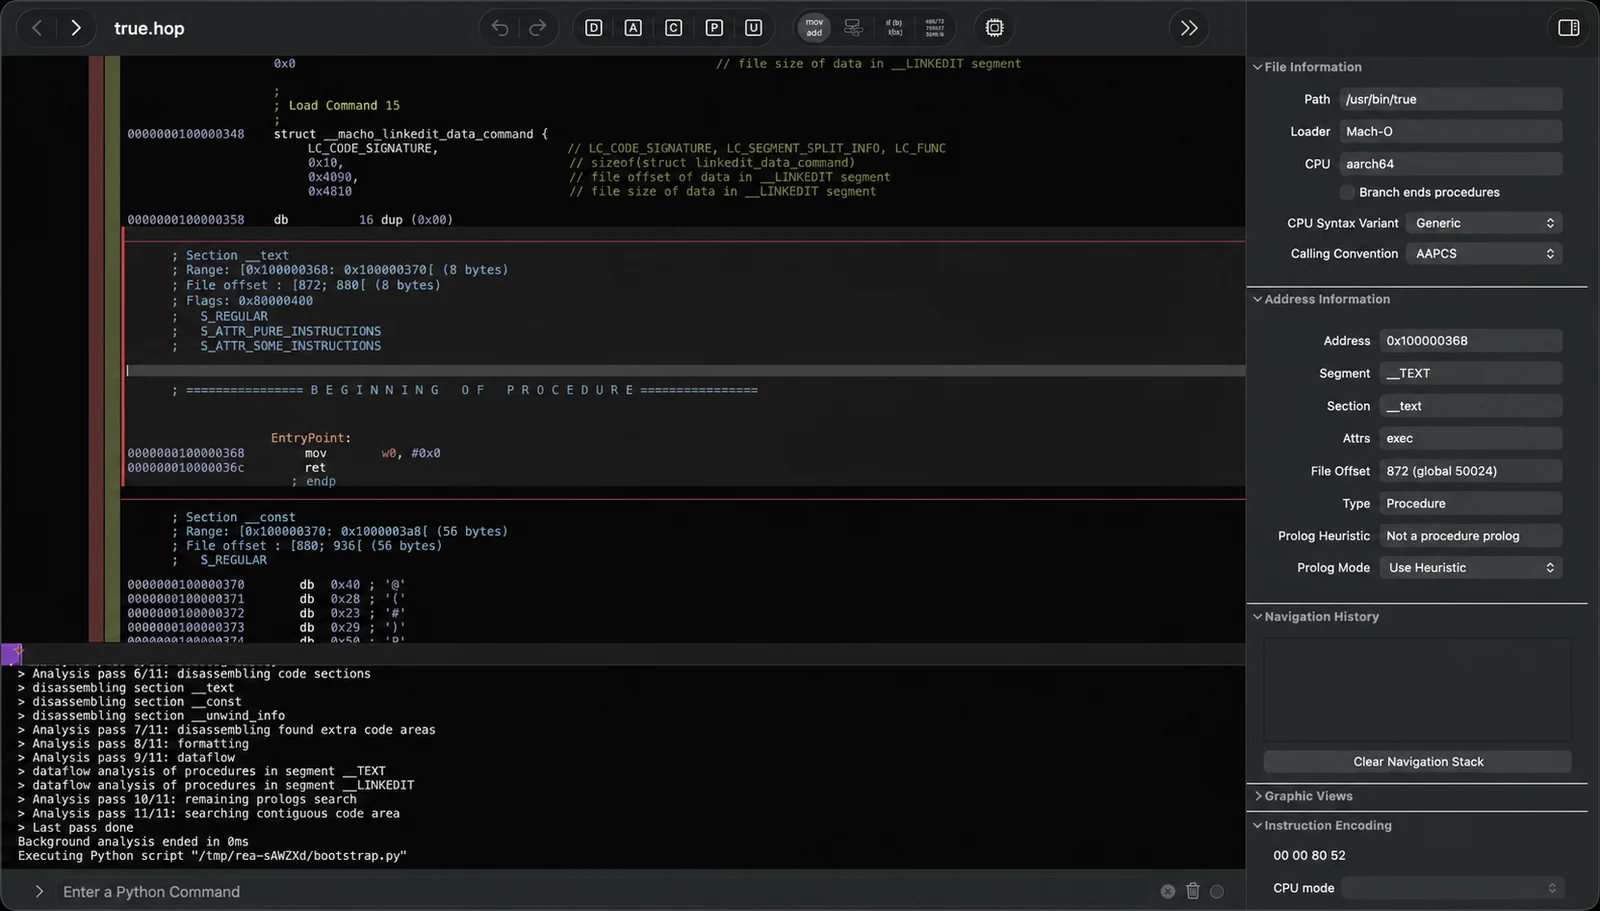
Reverse engineer anything with agents, from app behavior down to native binaries.