

grype
 anchore/grype
A vulnerability scanner for container images and filesystems
container-escapecontainer-securitydevsecops+4
anchore/grypeA vulnerability scanner for container images and filesystems
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 radareorg/r2ai
Radare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…
 owasp/cve-lite-cli
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 huhusmang/awesome-llms-for-vulnerability-detection
The community's most comprehensive, continuously-updated index of research on Large Language Models for software vulnerability detection — papers…
 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
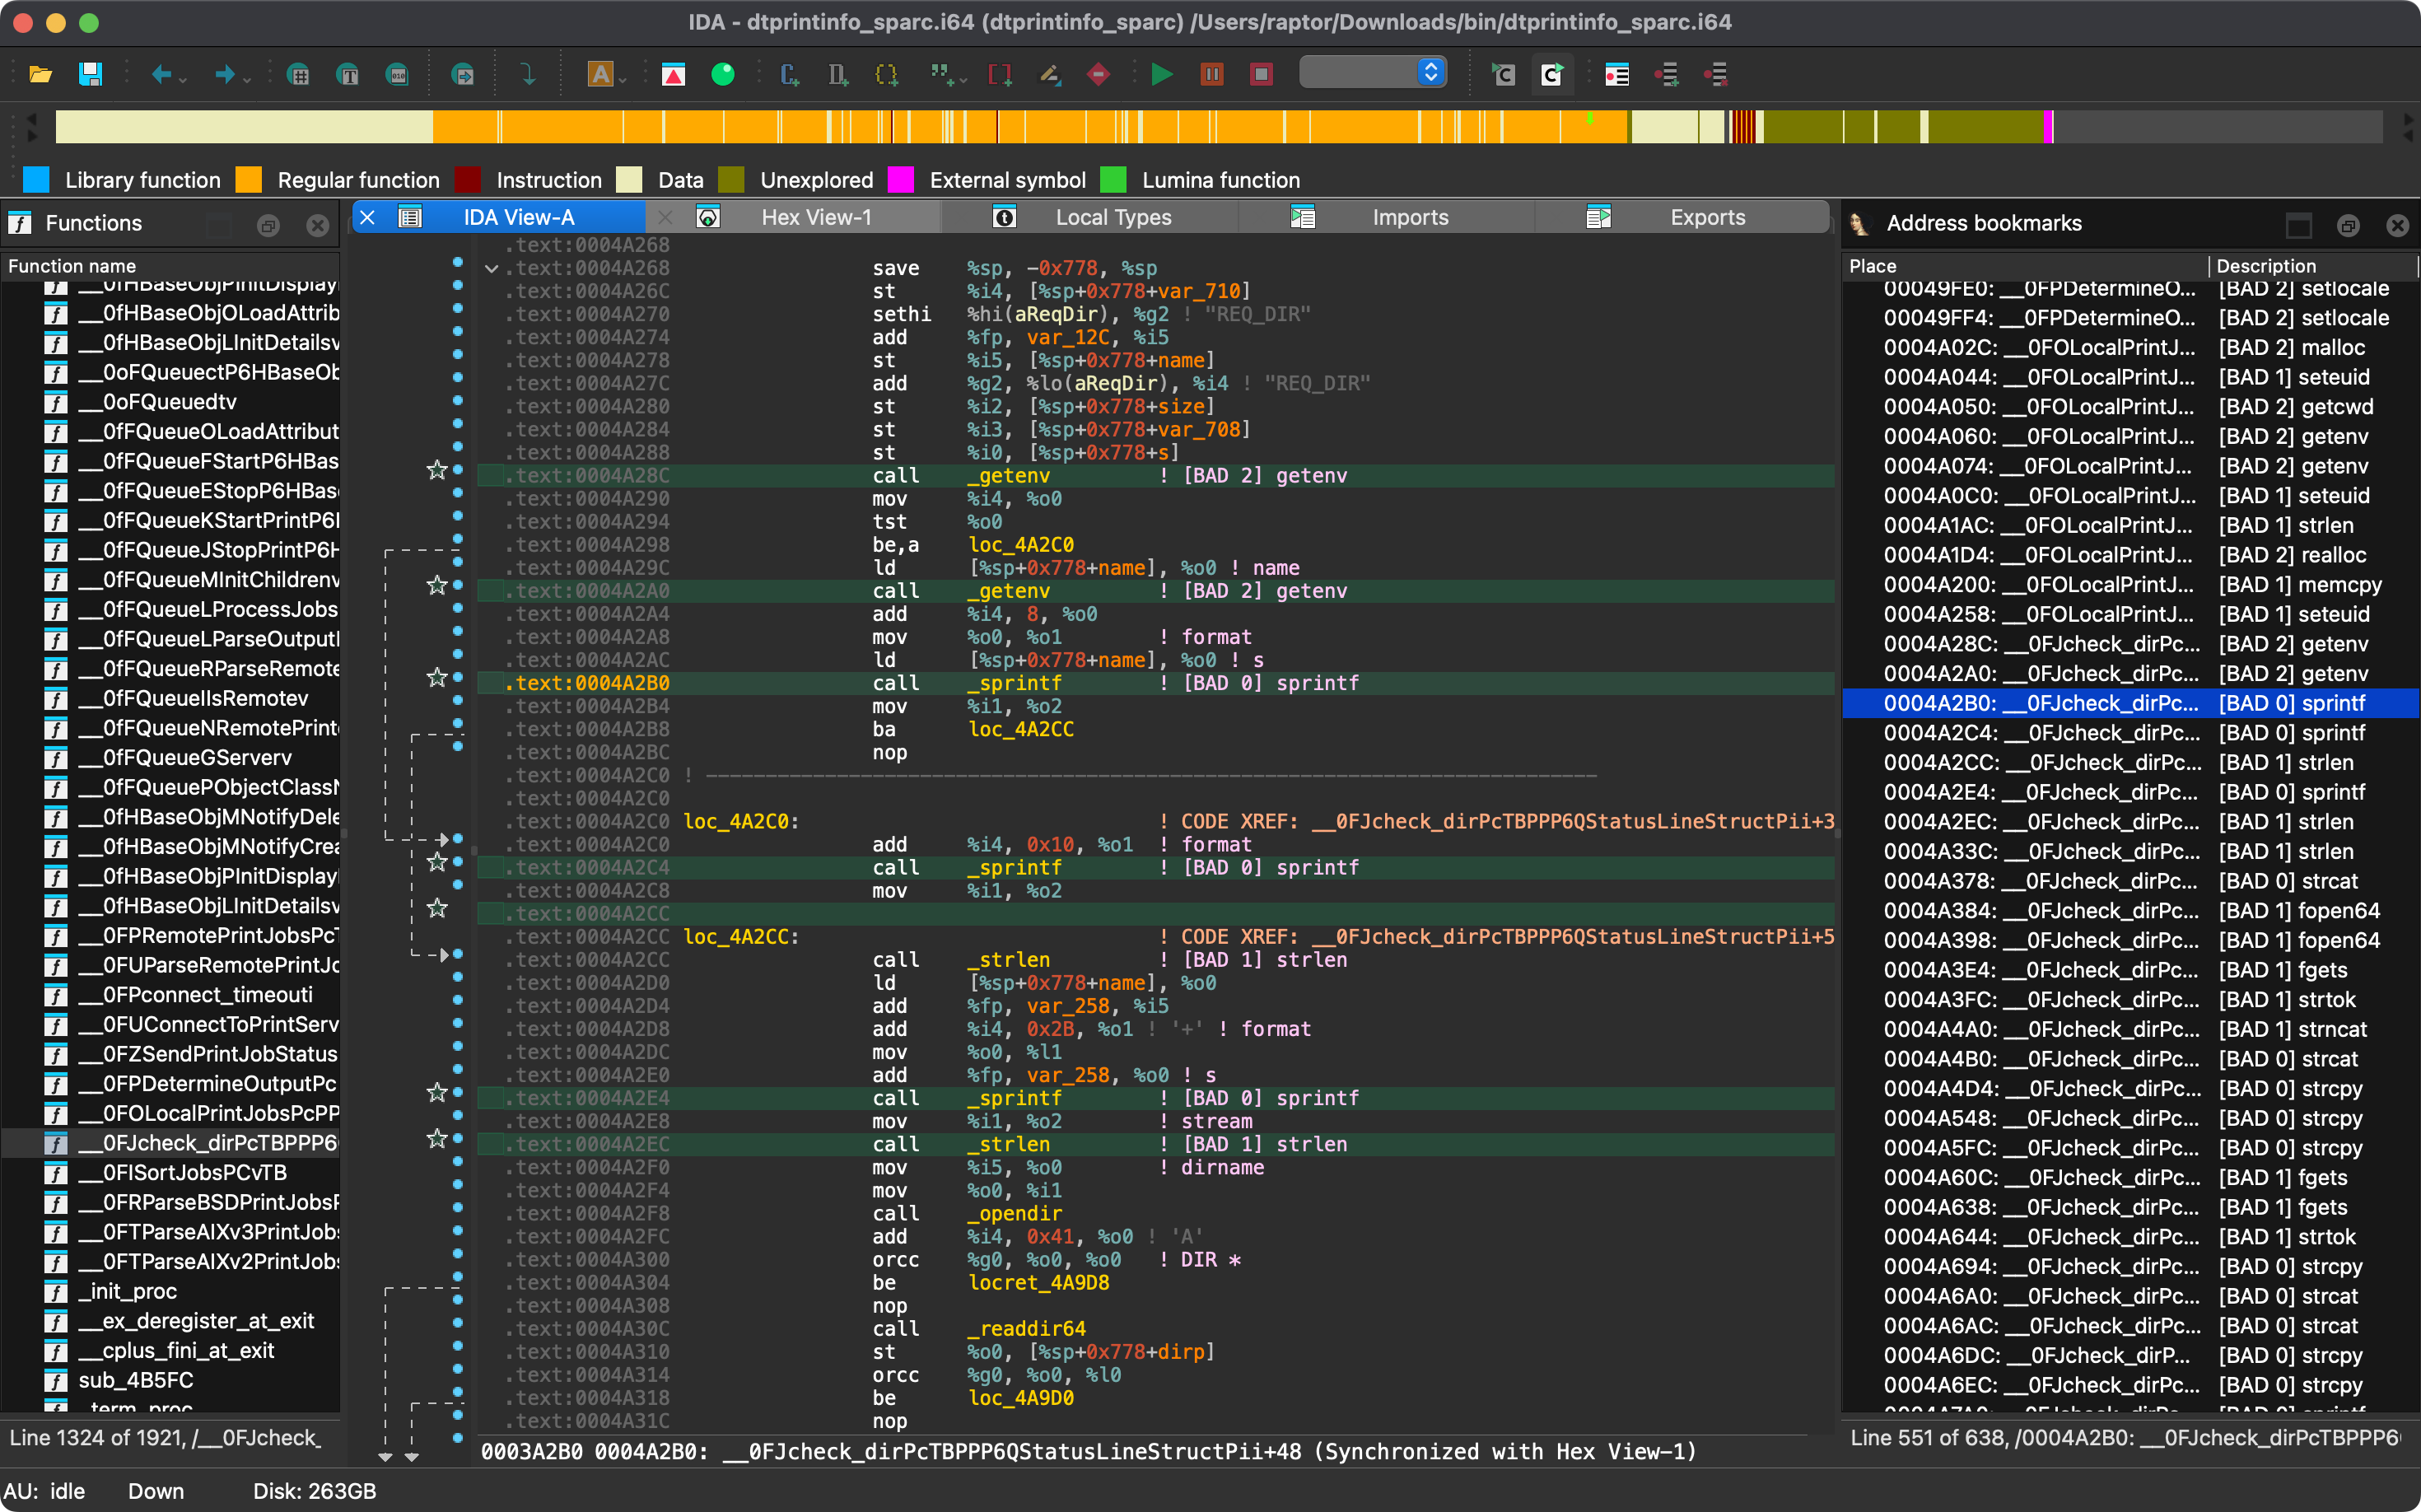 0xdea/rhabdomancer
Vulnerability research assistant that locates calls to potentially insecure API functions in a binary file.
 trailofbits/skills
Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
 mayank729/cve-2025-55182-scanner
🔍 Scan for CVE-2025-55182 risks in React Server Components with this non-intrusive tool that helps detect critical vulnerabilities in your…
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 presidentbeef/brakeman
A static analysis security vulnerability scanner for Ruby on Rails applications
 quay/clair
Vulnerability Static Analysis for Containers
 vercel-labs/deepsec
Agent-powered vulnerability scanner for large-scale codebases. Uses LLMs to find hard-to-detect security issues via regex matchers and AI…
 githubsecuritylab/seclab-taskflow-agent
MCP-enabled multi-agent framework for declarative YAML-driven agentic workflows, used for AI-assisted code auditing, vulnerability triage, and…
 sdodson/cve-2026-46595-proof
Go proof-of-concept demonstrating CVE-2026-46595 in golang.org/x/crypto/ssh, using symbol inspection of stripped binaries and image scans to verify…
 aipeacs/sc3010-computer-security
Using Struts2 and PowerShell to recreate CVE-2017-5638 OGNL Injection vulnerability.