
 synacktiv/octoscan
Octoscan is a static vulnerability scanner for GitHub action workflows.

Octoscan is a static vulnerability scanner for GitHub action workflows.

Vulnerable workflows for each rule are in testdata, to try the rules: ./octoscan scan testdata.
$ go mod tidy
$ go build
Or with docker:
$ docker pull ghcr.io/synacktiv/octoscan:latest
Octoscan can be run against a local git repository or you can download all the workflows with the dl action:
$ octoscan dl -h
Octoscan.

Usage:
	octoscan dl [options] --org <org> [--repo <repo> --token <pat> --default-branch --max-branches <num> --path <path> --output-dir <dir> --include-archives]

Options:
	-h, --help  						Show help
	-d, --debug  						Debug output
	--verbose  						Verbose output
	--org <org>  						Organizations to target
	--repo <repo>  						Repository to target
	--token <pat>  						GHP to authenticate to GitHub
	--default-branch  					Only download workflows from the default branch
	--max-branches <num>  					Limit the number of branches to download
	--path <path>  						GitHub file path to download [default: .github/workflows]
	--output-dir <dir>  					Output dir where to download files [default: octoscan-output]
	--include-archives  					Also download archived repositories
./octoscan dl --token ghp_<token> --org apache --repo incubator-answer
If you don't know what to run just run this:
./octoscan scan path/to/repos/ --disable-rules shellcheck,local-action --filter-triggers external
It will reduce false positives and give the most interesting results.
If you have downloaded the workflows with the dl command you might have duplicated workflows since by default octoscan will download all the workflows of all the branches. To delete duplicated workflows and speed up the analysis you can use the fdupes command before running the analysis:
fdupes -n -r -N -d path/to/repo
$ octoscan scan -h
octoscan

Usage:
	octoscan scan [options] --list-rules
	octoscan scan [options] <target>
	octoscan scan [options] <target> [--debug-rules --filter-triggers=<triggers> --filter-run --ignore=<pattern> ((--disable-rules | --enable-rules ) <rules>) --config-file <config>]

Options:
	-h, --help
	-v, --version
	-d, --debug
	--verbose
	--format <format>  				Output format, json, sarif or custom template to format error messages in Go template syntax. See https://github.com/rhysd/actionlint/tree/main/docs/usage.md#format
	--oneline 					Use one line per one error. Useful for reading error messages from programs

Args:
	<target>					Target File or directory to scan
	--filter-triggers <triggers>			Scan workflows with specific triggers (comma separated list: "push,pull_request_target" or pre-configured: external/allnopr)
	--filter-run					Search for expression injection only in run shell scripts.
	--ignore <pattern>				Regular expression matching to error messages you want to ignore.
	--disable-rules <rules>				Disable specific rules. Split on ","
	--enable-rules <rules>				Enable specific rules, this will disable all other rules. Split on ","
	--debug-rules					Enable debug rules.
	--config-file <config>				Config file.

Examples:
	$ octoscan scan ci.yml --disable-rules shellcheck,local-action --filter-triggers external
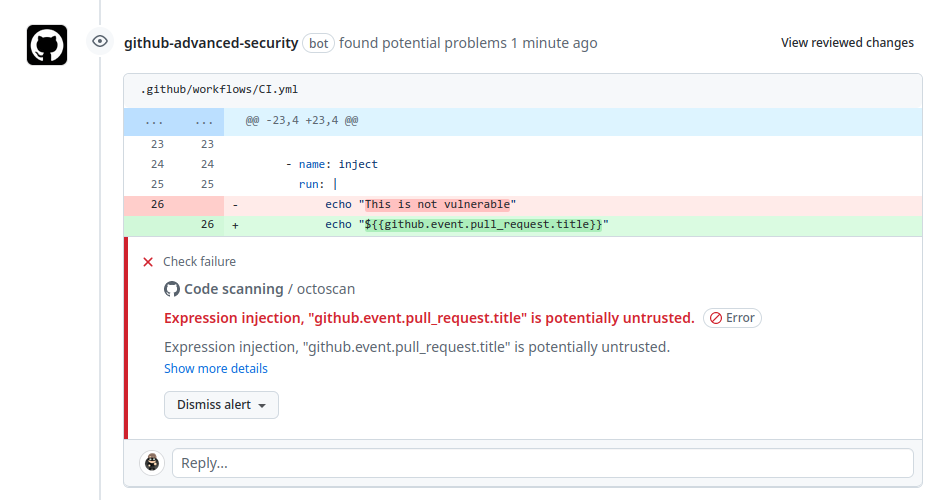
This tool can also be used directly as a GitHub action to scan your repository on push/pull_request events. For more information please check this repository.
The complete list of rules can be found with this command:
$ octoscan scan --list-rules
2024/08/07 16:50:48 [INFO] Available rules
- shellcheck
	Checks for shell script sources in "run:" using shellcheck
- credentials
	Checks for credentials in "services:" configuration
- dangerous-action
	Check for dangerous actions.
- dangerous-checkout
	Check for dangerous checkout.
- expression-injection
	Check for expression injection.
- dangerous-write
	Check for dangerous write operation on $GITHUB_OUTPUT or $GITHUB_ENV.
- local-action
	Check for local actions.
- runner-label
	Checks for GitHub-hosted and preset self-hosted runner labels in "runs-on:"
- unsecure-commands
	Check 'ACTIONS_ALLOW_UNSECURE_COMMANDS' env variable.
- known-vulnerability
	Check for known vulnerabilities.
- bot-check
	Check for if statements that are based on a bot identity.
- dangerous-artefact
	Check for workflow that upload artefacts containing sensitive files.
- overprovisioned-secrets
	Check for dumps (toJSON(secrets)) and dynamic accesses (secrets[...]) of the secrets context.
- toctou
	Check for checkouts of a mutable PR reference in workflows triggered after an approval (comment, dispatch, label).
- prompt-injection
	Check for AI agents that process untrusted input, that anyone can trigger or that have dangerous tools.
- unsound-condition
	Check for "if:" conditions that can be bypassed or that are always true.
- debug-external-trigger
	Check for workflow that can be externally triggered.
- debug-artefacts
	Check for workflow that upload artefacts.
- debug-js-exec
	Check for workflow that execute system commands in JS scripts.
- debug-oidc-action
	Check for OIDC actions.
- repo-jacking
	Verify that external actions are pointing to a valid GitHub user or organization.
Triggers like workflow_run or pull_request_target run in a privileged context, as they have read access to secrets and potentially have write access on the targeted repository. Performing an explicit checkout on the untrusted code will result in the attacker code being downloaded in such context.

Since actions/checkout v7, the action refuses to fetch fork PR code in pull_request_target and workflow_run workflows (the protection is backported to the floating major tags v2 and later, not to SHA, minor or patch pins). The rule reports:
ref or a repository that is the head repository of the PR, and tells for privileged events if the pinned version has this protection;allow-unsafe-pr-checkout, the input that disables the protection: it is a deliberate opt-out, look at it closely.





