 completetech-security/sharp-vectorfreed-check
Offline Sharp / librsvg evidence checker for CVE-2026-96889. Sharp and librsvg version and build evidence. Standalone Python; JSON/CSV/HTML reports; no exploit payloads.




An offline evidence checker for CVE-2026-96889 / GHSA-wq5f-xc86-pv6w, the librsvg memory vulnerability used through Sharp. It classifies the versions, provenance and configuration that you report; it does not inspect a running system.
The checker keeps the selected native library, reported version, provenance, platform, libc, SVG input path and hardening separate. It does not import Sharp, execute applications, decode an image, send a probe, test reachability or detect compromise. Every result retains exploitability: not_tested.
Results describe supplied evidence, not verified runtime state. Use the checker only for assets you are authorized to assess, and keep real inventories and reports outside version control.
python3 or a versioned executable where appropriate; python --version must report 3.10 or later.sharp_rsvg_rce_check.py. No packages, Node.js, companion files or network access are required.python sharp_rsvg_rce_check.py --sharp-version 0.35.4 --library-source bundled --sharp-build-source upstream
python sharp_rsvg_rce_check.py --sharp-version 0.35.5 --library-source bundled --sharp-build-source upstream
python sharp_rsvg_rce_check.py --library-source global --librsvg-version 2.63.2 --librsvg-build-source upstream
python sharp_rsvg_rce_check.py --inventory examples/inventory.json --format json
python sharp_rsvg_rce_check.py --inventory examples/inventory.json --format html --output report.html
The first two commands assess an official Sharp bundle below and at its reported fix, the third an independently reported global librsvg, and the last two a synthetic inventory. examples/inventory.json is synthetic. Without --output, the report is printed to stdout (JSON by default).
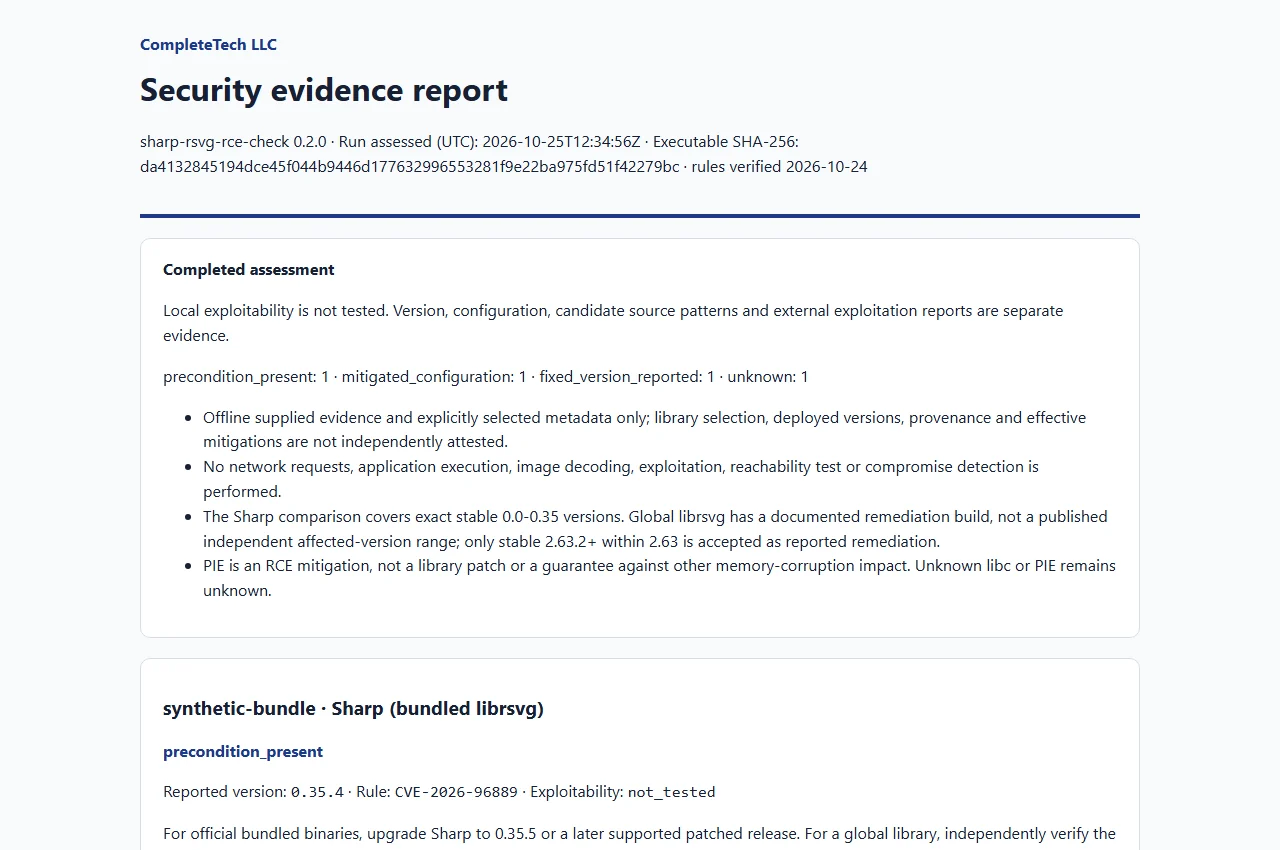
Open the synthetic example report. Example data only; this is not a live assessment. The preview images are screenshots of that example, not output from a real system.
Run python sharp_rsvg_rce_check.py --help for the complete option list. Supply an inventory, at least one reported version or explicit adapter files:
--inventory FILE, a bounded schema-v1 JSON inventory. It cannot be combined with per-asset options.--sharp-version, --librsvg-version, --library-source, --platform, --libc, --node-pie, --svg-decoder and --untrusted-svg. --sharp-version and --librsvg-version are repeatable so that conflicting observations are preserved rather than merged.--evidence-root (see Local metadata and source adapters).No directory is scanned implicitly. Field values, bounds and the inventory format are in the reference and the inventory schema.
--library-source bundled means the deployed process is reported to use the official Sharp bundle.--sharp-build-source upstream is an operator claim, not verified provenance.--library-source global with independent native-library evidence (--librsvg-version, --librsvg-build-source) for that case.| Status | Meaning |
|---|---|
unknown | Selection, exact version, provenance or supported rule coverage cannot establish the selected component's patch state. |
potentially_affected | A reported official Sharp bundle is below its fix. Runtime conditions remain separate; this does not confirm exploitability. |
precondition_present | That affected bundle and operator-reported conditions match the documented possible RCE conditions. No live verification was performed. |
mitigated_configuration | An affected bundle remains recorded while an operator reports effective SVG blocking or Node PIE. It is not a patched or safe result. |
fixed_version_reported | The selected component meets its reviewed remediation threshold. This does not attest the deployed binary or patch set. |
The version assessment of the selected component is separate from its platform, precondition and mitigation dimensions. fixed_version_reported is a reported-version result: it is neither a verified deployed patch nor a safety guarantee, and potentially_affected is not confirmed exploitability. A global result classifies the independently supplied native library, not an installed Sharp package.
Missing libc or PIE remains unknown in the precondition dimensions. A non-glibc platform or reported absence of an untrusted input path does not clear the underlying memory bug. PIE addresses the documented RCE condition; other memory-corruption impact can remain.
Operational failures (exit 2) are distinct from assessment results.
| Exit | Meaning |
|---|---|
0 | Completed and no enabled gate matched. Unknown evidence does not fail by default. |
1 | --fail-on-finding matched an affected version, including mitigated_configuration, because patching still needs review; or --fail-on-unknown matched an unknown version assessment or unresolved conditions on an affected version. The two gates are independent. |
2 | Argument, input or output error, hard limit or schema validation failure. |
130 | Interrupted. Completed assets are preserved with complete=false when the report can be written. |
An interruption after a complete report is published preserves that report and exits 130. If an interrupt leaves file publication indeterminate, the checker exits 130 without retrying; inspect the output before retrying, because the diagnostic does not establish whether publication succeeded. Once stdout publication starts, an interruption can leave a partial document, and no second report is appended.

