Mobile-Security-Framework-MobSF

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

The AI offensive security OS - open, self-improving, extensible. Find, verify, and fix vulnerabilities 24/7.

Some good resources for getting started with application security

C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…

AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.

Django application that performs SAST and Malware Analysis for Android APKs

AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)

Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.

Source code for the Binaries of OWASP WrongSecrets

opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis

A vulnerable version of Rails that follows the OWASP Top 10

The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…

Encode. Decode. Identify. Smart decoding for any data.

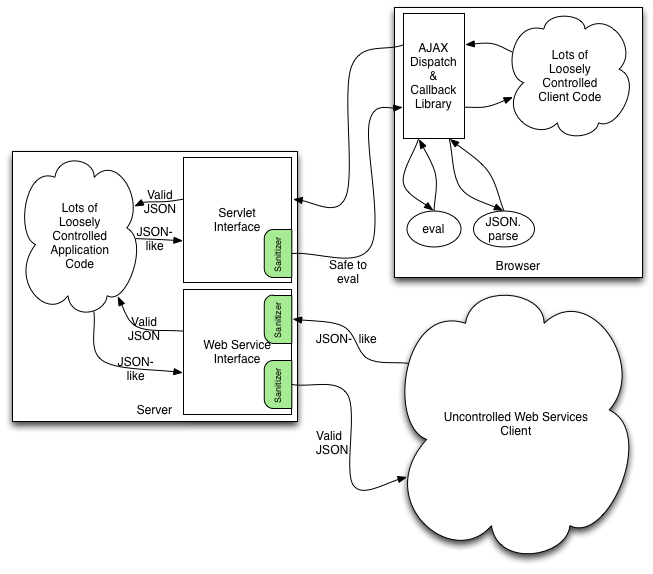
Given JSON-like content, The JSON Sanitizer converts it to valid JSON.

Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…

Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.

WEB SERVICE SECURITY ASSESSMENT TOOL

Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…