
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
FunctionStomping — Shellcode injection technique. Given as C++ header, standalone Rust program or library. | Kitploit
Tools/GitHubGitHub/idov31/functionstomping
Defensive ToolsPrivilege EscalationExploitationIDS/IPS EvasionShellcodePost-ExploitationRed TeamingShellcode GenerationPayload DevelopmentBinary ExploitationArchived
70690503 years agoReviewed by Kitploit
Share
GitHub
idov31/functionstomping

FunctionStomping

Shellcode injection technique. Given as C++ header, standalone Rust program or library.

View RepositoryWebsite

FunctionStomping

image image image

Description

This is a brand-new technique for shellcode injection to evade AVs and EDRs. This technique is inspired by Module Stomping and has some similarities. As to this date (23-01-2022) also hollows-hunter doesn't find it.

The biggest advantage of this technique is that it isn't overwritting an entire module or pe, just one function and the target process can still use any other function from the target module.

The disadvantage is that it won't work for every function in the wild (but it will work for most of them), the exact explanation is in my blog: The Good, The Bad And The Stomped Function.

NOTE: It is possible that AV will flag this, if the signature is a signature of msfvenom/metasploit it is fine! you just need to change the shellcode or encrypt it.

UPDATE: Apperantly this isn't the first PoC avaliable and RastaMouse wrote a blog post that is a similar thing in C#.

Usage

You either include the header to your program like this:

#include "functionstomping.hpp"

int main() {
    // Just get the pid in any way and pass it to the function.
    DWORD pid = 3110;
    FunctionStomping(pid);
    return 0;
}

Or use the rust program:

cd functionstomping
cargo b
functionstomping.exe <pid>

After you ran this program you MUST call the function from the remote process! (If you used the default function CreateFile then you must call to it from the remote process!).

Setup

Currently, the shellcode to run is just to pop a calculator, but all you need to do is replace the unsigned char shellcode[] with your shellcode. I used C++ 17 and VS2019 to compile the program with the C++ header and rust version 2021 to compile the rust program (you can see the dependencies in the Cargo.toml).
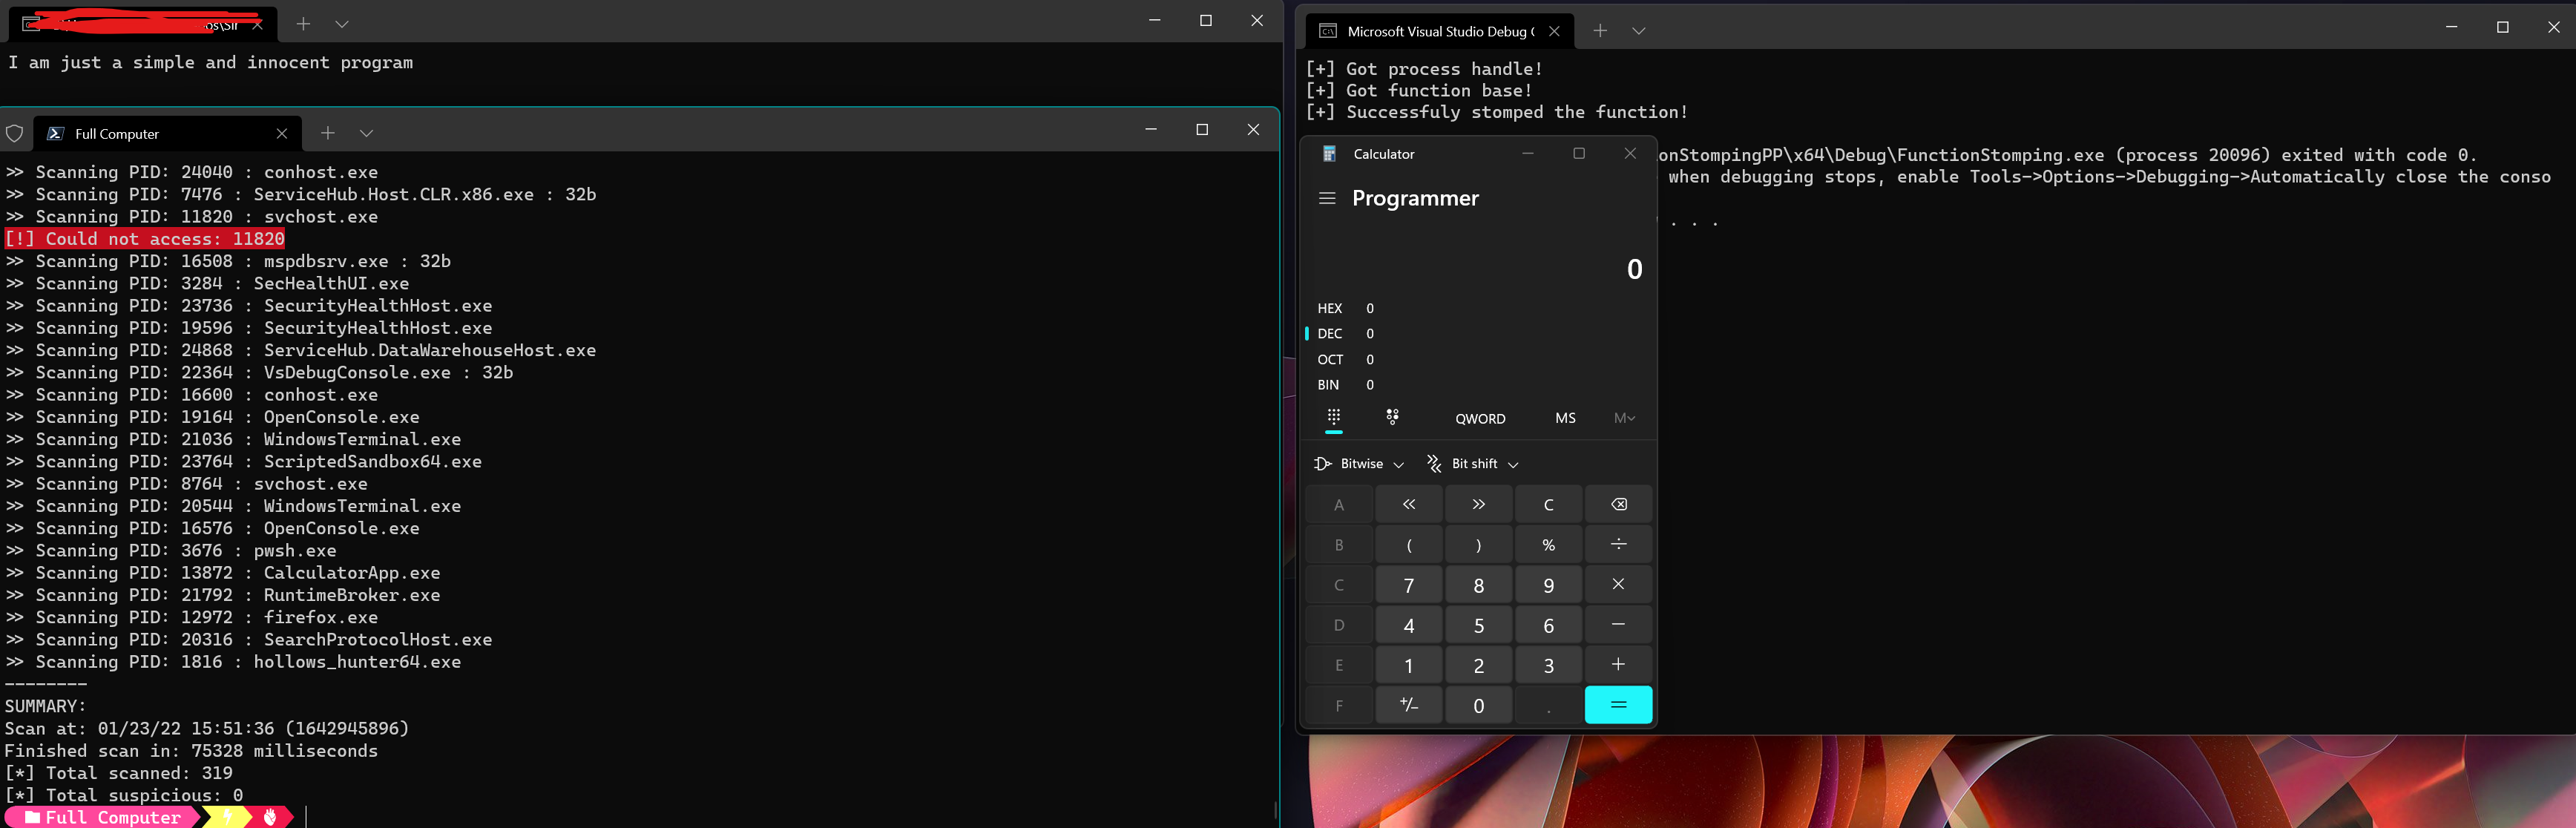
POC

Disclaimer

I'm not responsible in any way for any kind of damage that is done to your computer / program as cause of this project. I'm happily accept contribution, make a pull request and I will review it!


Acknowledgments

ModuleStomping

Masking Malicious Memory by CyberArk

RastaMouse's Version

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →






